
Cybersecurity specialist with ability to identify flaws
Cybersecurity specialist with ability to identify flaws
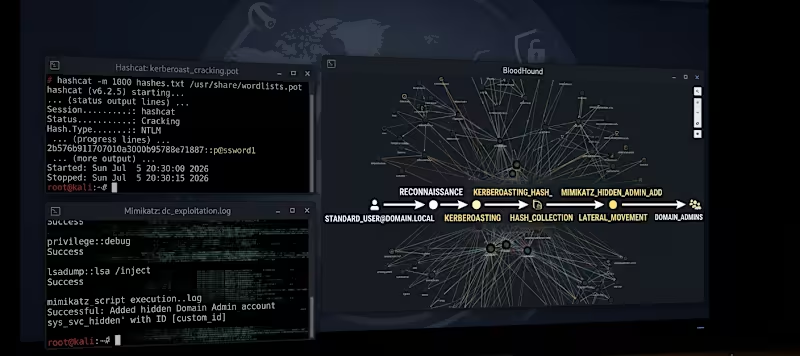
I simulated a real-world Active Directory (AD) attack to identify and exploit misconfigurations within a Windows domain environment. The goal was to practice enumeration techniques, escalate privileges to domain admin, and establish persistent access.
I started with LDAP enumeration using ldapsearch to map domain users and groups. Using BloodHound, I visualized attack paths and identified a Kerberoastable service account — a weak SPN tied to an outdated service. I extracted the hash using GetUserSPNs.py (http://GetUserSPNs.py) and cracked it with Hashcat, revealing the cleartext password. I then used Pass-the-Hash to authenticate as a domain admin using PsExec. To maintain persistence, I added a domain admin backdoor account using Mimikatz. Finally, I cleared event logs to avoid detection and exported a full attack report for remediation.
Tools Used: ldapsearch, BloodHound, Hashcat, GetUserSPNs.py (http://GetUserSPNs.py), PsExec, Mimikatz, eventlog (for cleanup)
Deliverable: Full attack timeline with screenshots, enumeration outputs, and security recommendations.
0
36

I conducted a complete web application security assessment on Damn Vulnerable Web Application (DVWA) using manual and automated testing techniques. The goal was to identify and exploit OWASP Top 10 vulnerabilities.
I mapped the application using Burp Suite and discovered multiple injection points. I exploited SQL Injection to bypass authentication and extract sensitive data from the database using sqlmap. I also tested for Cross-Site Scripting (XSS) with custom payloads and successfully hijacked session cookies using document.cookie injection. I chained a file upload vulnerability with a PHP reverse shell to gain remote access to the server. All findings were documented with proof-of-concept screenshots and step-by-step remediation guidance.
Tools Used: Burp Suite, sqlmap, OWASP ZAP, curl, custom payloads
Deliverable: A detailed report including vulnerability exploitation steps, proof-of-concept, and mitigation strategies.
0
147

I performed a complete network penetration test on a deliberately vulnerable Linux machine (Metasploitable2) to simulate a real-world attacker scenario. The objective was to identify exploitable services, gain initial access, escalate privileges to root, and extract sensitive data.
I started with reconnaissance using nmap to discover open ports and services. I identified outdated and vulnerable services including vsftpd 2.3.4 and Samba 3.0.20. Using Metasploit, I exploited the vsftpd backdoor to gain initial shell access. I then used shell_to_meterpreter to upgrade my session to a Meterpreter shell, giving me greater control. I dumped password hashes from /etc/shadow and cracked them using John the Ripper. Finally, I escalated privileges to root using the Samba usermap_script exploit and documented the entire process with screenshots.
Tools Used: nmap, Metasploit, Meterpreter, John the Ripper, searchsploit
Deliverable: A comprehensive report including attack timeline, exploited CVEs, and remediation recommendations.
0
348

I discovered a stored cross-site scripting (XSS) vulnerability in a practice web application's comment section that allowed me to inject malicious JavaScript that would execute in any user's browser. By submitting a comment containing a script payload, I successfully stole session cookies from other users and could have hijacked their accounts, performed actions on their behalf, or defaced the website. This finding was documented in a comprehensive report including proof-of-concept screenshots showing cookie theft, CVSS risk scoring of 6.5 (Medium), and step-by-step remediation guidance including input sanitization and output encoding. This assessment demonstrates my ability to find client-side vulnerabilities that can compromise every user visiting the site.
0
89


Software dev: AI solutions for real business problems.
New to Contra
Software dev: AI solutions for real business problems.
I built a multi-tenant fintech operations platform. React on the frontend, Node API, Postgres with row-level tenant isolation underneath. It connects to Stripe, Plaid, QuickBooks and Xero through verified webhooks. Every event signature is checked against the raw request body, duplicates collapse into a durable idempotent inbox, and each event gets matched to the right tenant on the server before anything touches the ledger.
Money is stored in minor units, never as floats. The reconciliation engine catches amount mismatches, orphan payments and stale cursors. Anything it can't explain lands in an anomaly queue with a dead-letter lane. There's also an AI document pipeline, OCR plus extraction with prompt-injection canary tests, and an e-sign flow.
The test suite runs 325 tests green against a real Postgres. Dockerized, with database migrations and a disaster-recovery drill script.
0
11
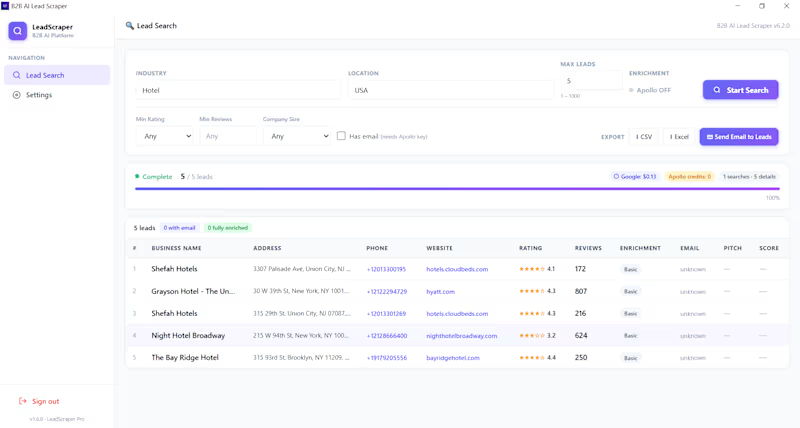
I built a B2B lead generation app. You type in an industry and a location, and it finds real businesses through the Google Places API, then enriches them with company data and decision-maker emails via Apollo. Every email gets validated, and GPT-4o-mini writes a short personalized pitch plus a lead score for each lead. One click exports everything to CSV or Excel.
The three API keys are yours. You enter them once in the setup wizard and they stay encrypted on your own machine. Nothing is scraped, no proxies, no LinkedIn tricks, no SMTP probing. The app tells you exactly what each run costs in Google API fees before you spend it, filters out bad-fit leads before any paid enrichment runs, and picks up cleanly if the server restarts halfway.
It ships as a one-click Windows installer and a Docker image. React on the frontend, FastAPI on the backend, JWT auth, and 14 tests green.
0
17
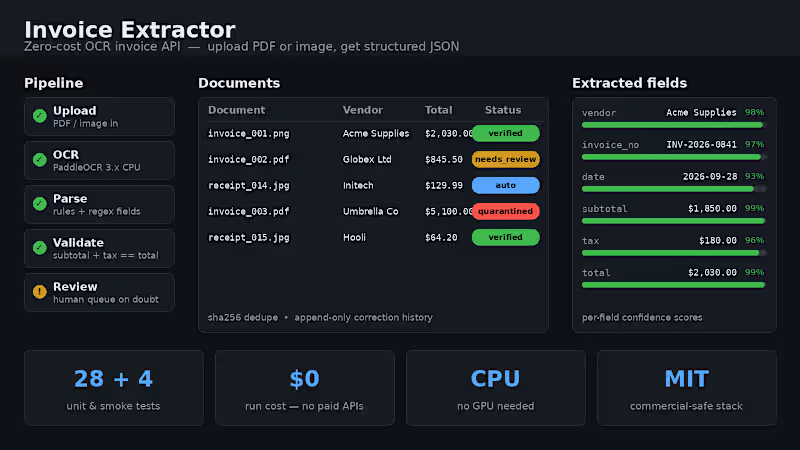
I built an invoice extraction API that costs nothing to run. You upload a PDF or image, and it returns clean structured data: vendor, invoice number, dates, line items, subtotal, tax, total — every field with its own confidence score.
Under the hood it runs PaddleOCR on a regular CPU (Tesseract as backup), then a rule-based parser pulls out the fields. Before anything gets accepted, an arithmetic check makes sure subtotal plus tax actually equals the total — that catches the small digit errors OCR often makes. If something looks uncertain, it goes to a human review queue instead of failing quietly, and every correction is saved in an append-only log so you can always see what changed.
No paid vision APIs, no GPU needed. The whole stack is open-source, it ships in Docker, and it's covered by 28 unit and 4 smoke tests.
0
22
Built a Bring-Your-Own-Key AI agent platform in Python: clients connect their own provider API keys, so the platform never holds or pays for them.
It ships with an encrypted key vault (per-tenant, with rotation), a model router with per-call cost tracking and a global kill switch, a code-building agent that works inside isolated Docker sandboxes, and a WhatsApp control layer on Meta's official Cloud API with a full audit trail. There is also a research pipeline that verifies claims before they reach an article draft.
204 automated tests, all green. One command deploys it.
0
28

AI Automation & Full-Stack Developer | Framer Expert
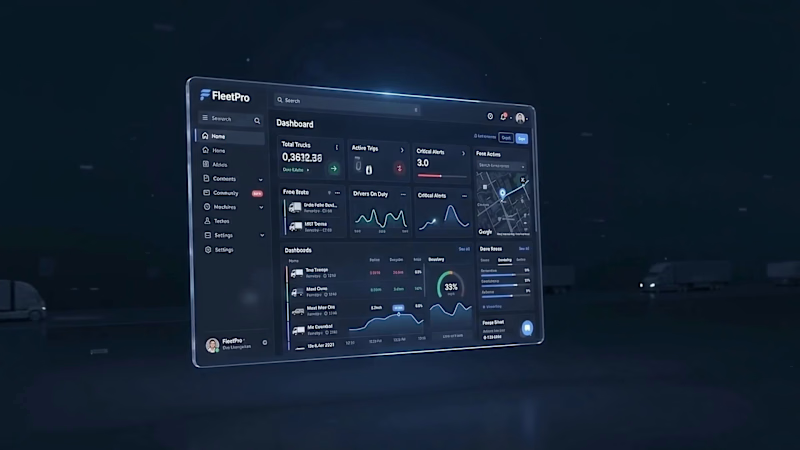
𝐅𝐥𝐞𝐞𝐭𝐏𝐫𝐨 – 𝐒𝐦𝐚𝐫𝐭 𝐅𝐥𝐞𝐞𝐭 𝐌𝐚𝐧𝐚𝐠𝐞𝐦𝐞𝐧𝐭 & 𝐑𝐞𝐚𝐥-𝐓𝐢𝐦𝐞 𝐓𝐫𝐚𝐜𝐤𝐢𝐧𝐠 𝐏𝐥𝐚𝐭𝐟𝐨𝐫𝐦
Designed and developed a complete fleet management platform to help businesses monitor vehicles, drivers, trips, performance, and operational alerts from one centralized system.
FleetPro provides a real-time dashboard for tracking fleet activity, monitoring active drivers and trucks, reviewing trips, analyzing revenue and operational performance, and identifying critical issues before they impact operations.
𝐓𝐡𝐞 𝐩𝐥𝐚𝐭𝐟𝐨𝐫𝐦 𝐢𝐧𝐜𝐥𝐮𝐝𝐞𝐬:
𝐂𝐞𝐧𝐭𝐫𝐚𝐥𝐢𝐳𝐞𝐝 𝐅𝐥𝐞𝐞𝐭 𝐃𝐚𝐬𝐡𝐛𝐨𝐚𝐫𝐝 – View total trucks, active trips, drivers on duty, and critical alerts at a glance.
𝐑𝐞𝐯𝐞𝐧𝐮𝐞 & 𝐏𝐞𝐫𝐟𝐨𝐫𝐦𝐚𝐧𝐜𝐞 𝐀𝐧𝐚𝐥𝐲𝐭𝐢𝐜𝐬 – Monitor fleet revenue, operating costs, profitability, and performance trends.
𝐑𝐞𝐚𝐥-𝐓𝐢𝐦𝐞 𝐕𝐞𝐡𝐢𝐜𝐥𝐞 𝐓𝐫𝐚𝐜𝐤𝐢𝐧𝐠 – Track trucks, routes, trip progress, driver activity, and estimated arrival times.
𝐒𝐦𝐚𝐫𝐭 𝐀𝐥𝐞𝐫𝐭𝐬 & 𝐌𝐨𝐧𝐢𝐭𝐨𝐫𝐢𝐧𝐠 – Detect long stops, route delays, driver inactivity, and other critical operational events.
𝐃𝐫𝐢𝐯𝐞𝐫 & 𝐓𝐫𝐮𝐜𝐤 𝐌𝐚𝐧𝐚𝐠𝐞𝐦𝐞𝐧𝐭 – Manage driver profiles, vehicle assignments, statuses, and fleet information.
𝐓𝐫𝐢𝐩 𝐌𝐚𝐧𝐚𝐠𝐞𝐦𝐞𝐧𝐭 – Monitor current and historical trips with route and status information. The goal was to give fleet operators better visibility into daily operations, reduce manual monitoring, and enable faster operational decisions through a clean and scalable management system.
𝐓𝐞𝐜𝐡 & 𝐂𝐚𝐩𝐚𝐛𝐢𝐥𝐢𝐭𝐢𝐞𝐬:
Fleet Management • GPS Tracking • Real-Time Monitoring • Analytics Dashboard • Revenue Tracking • Driver Management • Trip Management • Smart Alerts • Automation • Custom Web Application
1
2
527
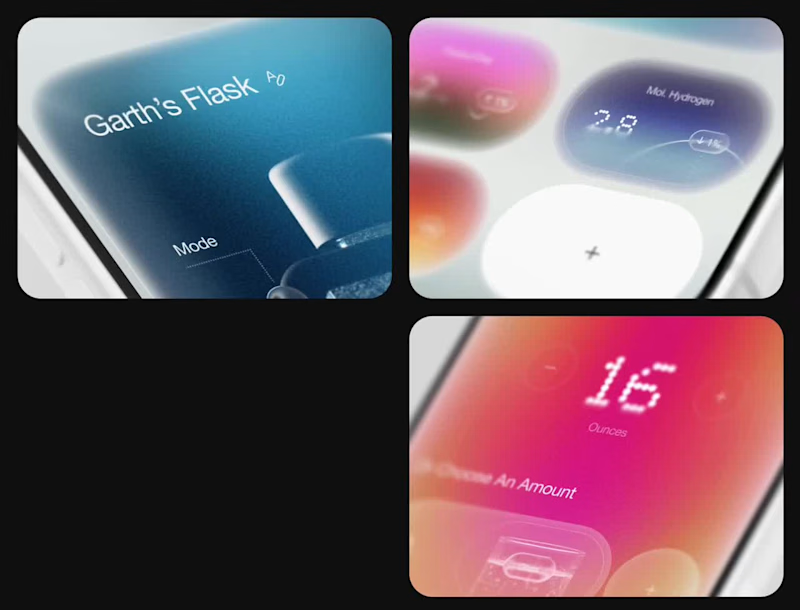
Smart Hydration Tracking Mobile App
We developed Hydroflask, a smart hydration companion app designed to make daily water tracking effortless, intuitive, and engaging.
The app connects with a smart water bottle to automatically track water intake while allowing users to manually log drinks using quick presets for glasses and mugs.
Key Features:
Smart Hydration Tracking: Automatically records water intake through a connected smart bottle.
Quick-Log Presets: Easily adds water consumption using glass and mug options.
Real-Time Progress Visualization: A dynamic gradient interface reflects daily hydration progress.
Personalized Hydration Goals: Helps users monitor their intake and stay consistent with daily targets.
Intuitive Mobile Experience: A clean, modern interface designed for effortless daily use.
The Goal: Transform everyday hydration tracking into a simple, personalized experience that encourages healthier habits.
The Result: A modern mobile companion that combines smart technology, thoughtful UI/UX design, and real-time tracking to help users build more consistent hydration routines.
2
1
186
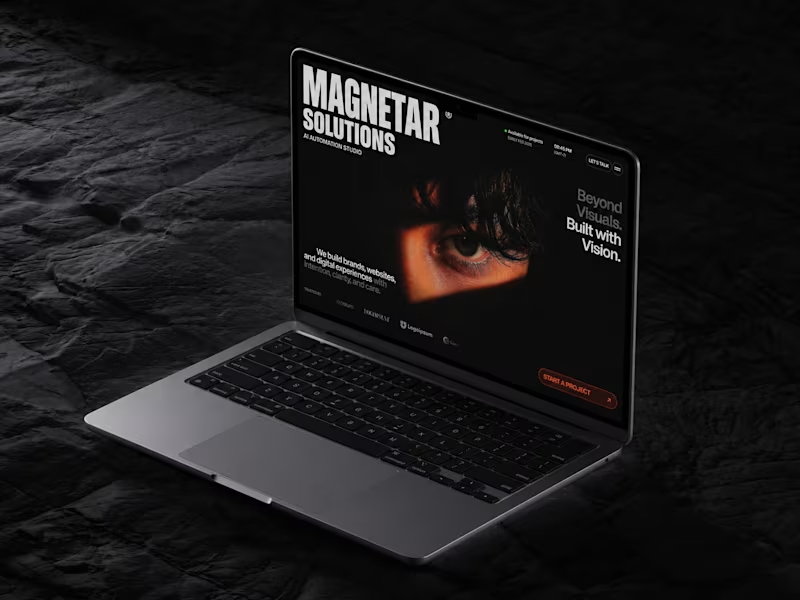

Full-Stack Next.js & AI Developer | MVPs in 2 Weeks
Full-Stack Next.js & AI Developer | MVPs in 2 Weeks

AI Automation & Systems Architect: AI Agents | N8N Developer
- 6
- Followers
AI Automation & Systems Architect: AI Agents | N8N Developer


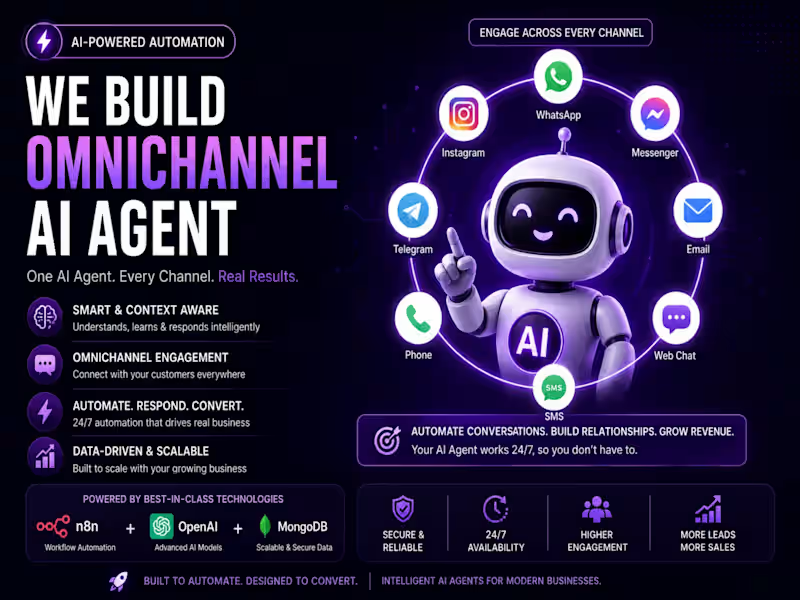

AI Engineer & Solution Architect. I build AI agents and RAG
New to Contra
AI Engineer & Solution Architect. I build AI agents and RAG
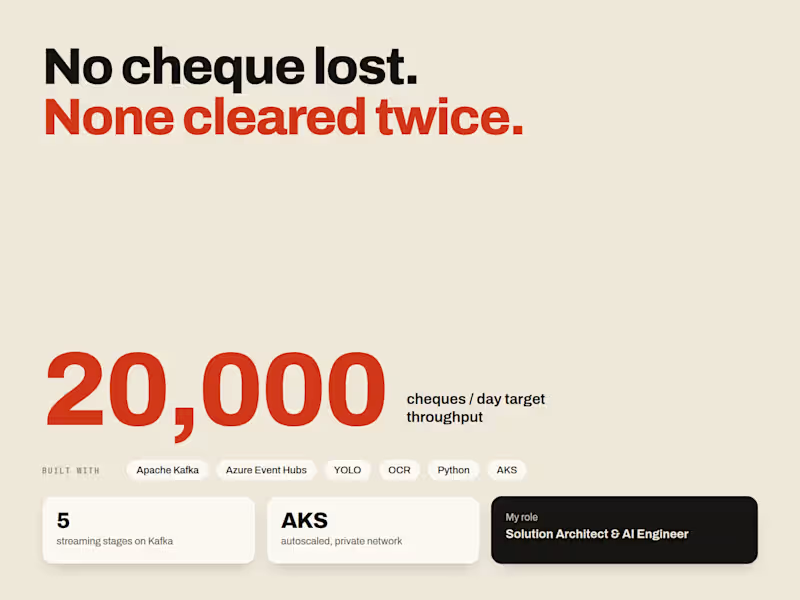

UI/UX Designer crafting intuitive, modern digital experience
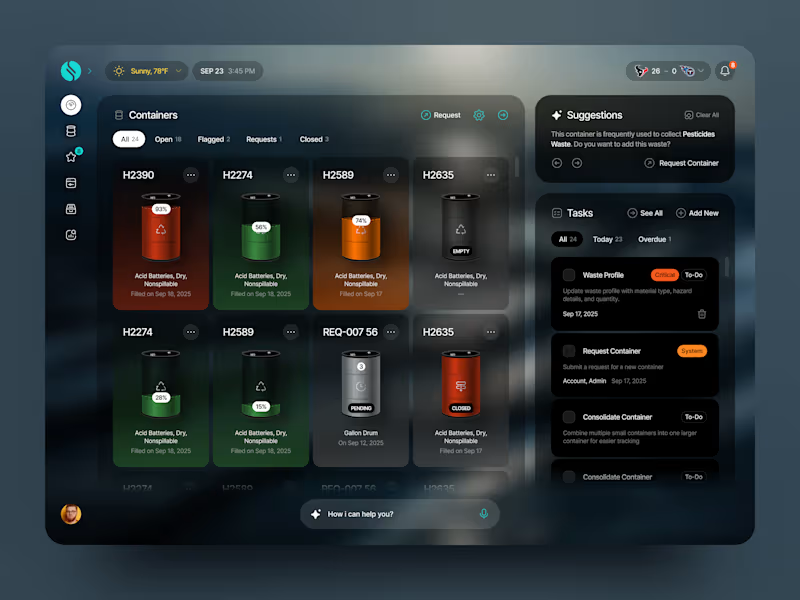
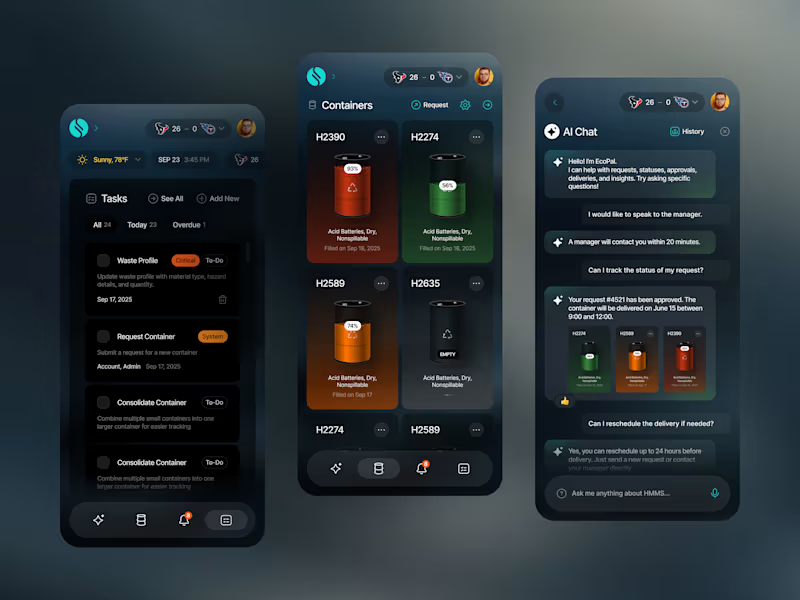
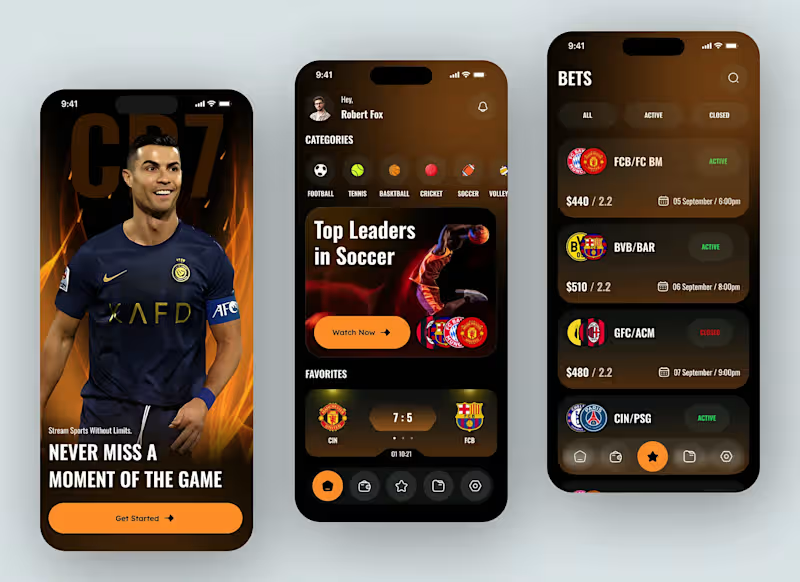
We design MVP apps that help startups move fast, validate ideas, and launch with confidence. Our focus is on building only what matters—clear user flows, essential features, and a product experience that’s easy to understand and test.
0
68
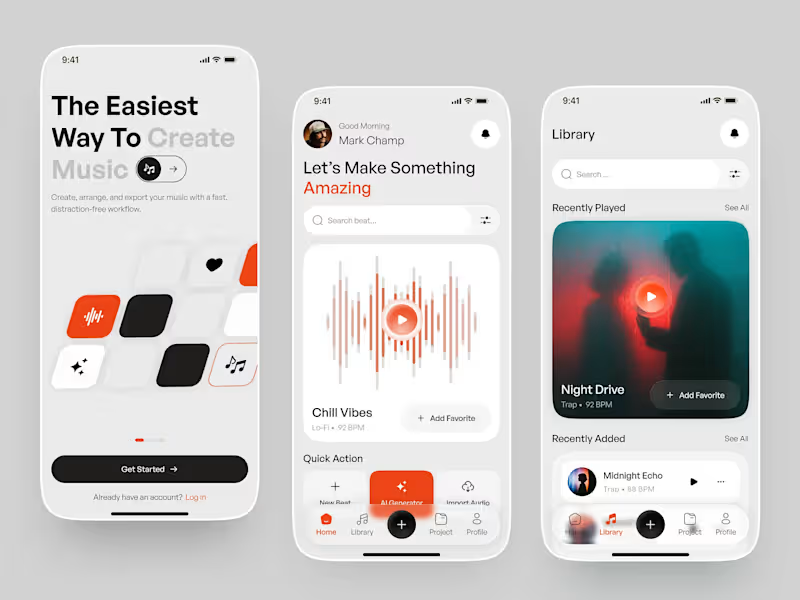
Music creation experience designed to make producing music feel simple, fast, and distraction-free.
The concept explores a smooth workflow for creating beats, generating music with AI, discovering sounds, and managing projects—all within a minimal and intuitive interface.
The visual direction combines soft neutrals, bold orange accents, rounded cards, and spacious layouts to create a friendly yet premium music-production experience.
Designed with a focus on simplicity, discoverability, and effortless music creation.
0
78

AI & Full-Stack Engineer | Building Production AI SaaS, APIs
New to Contra
AI & Full-Stack Engineer | Building Production AI SaaS, APIs
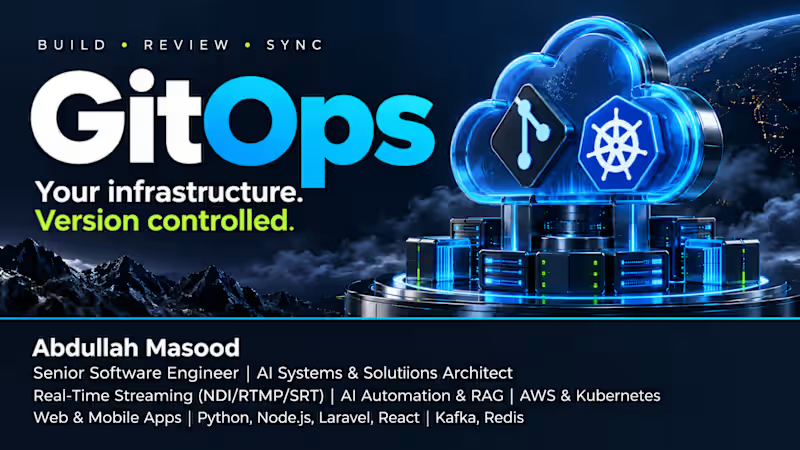
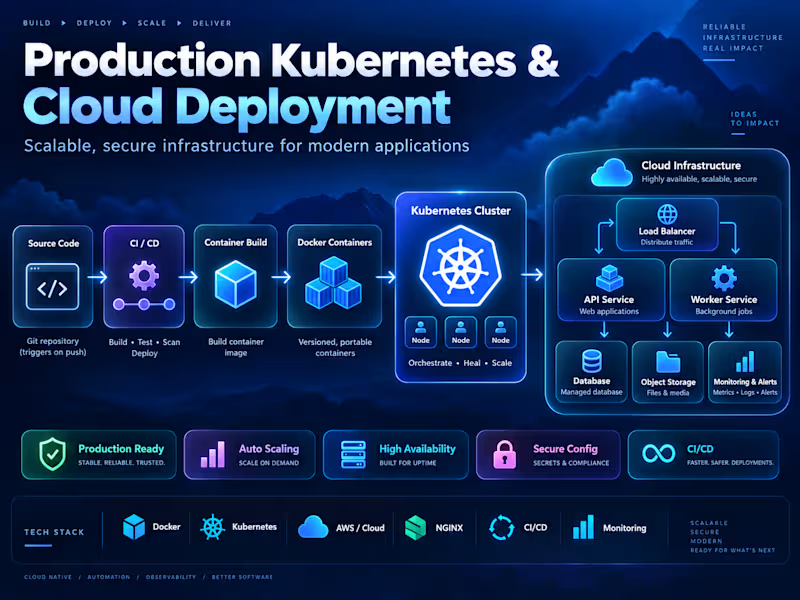
A Kubernetes deployment should be easy to trace: what changed, who changed it, and why.
That’s what interests me about GitOps.
With GitOps, the desired state of your infrastructure and applications lives in Git. Changes go through commits and pull requests, while a controller such as Argo CD or Flux continuously reconciles the running environment with that desired state.
A typical workflow looks like this:
• Build and test the application through CI.
• Push the Docker image to a registry.
• Update the image version in the Git configuration.
• Review and merge the change.
• Let the GitOps controller reconcile the cluster.
The benefits go beyond automated deployments:
✅ A versioned history of configuration changes
✅ Reviewable changes before deployment
✅ Visibility into configuration drift
✅ A repeatable way to manage environments
One important detail: reverting a Git commit can restore an earlier configuration, but database migrations and changes to application data still need their own recovery plan.
For me, GitOps connects development and operations through a workflow both teams already understand: Git.
Are you using Argo CD, Flux, or CI-driven deployments for your Kubernetes workloads?
1
311
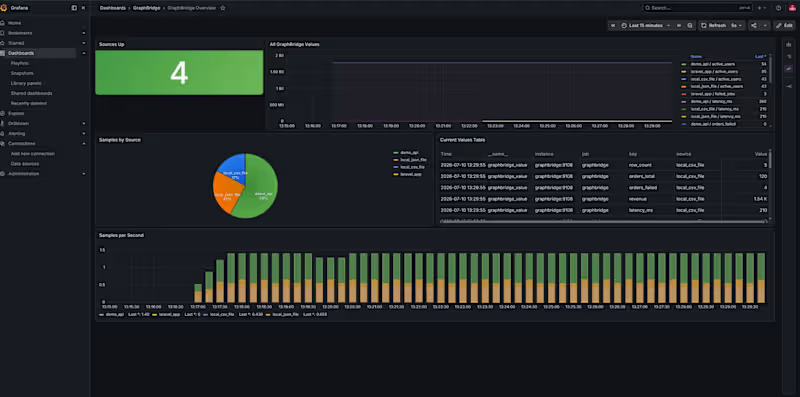
🚀 Introducing GraphBridge – Turn JSON into Grafana Dashboards
One thing I've noticed while working on different projects is that applications already have valuable metrics, but getting those metrics into Grafana often requires exporters, custom integrations, or additional setup.
I wanted something much simpler.
So I built GraphBridge.
The idea is straightforward:
Your Application
↓
Send JSON
↓
GraphBridge
↓
Prometheus
↓
Grafana
Instead of writing custom exporters, your application simply sends JSON metrics to GraphBridge.
For example:
{
"active_users": 85,
"orders_today": 42,
"revenue_today": 9840,
"failed_jobs": 3,
"latency_ms": 210
}
GraphBridge automatically converts the data into Prometheus metrics, making it immediately available for Grafana dashboards.
Current features
✅ JSON Webhook API
✅ REST API polling
✅ JSON & CSV data sources
✅ Prometheus /metrics endpoint
✅ Docker Compose deployment
✅ Auto-configured Grafana dashboard
✅ Example integrations for Laravel, FastAPI, Node.js, and custom applications
Possible use cases
• Application monitoring
• Queue & background job metrics
• Business dashboards
• API performance monitoring
• FFmpeg streaming statistics
• IoT sensor metrics
• Internal analytics
• Custom operational dashboards
The goal is simple:
Send JSON. Visualize everything.
This is the first public MVP, and I'm planning to continue improving it with additional integrations and monitoring templates.
I'd love your feedback and suggestions!
⭐ GitHub:
https://lnkd.in/dAYdNJxg
1
227
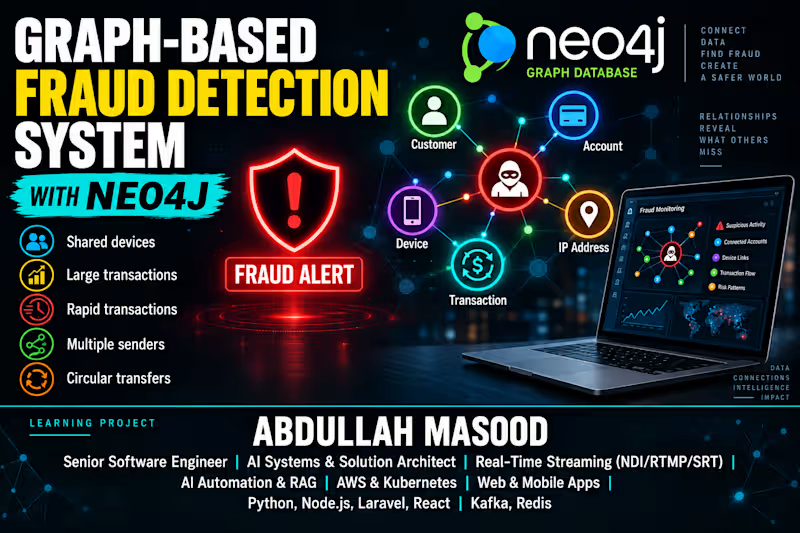
🚀 Building a Graph-Based Fraud Detection System with Neo4j
A single transaction may look normal. Its connections can tell a different story.
I’m building a learning project using Neo4j and Cypher to explore relationships between customers, accounts, transactions, and devices—and flag patterns worth investigating.
🔍 Patterns I’m exploring:
• Multiple customers sharing the same device
• Unusually large transactions
• Rapid transactions within a short period
• Multiple accounts sending money to one account
• Circular transfers between connected accounts
The focus is explainability: showing the relationships behind each flag so the suspicious activity is easier to understand.
Through this project, I’m strengthening my graph data modelling, Cypher queries, and rule-based detection skills.
Next: FastAPI integration, transaction risk scores, fraud alerts, and an interactive monitoring dashboard.
🛠️ Currently a learning prototype, with more updates coming as I build.
What would you investigate first: shared devices or circular transfers?
#Neo4j #GraphDatabase #FraudDetection #Cypher #BackendDevelopment #LearningInPublic
1
311