
I conducted a complete web application security assessment on Damn Vulnerable Web Application (DVWA) using manual and automated testing techniques. The goal was to identify and exploit OWASP Top 10 vulnerabilities.
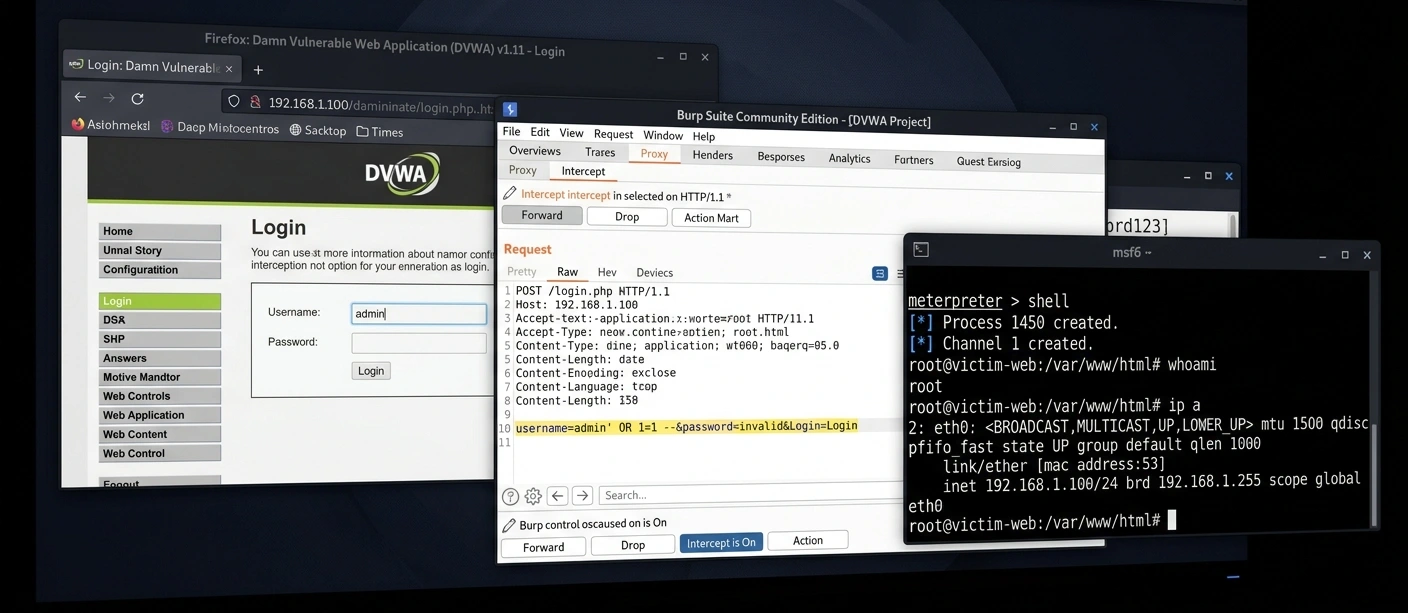
I mapped the application using Burp Suite and discovered multiple injection points. I exploited SQL Injection to bypass authentication and extract sensitive data from the database using sqlmap. I also tested for Cross-Site Scripting (XSS) with custom payloads and successfully hijacked session cookies using document.cookie injection. I chained a file upload vulnerability with a PHP reverse shell to gain remote access to the server. All findings were documented with proof-of-concept screenshots and step-by-step remediation guidance.
Tools Used: Burp Suite, sqlmap, OWASP ZAP, curl, custom payloads
Deliverable: A detailed report including vulnerability exploitation steps, proof-of-concept, and mitigation strategies.
0 likes · 0 views · Jul 6, 2026
I conducted a complete web application security assessment on Damn Vulnerable Web Application (DVWA) using manual and automated testing techniques. The goal ...


