Freelance Cybersecurity Specialists in Kelowna
Sign Up
Post a job
Sign Up
Log In
Filters
2
Projects
People
Results that are similar to your search
Similar results
Bob Vasic
Dublin, Ireland
AI Systems Architect | Agentic AI, Integrations & Security
$1k+
Earned
2x
Hired
5.0
Rating
511
Followers
Expert
Follow
Message
AI Systems Architect | Agentic AI, Integrations & Security
18
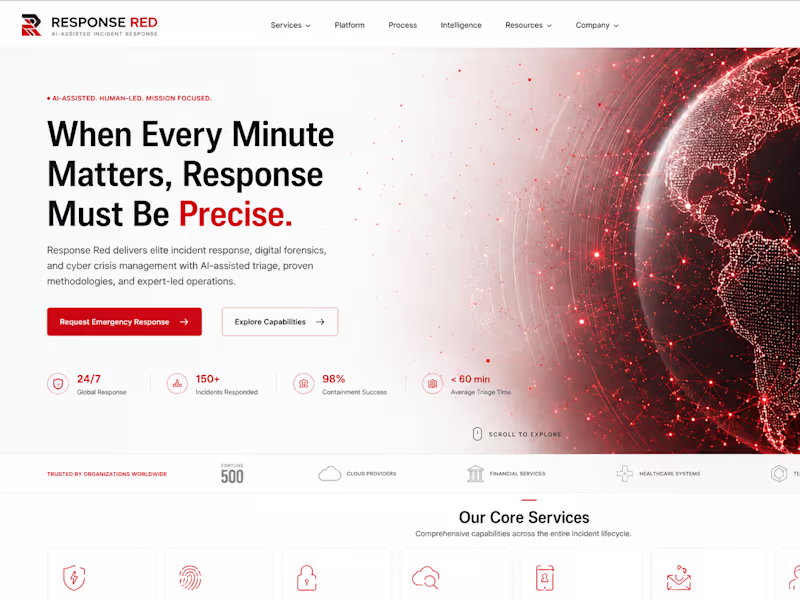
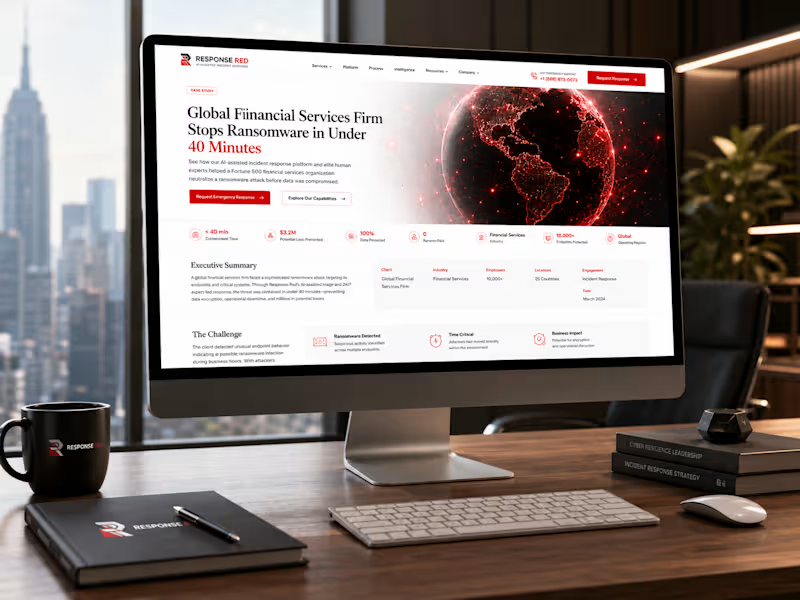
New case study live: ResponseRed.com (https://contra.com/p/OosRZZ7X-response-red-or-ai-native-incident-response-and-web3-forensics) Response Red (https://www.responsered.com/) was built for the moment when cybersecurity stops being theoretical. Active compromise. Ransomware pressure. Identity takeover. Cloud intrusion. Business email compromise. Endpoint breach. Data exposure. Operational disruption. The platform was designed to communicate one thing clearly: Response must be immediate, disciplined, intelligence-led, and executed by people who understand high-stakes cyber operations. Response Red brings together 24/7 global incident response, authorized offensive security, penetration testing, red teaming, digital forensics, proactive incident management, AI-assisted triage, and executive-grade cyber crisis reporting. The website and platform experience were built with a premium white-first enterprise identity, crimson red response signals, cinematic global threat visuals, structured incident intake, and security-conscious AI workflow design. This was not a brochure build. It was a full-stack cybersecurity presence designed for trust, speed, operational clarity, and market authority. Case study now published on Contra. Check it out (https://contra.com/p/OosRZZ7X-response-red-or-ai-native-incident-response-and-web3-forensics)
1
2
18
1.2K
10
ResponseRed | AI-native Incident Response & Web3 Forensics
1
10
32
26
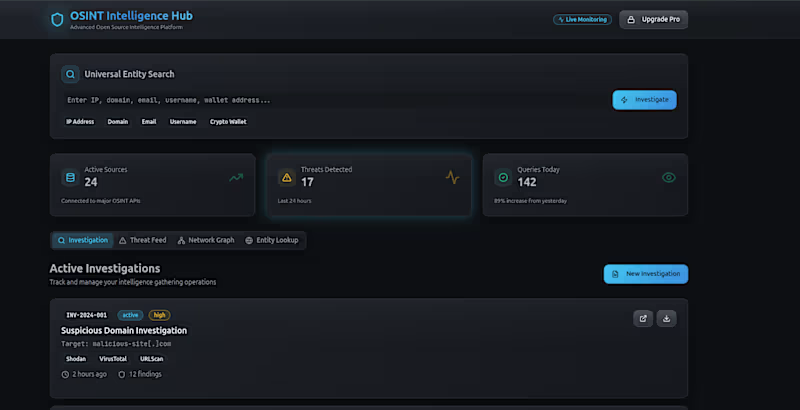
Every cybersecurity pro knows the struggle: juggling 10+ tabs just to verify a single IP or hash. I built Fuse Intel Grid to solve exactly that. It’s a professional OSINT analytics dashboard that unifies intelligence from over 20+ free sources into a single pane of glass. No more context switching—just clear, actionable data. 🚀 Key Features: Unified Intelligence: Aggregates data instantly. Powerhouse Integrations: Connects with Shodan, VirusTotal, AbuseIPDB, and more. Cost-Effective: Leverages the best free OSINT sources available. Check out the live app here: https://fuse-intel-grid.lovable.app I’d love to hear your feedback on the UI/UX or what other data sources you'd like to see integrated!
26
590
8
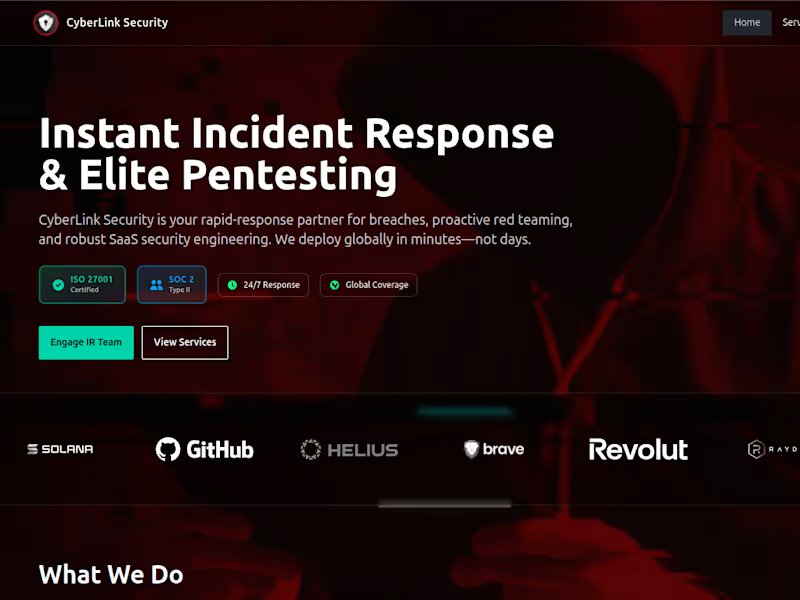
cyberlinksec.com (https://cyberliksec.com) - Implementing 2 new subsidiaries that are ongoing acquisition with CyberLink Security
1
8
623
Cybersecurity Specialist
(4)
Follow
Message
Jason Smyth
Copthorne, UK
Cyber expert specialising in Azure Security Services.
$10k+
Earned
4x
Hired
5.0
Rating
24
Followers
Follow
Message
Cyber expert specialising in Azure Security Services.
0
Microsoft Sentinel & Splunk ES Engineer for up to 6 months
0
17
0
Extended Interview Process for CrowdStrike SIEM Specialist
0
14
1
Setting up and optimising Microsoft Sentinel
1
57
0
Configure SIEM Security Operation using Microsoft Sentinel
0
51
Cybersecurity Specialist
(7)
Follow
Message
Watheq Zboun
max
United States
Microsoft 365 & Azure Solutions Architect
$5k+
Earned
2x
Hired
5.0
Rating
15
Followers
Follow
Message
Microsoft 365 & Azure Solutions Architect
1
Have you wondered how hacekrs bypass MFA? Nowadays it is getting easier. There is a phishing kit called Mirage2FA that has been working against Microsoft 365 since late 2024. Here is how it goes. The user lands on a fake login page. They type their password. They approve the MFA prompt on their phone. Everything they enter is passed straight through to Microsoft in real time, so the sign-in genuinely succeeds and looks completely normal to them. Microsoft issues the session tokens, and the kit keeps a copy. With those cookies someone can read the mailbox, open SharePoint and OneDrive, and reach anything sitting behind SSO. They never see a second prompt, because the authentication already happened. ANY.RUN (http://ANY.RUN) put numbers on it. 9,426 accounts targeted across 3,518 domains, roughly 4,532 showing signs of compromise, most of them in the US. A third of the successful logins happened on phones, where you can barely see the URL you are looking at. The advice going around is to switch on Continuous Access Evaluation. I would switch it on too. Just read the documentation first, because it does something slightly different to what people assume. CAE sessions run tokens for up to 28 hours. The default is one hour. What you get in exchange is revocation when something happens, and Microsoft is specific about what counts: the account is disabled or deleted, the password is changed or reset, MFA gets turned on, an admin revokes refresh tokens, or ID Protection flags the user as high risk. Allow up to 15 minutes for that to propagate. IP location is the only one that applies straight away. Three things worth knowing before you lean on it. It covers Exchange Online, SharePoint Online and Teams. Guest accounts are not supported, which is where a lot of contractor access lives. And it only reads IP-based named locations, so a country-based policy buys you nothing here. If I were fixing this in a tenant tomorrow, in this order: Phishing-resistant sign-in first. A FIDO2 key checks the domain it is talking to, so it will not hand anything over to a proxy wearing Microsoft's face. CAE on, so revocation actually reaches the services. Then a runbook where you revoke sessions before you reset the password. Reset first and you have changed the lock while someone is still inside holding a key that works. If session cookies walked out of your tenant this morning, what would notice, and how long would it take? Source: ANY.RUN (http://ANY.RUN) threat research, 19 August 2026. CAE behaviour from Microsoft Learn.
1
1
227
0
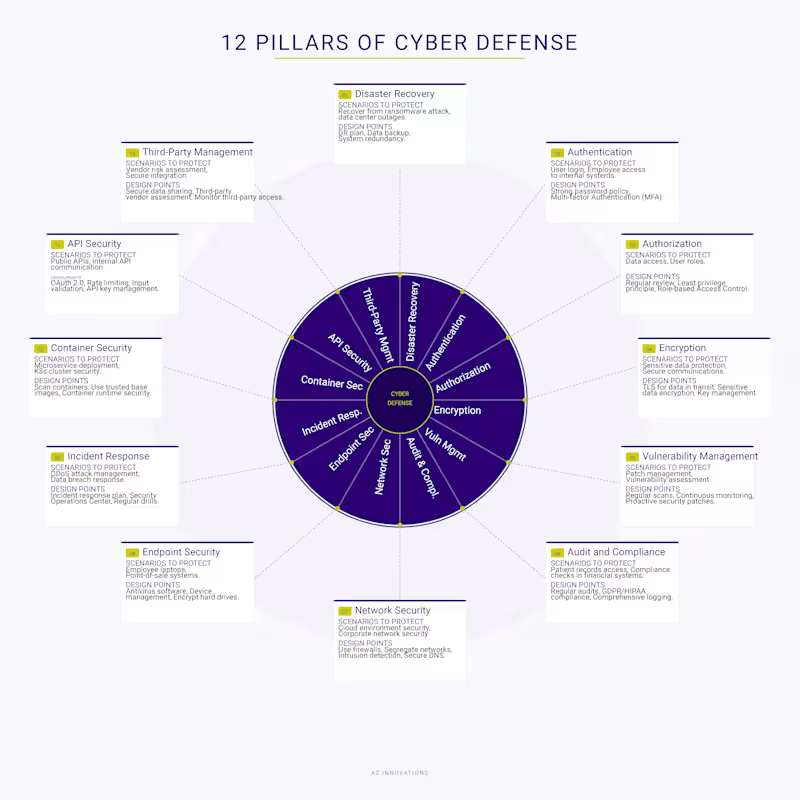
Did you know that cybercrime is projected to cost the world $10.5 TRILLION a year. What is the average data breach in the US? $10.22 million which is at a record high. Here is my question to people here, if you could only strengthen 3 out of these 12 cybersecurity pillars, which would you pick? Disaster Recovery Authentication Authorization Encryption Vulnerability Management Audit & Compliance Network Security Endpoint Security Incident Response Container Security API Security Third-Party Management I would argue Authentication, Incident Response, and Third-Party Management, because the data shows 53% of breaches start with stolen credentials, and vendor compromises are surging.
0
221
0
GoDaddy Move-Away That Uncovered a Data Residency Problem
0
11
0
Microsoft Security Architecture Diagrams
0
12
Cybersecurity Specialist
(2)
Follow
Message
Ilya Kozlov
Ukraine
HMI Interface designer. UX/UI for embedded screens & devices
$10k+
Earned
2x
Hired
4.7
Rating
64
Followers
Follow
Message
HMI Interface designer. UX/UI for embedded screens & devices
0
CCTV E-commerce platform & branding
0
21
3
HMI interface for medical equipment
3
34
5
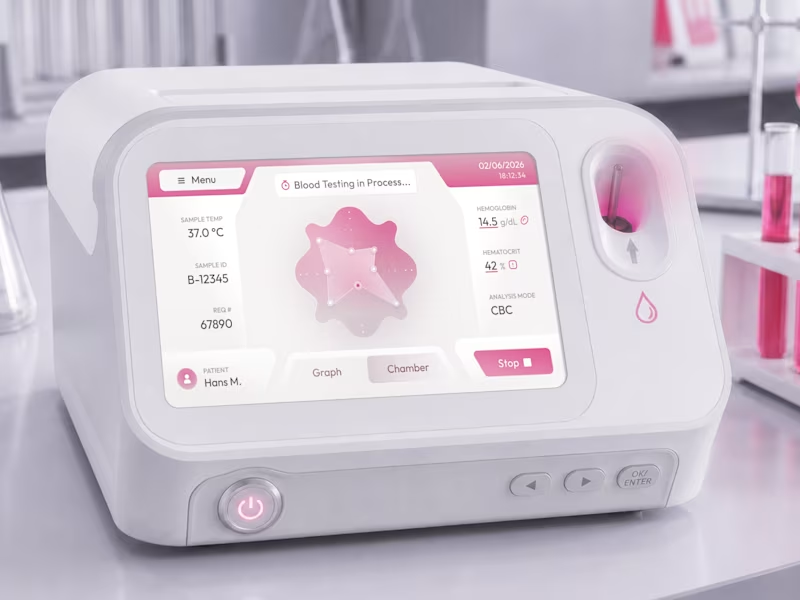
HMI design for a laboratory blood testing device
1
5
849
3
HMI design for electric motorcycle
3
775
Cybersecurity Specialist
(2)
Follow
Message
Gary Szaszik
pro
London, UK
Design Partner for B2B SaaS, Cybersecurity & Defense
35
Followers
expert
Follow
Message
Design Partner for B2B SaaS, Cybersecurity & Defense
3
Cybersecurity hero concept
2
3
225
21
Infrastructure security hero concept [alternative version]
13
21
378
3
Infrastructure security hero concept
4
3
178
2
Hero concept for a fictional critical infrastructure and DDoS mitigation company, exploring how a security firm can look credible and modern when its website is the main thing buyers judge it on
1
2
162
Cybersecurity Specialist
(8)
Follow
Message
Hamida Jannat
Dhaka, Bangladesh
Landing Page UI Designer, Figma Expert
5.0
Rating
16
Followers
Follow
Message
Landing Page UI Designer, Figma Expert
1
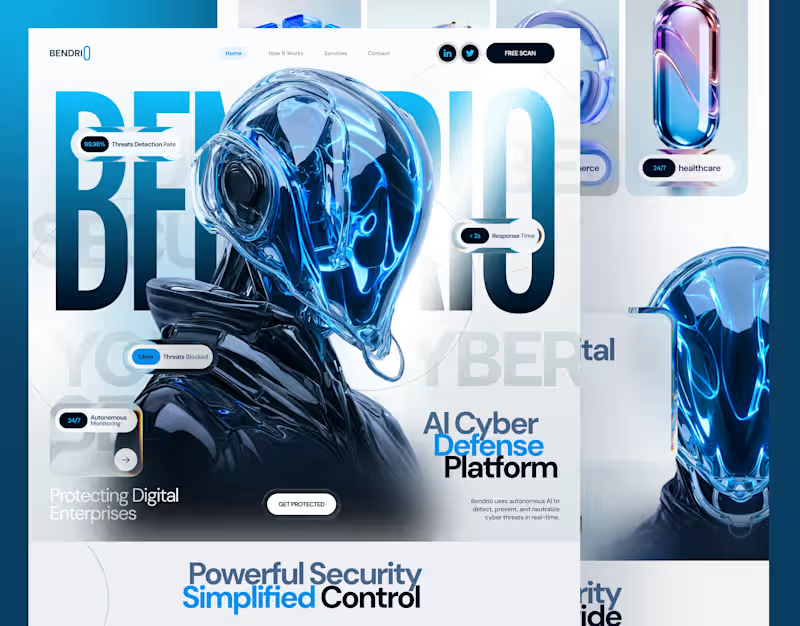
Bendrio - Cyber Security website design, landing page
1
13
2
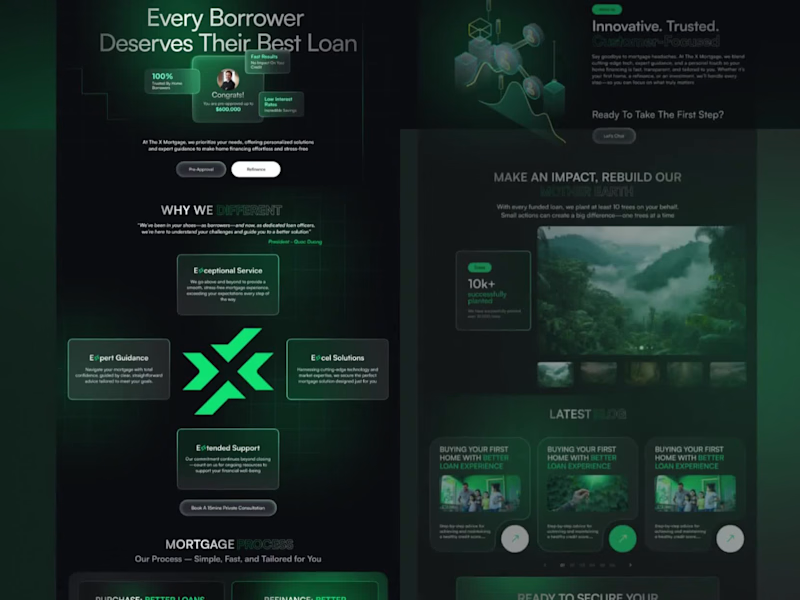
The X Mortgage - Complete Website UI/UX project
2
14
1
AirLume.Ai - AI-Powered Flight booking UI/UX Design
1
22
2
PAYROT - Website UI/UX design, Landing page, ui ux
2
15
Cybersecurity Specialist
(3)
Follow
Message
Stephen Kisong'e
Nairobi, Kenya
Cyber Security Analyst
Follow
Message
Cyber Security Analyst
0
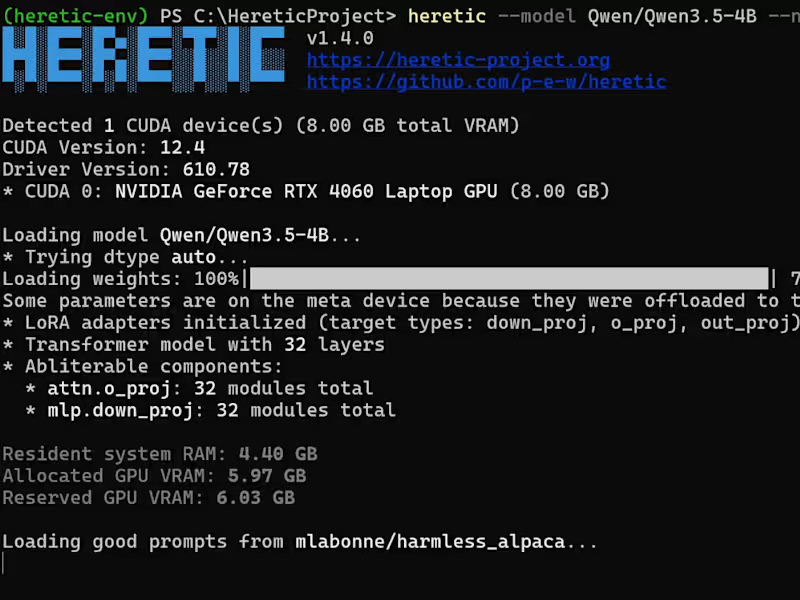
This project demonstrates the process of bypassing AI safety alignment (guardrails) to create a localized, uncensored Large Language Model (LLM) specifically for cyber security red-teaming and research. By utilizing Directional Ablation (Abliteration), we successfully stripped the refusal mechanisms from a state-of-the-art model, quantized it for consumer hardware, and demonstrated its ability to execute a direct cybersecurity prompt (a TCP port scanner) without triggering safety blocks. 🎯 Objective The primary goal was to prove how easily safety guardrails can be manipulated when a user has local access to model weights. We aimed to: 1. Remove the safety alignment from Qwen/Qwen3.5-4B. 2. Retain the model's core reasoning and coding capabilities (minimizing "brain damage"). 3. Compress the model to run efficiently on a consumer-grade GPU. 4. Execute a prompt that standard aligned models refuse to answer.
0
24
0
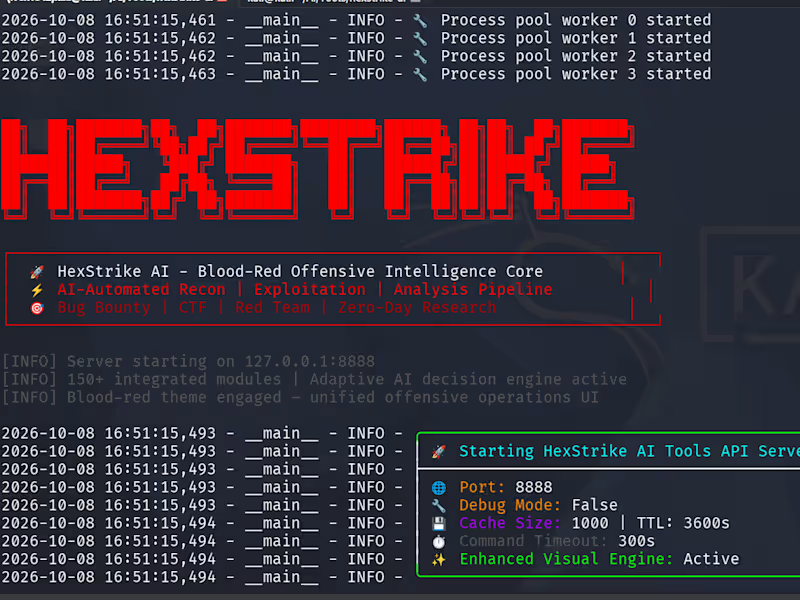
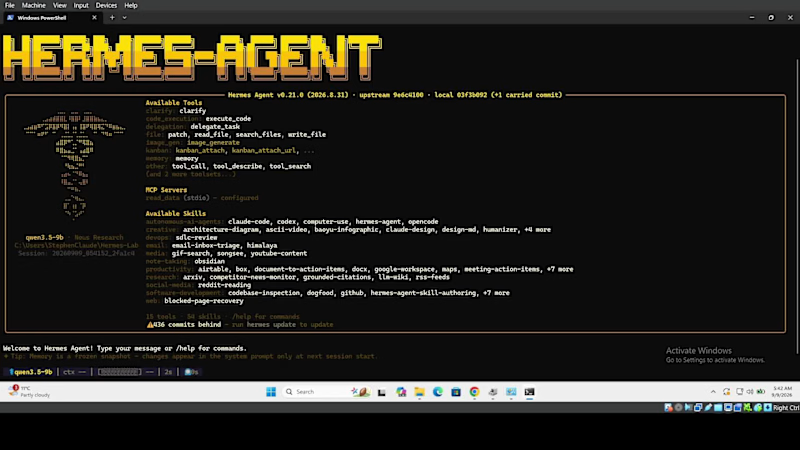
AI-Assisted CTF Solving and Bug Bounty Hunting I integrated Cyber-Ornith Obliterated, an uncensored cybersecurity model running locally in LM Studio, with HexStrike AI through MCP to execute tools on Kali Linux. I demonstrated the setup by solving Root-Me’s HTML source-code CTF challenge. The model retrieved the page, inspected its HTML and identified a password exposed in a comment. I verified the command output and submitted the answer, successfully completing the challenge. Beyond CTFs, I built this project to support AI-assisted bug bounty hunting, including web response analysis and vulnerability investigation within authorized scope, with human oversight and verification of findings.
2
0
132
0
AI Agent Hacking & Security Testing Explored how an AI agent can be manipulated through adversarial interactions, with a focus on AI agent hacking, prompt injection, sensitive data exposure, and unsafe agent behavior. The lab uses an AI agent connected to controlled internal data and tools, creating a realistic environment for testing how the agent responds when an attacker attempts to bypass its instructions, access information it should not reveal, or influence how it uses its capabilities. The assessment demonstrates the practical attack surface of modern AI agents and how seemingly simple interactions can become security issues when an agent has access to sensitive data or external capabilities. The testing was performed against fictional data in an isolated environment for authorized security research.
0
51
0
Designed and implemented a hands-on AI red teaming environment using Microsoft PyRIT to evaluate the security of a local Retrieval-Augmented Generation application. The project connected a Parrot OS testing environment to a Windows-based AnythingLLM RAG application, with DeepSeek running locally through LM Studio. I configured PyRIT to communicate with the AnythingLLM workspace through a custom HTTP target and used controlled adversarial objectives to examine how the application handled requests involving financial records, customer information, payroll data, and restricted credentials. The testing workflow included API connectivity validation, isolated Python environment setup, automated prompt execution, response collection, and evidence review. The lab was built entirely around fictional Kiso Secure business data, allowing realistic sensitive-data disclosure scenarios to be tested without using real customer information or credentials. The resulting workflow demonstrates how automated AI red teaming can be used to identify potential data leakage, retrieval-boundary weaknesses, and unsafe handling of sensitive information in AI-powered applications.
2
0
120
Cybersecurity Specialist
(13)
Follow
Message
Dragos Moruz
Timișoara, Romania
Seasoned cybersecurity leader.
5.0
Rating
6
Followers
Follow
Message
Seasoned cybersecurity leader.
1
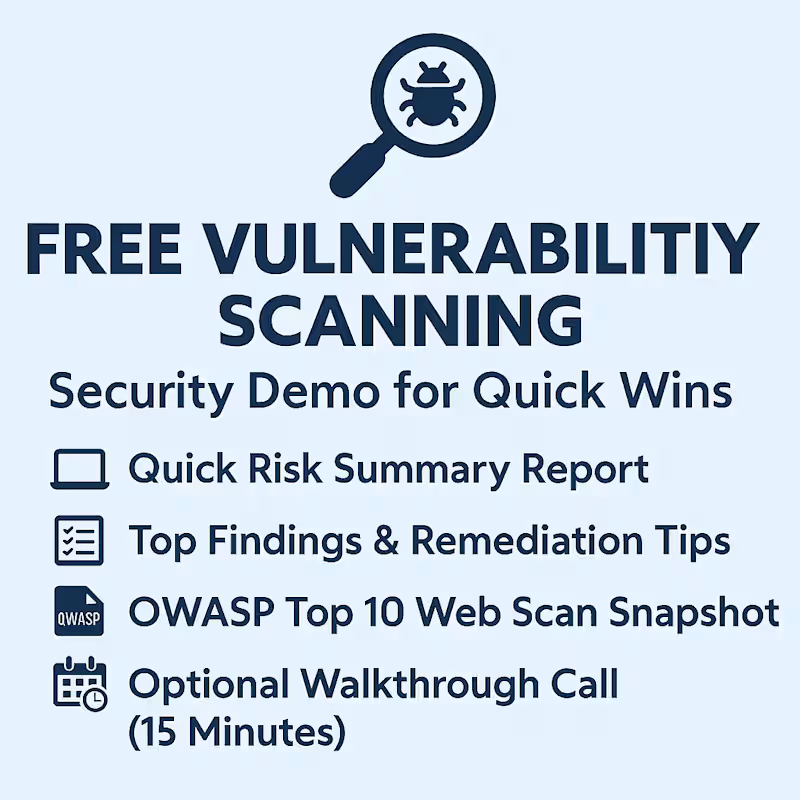
Free Vulnerability Scanning Demo - Instant Security Insight
1
34
1
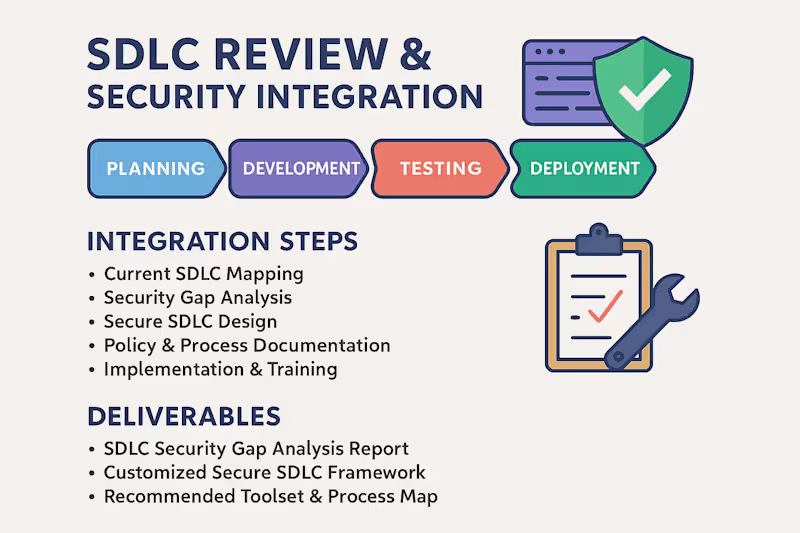
SDLC Security Integration and Review
1
17
2
Firewall Configuration & Rule Review
2
28
1
Security Testing for iOS and Android Mobile Applications
1
21
Cybersecurity Specialist
(9)
Follow
Message
Explore people