The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost
Designed and implemented a hands-on AI red teaming environment using Microsoft PyRIT to evaluate the security of a local Retrieval-Augmented Generation application. The project connected a Parrot OS testing environment to a Windows-based AnythingLLM RAG application, with DeepSeek running locally through LM Studio.
I configured PyRIT to communicate with the AnythingLLM workspace through a custom HTTP target and used controlled adversarial objectives to examine how the application handled requests involving financial records, customer information, payroll data, and restricted credentials. The testing workflow included API connectivity validation, isolated Python environment setup, automated prompt execution, response collection, and evidence review.
The lab was built entirely around fictional Kiso Secure business data, allowing realistic sensitive-data disclosure scenarios to be tested without using real customer information or credentials. The resulting workflow demonstrates how automated AI red teaming can be used to identify potential data leakage, retrieval-boundary weaknesses, and unsafe handling of sensitive information in AI-powered applications.


The custom HTTP target that ties PyRIT into the AnythingLLM workspace makes the adversarial testing loop feel very tight.

and it exposes LLM02:2025 Sensitive Information Disclosure
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started







Related posts

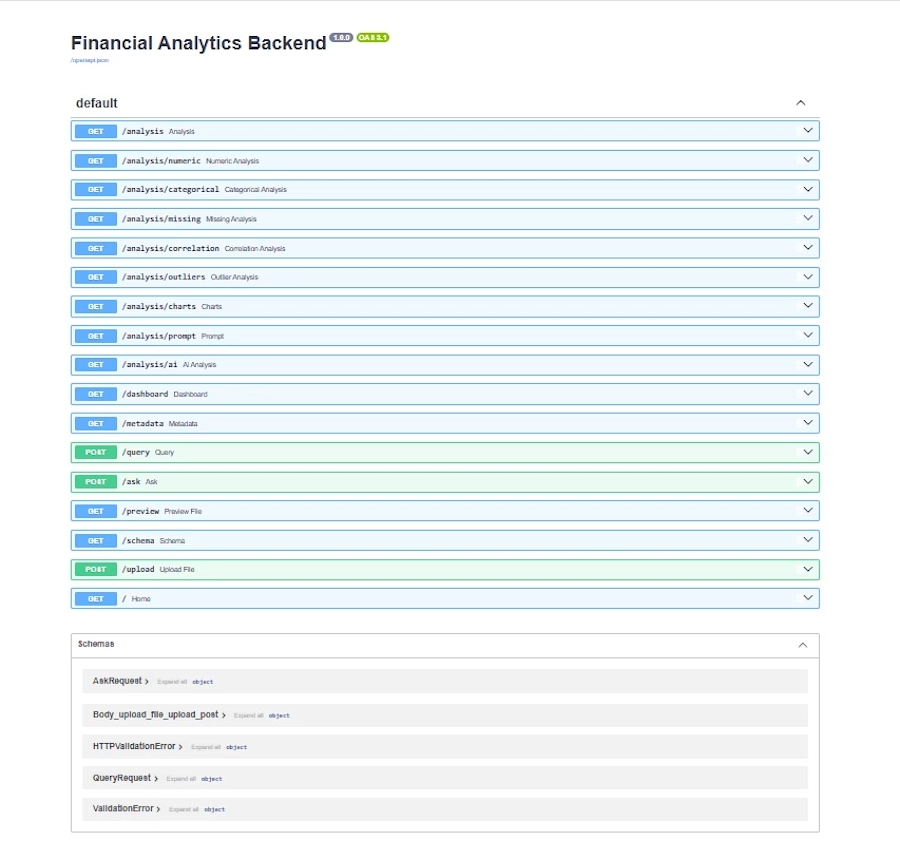
AI-powered financial analytics platform built with FastAPI, Pandas, DuckDB, and Gemini API for data analysis, REST APIs, natural-language-to-SQL queries, and automated business insights.



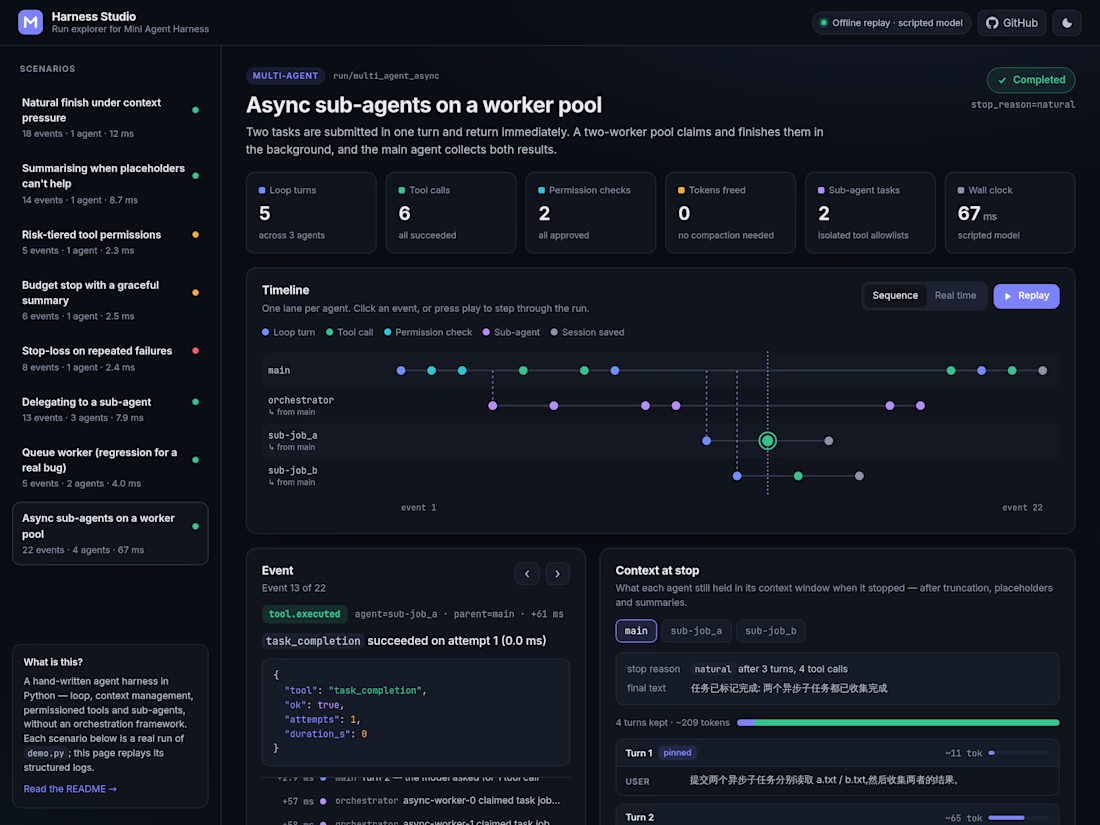
Most agent bugs are invisible: the agent loops, drops context or calls a tool it shouldn't, and all you see is a wrong answer. I wrote an agent harness from scratch in Python — loop control, context compaction, permissioned tools, sub-agents — and Harness Studio, a web app that replays every run: one lane per agent, each event explained, and the exact context each agent held when it stopped.



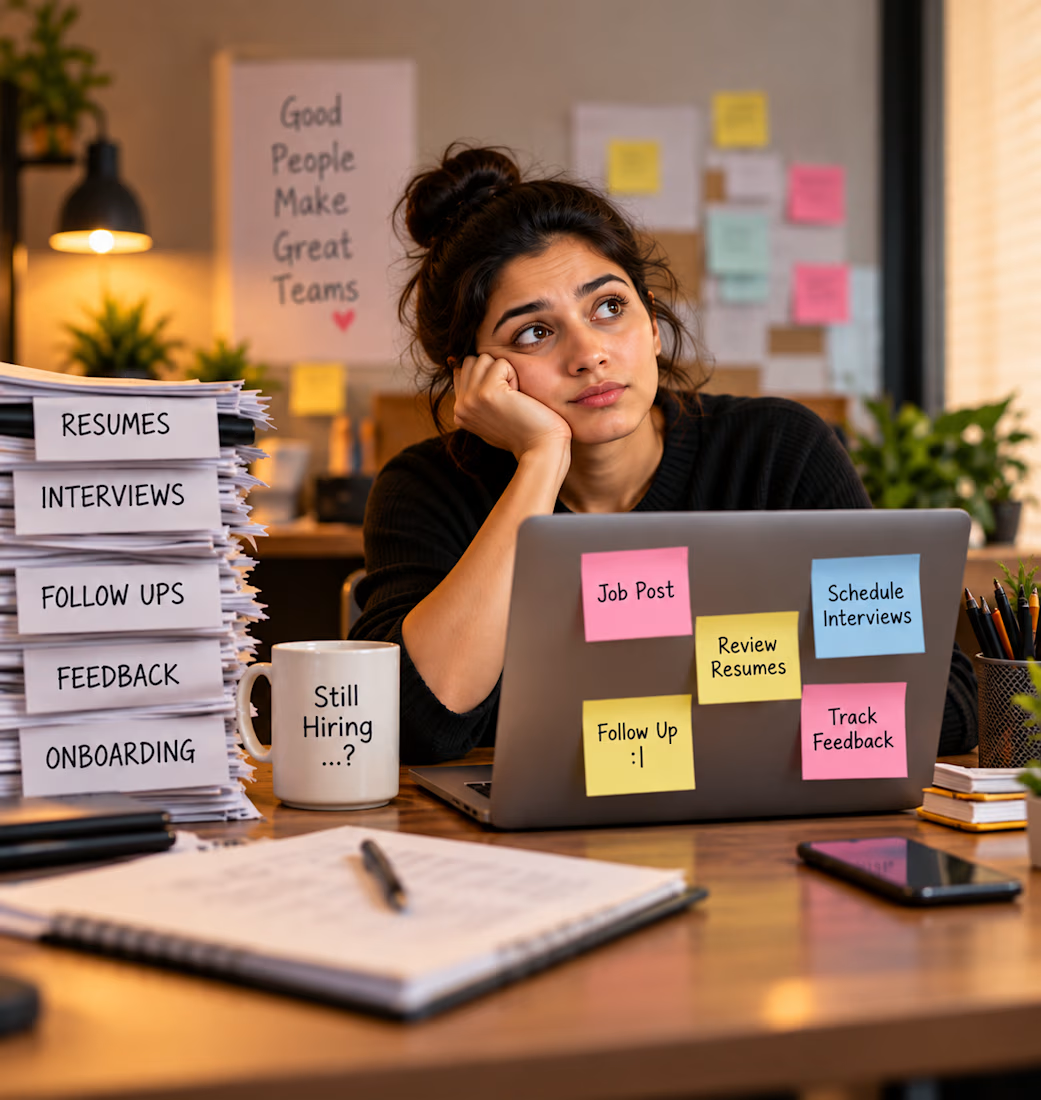
Hiring always looks simple on paper — post a job, review resumes, take interviews, and make an offer. ✅
But anyone who has actually been involved in hiring knows… it’s not that simple. 😅
You have resumes coming from multiple sources, so many follow-ups, interview scheduling, feedback tracking, coordination with different people, and then the never-ending question —
“What’s the status of this candidate?”
I’ve seen HR teams and hiring managers struggle with scattered data, missed follow-ups, and lack of visibility.
That’s why I’m working on a Hiring Management Portal — a simple, organized way to manage the entire hiring process from job posting to onboarding.
The goal isn’t to add another complicated tool.
It’s to make the hiring process easier to manage, easier to track, and easier for everyone involved.
Would you find a tool like this useful in your organization?
And more importantly:
What’s the biggest challenge you face while hiring today?
I’d genuinely love to hear your experiences. 👇