pro
Bolutife Alli
IT, Cloud & AI Automation | Social Graphics & Promo Videos
- 3
- Followers



Most small teams that ship Docker images never check them for known vulnerabilities. Here's the free check I built into my own pipeline.
On every push, a GitHub Actions job builds the image and scans it with Trivy, an open-source scanner. If it finds HIGH or CRITICAL CVEs, the...
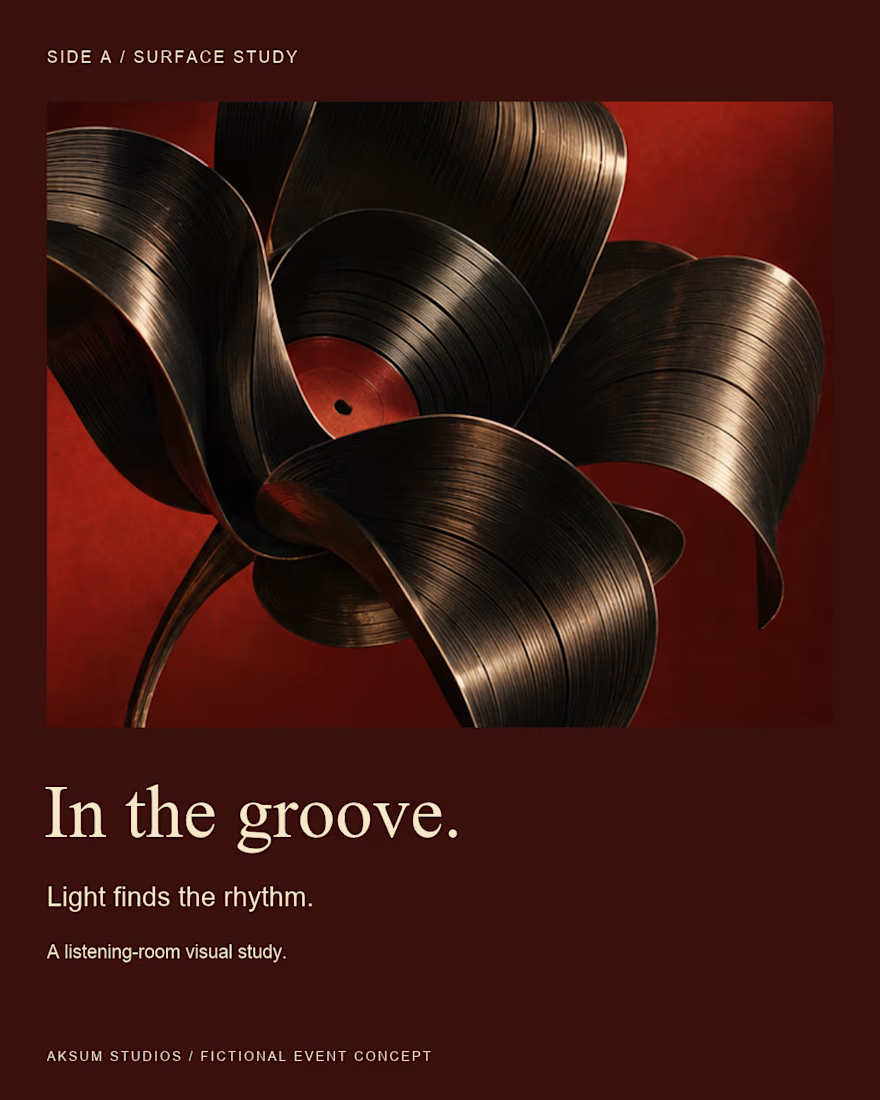
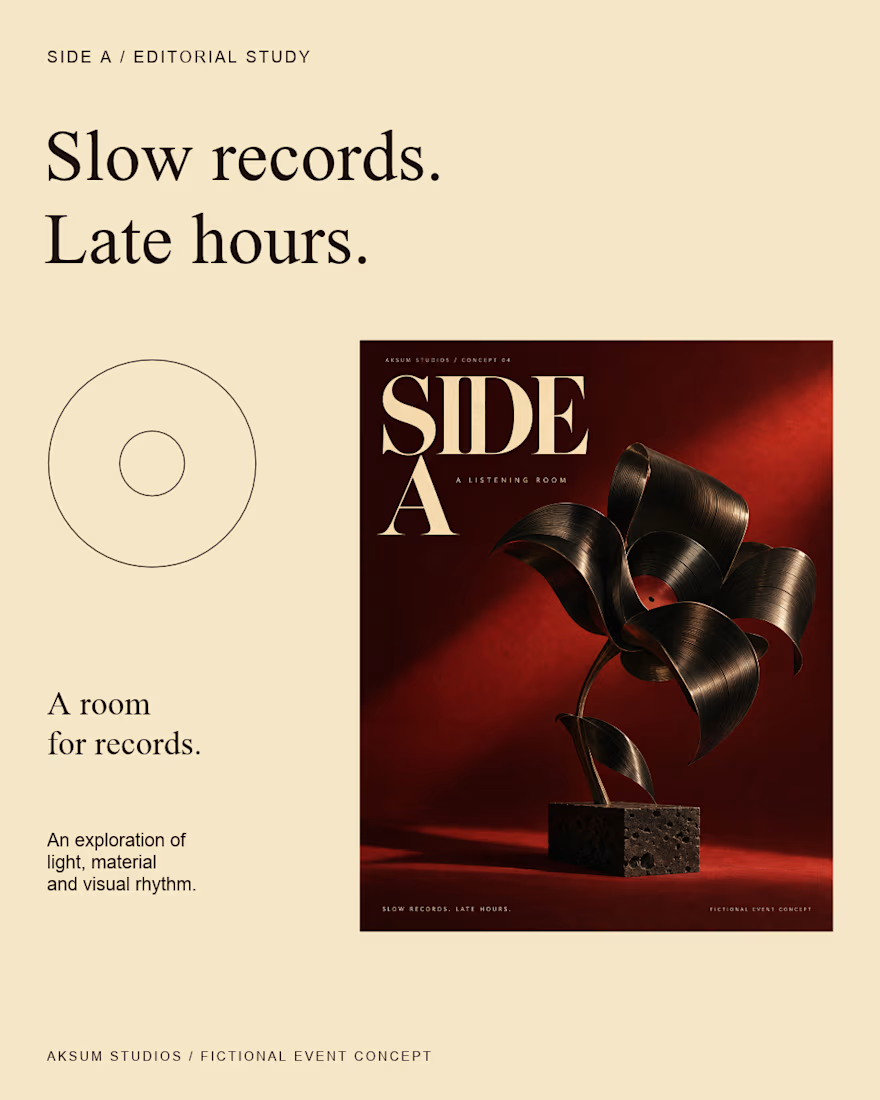
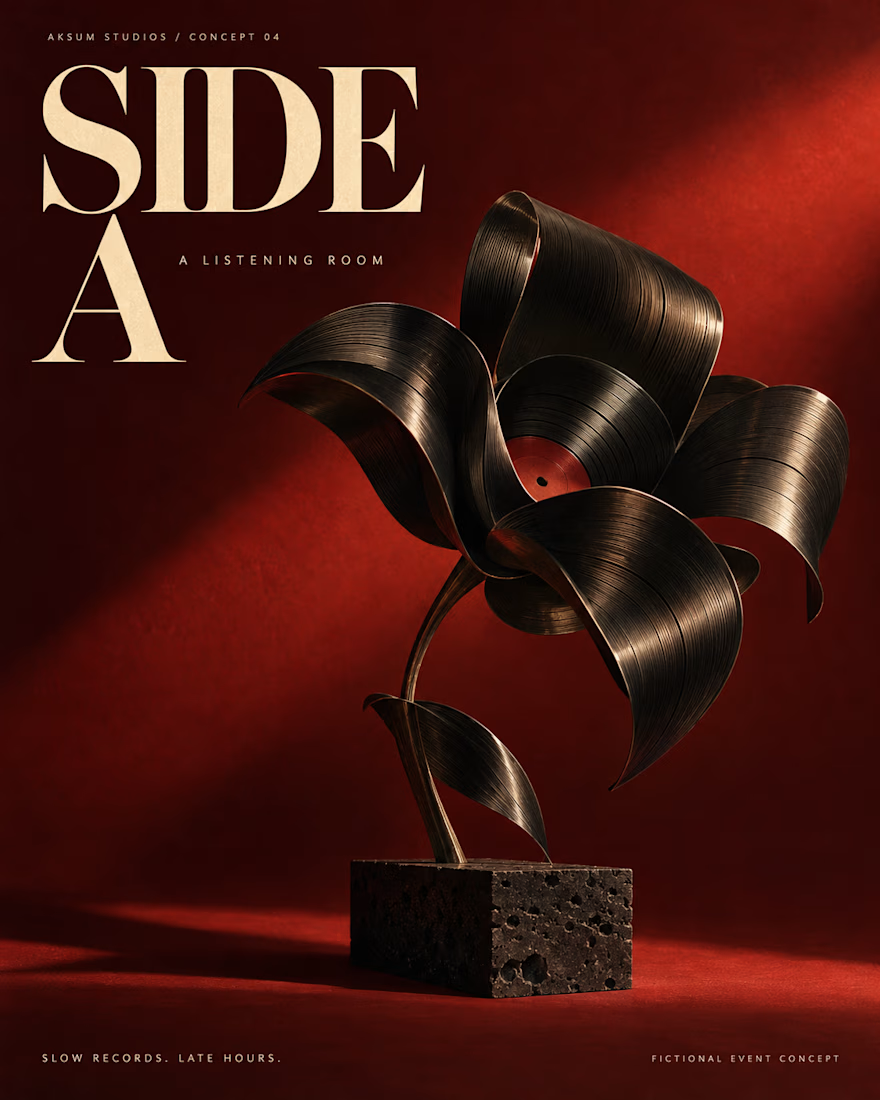
SIDE A — one visual idea, three different jobs.
For this fictional listening-room campaign, vinyl becomes a sculptural bloom. The hero establishes the mood; the close crop brings out the record grooves; the quieter editorial layout gives the typography room to breathe.
The two...
I got tired of scrolling job boards, so I built an AI agent to do the boring part of my job search.
How it works:
1. Collect - pulls new postings from job boards into a SQLite database (Node.js)
2. Screen - an LLM API reads each job against my resume and flags dealbreakers...
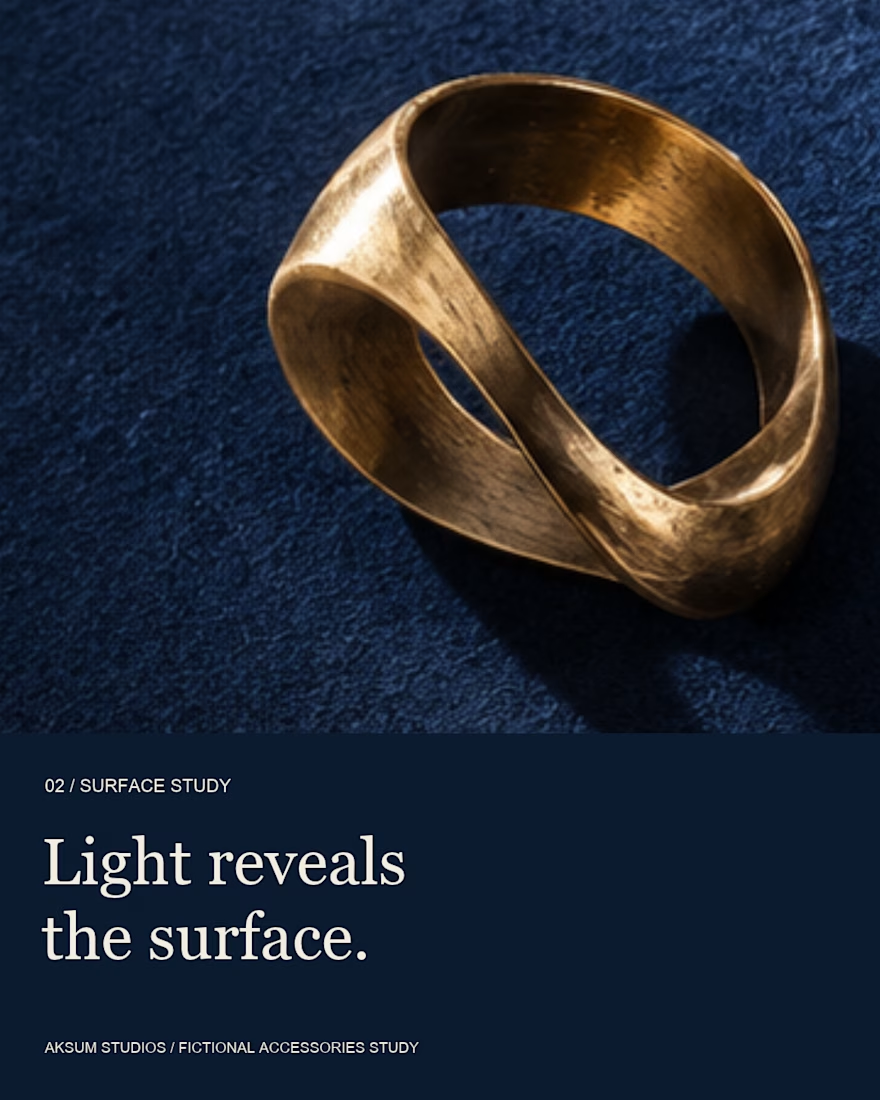
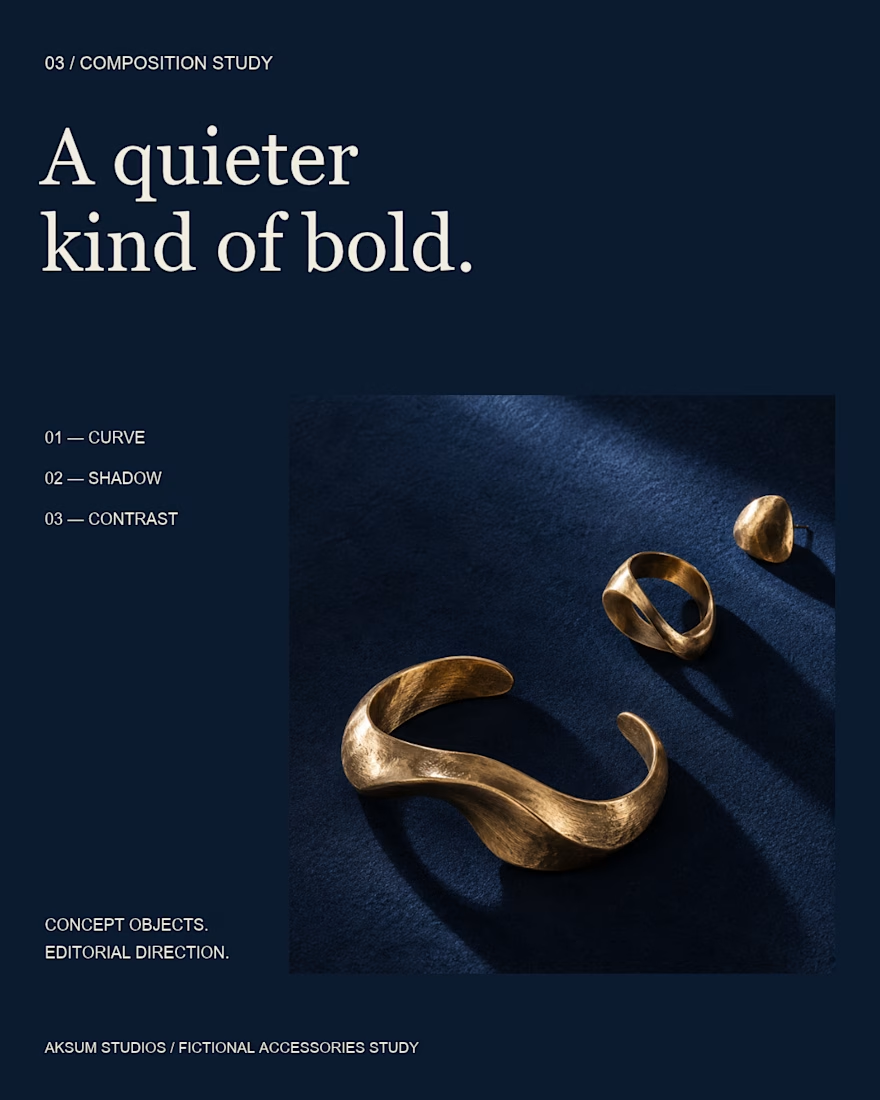
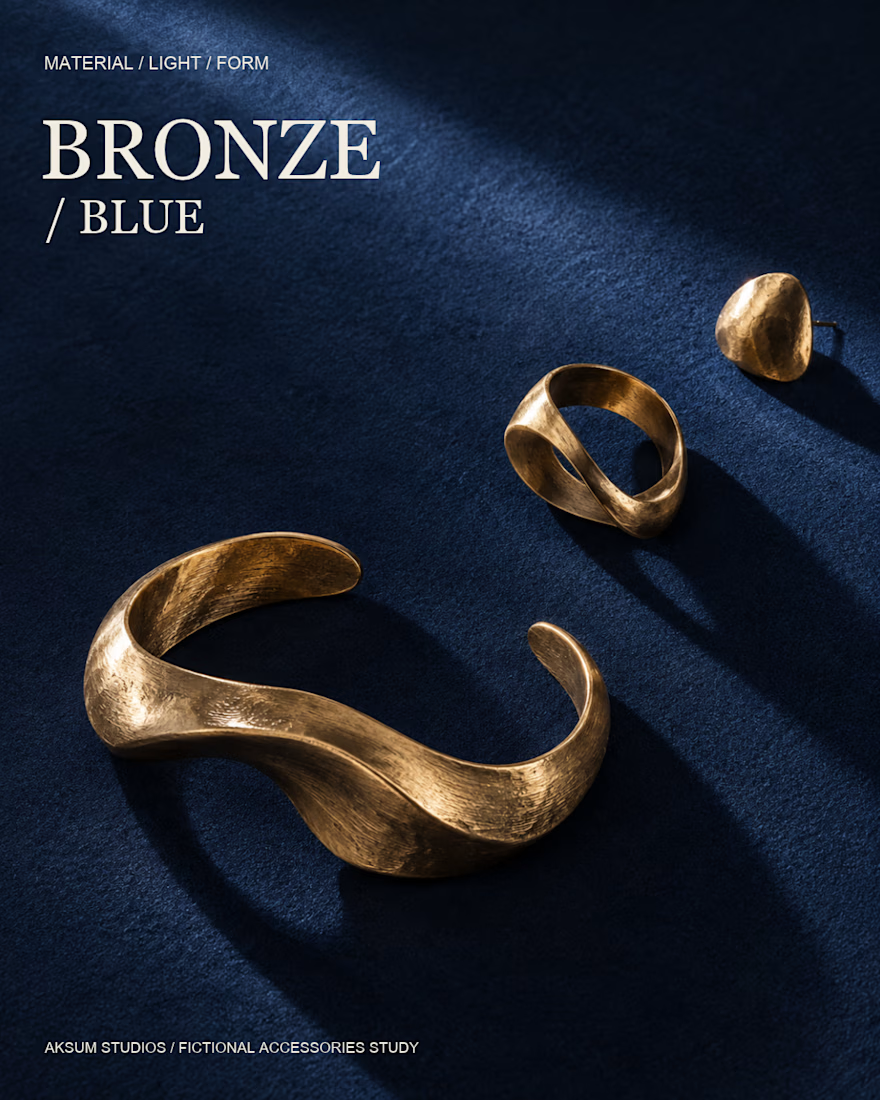
BRONZE / BLUE — one visual world, three different compositions.
For this fictional accessories study, I used warm metallic forms against deep blue texture, directional light and generous negative space. The hero introduces the collection; the close crop studies its surface; the...
Three AWS mistakes I see small businesses make in their first month, and how to avoid them.
1) Using the root account for everything. Turn on MFA for root, create named IAM users, and lock root away.
2) No billing alerts. A forgotten test server can run for months. Set an AWS...