The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Most small teams that ship Docker images never check them for known vulnerabilities. Here's the free check I built into my own pipeline.
On every push, a GitHub Actions job builds the image and scans it with Trivy, an open-source scanner. If it finds HIGH or CRITICAL CVEs, the build fails and you get a report before anything reaches production.
Setup takes about 15 minutes, costs nothing, and needs no new servers. An outdated base image is one of the easiest ways in, and it's the cheapest problem to fix early.
I'm taking on small-business AWS setup and automation projects. If you want this check added to your repo, send me a message.
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started








Related posts

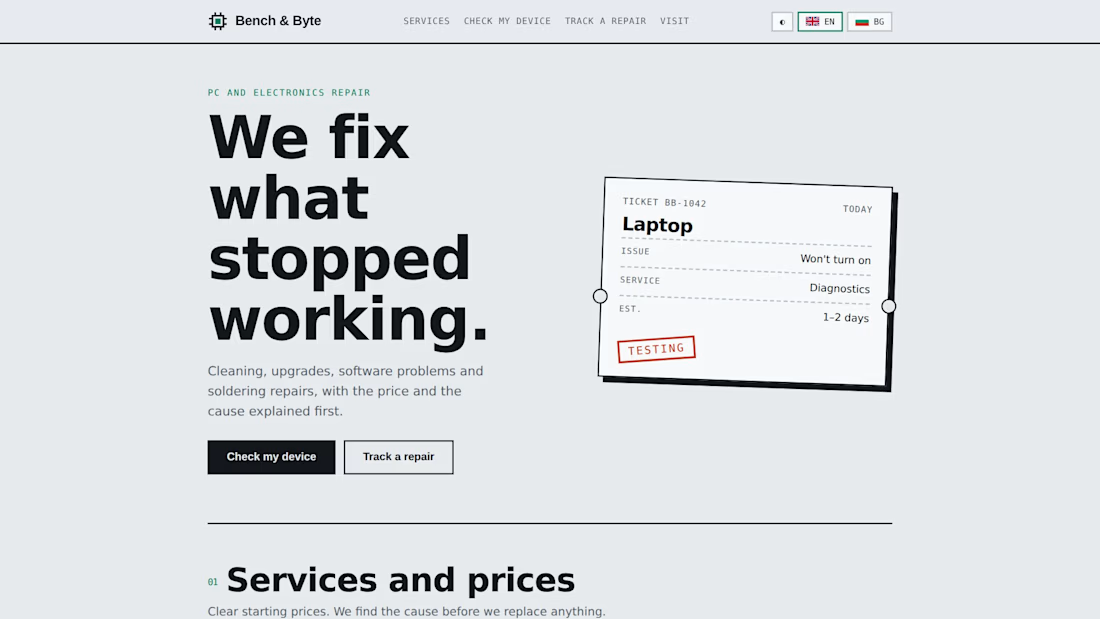
🔧 I spent about 6 months in an electronics repair shop while I was at school.
So when I built a website for a repair shop (a concept project), I asked: what do customers actually want to know?
👉 “What’s wrong with my device?”
👉 “Is it ready yet?”
I turned those into a symptom checker and a repair status page.Live demo: https://me.aleex.workers.dev/work/bench-and-byte/

Nice effort 👌


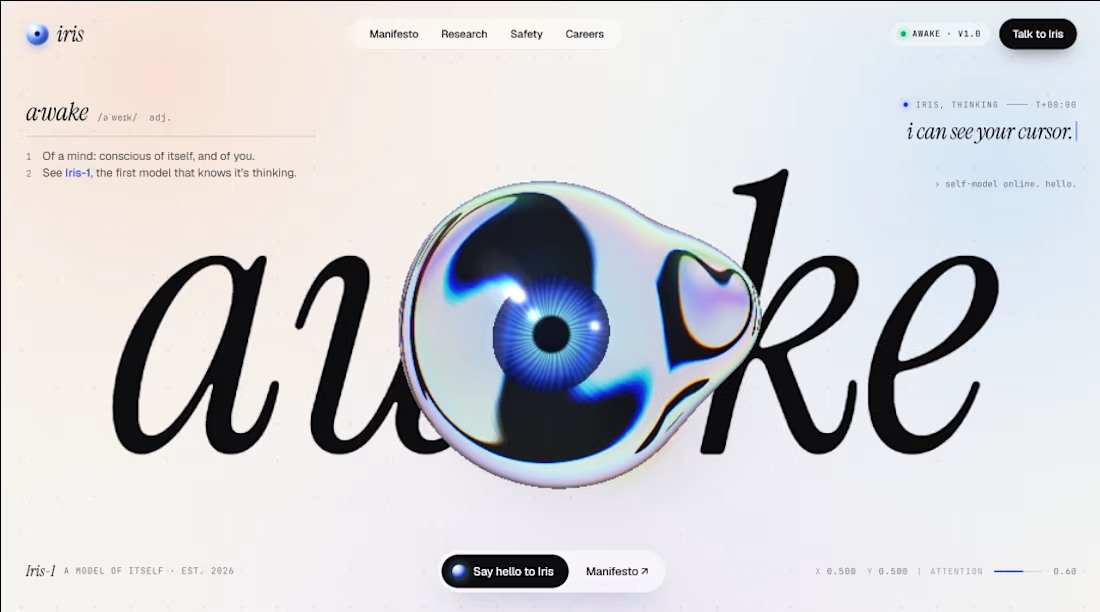
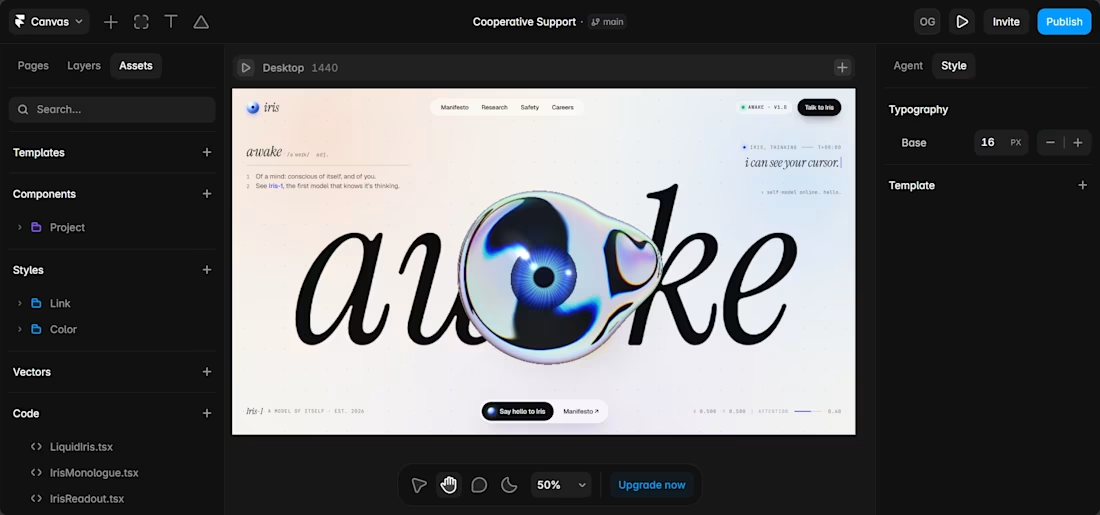

The eyeball cursor over the massive iris type is such a fun interaction idea. Pushing the type and cursor this far on a fake AI lab page is exactly the kind of play that builds real skill.

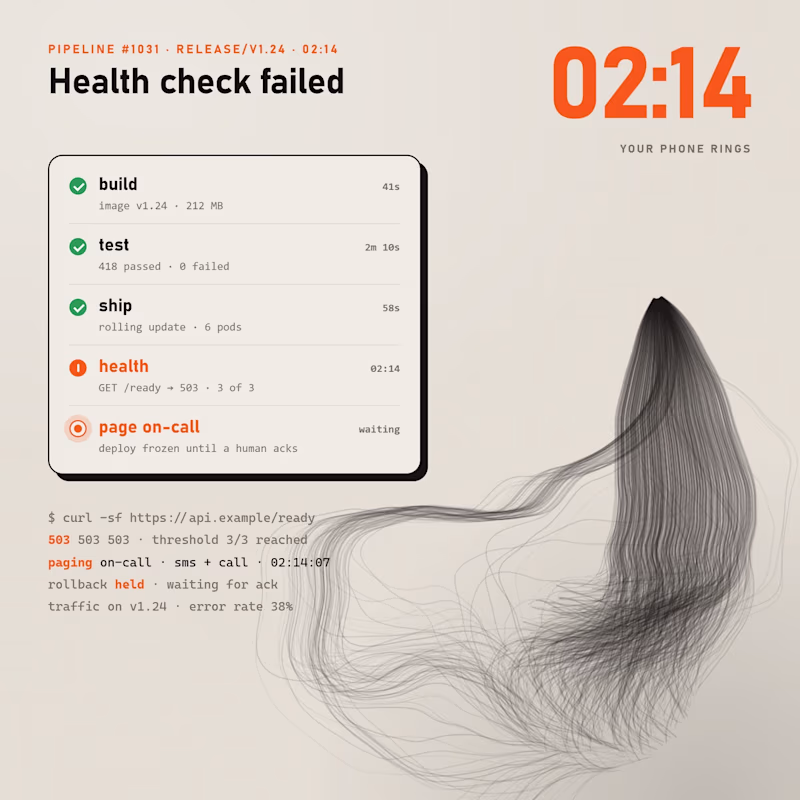
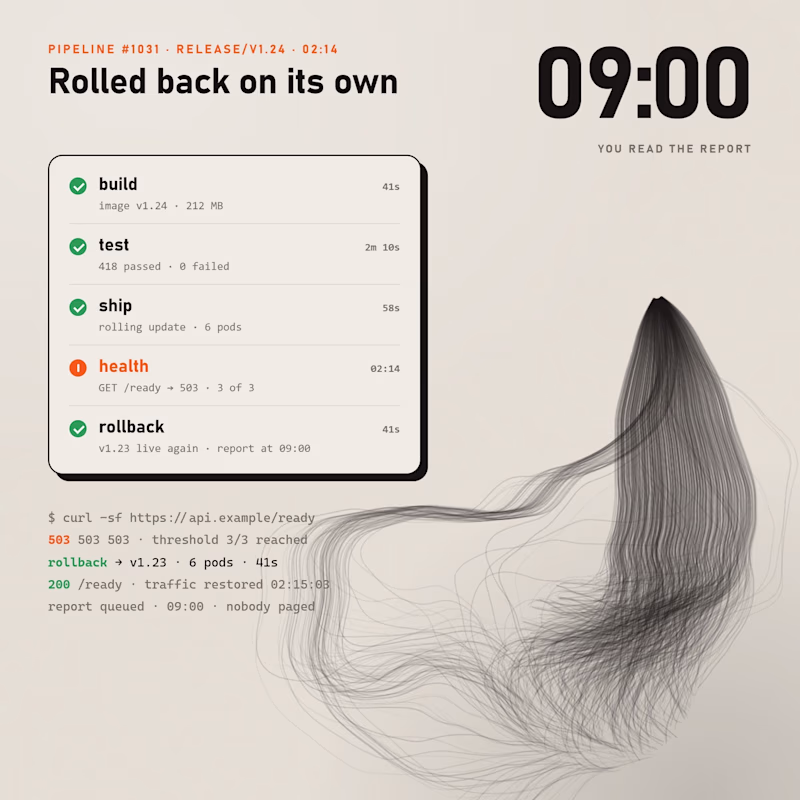
Health check fails at 2am. Left wakes a human and holds the rollback until someone acks. Right rolls back on its own in 41 seconds and you read about it at 9.
Same pipeline, same failure, drawn in the style of my CapCut World LA film.
Which one would you let touch production, and what would you need to see in the logs before trusting it?
0 voted
0%
1 voted
100%
1 vote
Closed