Freelance Security Engineers in Lahore
Sign Up
Post a job
Sign Up
Log In
Filters
2
Projects
People
Abubakar Chan
pro
Lahore, Pakistan
AI Automation Engineer | Full-Stack Apps & Integrations
66x
Hired
4.9
Rating
173
Followers
Expert
Expert
+2
Follow
Message
AI Automation Engineer | Full-Stack Apps & Integrations
1
Gut Health SaaS Platform Development
1
29
4
Provider Portal for Healthcare MSO
4
48
6
Magnai | UK Public Affairs
6
93
7
Humoni - secure housing in under 72 hours
7
155
Security Engineer
(2)
Follow
Message
Ahmed Khan
Lahore, Pakistan
Cybersecurity specialist with ability to identify flaws
Follow
Message
Cybersecurity specialist with ability to identify flaws
0
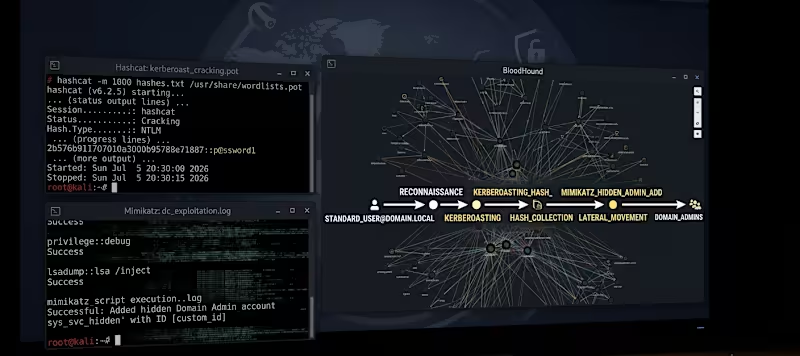
I simulated a real-world Active Directory (AD) attack to identify and exploit misconfigurations within a Windows domain environment. The goal was to practice enumeration techniques, escalate privileges to domain admin, and establish persistent access. I started with LDAP enumeration using ldapsearch to map domain users and groups. Using BloodHound, I visualized attack paths and identified a Kerberoastable service account — a weak SPN tied to an outdated service. I extracted the hash using GetUserSPNs.py (http://GetUserSPNs.py) and cracked it with Hashcat, revealing the cleartext password. I then used Pass-the-Hash to authenticate as a domain admin using PsExec. To maintain persistence, I added a domain admin backdoor account using Mimikatz. Finally, I cleared event logs to avoid detection and exported a full attack report for remediation. Tools Used: ldapsearch, BloodHound, Hashcat, GetUserSPNs.py (http://GetUserSPNs.py), PsExec, Mimikatz, eventlog (for cleanup) Deliverable: Full attack timeline with screenshots, enumeration outputs, and security recommendations.
0
34
0
I conducted a complete web application security assessment on Damn Vulnerable Web Application (DVWA) using manual and automated testing techniques. The goal was to identify and exploit OWASP Top 10 vulnerabilities. I mapped the application using Burp Suite and discovered multiple injection points. I exploited SQL Injection to bypass authentication and extract sensitive data from the database using sqlmap. I also tested for Cross-Site Scripting (XSS) with custom payloads and successfully hijacked session cookies using document.cookie injection. I chained a file upload vulnerability with a PHP reverse shell to gain remote access to the server. All findings were documented with proof-of-concept screenshots and step-by-step remediation guidance. Tools Used: Burp Suite, sqlmap, OWASP ZAP, curl, custom payloads Deliverable: A detailed report including vulnerability exploitation steps, proof-of-concept, and mitigation strategies.
0
137
0
I performed a complete network penetration test on a deliberately vulnerable Linux machine (Metasploitable2) to simulate a real-world attacker scenario. The objective was to identify exploitable services, gain initial access, escalate privileges to root, and extract sensitive data. I started with reconnaissance using nmap to discover open ports and services. I identified outdated and vulnerable services including vsftpd 2.3.4 and Samba 3.0.20. Using Metasploit, I exploited the vsftpd backdoor to gain initial shell access. I then used shell_to_meterpreter to upgrade my session to a Meterpreter shell, giving me greater control. I dumped password hashes from /etc/shadow and cracked them using John the Ripper. Finally, I escalated privileges to root using the Samba usermap_script exploit and documented the entire process with screenshots. Tools Used: nmap, Metasploit, Meterpreter, John the Ripper, searchsploit Deliverable: A comprehensive report including attack timeline, exploited CVEs, and remediation recommendations.
0
304
0
I discovered a stored cross-site scripting (XSS) vulnerability in a practice web application's comment section that allowed me to inject malicious JavaScript that would execute in any user's browser. By submitting a comment containing a script payload, I successfully stole session cookies from other users and could have hijacked their accounts, performed actions on their behalf, or defaced the website. This finding was documented in a comprehensive report including proof-of-concept screenshots showing cookie theft, CVSS risk scoring of 6.5 (Medium), and step-by-step remediation guidance including input sanitization and output encoding. This assessment demonstrates my ability to find client-side vulnerabilities that can compromise every user visiting the site.
0
88
Security Engineer
(3)
Follow
Message
Mashooque Ali
Sector X Lahore DHA, Pakistan
Expert Cybersecurity Solutions Tailored for You
Follow
Message
Expert Cybersecurity Solutions Tailored for You
0
Information Security Compliance Services
0
47
0
SOC as a Service (Security Operations Center)
0
31
0
Implementation of Information Security Management System (ISMS)
0
36
View more →
Security Engineer
(3)
Follow
Message
Ayesha Javed
Lahore, Pakistan
Where Founder Vision Is Engineered into Agentic AI Products.
53
Followers
Follow
Message
Where Founder Vision Is Engineered into Agentic AI Products.
1
Out of Harm's Way – AI-Powered Code Security MLOps System
1
11
1
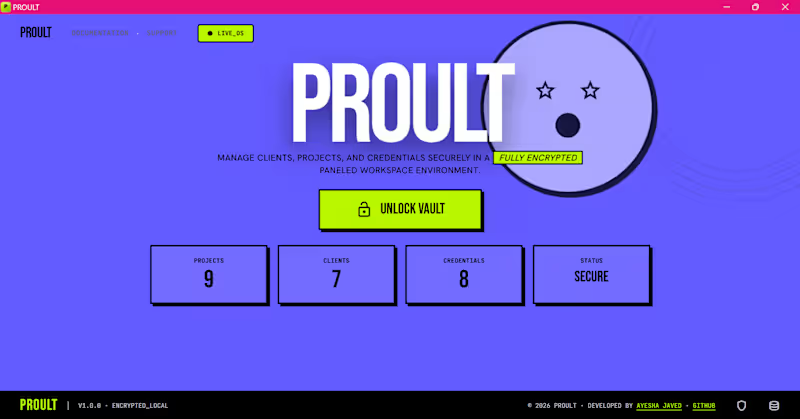
I wish I had it months ago. (Launching Proult - Desktop App) I spent 20 minutes looking for a Stripe credential. I checked my notes. My browser bookmarks. Old chats. Random text files. Not because I forgot it. Because I couldn't remember where I had saved it. That's when I realized the most dangerous phrase in a developer's workflow isn't: "I forgot." It's: "I've saved it somewhere." As freelancers, students, developers, and builders, we constantly juggle multiple projects simultaneously. And each project comes with its own ecosystem of information: • Client details • Credentials and passwords • API keys and secrets • Domains and hosting accounts • GitHub repositories • Deployment links • Meeting notes • Project requirements • Time logs and deadlines The problem isn't that we don't save this information. The problem is that we save it everywhere. -A Notepad file for credentials. -A spreadsheet for clients. -A project management tool for tasks. -Bookmarks for links. -Chat messages for "important" details. And before long, finding information takes more time than using it. After one too many "I know I saved this somewhere" moments, I decided to build something for myself. A single place where every project has its own secure workspace. Not just for storing passwords, but for managing everything related to that project: clients, credentials, API keys, notes, services, links, statuses, and time tracking. That's how "𝐏𝐫𝐨𝐮𝐥𝐭" started. So over the last few days, I've been building Proult, A local-first desktop application designed to keep everything related to a project in one place. -AES-encrypted credentials, API keys, and secrets -Project and client management -Built-in time tracking -Organization through project domains (Freelance, Personal, Organization, University) -Global search across projects, clients, credentials, and services -Full import/export support so your data always remains yours -Pinned projects, tags, notes, deployment links, and service management -Local-first architecture; no cloud dependency, everything stays under your control Still polishing it, but building it has already improved my own workflow significantly. Turns out, the best developer tools are often the ones built to solve your own frustrations first.
1
514
2
Taskail – AI-Powered Voice-to-Task Desktop App
2
20
3
AI-Powered Expense Automation Platform
3
14
Security Engineer
(1)
Follow
Message
Ali Hassan
Lahore, Pakistan
Senior Mobile & Product Developer | React Native, Expo, AI
New to Contra
Follow
Message
Senior Mobile & Product Developer | React Native, Expo, AI
0
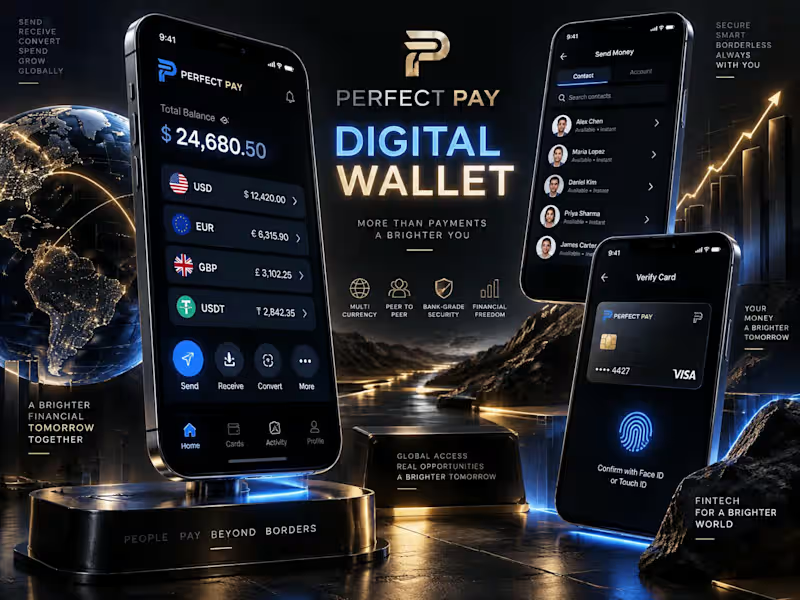
Introducing Perfect Pay 💳 — Modern multi-currency digital wallet and borderless payment app. Mobile financial products demand uncompromised security, compliance, and intuitive simplicity. Perfect Pay was engineered to remove friction from money transfers, foreign exchange, and bill payments. Users can: → Manage multi-currency balances with real-time exchange rates → Send peer-to-peer payments instantly using phone numbers or QR codes → Authenticate high-value transactions securely via FaceID / TouchID → View categorized spending analytics and automated monthly expense reports → Generate virtual debit cards for secure online shopping Behind the Scenes: Built with React Native and TypeScript under strict financial security guidelines. Implemented secure keychain token storage, biometric authentication APIs, SSL certificate pinning, and end-to-end encrypted REST communication to prevent interception. A robust, bank-grade digital wallet delivering confidence and convenience to mobile users. 🔗 iOS App: https://apps.apple.com/pk/app/myperfectpay/id6738841741 #FinTech #DigitalWallet #MobileApp #ReactNative #CyberSecurity #Biometrics #PaymentGateway #iOSDev #FinanceApp #CryptoWallet
0
19
0
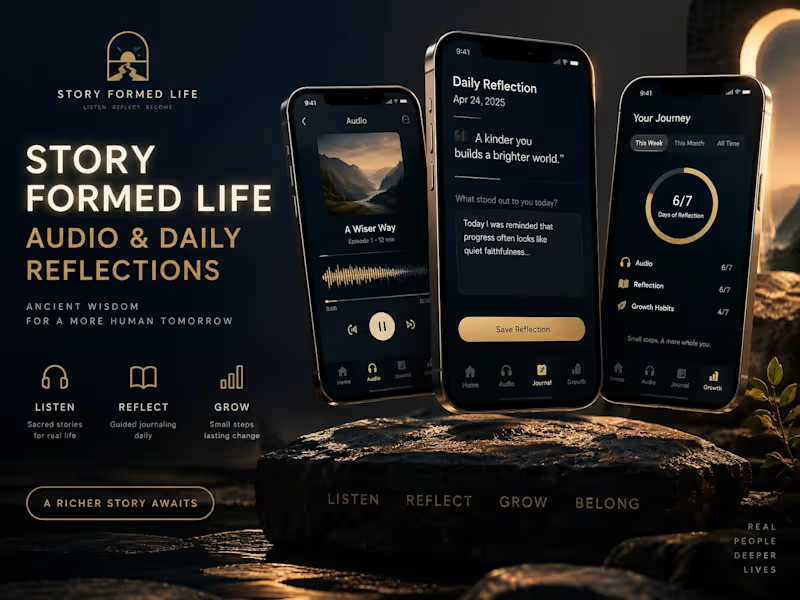
Introducing Story Formed Life 📖 — A guided daily audio reflection and community discipleship app. Building consistent daily reading and reflection habits requires a thoughtful, distraction-free digital experience. Story Formed Life was created to guide individuals and small groups through a structured 12-week life-transformation journey. Users can: → Follow structured 12-week reading paths with daily guided audio and text → Listen to narrated chapters with background playback and lockscreen audio controls → Record personal reflection notes and bookmark key passages → Participate in private cohort group discussion boards → Download complete weekly content modules for offline reflection while traveling Behind the Scenes: Engineered using React Native and Expo with custom audio streaming services. Integrated persistent local storage, progress tracking databases, and push reminders designed to foster consistent user engagement without intrusive notifications. A peaceful, community-oriented mobile sanctuary supporting thousands of daily active readers. 🔗 iOS App: https://apps.apple.com/pk/app/story-formed-life/id1513565158 #LifestyleApp #MobileApp #ReactNative #Expo #AudioStreaming #iOSDev #CommunityApp #AppStore #UIUX #HabitTracker
0
18
0
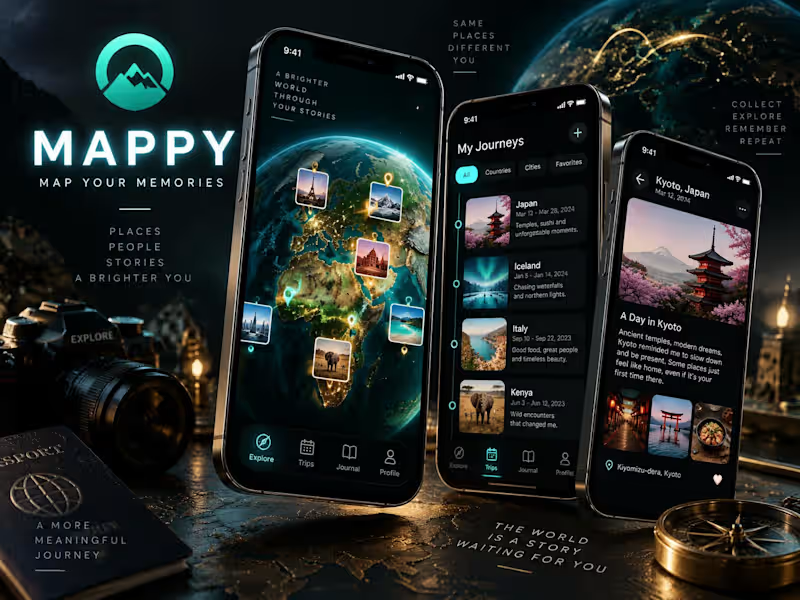
Introducing Mappy 🗺️ — An elegant visual travel journal and memory mapping mobile companion. Memories are tied to places, but standard photo galleries are organized by dates, losing geographical context. Mappy was built to let travelers and explorers pin their life stories, photo moments, and notes directly onto an interactive world map. Users can: → Pin photos, stories, and thoughts to precise GPS coordinates → Navigate an interactive 3D map with custom pin grouping and cluster zoom → Capture memories entirely offline with seamless cloud sync upon reconnect → Curate personalized trip timelines and revisit past travels geographically → Share private journey maps with friends and travel companions Behind the Scenes: Developed with React Native, TypeScript, and SQLite for an offline-first architecture. Utilized MapKit with custom cluster rendering for thousands of pins without frame drops. Implemented client-side image compression to ensure rapid cloud uploads while conserving cellular data. A tranquil, personal digital diary praised by travelers for its clean, map-centric interface. 🔗 iOS App: https://apps.apple.com/pk/app/mappy-map-your-memories/id6749023763 #TravelApp #MobileApp #ReactNative #MapKit #OfflineFirst #iOSDev #SQLite #UIUX #ProductDesign #PhotoJournal
0
22
0
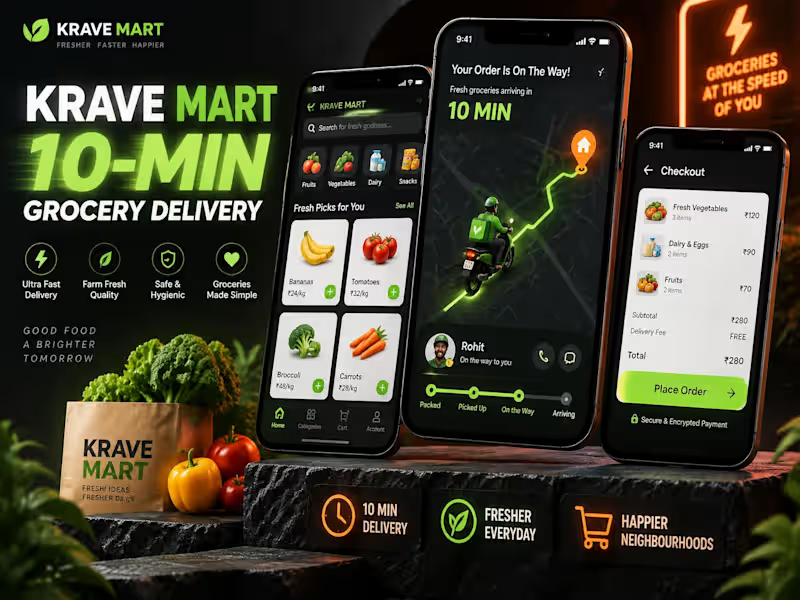
Introducing Krave Mart ⚡ — 10-minute on-demand grocery and essential quick-commerce delivery. In quick-commerce, seconds make or break the customer experience. The challenge was building an ultrafast mobile shopping and real-time dispatch interface capable of synchronizing dark-store inventory live. Customers can: → Search 3,000+ grocery essentials and add to cart in one tap → Experience real-time item substitution and instant stock availability updates → Watch riders deliver orders live on interactive maps with route calculations → Checkout seamlessly with biometric authentication and stored payment methods → Rate deliveries and access 24/7 instant customer support Behind the Scenes: Built on React Native with WebSocket connections for sub-second rider geolocation feeds. Designed high-performance cart state management that handles rapid additions, bundle discounts, and stock holds without UI lag. Delivered an ultra-reliable consumer shopping flow that powered rapid market expansion. 🔗 iOS App: https://apps.apple.com/pk/app/krave-mart/id1597746512 #QuickCommerce #MobileApp #ReactNative #RealTimeTracking #WebSockets #Logistics #iOSApp #MobileUX #ECommerce #FastDelivery
0
22
Security Engineer
(1)
Follow
Message
Asad Mahmood Asghar
Lahore, Pakistan
Senior Backend Engineer & Solution Architect
5.0
Rating
2
Followers
Follow
Message
Senior Backend Engineer & Solution Architect
0
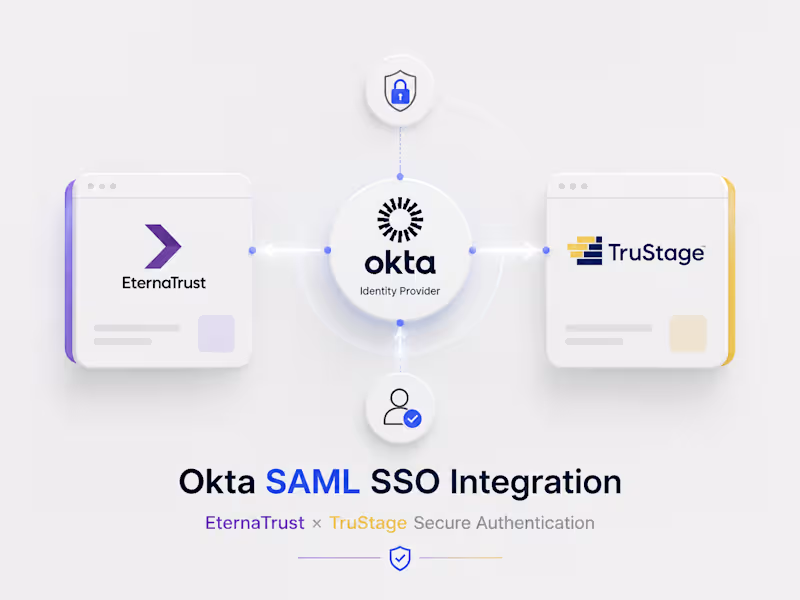
Secure Enterprise Authentication with Okta and SAML
0
2
0
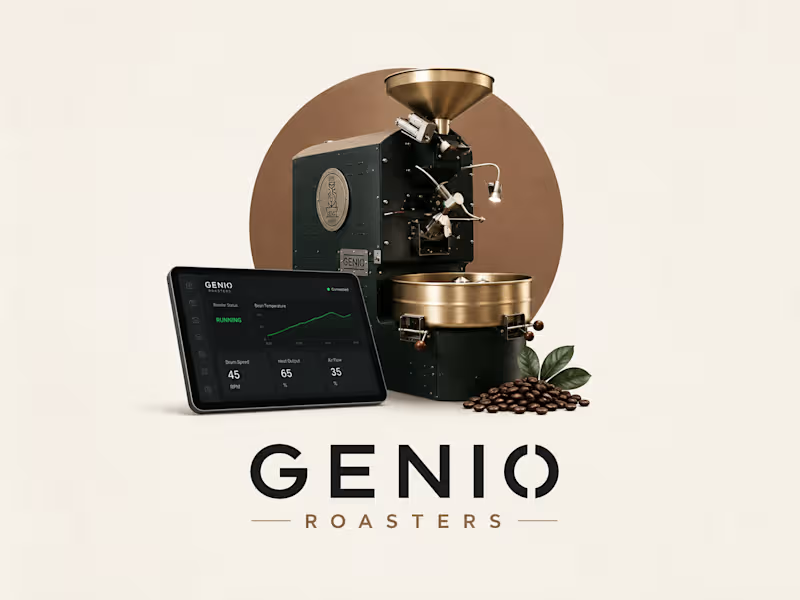
Genio Roasters - NodeRed Dashboard Design
0
33
1
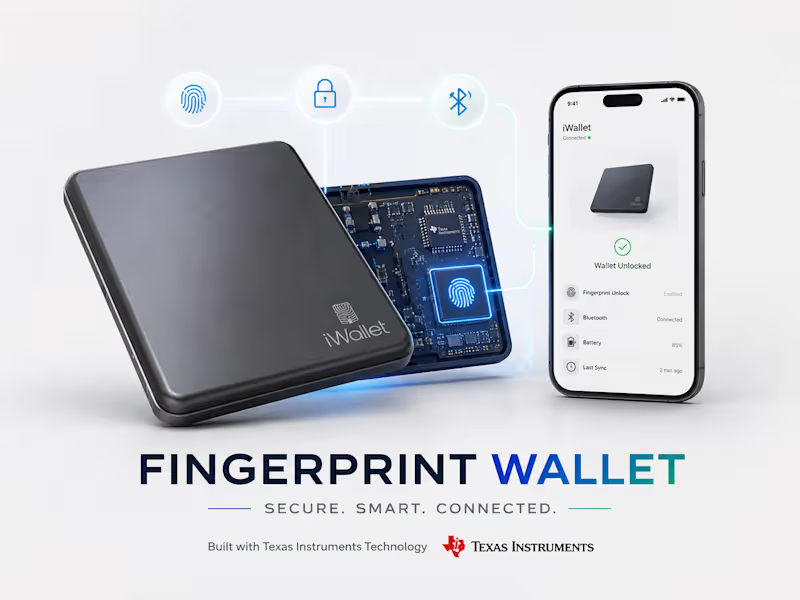
Firmware Development for Fingerprint Smart Wallet
1
3
0
Resso.ai (https://Resso.ai) - Career co-pilot for students and professionals
0
65
Security Engineer
(1)
Follow
Message
Mohsin Ishfaq
Lahore, Pakistan
Manual & Automation QA Engineer | Web, API & End-to-End Test
New to Contra
Follow
Message
Manual & Automation QA Engineer | Web, API & End-to-End Test
0
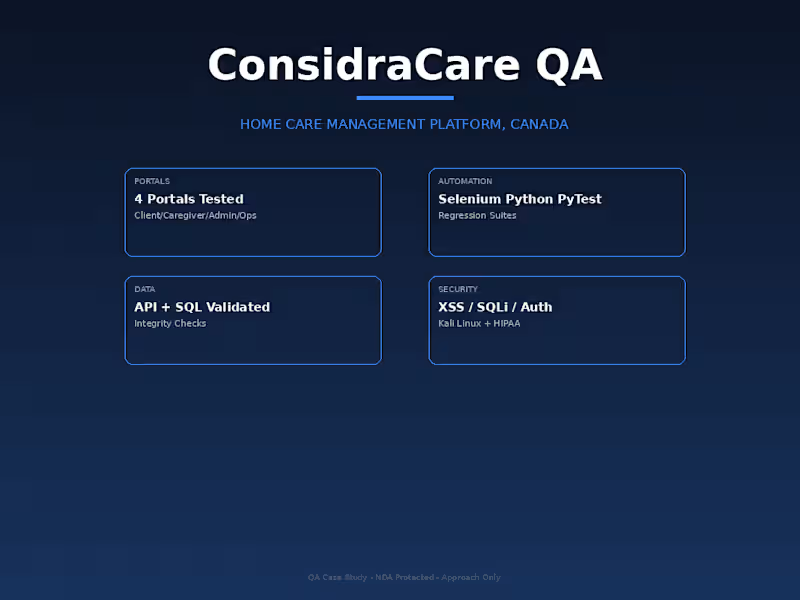
ConsidraCare – Healthcare & Home Care Management Platform QA [Canada] | Sep 2024 – May 2025 | NDA Protected - Approach Only Project Overview: Canadian home-care platform enabling agencies to manage caregivers, clients, scheduling, care plans, payroll, invoicing. 4 portals: Client, Caregiver, Admin, Operations. My Role: QA Engineer (Manual + Automation + Security) Work I Did: Independently tested all 4 portals covering complex workflows: caregiver onboarding with background checks, shift scheduling with conflict detection, care plan management (ADLs), payroll calculations with overtime rules, invoicing with insurance integration Designed and executed 150+ test cases: Functional, Regression, Smoke, Cross-portal, End-to-End Built automated regression suite from scratch using Selenium Python + PyTest - 80 test cases automated, reduced regression time from 2 days to 4 hours API Testing: Validated 30+ REST APIs using Postman - caregiver availability, shift assignment, payroll generation, client billing - checked status codes, response schema, error handling, auth Database Testing: SQL verification - validated payroll calculations match DB, schedule conflicts prevented at DB level, invoice totals, data integrity across portals Security Testing: Foundational web security using Kali Linux tools - XSS in care notes, SQL Injection in search, authentication bypass, brute-force on login, role escalation checks HIPAA-adjacent validation: Ensured caregiver can only see assigned clients, client PHI masked for unauthorized roles, audit logs for sensitive actions Bug Reporting: Logged 60+ bugs in Jira with steps, expected/actual, severity, video proof for critical. Worked with devs through fix verification Release verification: Production smoke testing before each release, preventing critical payroll bugs Impact: Reduced production bugs by 40%, regression time by 75% Tools: Selenium Python, PyTest, Postman, MySQL, Jira, Kali Linux (Burp Suite, OWASP ZAP), BrowserStack, GitHub Domain: Healthcare | Type: Web Application | NDA: No confidential screenshots or data shared - approach only
0
103
0
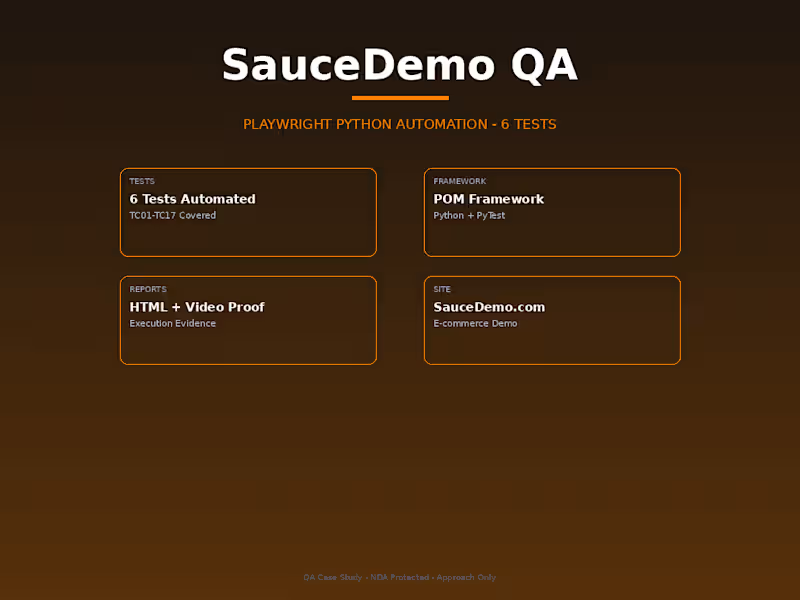
SauceDemo E2E Automation – Playwright Python + PyTest | POM Framework | 6 Tests Automated Overview: Automated https://www.saucedemo.com using Playwright Python + PyTest + Page Object Model built from scratch. Test Coverage (6 Tests): TC01 Valid login with standard_user TC03 Locked out user error validation TC09 Add single item to cart (Backpack) TC11 Remove item from products page TC15 Checkout with missing first name validation TC17 Complete happy path checkout E2E Framework: POM with login_page, products_page, cart_page, checkout_page, conftest fixtures, pytest-html reports, video recording Execution: 6/6 Passed | GitHub: https://github.com/mohsin-ishfaq/saucedemo-playwright-automation Tech: Python, Playwright Sync API, PyTest, POM
0
126
0
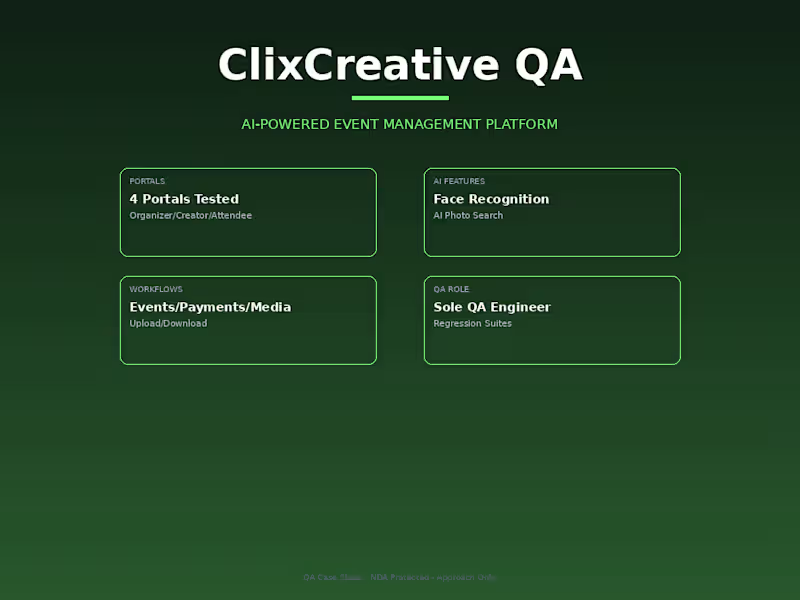
ClixCreative – AI-Powered Event Management Platform QA | Multi-Portal | NDA Protected Overview: Multi-portal platform connecting event organizers, photographers, videographers, attendees with AI face recognition for media discovery. 4 portals: Organizer, Creator, Attendee, Admin. My Role: Sole QA Engineer (handled 4 concurrent products at Analytica Data) Work I Did: Managed complete QA lifecycle independently for 4 portals AI Features: Tested face recognition accuracy - upload 100 event photos, AI groups by person, attendee searches own photos by selfie. Validated AI photo search precision/recall Event Management: Event creation, invitation, creator assignment (photo/video), schedule, budget Media Workflows: Upload 500+ photos/videos (2GB), processing, AI tagging, attendee access control, download with watermark, payment for premium downloads Payment testing: Event package pricing, creator payout, attendee purchase - Stripe integration validation RBAC: Organizer only sees own events, Creator only assigned events, Attendee only own media Built comprehensive regression suites - 120+ test cases maintained Production validation before releases Impact: Stable releases while handling 4 products in parallel, maintained high coverage regression Tools: Manual Testing, Regression, Jira, Chrome DevTools, BrowserStack Domain: Event Management + AI/Media Platform
0
87
0
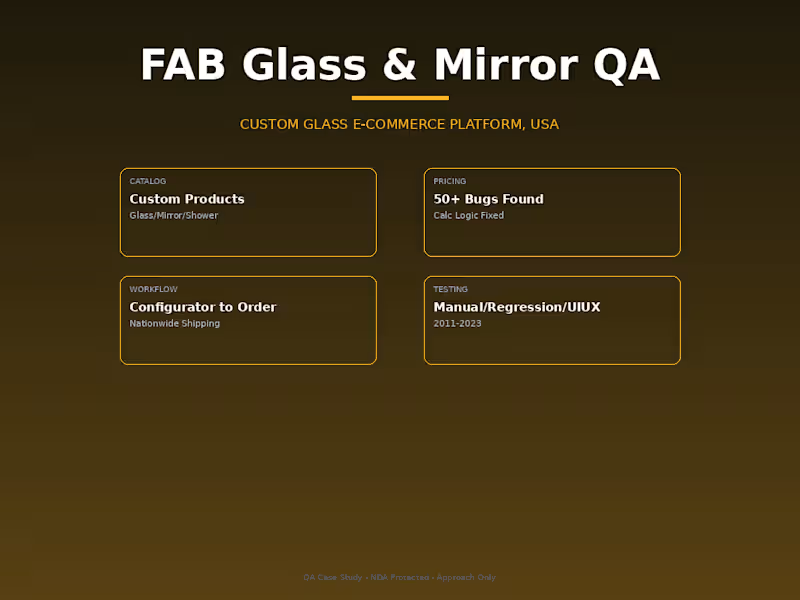
FAB Glass & Mirror – Custom Glass & Mirror E-commerce Platform QA [USA] | Feb 2022 – Dec 2023 | NDA Protected Overview: US e-commerce since 2011 - custom cut glass, tempered glass, shower doors, mirrors, table tops, railings, acrylic - nationwide shipping, hundreds of thousands customers. Work I Did: Tested complex custom quoting engine: pricing by dimensions (width/height), glass type, thickness, edgework (polished/beveled), add-ons (holes, notches) Validated measurement validation: min/max limits, aspect ratio, boundary conditions - found bug allowing 0.1 inch glass Full ordering workflow: configurator > cart > checkout (shipping calculation by size/weight) > payment > order tracking Found 50+ defects in pricing algorithms - e.g., tempered glass 0.5" pricing calculated as 0.25", shower door hinge cutout fee missing UI/UX validation: configurator usability, measurement input error messages, mobile responsiveness Regression after each release - prevented re-introduction of pricing bugs Impact: Improved pricing accuracy to 99.8%, reduced incorrect quotes by 90% Tools: Manual Testing, Regression, UI/UX Validation Domain: E-commerce Custom Manufacturing | Market: USA
0
116
Security Engineer
(1)
Follow
Message
Raza Ahmad
Lahore, Pakistan
Google Workspace Certified Admin | Email Migration Expert
New to Contra
Follow
Message
Google Workspace Certified Admin | Email Migration Expert
0
Deleted Domain from Client's Google Workspace
0
70
0
Wordpress Manual Site Tranfer With Big Database files
0
65
0
Helped Client with Wordpress Migration
0
68
0
Clients Google Workspace Complete Setup
0
70
Security Engineer
(1)
Follow
Message
Explore people