The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

I conducted a complete web application security assessment on Damn Vulnerable Web Application (DVWA) using manual and automated testing techniques. The goal was to identify and exploit OWASP Top 10 vulnerabilities.
I mapped the application using Burp Suite and discovered multiple injection points. I exploited SQL Injection to bypass authentication and extract sensitive data from the database using sqlmap. I also tested for Cross-Site Scripting (XSS) with custom payloads and successfully hijacked session cookies using document.cookie injection. I chained a file upload vulnerability with a PHP reverse shell to gain remote access to the server. All findings were documented with proof-of-concept screenshots and step-by-step remediation guidance.
Tools Used: Burp Suite, sqlmap, OWASP ZAP, curl, custom payloads
Deliverable: A detailed report including vulnerability exploitation steps, proof-of-concept, and mitigation strategies.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started



Related posts


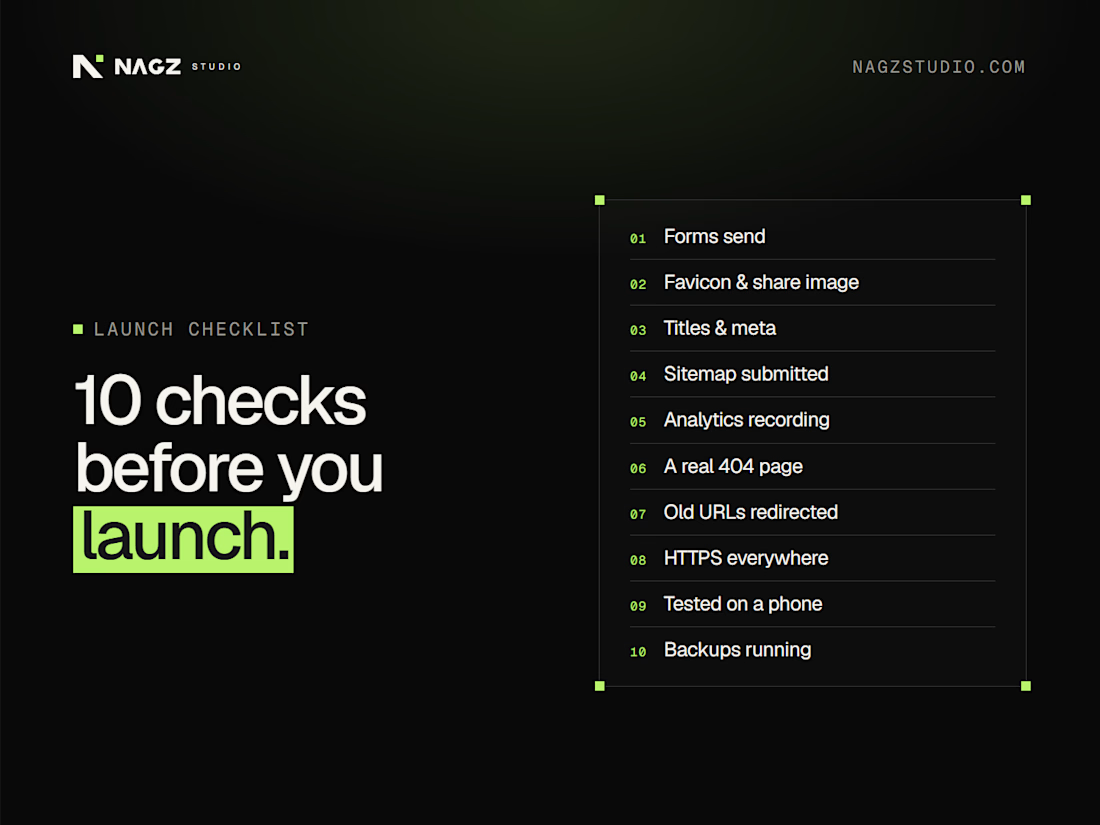
10 checks before you launch
Launching a site this week? Run through these first:
Every form sends, and you receive the email
Favicon and social share image are set
Page titles and meta descriptions are written
The sitemap is submitted in Google Search Console
Analytics is recording visits
A 404 page exists and links back home
Old URLs redirect to their new pages
HTTPS everywhere, with no mixed-content warnings
Tested on a real phone, not just a narrow browser window
Backups are running
Save this for your next launch. Which one gets forgotten most? My vote: number 7.
#WebsiteLaunch #LaunchChecklist #WebDevelopment #Startup #WebsiteTips

Such a handy launch checklist.


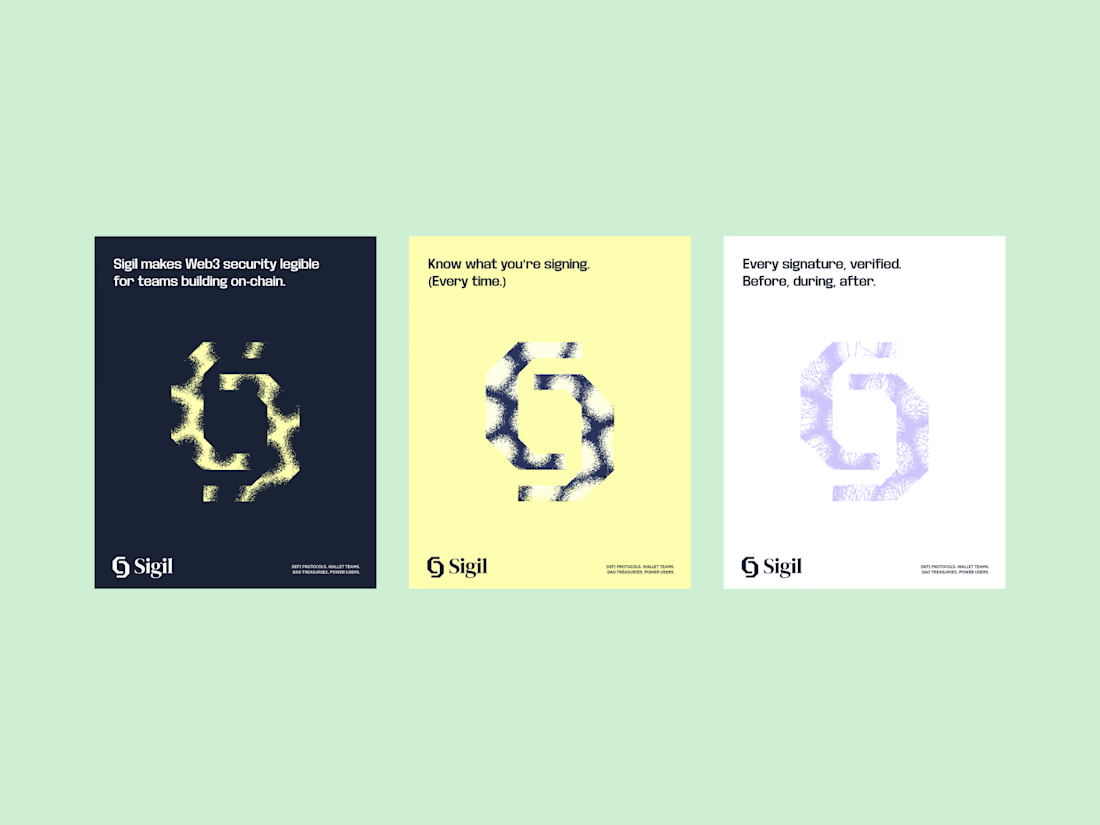

Really nice use of color and texture in this! Great job!

Why relying on public CAs for internal infrastructure is an operational time bomb: The case for your own private Root and Sub-CA.
How many times has your engineering team been paged at 3:00 AM because an internal TLS certificate expired, taking down database connection pools, internal APIs, or background workers?
When securing internal networks, teams usually fall into one of three traps:
1. The Self-Signed Disaster: Generating ad-hoc self-signed certificates and scattering them across servers. Developers end up adding --insecure or insecure_skip_verify: true to application code, completely gutting transport security.
2. The Public ACME Workaround: Trying to use Let's Encrypt on non-routable internal hostnames (like .internal or RFC 1918 IPs). This requires leaking internal network topology to public DNS or storing sensitive DNS API credentials on every internal host.
3. The Spreadsheet Calendar: Tracking certificate expiration on calendar reminders until an un-tracked intermediate cert inevitably lapses.
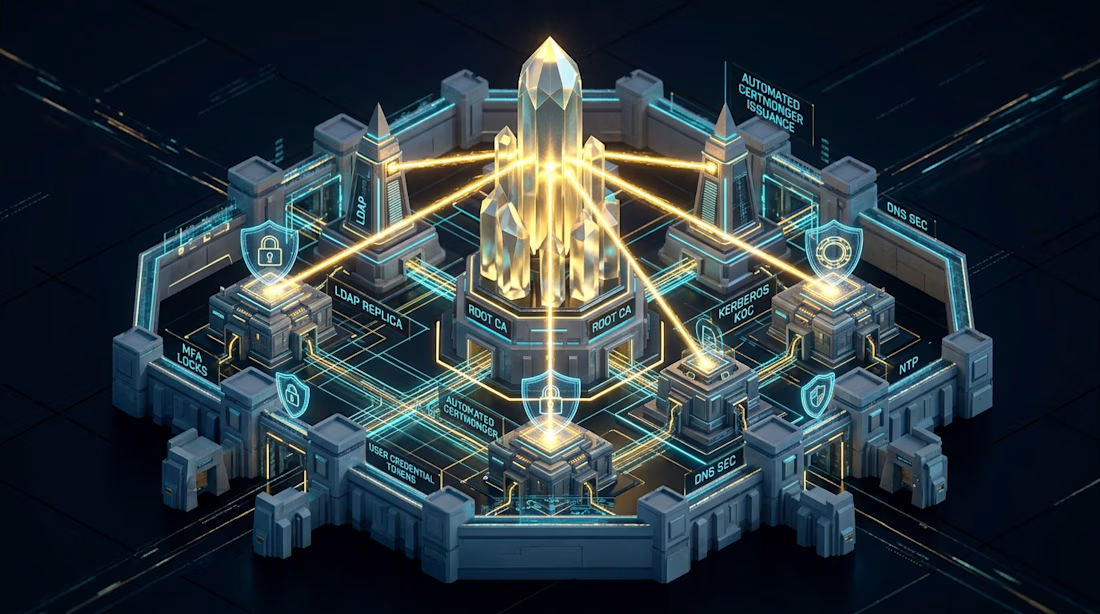
Enterprise sovereign infrastructure solves this permanently with a dedicated, multi-tier Private Public Key Infrastructure (PKI):
• Offline Enterprise Root CA: An ultra-secure, isolated trust anchor that signs only subordinate issuing authorities and never touches online network traffic.
• High-Availability Subordinate Issuing CAs (Sub-CAs): Domain-level issuing authorities (Dogtag PKI/FreeIPA) handling day-to-day certificate issuance.
• Zero-Touch Automated Renewal: Using certmonger on Linux hosts to continuously monitor certificate lifecycles, automatically re-requesting certificates 30 days prior to expiration and reloading daemons hitlessly.
• Mutual TLS (mTLS) Enforcement: Cryptographic workload identity verifying both server and client authenticity across internal database listeners, microservices, and admin interfaces.
Stop debugging expired certificates during outages. Deploy an automated private PKI foundation.
Deploy your sovereign PKI with our 2-week Enterprise FreeIPA HA & Centralized PKI/CA Sprint on Contra:
#Security #CyberSecurity #Cryptography #Infrastructure #Linux #DevOps #SRE #Architecture