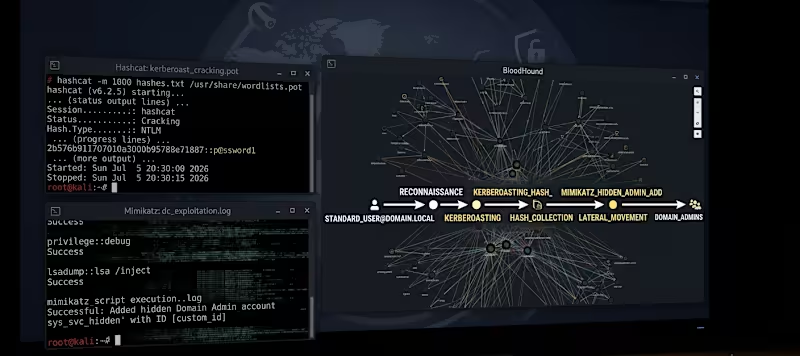
Security Engineering Projects in Lahore DHASecurity Engineering Projects in Lahore DHAI simulated a real-world Active Directory (AD) attack to identify and exploit misconfigurations within a Windows domain environment. The goal was to practice enumeration techniques, escalate privileges to domain admin, and establish persistent access.
I started with LDAP enumeration using ldapsearch to map domain users and groups. Using BloodHound, I visualized attack paths and identified a Kerberoastable service account — a weak SPN tied to an outdated service. I extracted the hash using GetUserSPNs.py (http://GetUserSPNs.py) and cracked it with Hashcat, revealing the cleartext password. I then used Pass-the-Hash to authenticate as a domain admin using PsExec. To maintain persistence, I added a domain admin backdoor account using Mimikatz. Finally, I cleared event logs to avoid detection and exported a full attack report for remediation.
Tools Used: ldapsearch, BloodHound, Hashcat, GetUserSPNs.py (http://GetUserSPNs.py), PsExec, Mimikatz, eventlog (for cleanup)
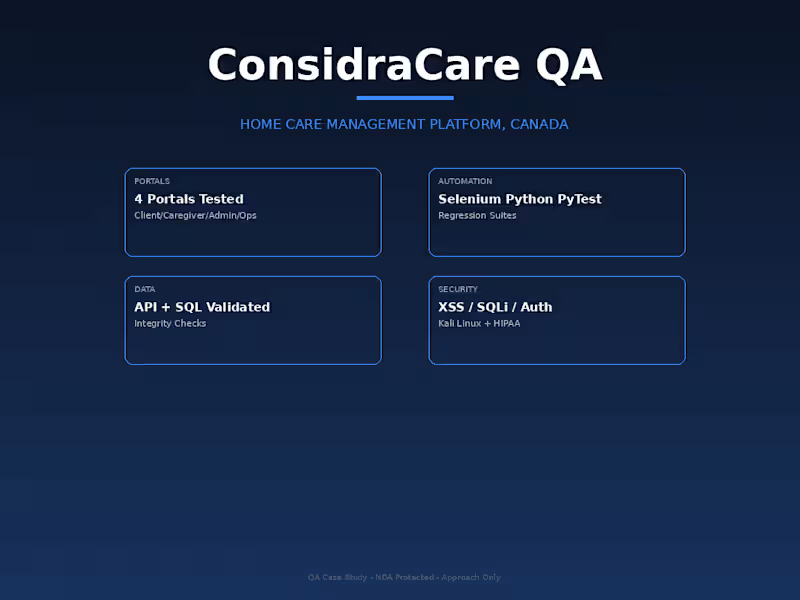
Deliverable: Full attack timeline with screenshots, enumeration outputs, and security recommendations. ConsidraCare – Healthcare & Home Care Management Platform QA [Canada] | Sep 2024 – May 2025 | NDA Protected - Approach Only
Project Overview:
Canadian home-care platform enabling agencies to manage caregivers, clients, scheduling, care plans, payroll, invoicing. 4 portals: Client, Caregiver, Admin, Operations.
My Role: QA Engineer (Manual + Automation + Security)
Work I Did:
Independently tested all 4 portals covering complex workflows: caregiver onboarding with background checks, shift scheduling with conflict detection, care plan management (ADLs), payroll calculations with overtime rules, invoicing with insurance integration
Designed and executed 150+ test cases: Functional, Regression, Smoke, Cross-portal, End-to-End
Built automated regression suite from scratch using Selenium Python + PyTest - 80 test cases automated, reduced regression time from 2 days to 4 hours
API Testing: Validated 30+ REST APIs using Postman - caregiver availability, shift assignment, payroll generation, client billing - checked status codes, response schema, error handling, auth
Database Testing: SQL verification - validated payroll calculations match DB, schedule conflicts prevented at DB level, invoice totals, data integrity across portals
Security Testing: Foundational web security using Kali Linux tools - XSS in care notes, SQL Injection in search, authentication bypass, brute-force on login, role escalation checks
HIPAA-adjacent validation: Ensured caregiver can only see assigned clients, client PHI masked for unauthorized roles, audit logs for sensitive actions
Bug Reporting: Logged 60+ bugs in Jira with steps, expected/actual, severity, video proof for critical. Worked with devs through fix verification
Release verification: Production smoke testing before each release, preventing critical payroll bugs
Impact: Reduced production bugs by 40%, regression time by 75%
Tools: Selenium Python, PyTest, Postman, MySQL, Jira, Kali Linux (Burp Suite, OWASP ZAP), BrowserStack, GitHub
Domain: Healthcare | Type: Web Application | NDA: No confidential screenshots or data shared - approach only I performed a complete network penetration test on a deliberately vulnerable Linux machine (Metasploitable2) to simulate a real-world attacker scenario. The objective was to identify exploitable services, gain initial access, escalate privileges to root, and extract sensitive data.
I started with reconnaissance using nmap to discover open ports and services. I identified outdated and vulnerable services including vsftpd 2.3.4 and Samba 3.0.20. Using Metasploit, I exploited the vsftpd backdoor to gain initial shell access. I then used shell_to_meterpreter to upgrade my session to a Meterpreter shell, giving me greater control. I dumped password hashes from /etc/shadow and cracked them using John the Ripper. Finally, I escalated privileges to root using the Samba usermap_script exploit and documented the entire process with screenshots.
Tools Used: nmap, Metasploit, Meterpreter, John the Ripper, searchsploit
Deliverable: A comprehensive report including attack timeline, exploited CVEs, and remediation recommendations.