The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Built a complete enterprise-grade SOC environment from scratch: featuring Wazuh SIEM with custom detection rules, Security Onion with Suricata IDS/IPS and Zeek network monitoring, Active Directory with advanced security logging via Group Policy, and Windows Server with Sysmon telemetry. Designed and executed MITRE ATT&CK-aligned attack simulations from Kali Linux and validated detection coverage through red team exercises. Achieved over 95% detection rate across all tested techniques and tactics. This project served as the foundation for understanding how detection engineering decisions translate into real gaps and how to close them.


Is this the finish design? Are you going to take this design and step it up? It's too A.I. looking.
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts

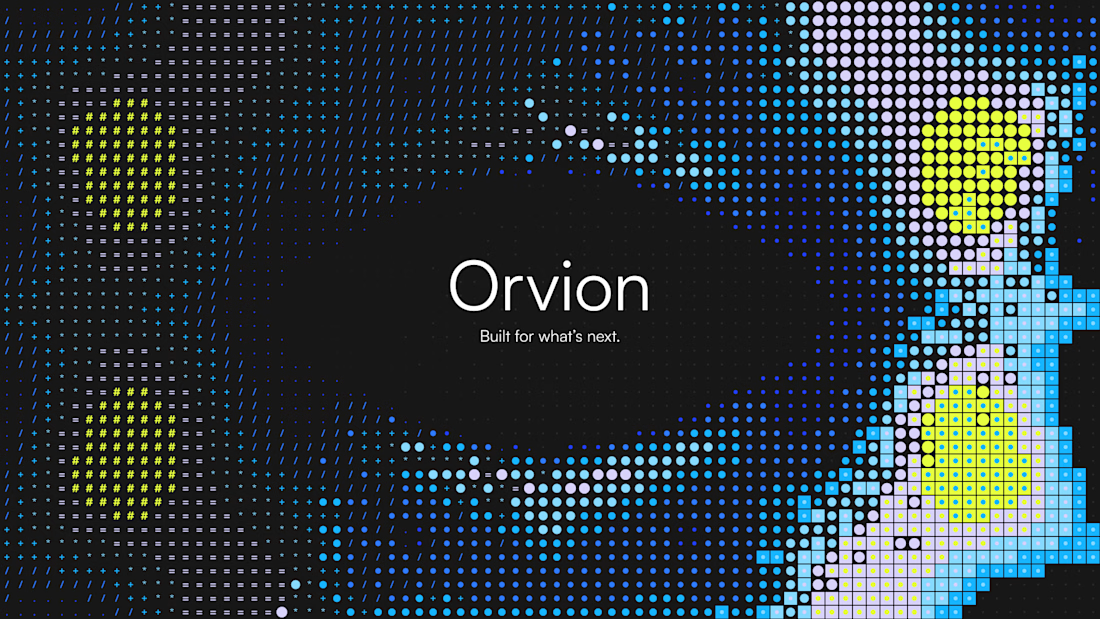
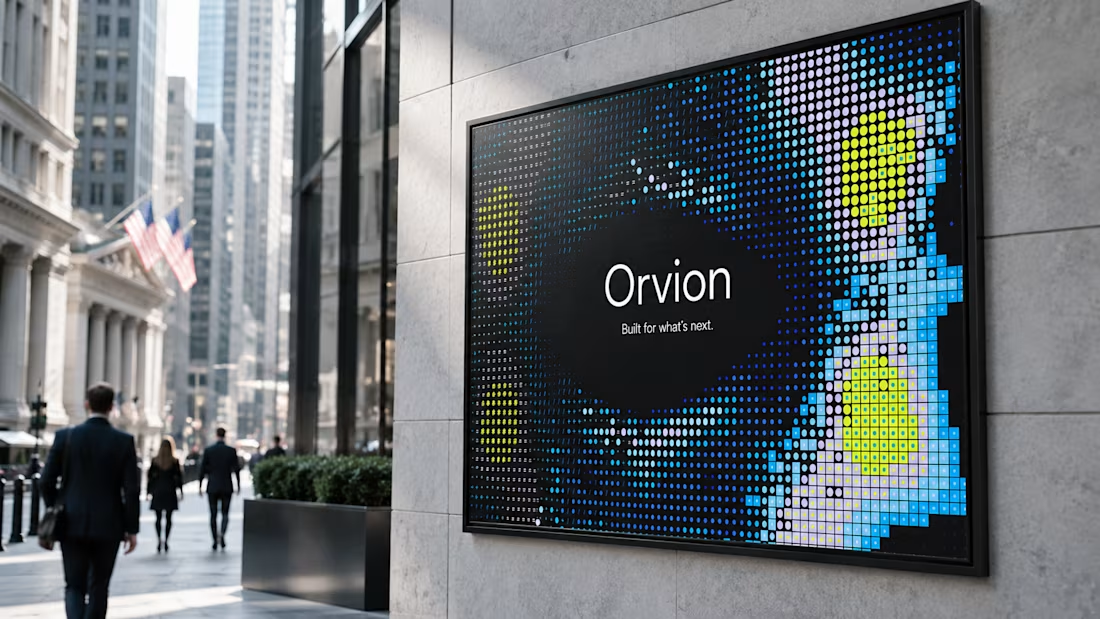

Very clean design

Hero section exproration: Glacier, a compliance platform for SaaS teams.
The brief: security should feel calm, not stressful.
A still lake and one peak carry the calm. Technical type carries the precision. A halftone texture ties them together.

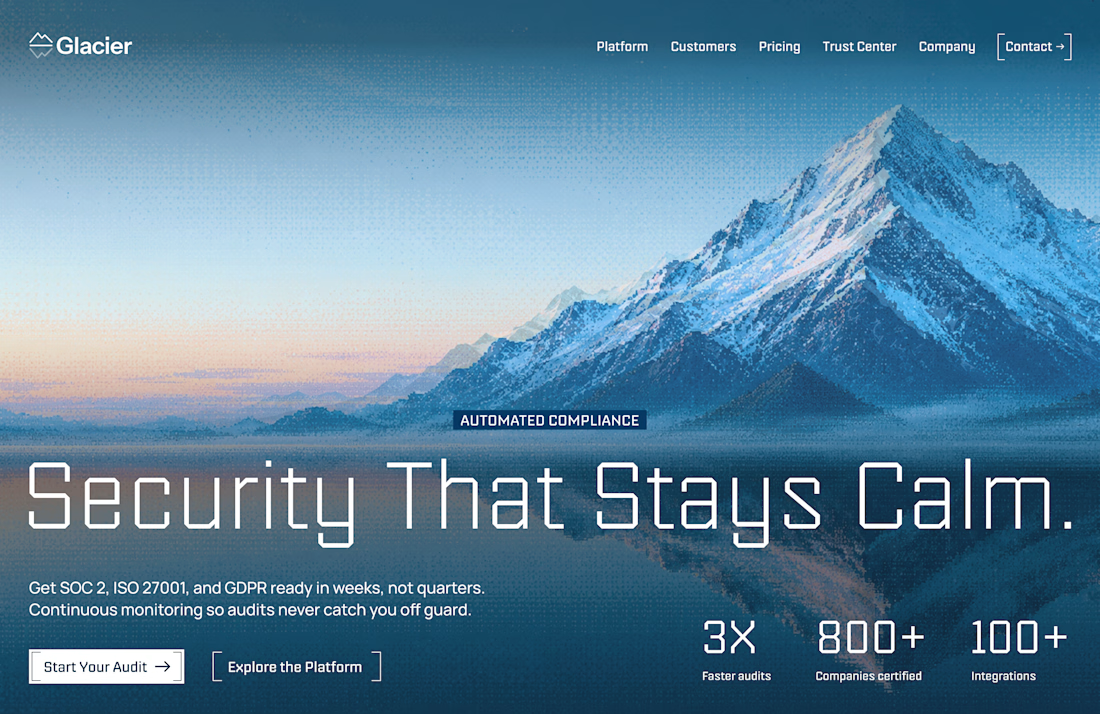

The hero is too calm. like the direction

Why your 10-person engineering team probably doesn't need Kubernetes: The power of rootless Podman and systemd Quadlets.
The modern tech industry has convinced early-stage founders and engineering teams that to run containerized web services, they must deploy a multi-node Kubernetes cluster.
Here is what happens in practice: You spin up managed Kubernetes (EKS, GKE, or AKS). You immediately burn $300–$800/month just on control plane fees and worker nodes before your first customer signs up. Then comes the operational tax: 35% of node memory is consumed by ingress controllers, CNI overlay networks, and daemonsets. Your developers spend more time debugging Helm charts and ingress routing bugs than writing business features.
On the opposite extreme, teams deploy unmanaged Docker engines running as root, using fragile ``docker-compose`` scripts that fail to restart cleanly after host reboots.
There is a battle-tested, high-performance sweet spot: **Rootless Podman managed natively by systemd Quadlets**.
• Native Linux Supervision: Declarative ``.container`` and ``.network`` Quadlet files let systemd supervise your containers natively. You get automated restarts, dependency ordering, watchdog probes, and structured journald logging out of the box. • Zero Control Plane Overhead: No etcd consensus cluster, no heavy daemon eating RAM. If your containers need 2GB of memory, they use 2GB—not 8GB. • Rootless Security by Default: Containers run inside unprivileged user namespaces with strict SELinux volume isolation (``:z``/``:Z``). Even if an attacker breaks out of the container process, they possess zero root privileges on the underlying host. • Instant Portability: Standard OCI container images. If you ever genuinely scale to the point where multi-datacenter orchestration is necessary, your containers migrate cleanly.
Stop paying a 40% complexity tax for infrastructure you don't need.
Harden your container platform with our 2-week Hardened Linux & Container Infrastructure Sprint on Contra: https://contra.com/s/Xbg7ALqN-hardened-linux-and-container-infrastructure
#Docker #Kubernetes #Infrastructure #Architecture #Linux #DevOps #SRE #Performance



Podman + Quadlets is such an underrated story for small teams — you get container workflows without paying the operational tax of k8s before you have a k8s problem.