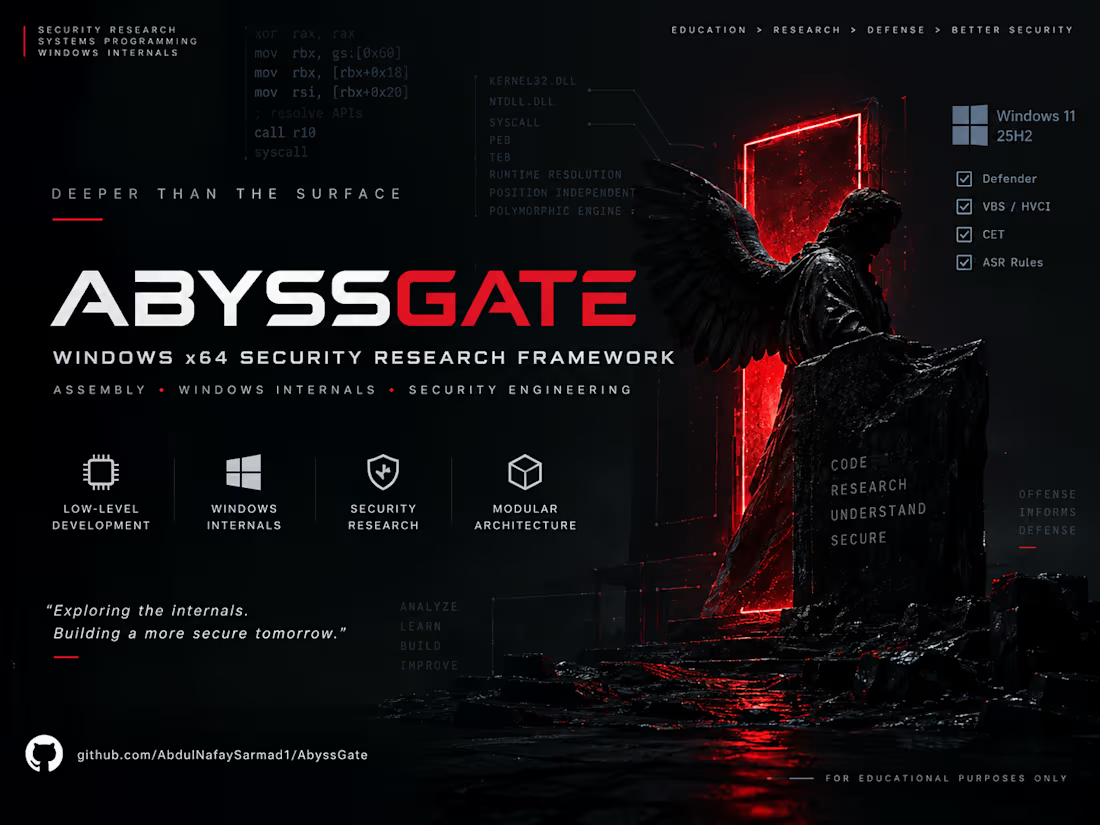
AbyssGate is an educational x64 assembly security research project built to explore low-level Windows internals and defensive security concepts. The project demonstrates position-independent assembly, Windows API resolution, memory management, system-call research, and modular framework design. It showcases my ability to work close to the operating-system layer, understand Windows security architecture, and build security-focused tooling from the ground up
0
94
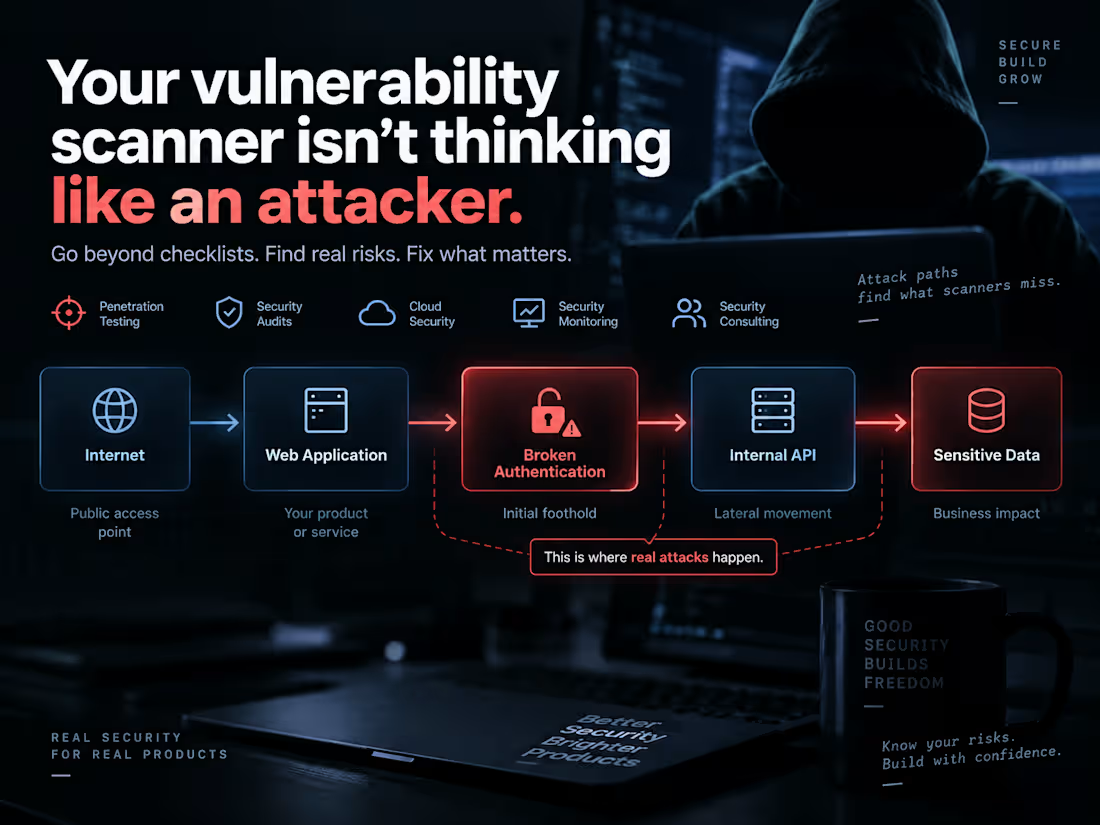
Most companies don't need another 80-page security report.
They need someone to tell them:
What can actually be exploited?
What could it cost us?
And what should we fix first?
That's the difference between checking a cybersecurity box and actually improving your security.
When I assess an application or infrastructure, I'm not interested in filling a report with 50 low-impact findings just to make it look impressive.
I care about attack paths.
→ Can authentication be bypassed?
→ Can one compromised account lead to something bigger?
→ Are APIs exposing data they shouldn't?
→ Can permissions be chained into privilege escalation?
→ Are cloud or infrastructure misconfigurations creating an easy entry point?
→ Would your monitoring actually notice an attacker?
And most importantly:
What should your team fix first?
That's the approach I bring to cybersecurity work — whether it's penetration testing, security audits, SOC/security monitoring, or security consulting.
I'm currently taking on new projects through Contra.
If you're building a SaaS product, web application, API, or growing infrastructure and you're unsure how it would hold up against a real attack, send me a message.
I'll happily take a look at what you're building and tell you where I'd start.
0
58
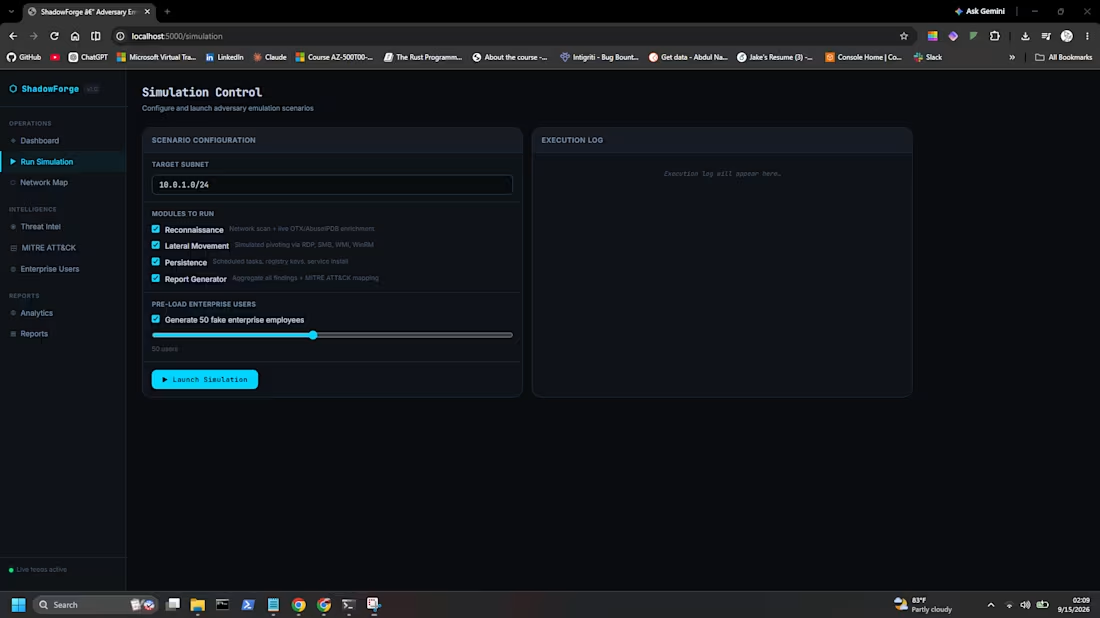
ShadowForge is an adversary-emulation and security-validation platform I built to help security teams model attack scenarios, visualize activity, correlate threat intelligence, and evaluate defensive visibility from a single operations interface.
The platform brings together scenario orchestration, network visualization, threat intelligence, MITRE ATT&CK mapping, enterprise identity simulation, analytics, and reporting into one unified workflow.
I designed the application around modular simulation components so authorized lab and security-validation exercises can be configured, observed, and translated into useful defensive findings rather than scattered logs and manual notes.
Key engineering work included:
Centralized security operations dashboard
Configurable adversary-emulation scenarios
Reconnaissance and environment-discovery simulation
Lateral-movement and persistence scenario modeling
Live execution-event visualization
Network topology and host mapping
MITRE ATT&CK technique mapping
Threat-intelligence and IOC enrichment
Enterprise user simulation for realistic lab scenarios
Security analytics and severity tracking
Automated findings and report generation
Modular architecture designed for controlled security testing
ShadowForge turns an authorized security exercise into something measurable: operators can configure a scenario, observe activity as it happens, correlate findings with threat intelligence and ATT&CK techniques, and produce structured results for defensive analysis.
Built for controlled labs, security validation, and authorized adversary-emulation environments.
0
90
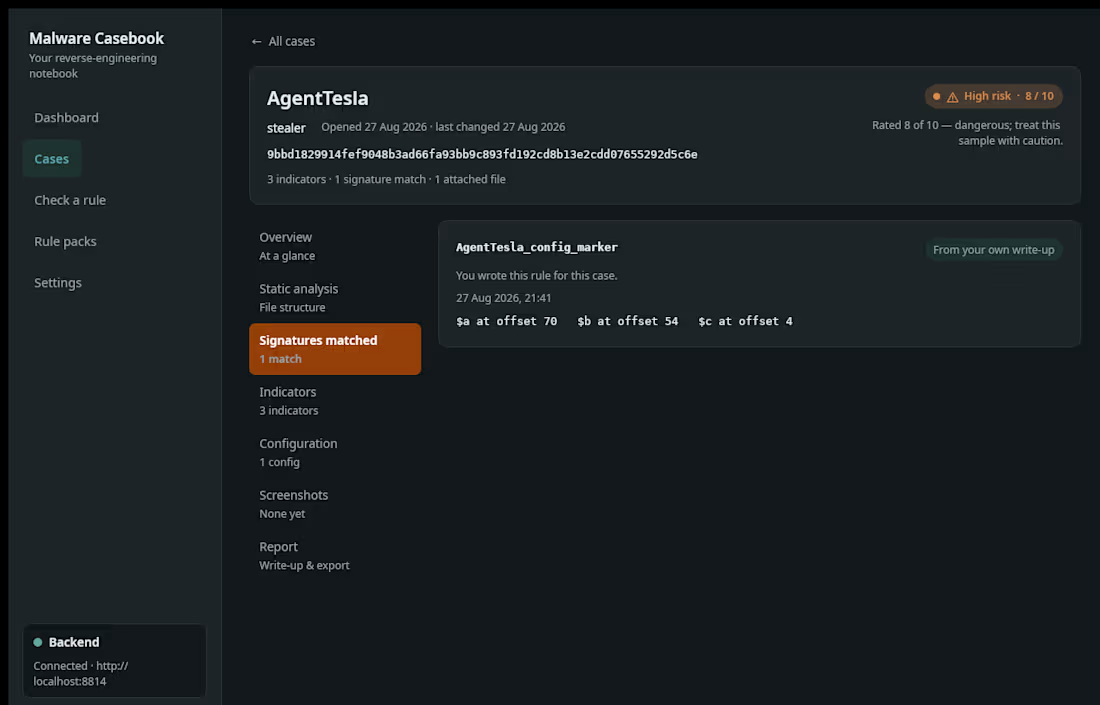
Grim Lens is a local-first malware intelligence and threat-hunting workbench I built for security teams that need to analyze evidence without sending sensitive samples to the cloud.
The platform ingests static artifacts such as PE metadata, strings, YARA matches, decoded configurations, PCAP summaries, and screenshots, then organizes them into investigation cases with risk scoring, enrichment, reporting, and cross-case intelligence.
I designed the system around a strict security boundary: no sample execution, no automatic uploads, and no outbound enrichment unless explicitly requested.
The backend is built in Rust using Axum, Tokio, SQLx, SQLite, YARA-X, and structured analysis modules, while the desktop interface is built with Avalonia/.NET 10 using MVVM and interactive charts.
Key engineering work included:
Local-first malware case management
Static PE analysis and entropy inspection
YARA rule matching and rule-pack management
Threat-intelligence enrichment using services such as VirusTotal, abuse.ch (http://abuse.ch), and AlienVault OTX
Rate limiting and TTL caching for external enrichment
Cross-case indicator correlation
Automated Markdown and PDF report generation
Risk distribution, family, and category dashboards
Rust REST API with structured validation and errors
SQLite-backed local storage and migrations
Cross-platform Avalonia desktop application
CI builds and packaged Windows/Linux releases
The result is a practical analyst workbench that turns scattered malware artifacts into a structured, searchable casebook while keeping control of sensitive data on the analyst’s own workstation.
0
98