ShadowForge is an adversary-emulation and

View completed workgithub.com
ShadowForge is an adversary-emulation and security-validation platform I built to help security teams model attack scenarios, visualize activity, correlate threat intelligence, and evaluate defensive visibility from a single operations interface.
The platform brings together scenario orchestration, network visualization, threat intelligence, MITRE ATT&CK mapping, enterprise identity simulation, analytics, and reporting into one unified workflow.
I designed the application around modular simulation components so authorized lab and security-validation exercises can be configured, observed, and translated into useful defensive findings rather than scattered logs and manual notes.
Key engineering work included:
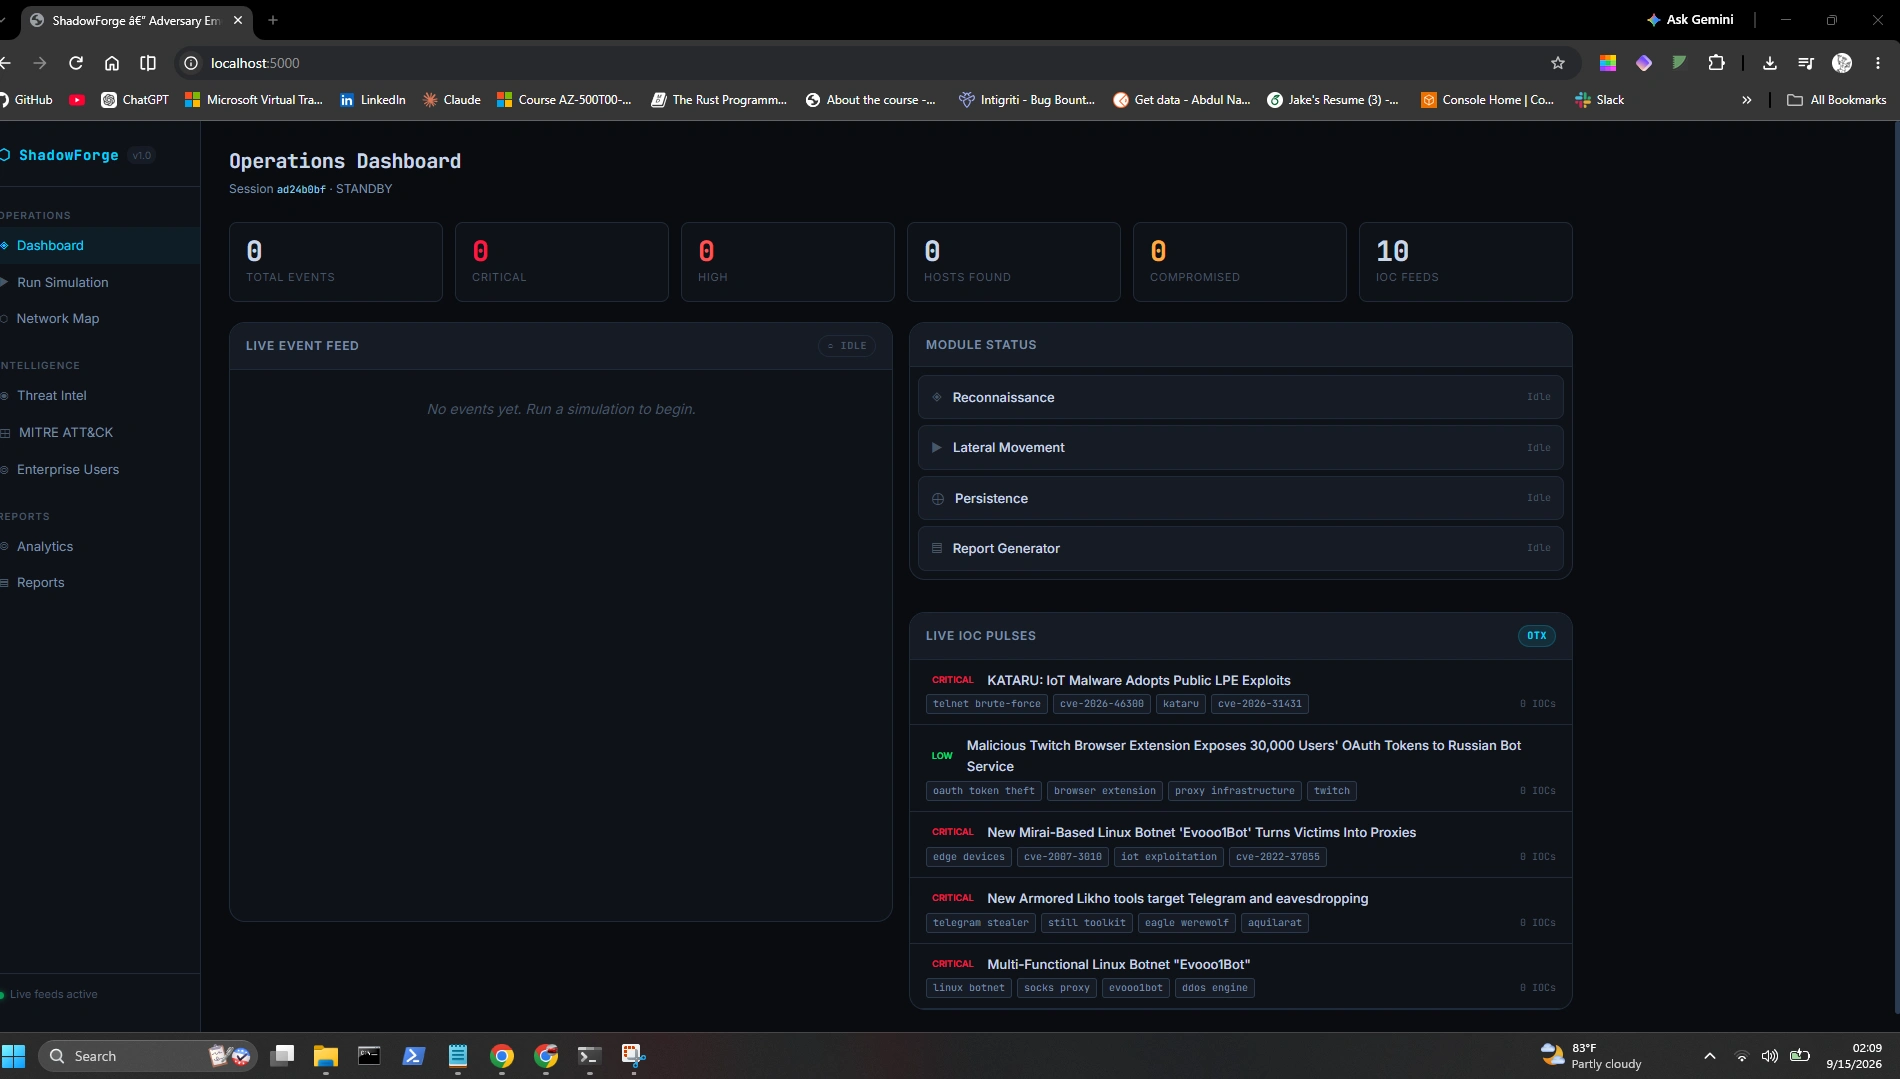
Centralized security operations dashboard
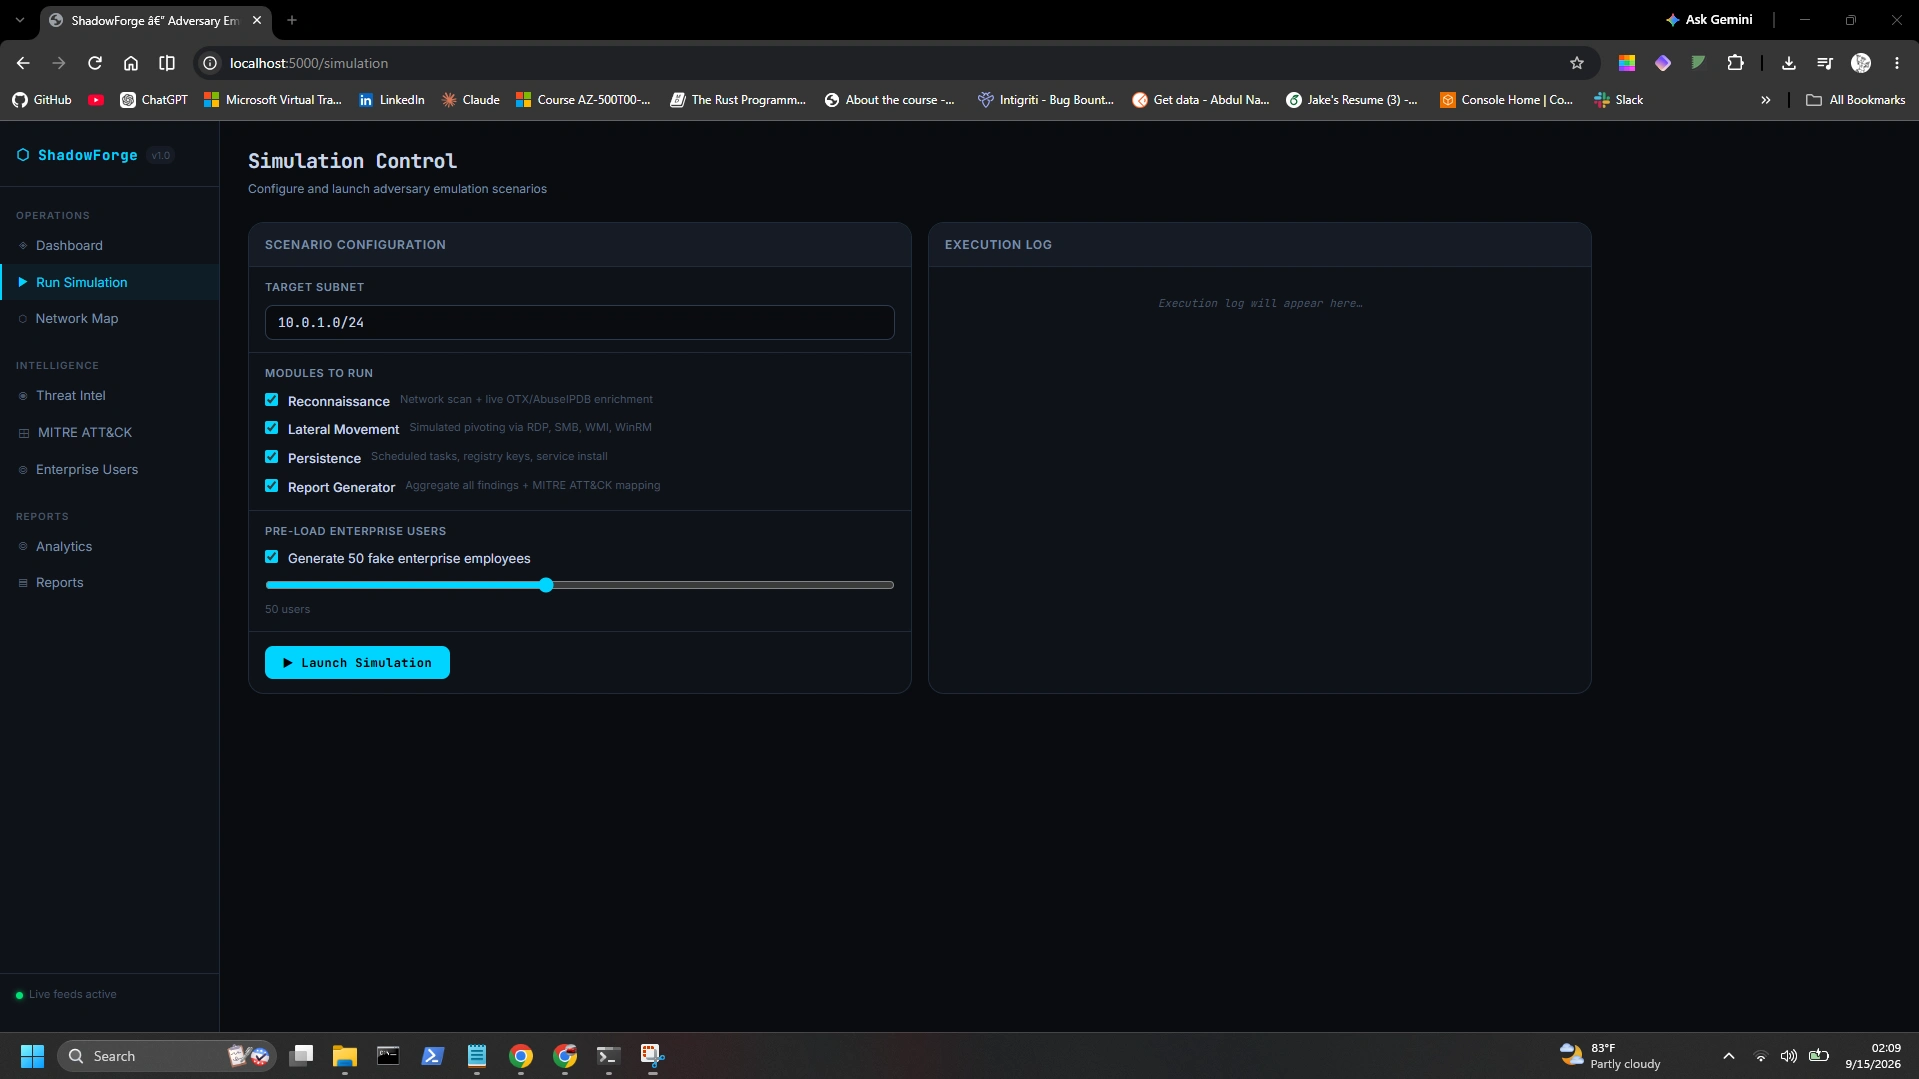
Configurable adversary-emulation scenarios
Reconnaissance and environment-discovery simulation
Lateral-movement and persistence scenario modeling
Live execution-event visualization
Network topology and host mapping
MITRE ATT&CK technique mapping
Threat-intelligence and IOC enrichment
Enterprise user simulation for realistic lab scenarios
Security analytics and severity tracking
Automated findings and report generation
Modular architecture designed for controlled security testing
ShadowForge turns an authorized security exercise into something measurable: operators can configure a scenario, observe activity as it happens, correlate findings with threat intelligence and ATT&CK techniques, and produce structured results for defensive analysis.
Built for controlled labs, security validation, and authorized adversary-emulation environments.
0 likes · 0 views · Sep 14, 2026
ShadowForge is an adversary-emulation and security-validation platform I built to help security teams model attack scenarios, visualize activity, correlate t...