Most companies don't need another

Most companies don't need another 80-page security report.
They need someone to tell them:
What can actually be exploited?
What could it cost us?
And what should we fix first?
That's the difference between checking a cybersecurity box and actually improving your security.
When I assess an application or infrastructure, I'm not interested in filling a report with 50 low-impact findings just to make it look impressive.
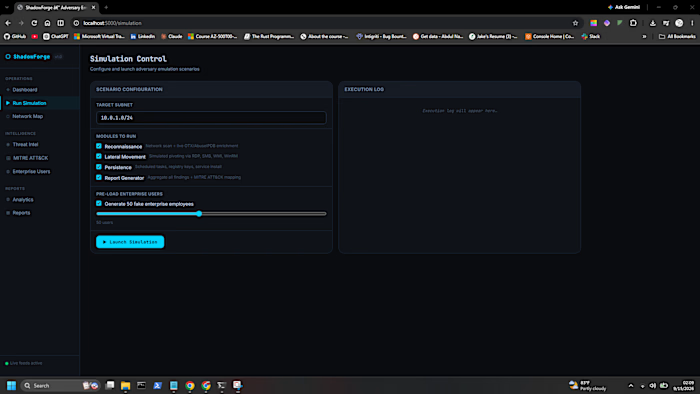
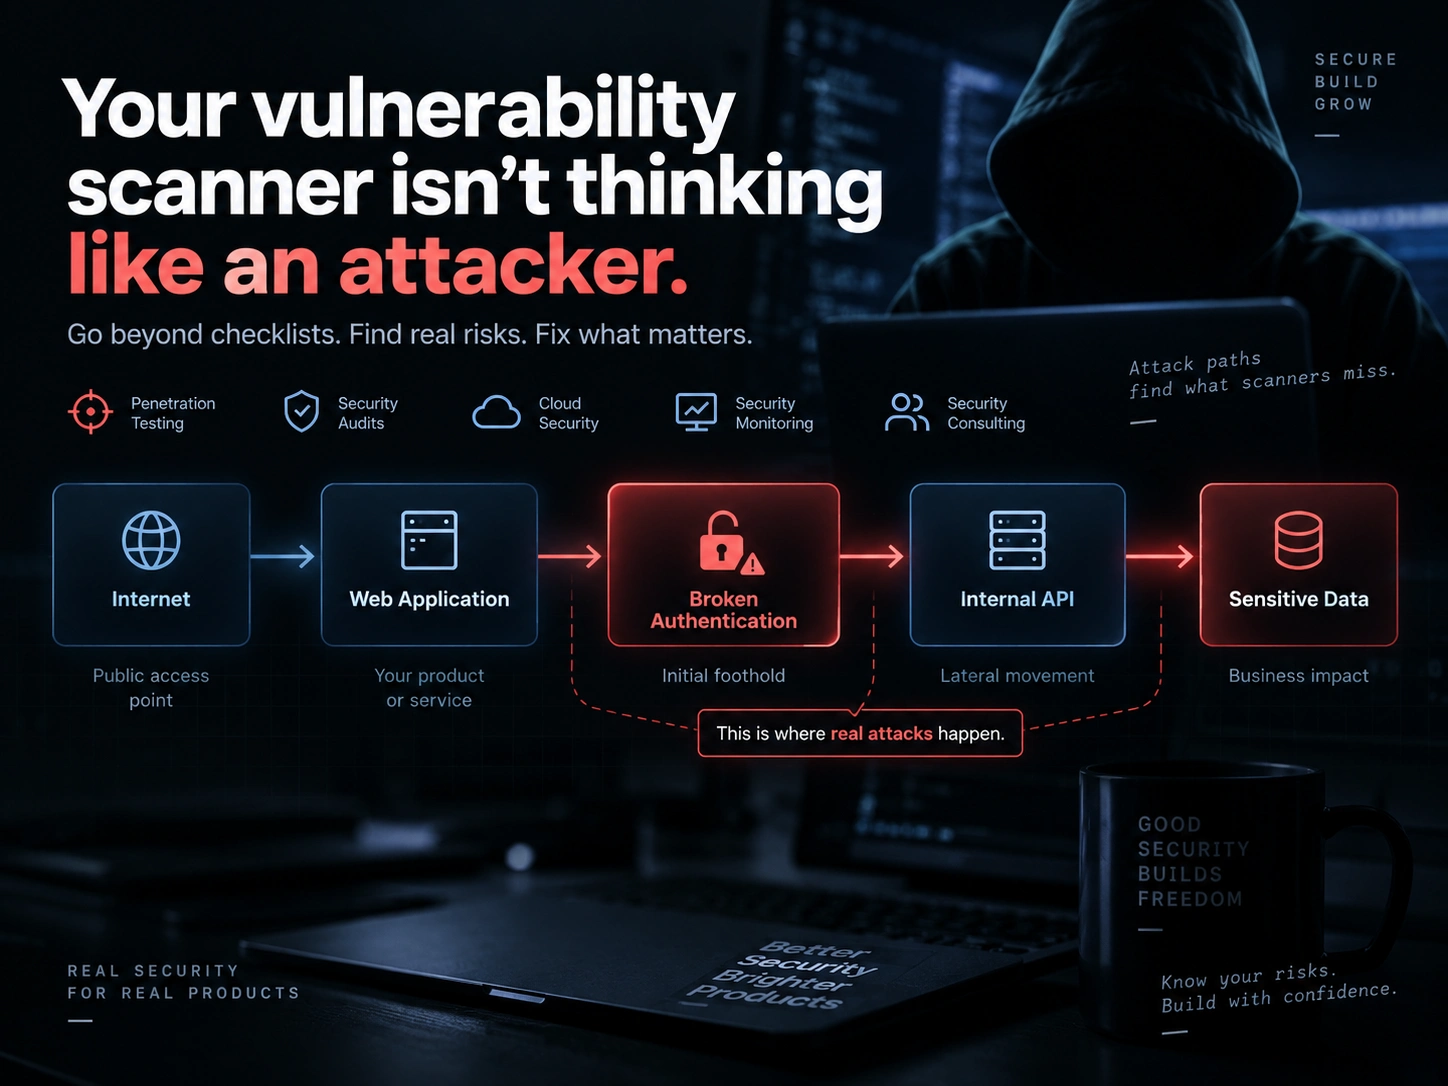
I care about attack paths.
→ Can authentication be bypassed?
→ Can one compromised account lead to something bigger?
→ Are APIs exposing data they shouldn't?
→ Can permissions be chained into privilege escalation?
→ Are cloud or infrastructure misconfigurations creating an easy entry point?
→ Would your monitoring actually notice an attacker?
And most importantly:
What should your team fix first?
That's the approach I bring to cybersecurity work — whether it's penetration testing, security audits, SOC/security monitoring, or security consulting.
I'm currently taking on new projects through Contra.
If you're building a SaaS product, web application, API, or growing infrastructure and you're unsure how it would hold up against a real attack, send me a message.
I'll happily take a look at what you're building and tell you where I'd start.
0 likes · 0 views · Sep 16, 2026
Most companies don't need another 80-page security report. They need someone to tell them: What can actually be exploited? What could it cost us? And what ...