Usama Rasheed
Web security expert & pentesting specialist.
- 1
- Followers

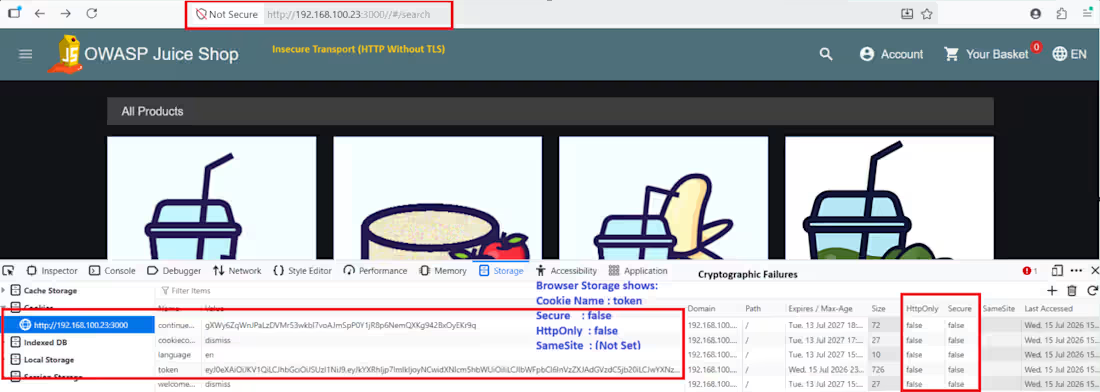
OWASP A02: Cryptographic Failures
🔐 OWASP A02 — Cryptographic Failures Assessment
Overview
Conducted a manual assessment focusing on the protection of sensitive data during storage and transmission.
What I Found
Sensitive information exposed inside JWTs
JWT information disclosure
Missing Secure, HttpOnly, and SameSite cookie attributes
HTTP used instead of HTTPS
Stack trace and debug information disclosure
Application version disclosure
Impact
Sensitive information leakage can assist attackers in account compromise, session theft, and application reconnaissance.
Mitigation
Avoid storing sensitive data inside JWTs.
Enforce HTTPS across the application.
Configure cookies with Secure, HttpOnly, and SameSite.
Disable verbose error messages in production.
Minimize unnecessary information disclosure.
Tools Used
Burp Suite Professional
JWT Decoder
Browser Developer Tools
0
135
OWASP A01: Broken Access Control
🔒 OWASP A01 — Broken Access Control Assessment
Overview
Performed a manual security assessment of a vulnerable web application to identify Broken Access Control issues affecting API endpoints.
What I Found
Horizontal Privilege Escalation (IDOR)
Vertical Privilege Escalation
Unauthorized access to restricted API endpoints
User enumeration through exposed APIs
Impact
Unauthorized users could access resources belonging to other users and retrieve sensitive information without proper authorization.
Mitigation
Enforce server-side authorization on every request.
Implement Role-Based Access Control (RBAC).
Validate object ownership before returning data.
Apply the principle of least privilege.
Tools Used
Burp Suite Professional
Firefox Developer Tools
JWT Decoder
1
184
🚨 Vulnerability Spotlight: OS Command Injection
⚠️ The Flaw: Unsanitized input in a "Ping Device" feature allowed arbitrary command execution directly on the server shell.
🕵️♂️ The Exploit (via Burp Suite):
Instead of a normal IP, I injected shell metacharacters: 127.0.0.1; cat /etc/passwd.
Result: The backend blindly executed it, leaking sensitive OS files and confirming unauthorized system access.
🛡️ The Fix:
✅ Stop Direct Execution: Never pass raw input to exec() or system().
✅ Strict Allow-listing: Validate inputs with Regex (e.g., enforce standard IPv4 format).
✅ Command Escaping: Neutralize malicious operators using escapeshellarg().
Rule of thumb: Never trust user input!
0
118
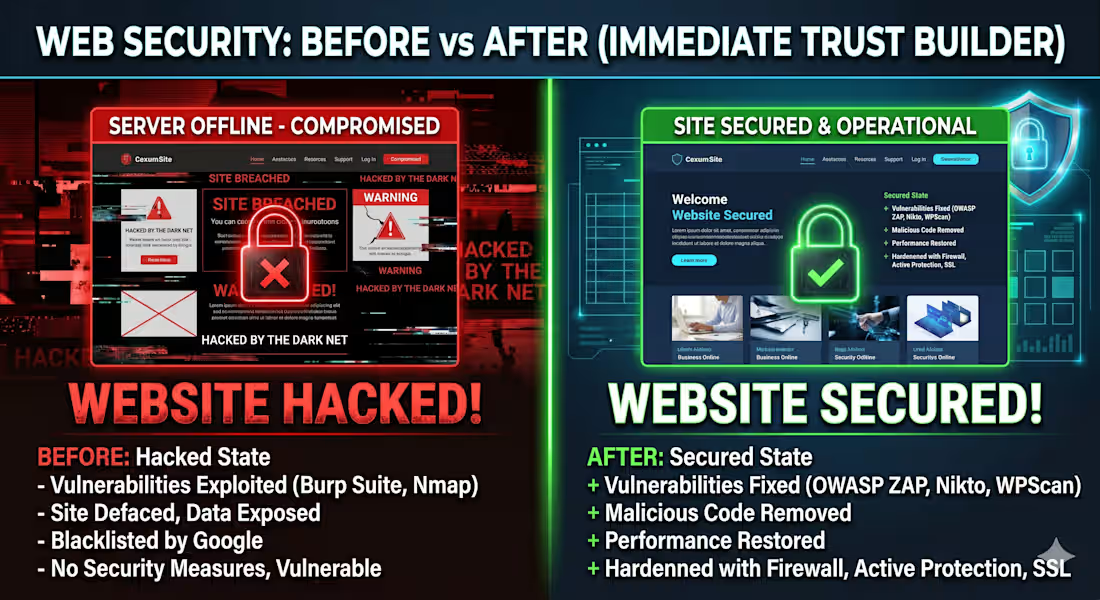
Emergency recovery and malware removal for a compromised website, transforming it from a hacked state to a fully secured, hardened, and operational platform.
0
85