
Starting from zero is uncomfortable. But sometimes, it’s exactly what you need to build the next chapter.
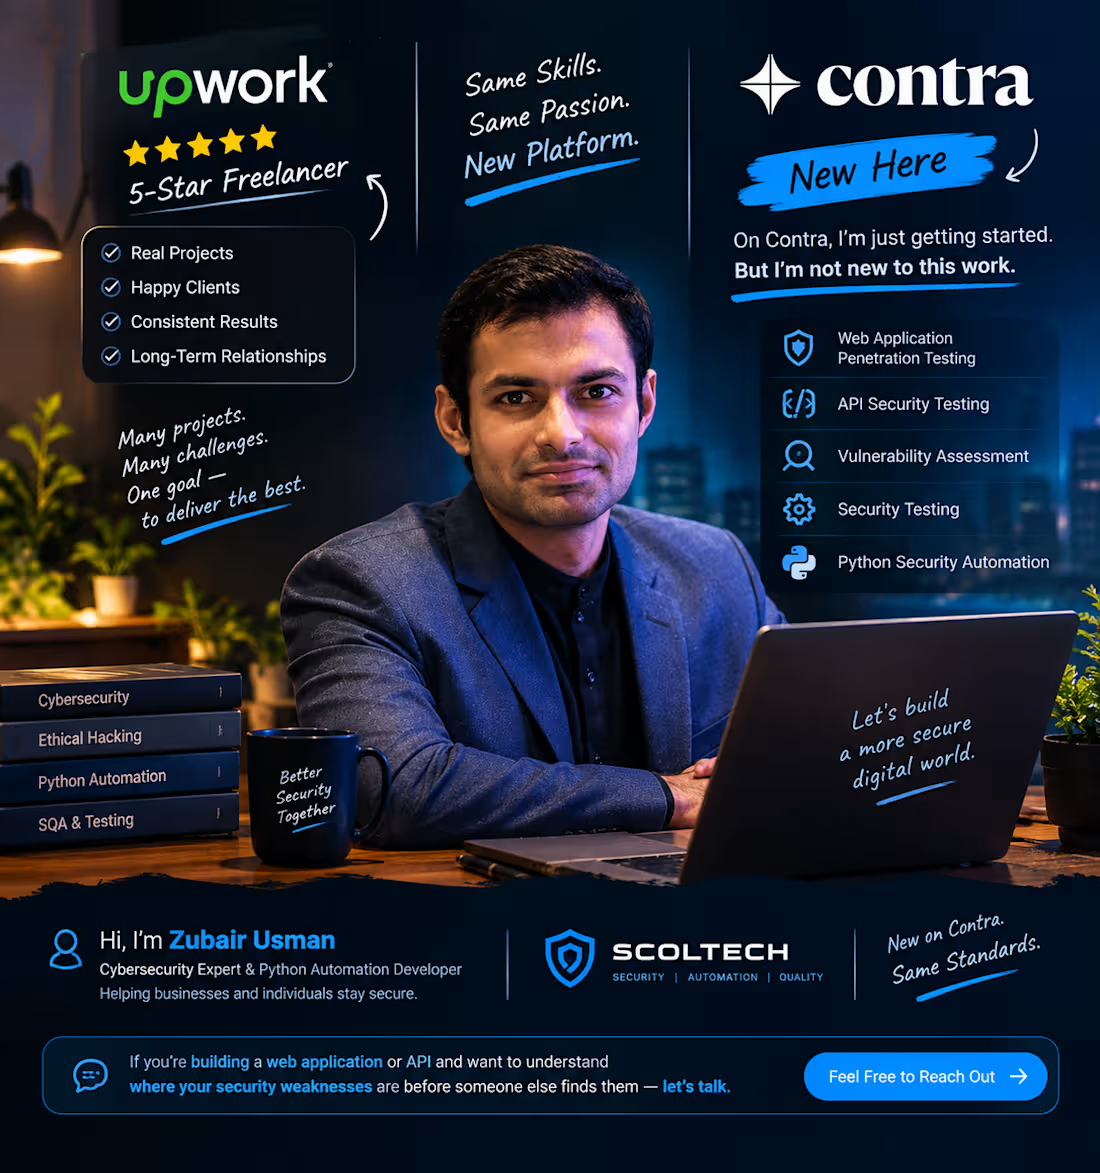
I’m new to Contra. But I’m definitely not new to cybersecurity.
A few years ago, I started taking on security and automation projects on Upwork.
Since then, I’ve worked with clients on real technical problems from vulnerability discovery and web security testing to Python automation and QA.
That journey taught me something important:
Clients don’t just need someone who can find a vulnerability.
They need someone who can understand it, validate it, explain the risk, and help fix it.
I’m now bringing that same mindset to Contra.
Here’s what I help with:
🔐 Web Application Penetration Testing
🔐 API Security Testing
🔍 Vulnerability Assessment
🛡️ Security Testing & Retesting
🐍 Python Security Automation
🧪 QA / SQA & Test Automation
I’m proud to have built a 5-star track record on Upwork, but starting on a new platform means starting from zero again.
And honestly?
I’m okay with that.
Because the platform is new to me
the work isn’t.
This is a new chapter for SCOLTECH, and I’m looking forward to connecting with founders, developers, startups, and businesses that care about building secure software.
If you’re building a web application or API and want to know where your security weaknesses are before someone else finds them let’s talk.
New on Contra.
Same standards.
Same commitment to quality.
#Cybersecurity #PenetrationTesting #APIsecurity #WebSecurity #Python #SecurityTesting #Contra #Freelancer #SCOLTECH
0
16
Full Web Security Audit & OWASP ASVS Compliance (27 Findings)
Comprehensive web application penetration test and vulnerability assessment for a production hosting infrastructure.
A production hosting provider required a full-scope security audit to evaluate their attack surface, verify compliance with the OWASP Application Security Verification Standard (ASVS Level 2), and uncover critical business-logic vulnerabilities before public deployment.
I executed a hybrid security assessment combining automated reconnaissance with deep manual exploitation using Burp Suite. Every vulnerability was manually validated to eliminate false positives and scored using standard CVSS 3.1 metrics.
From a single comprehensive audit, I uncovered 27 reproducible findings:
2 High Severity: Exposed database backups and critical Cross-Site Scripting (XSS) execution vectors.
8 Medium Severity: CORS misconfigurations, XML-RPC brute-force paths, and authentication bypass vectors.
10 Low Severity: Unrestricted directory listings and insecure header configurations.
7 Informational: Information disclosure and software version leaks.
0
15
Enterprise VPN Infrastructure & Cloud Server Manager (12.8k Lines of Python)
Production-grade OpenVPN & WireGuard server automation platform with a live customer portal and real-time network diagnostics.
Managing secure, multi-protocol VPN infrastructure manually leads to configuration drift, complex user onboarding, and lack of real-time visibility into server metrics. To deliver a seamless user experience while maintaining enterprise-grade network security, the platform required a fully automated backend to manage server daemons, user access controls, and diagnostics without manual administrator intervention.
0
21
AI Security Research: Windsurf IDE OAuth 2.0 Vulnerability (CVSS 7.1)
Zero-Day vulnerability research and responsible disclosure on an AI-powered IDE authentication pipeline
During deep-dive protocol analysis of the OAuth 2.0 implicit flow, I identified a critical missing nonce parameter validation [1]. Using manual request manipulation and custom test vectors, I successfully confirmed three severe exploit paths end-to-end:
Session Replay (25/25 Confirmed): Captured tokens re-authenticated unauthorized sessions without validation.
CSRF Attacks (3/3 Confirmed): Unvalidated state parameters allowed forced account state binding.
Session Fixation (5/5 Confirmed): Pre-authentication identifiers remained active post-login.
Severity Rating: Scored CVSS 3.1: 7.1 (High) under standard vulnerability scoring frameworks.
0
36