The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Full Web Security Audit & OWASP ASVS Compliance (27 Findings)
Comprehensive web application penetration test and vulnerability assessment for a production hosting infrastructure.
A production hosting provider required a full-scope security audit to evaluate their attack surface, verify compliance with the OWASP Application Security Verification Standard (ASVS Level 2), and uncover critical business-logic vulnerabilities before public deployment.
I executed a hybrid security assessment combining automated reconnaissance with deep manual exploitation using Burp Suite. Every vulnerability was manually validated to eliminate false positives and scored using standard CVSS 3.1 metrics.
From a single comprehensive audit, I uncovered 27 reproducible findings:
2 High Severity: Exposed database backups and critical Cross-Site Scripting (XSS) execution vectors.
8 Medium Severity: CORS misconfigurations, XML-RPC brute-force paths, and authentication bypass vectors.
10 Low Severity: Unrestricted directory listings and insecure header configurations.
7 Informational: Information disclosure and software version leaks.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started






Related posts


Yora is a cloud-based cyber security platform that helps you clean, monitor, and protect your website from malware, threats, and vulnerabilities with real-time detection, automated defense, and centralized security management.


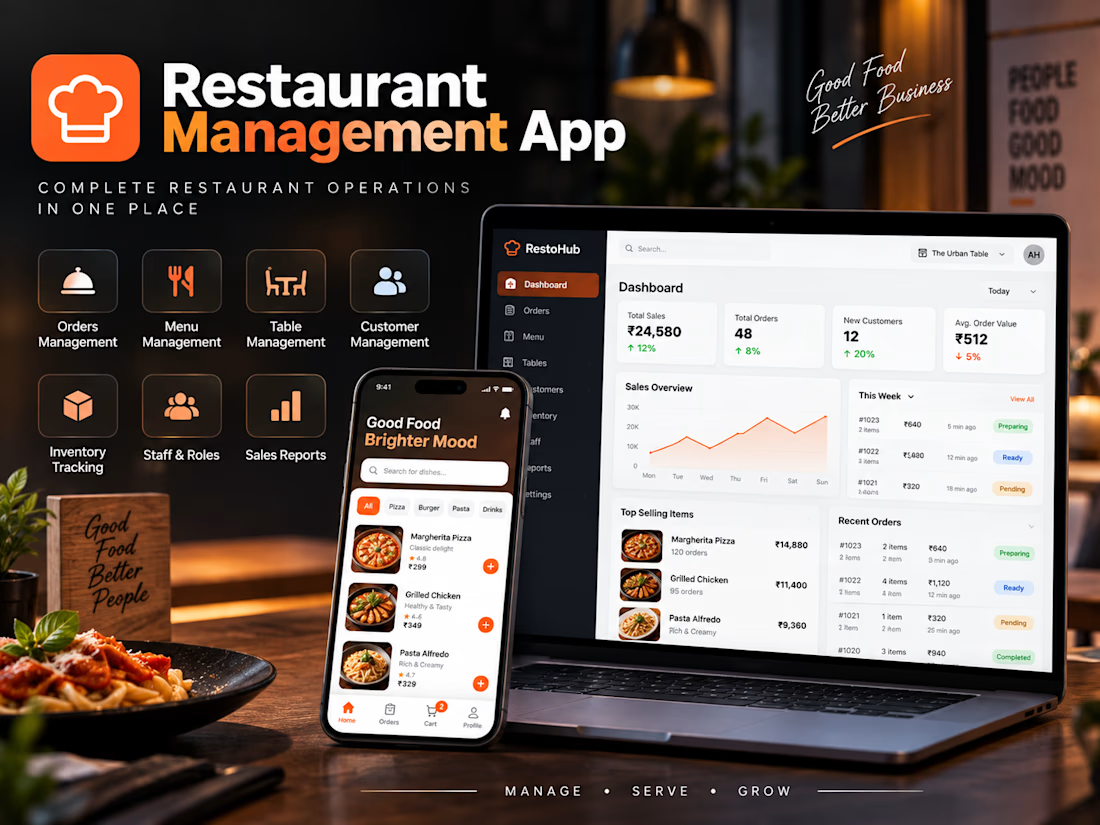
Full-stack restaurant management system with order, menu, table, inventory, staff, customer, sales, and reporting features, built for efficient daily operations.



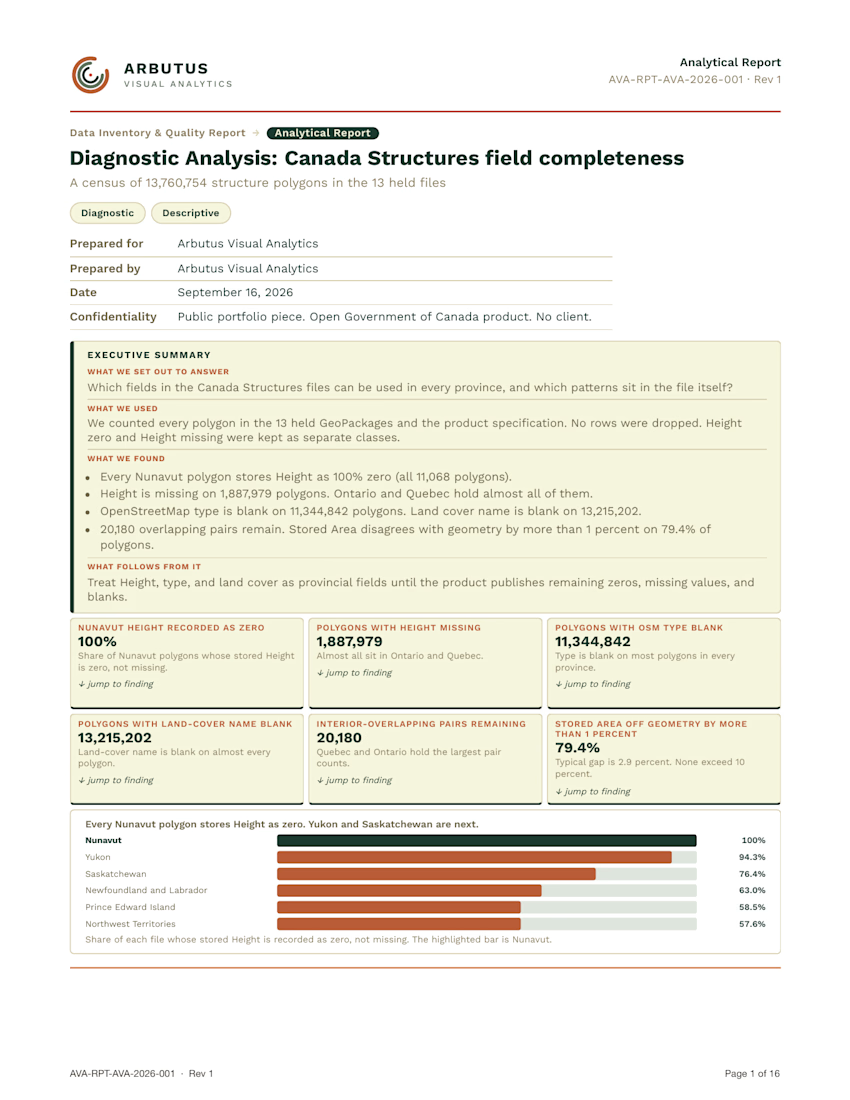
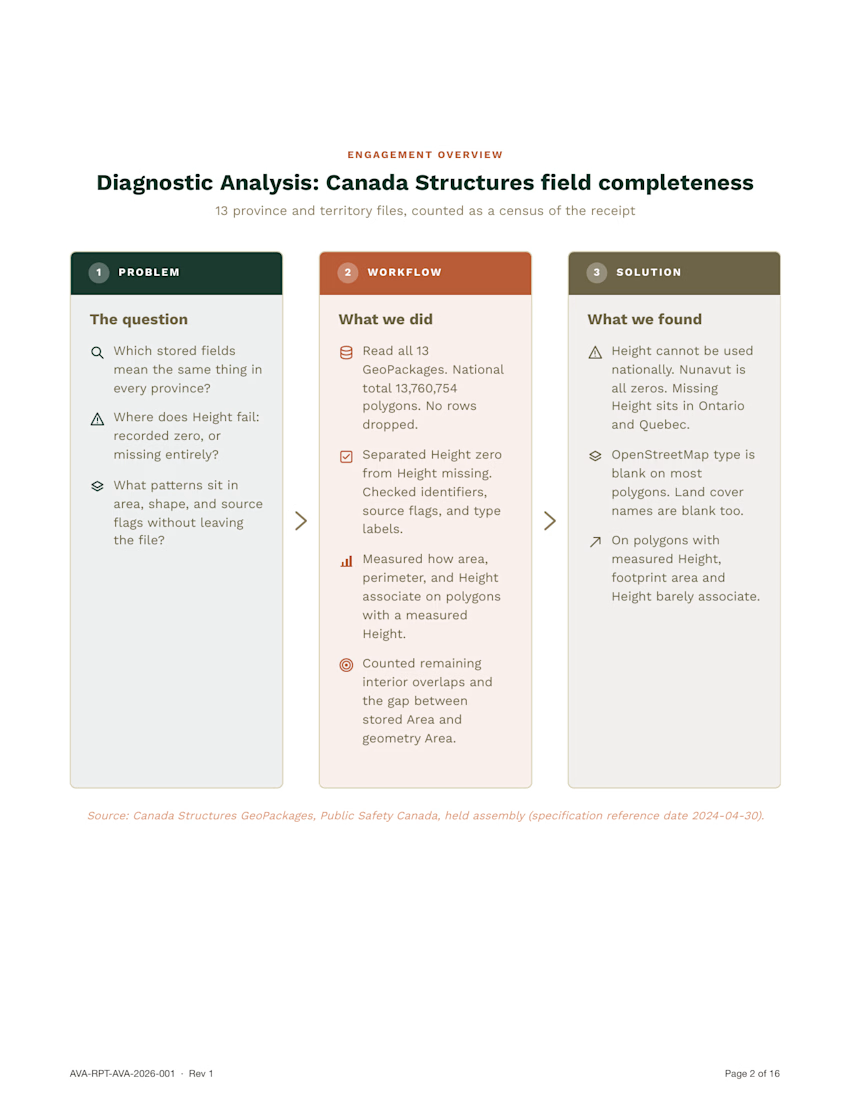
If you have ever been handed a dataset and wanted to know the integrity of the content, and any key information sitting inside it, you needed a descriptive analysis.
This is a descriptive analysis of Canada Structures, the federal building-footprint product. A file like this is assembled from several sources and file types, and that mix can leave artifacts. The work was looking for those artifacts so the file can be trusted before anyone treats stored height or type as national fields.
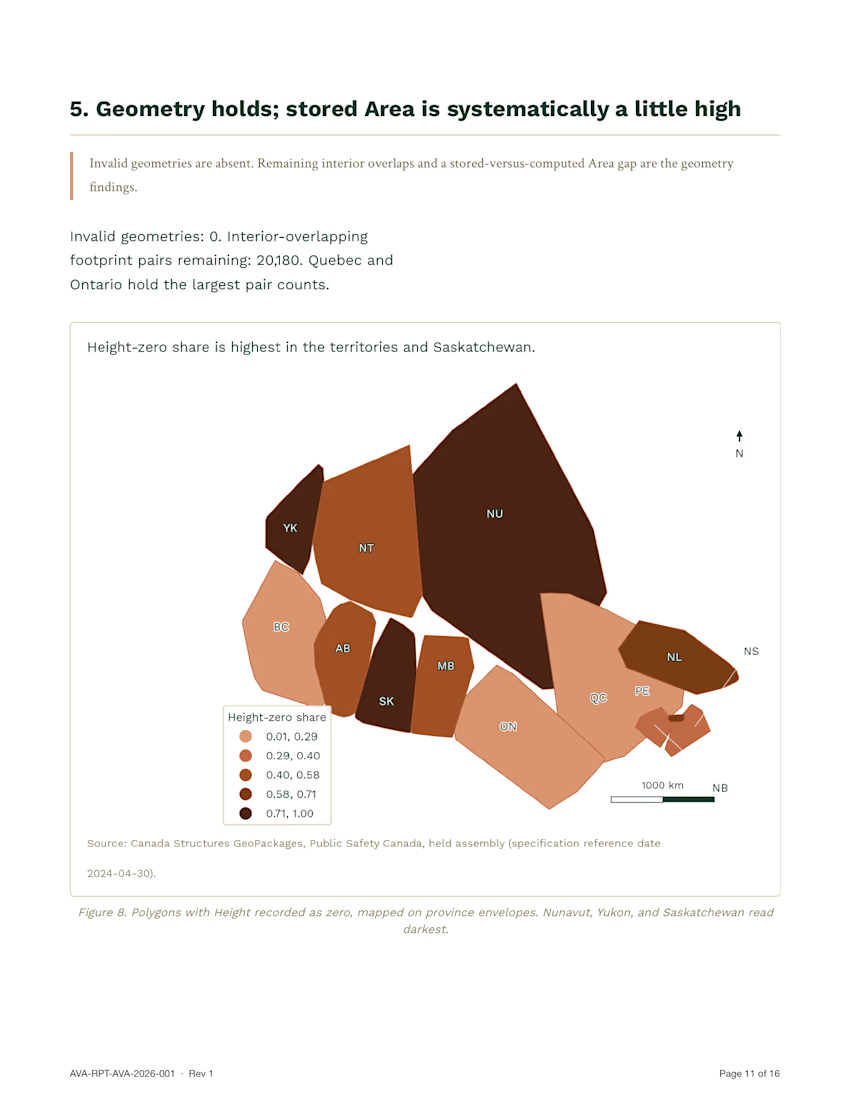
National count is 13,760,754, matching the spec. Every Nunavut footprint stores height as zero (11,068). 66.5% of footprints have a positive stored height. 82.4% carry no building type. Shape, size, and province together score 0.42 at guessing source class, against 0.32 from province alone.