The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

AI Security Research: Windsurf IDE OAuth 2.0 Vulnerability (CVSS 7.1)
Zero-Day vulnerability research and responsible disclosure on an AI-powered IDE authentication pipeline
During deep-dive protocol analysis of the OAuth 2.0 implicit flow, I identified a critical missing nonce parameter validation [1]. Using manual request manipulation and custom test vectors, I successfully confirmed three severe exploit paths end-to-end:
Session Replay (25/25 Confirmed): Captured tokens re-authenticated unauthorized sessions without validation.
CSRF Attacks (3/3 Confirmed): Unvalidated state parameters allowed forced account state binding.
Session Fixation (5/5 Confirmed): Pre-authentication identifiers remained active post-login.
Severity Rating: Scored CVSS 3.1: 7.1 (High) under standard vulnerability scoring frameworks.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started






Related posts


A sneak peak to a B2B solution I'm building.


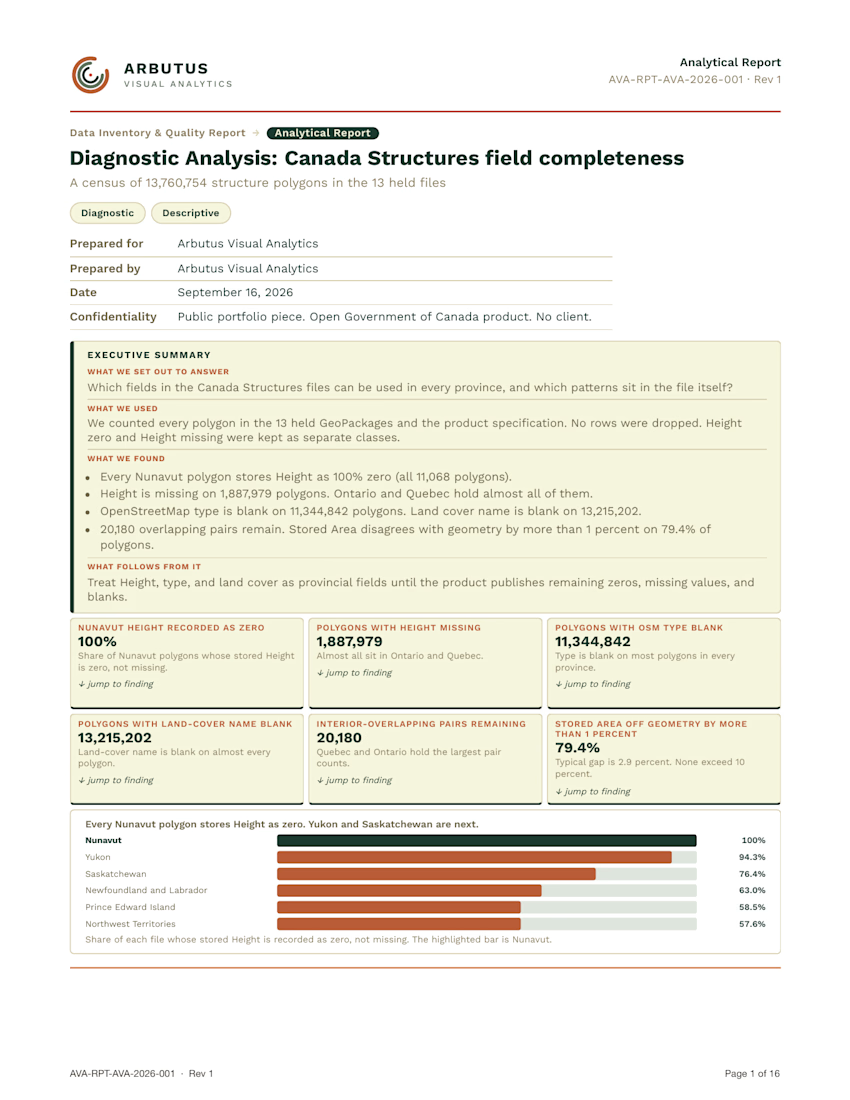
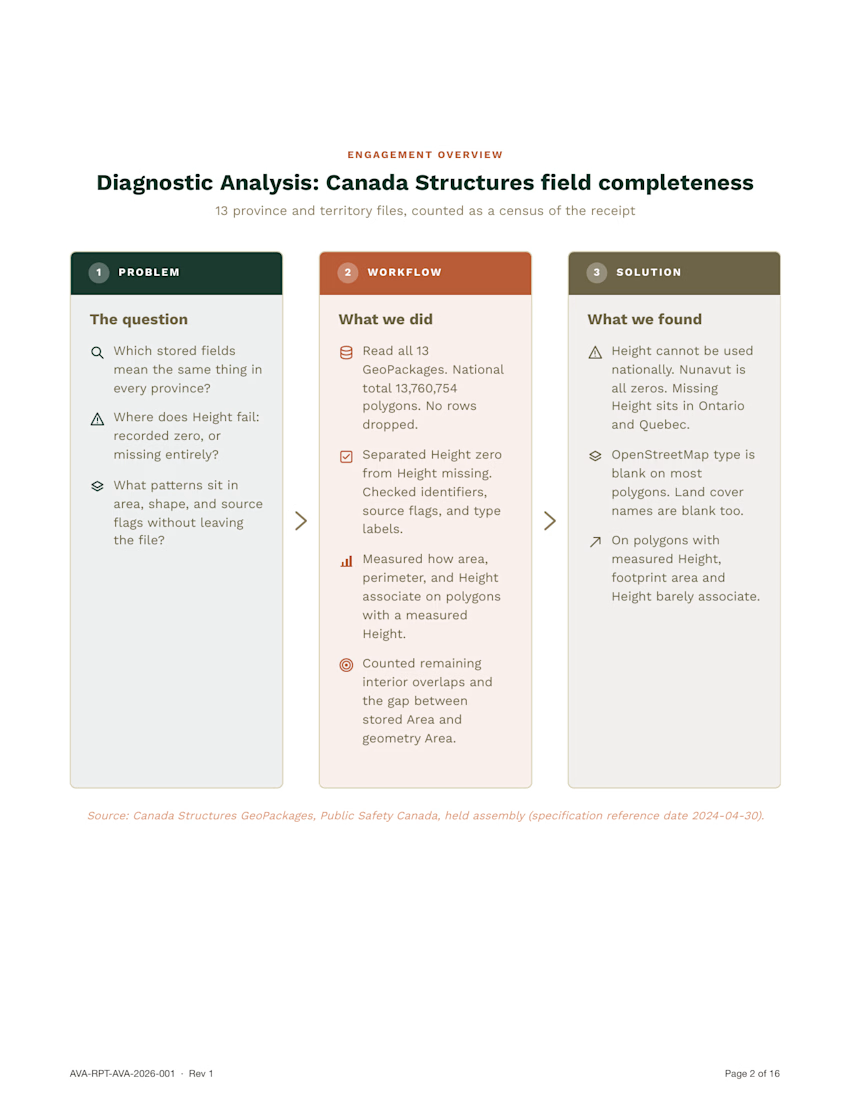
If you have ever been handed a dataset and wanted to know the integrity of the content, and any key information sitting inside it, you needed a descriptive analysis.
This is a descriptive analysis of Canada Structures, the federal building-footprint product. A file like this is assembled from several sources and file types, and that mix can leave artifacts. The work was looking for those artifacts so the file can be trusted before anyone treats stored height or type as national fields.
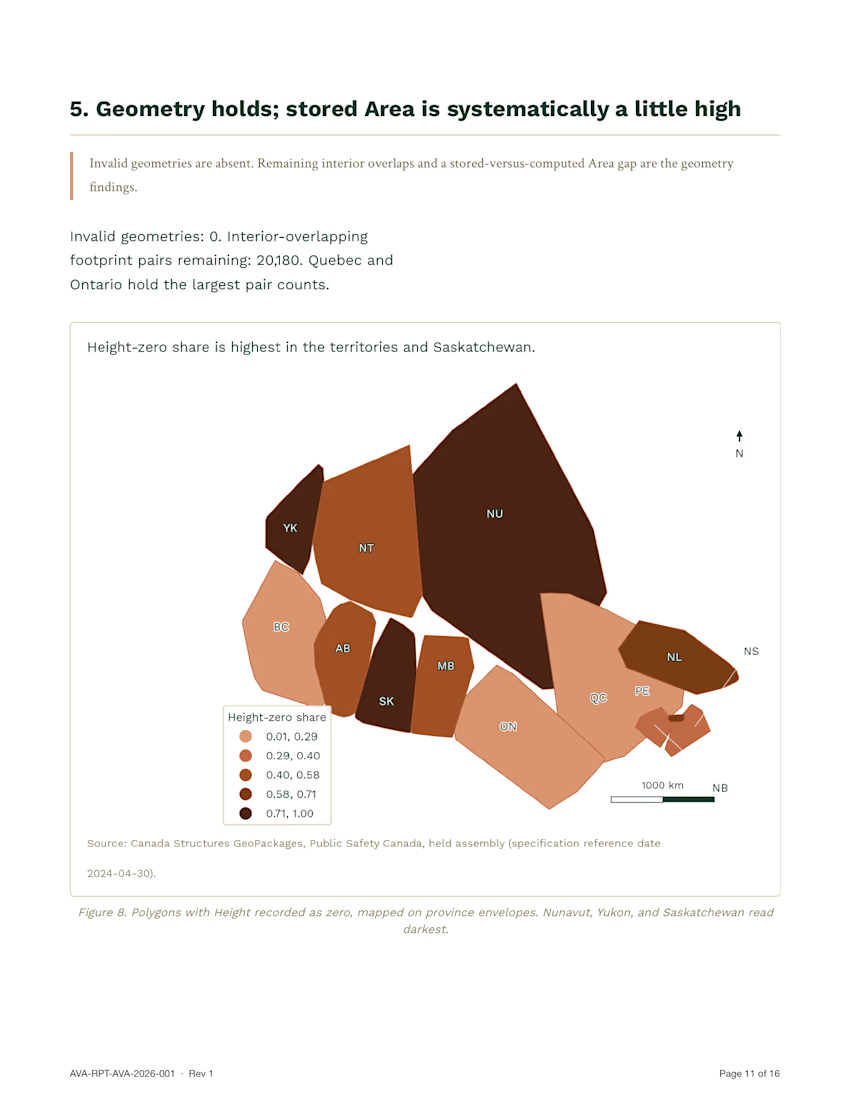
National count is 13,760,754, matching the spec. Every Nunavut footprint stores height as zero (11,068). 66.5% of footprints have a positive stored height. 82.4% carry no building type. Shape, size, and province together score 0.42 at guessing source class, against 0.32 from province alone.