Threat Intelligence API: AbuseIPDB, OTX, STIX & MISP

Mojtaba Karimiabdar


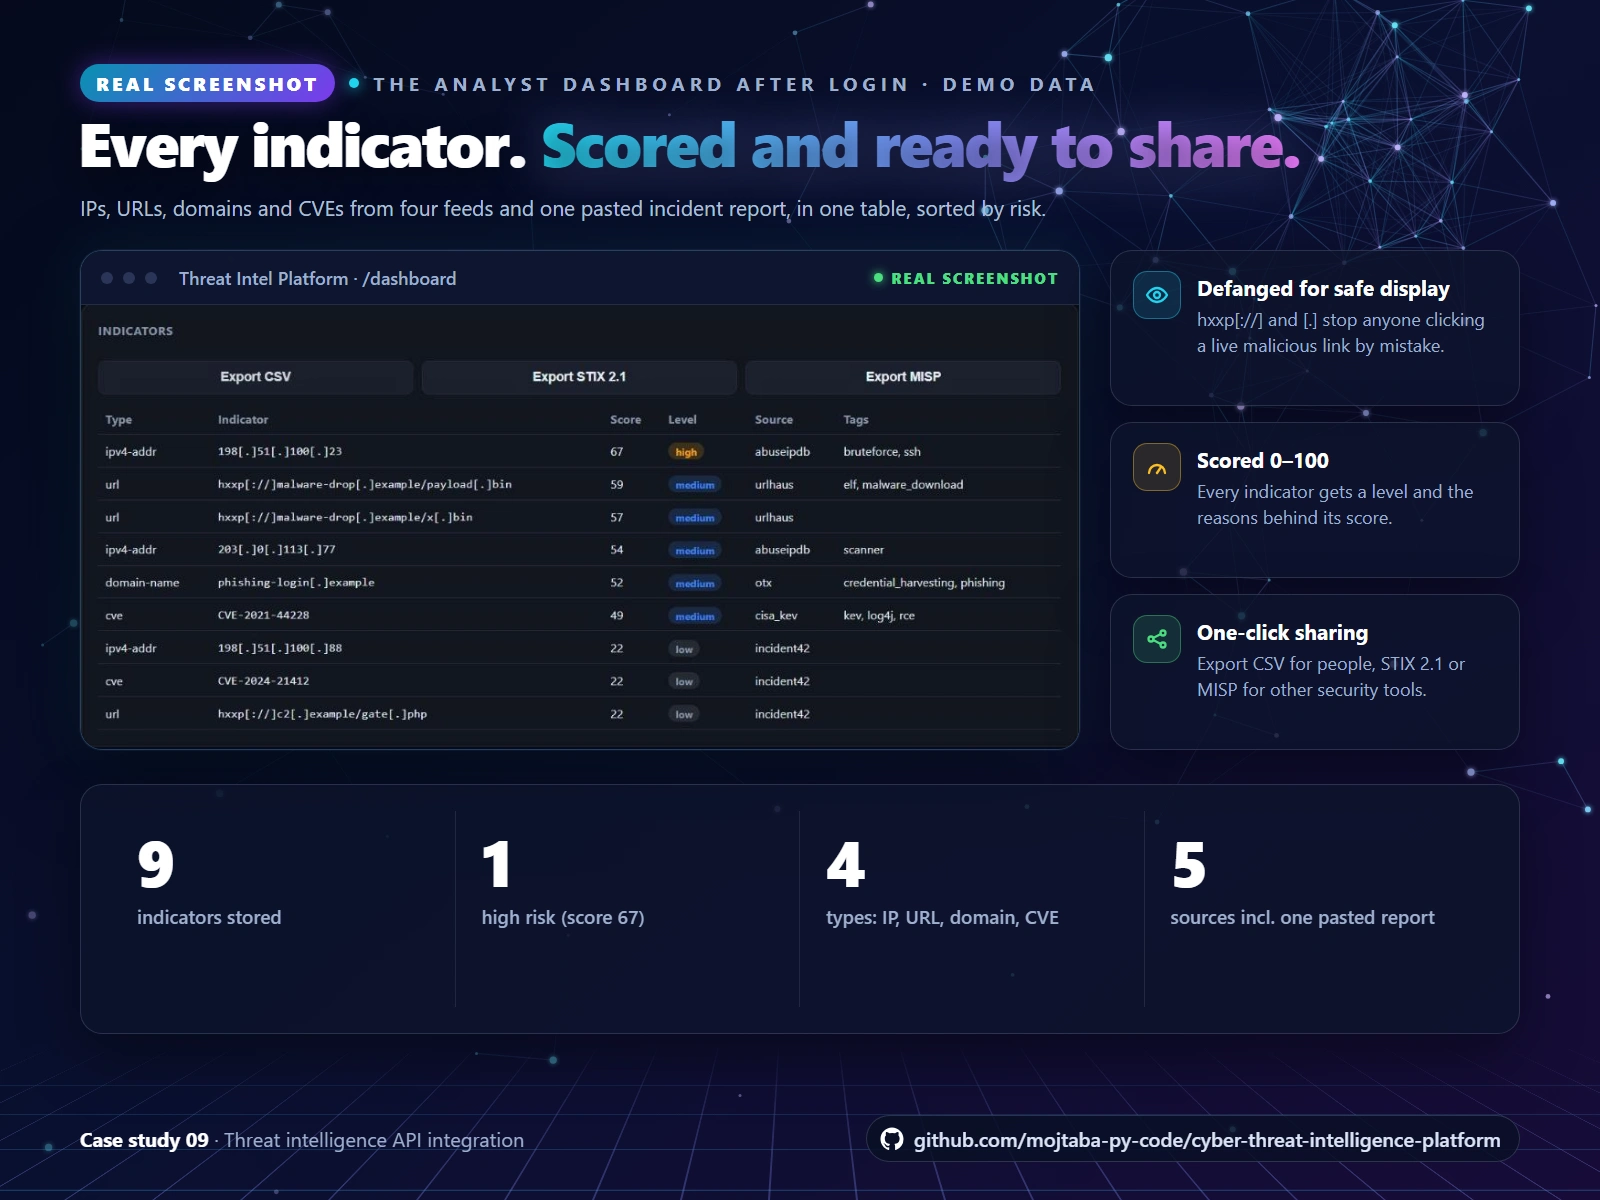
The real analyst dashboard: every indicator defanged for safe display, scored 0-100 and ready to export as CSV, STIX 2.1 or MISP.
The challenge
Security teams pull indicators from many feeds, such as AbuseIPDB, URLHaus, AlienVault OTX, CISA KEV and vendor reports, each with its own API and format. Copying them into spreadsheets wastes time, and nobody can say why one IP matters more than another.
The solution
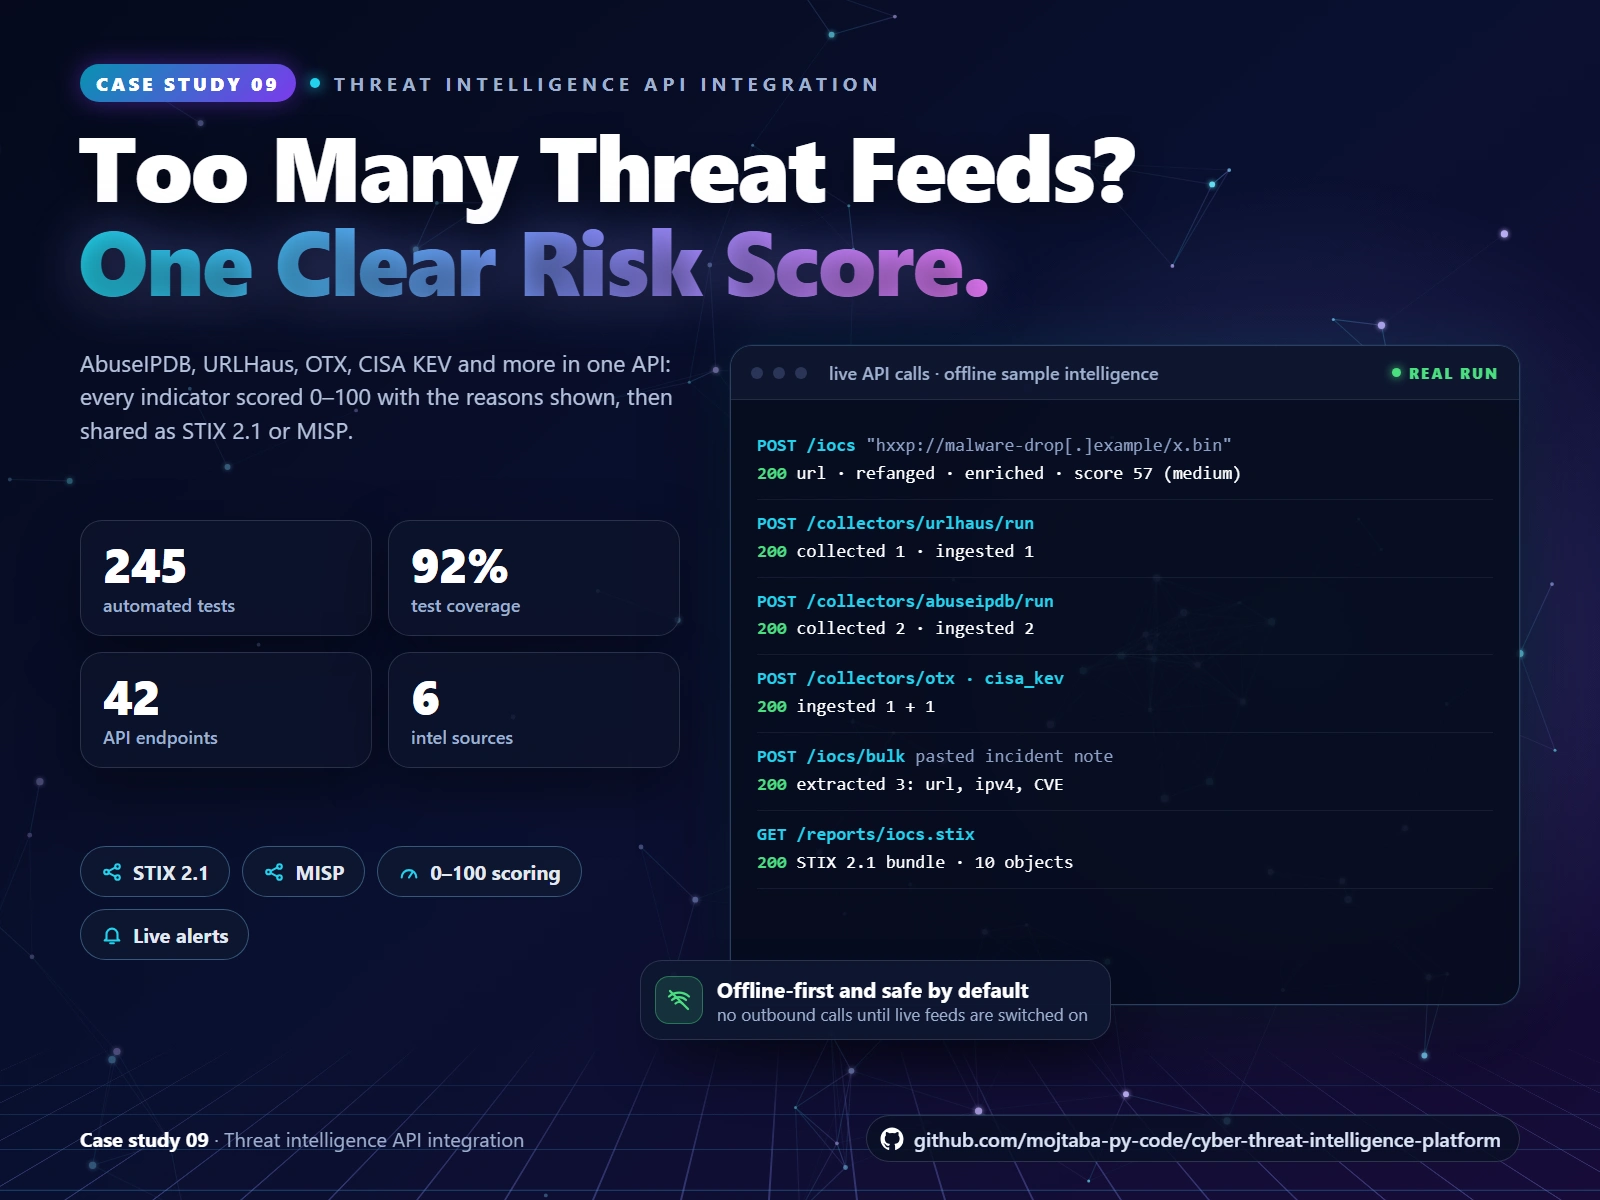
I built a threat intelligence platform that connects to six feeds through one API, turns every indicator into the same clean format, scores it 0-100 with the reasons shown, and shares it as STIX 2.1 or MISP.
The dashboard
9 indicators from four feeds and one pasted incident report, in one table sorted by risk.
Every value is defanged (hxxp[://], [.]) so nobody clicks a malicious link by mistake.
One-click export to CSV for people, or STIX 2.1 and MISP for other security tools.
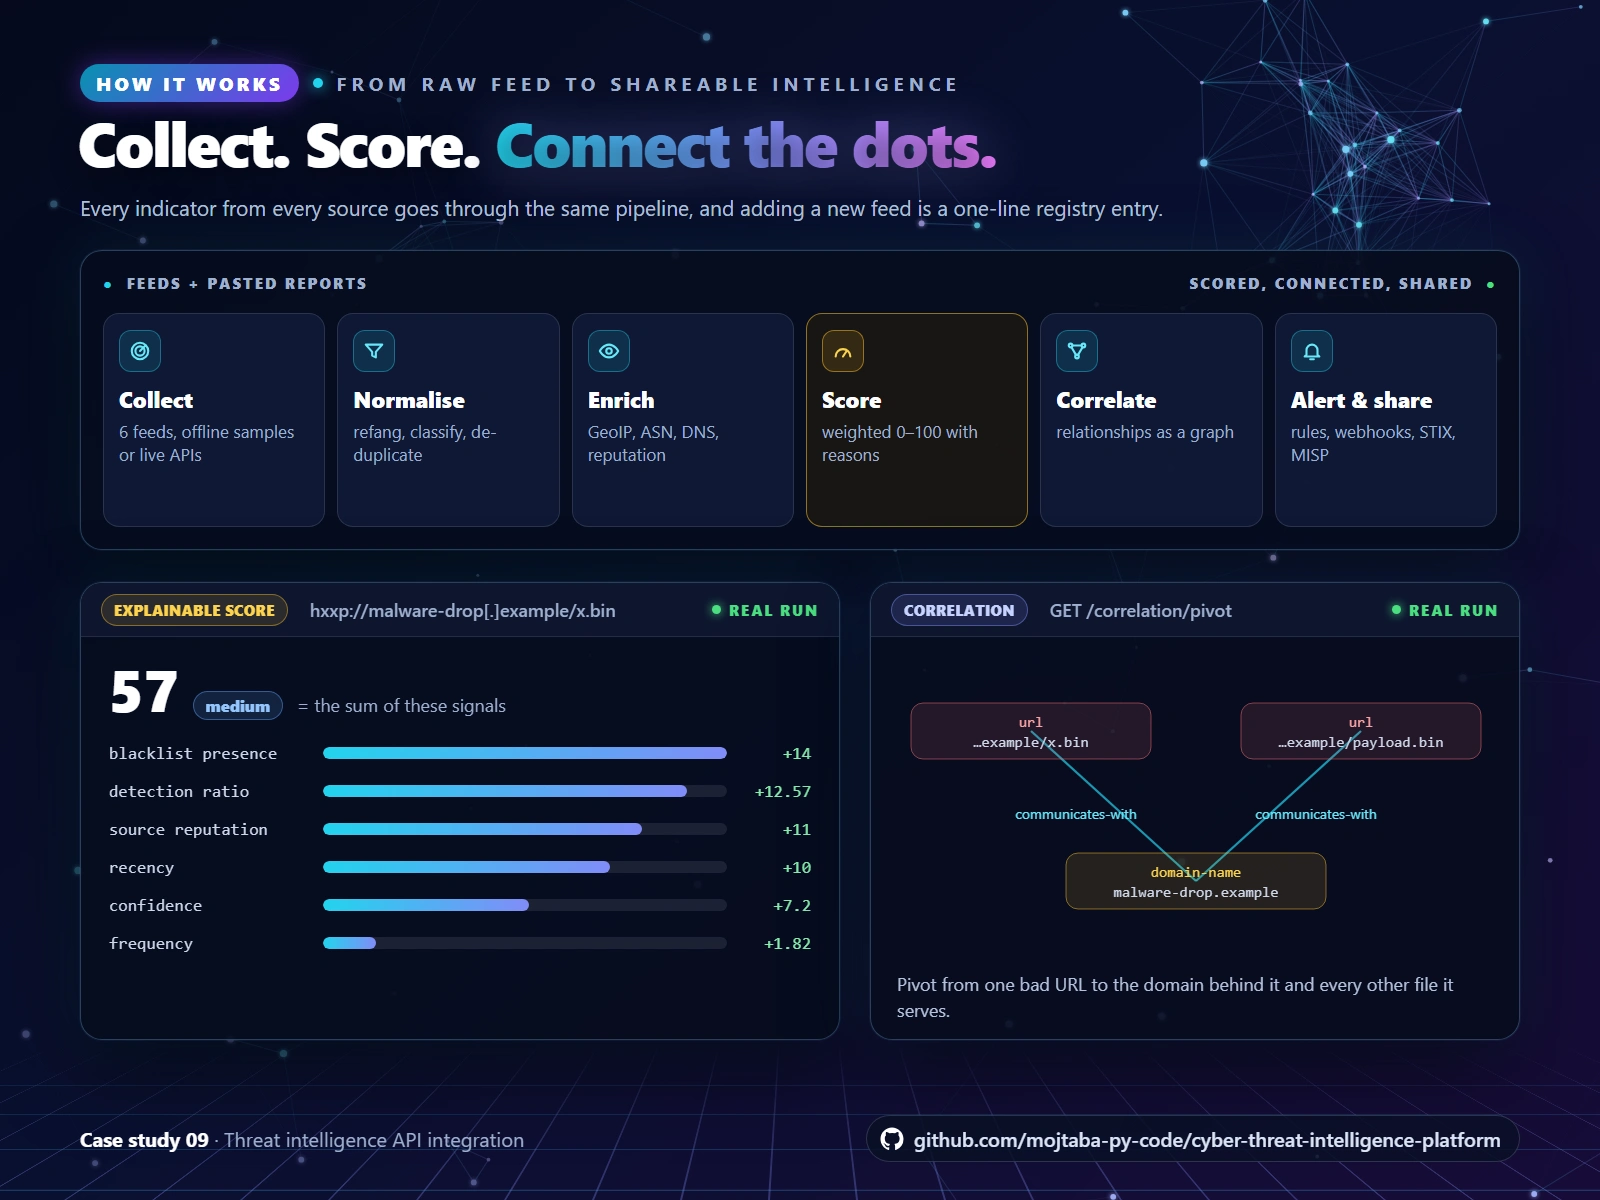
One pipeline for every feed, with a real explainable score (57 is the sum of its signals) and a real correlation pivot.
How it works
Collect: pluggable collectors for AbuseIPDB, URLHaus, MalwareBazaar, AlienVault OTX, CISA KEV and RSS advisories; offline samples by default, live APIs when keys are supplied.
Normalise: defanged values are refanged, classified (IP, domain, URL, hash, e-mail, CVE, ATT&CK technique) and de-duplicated. A pasted report gave 3 indicators, and the filename payload.exe was correctly ignored.
Enrich and score: GeoIP, ASN, DNS and reputation, then a transparent 0-100 score. The URL in the image scored 57: blacklist presence +14, detection ratio +12.57, source reputation +11, recency +10 and more.
Correlate: relationships are stored as a graph, so one bad URL leads to its domain and every other file it serves.
Alert: rules fire on every ingest and stream to the dashboard live, or to a webhook.
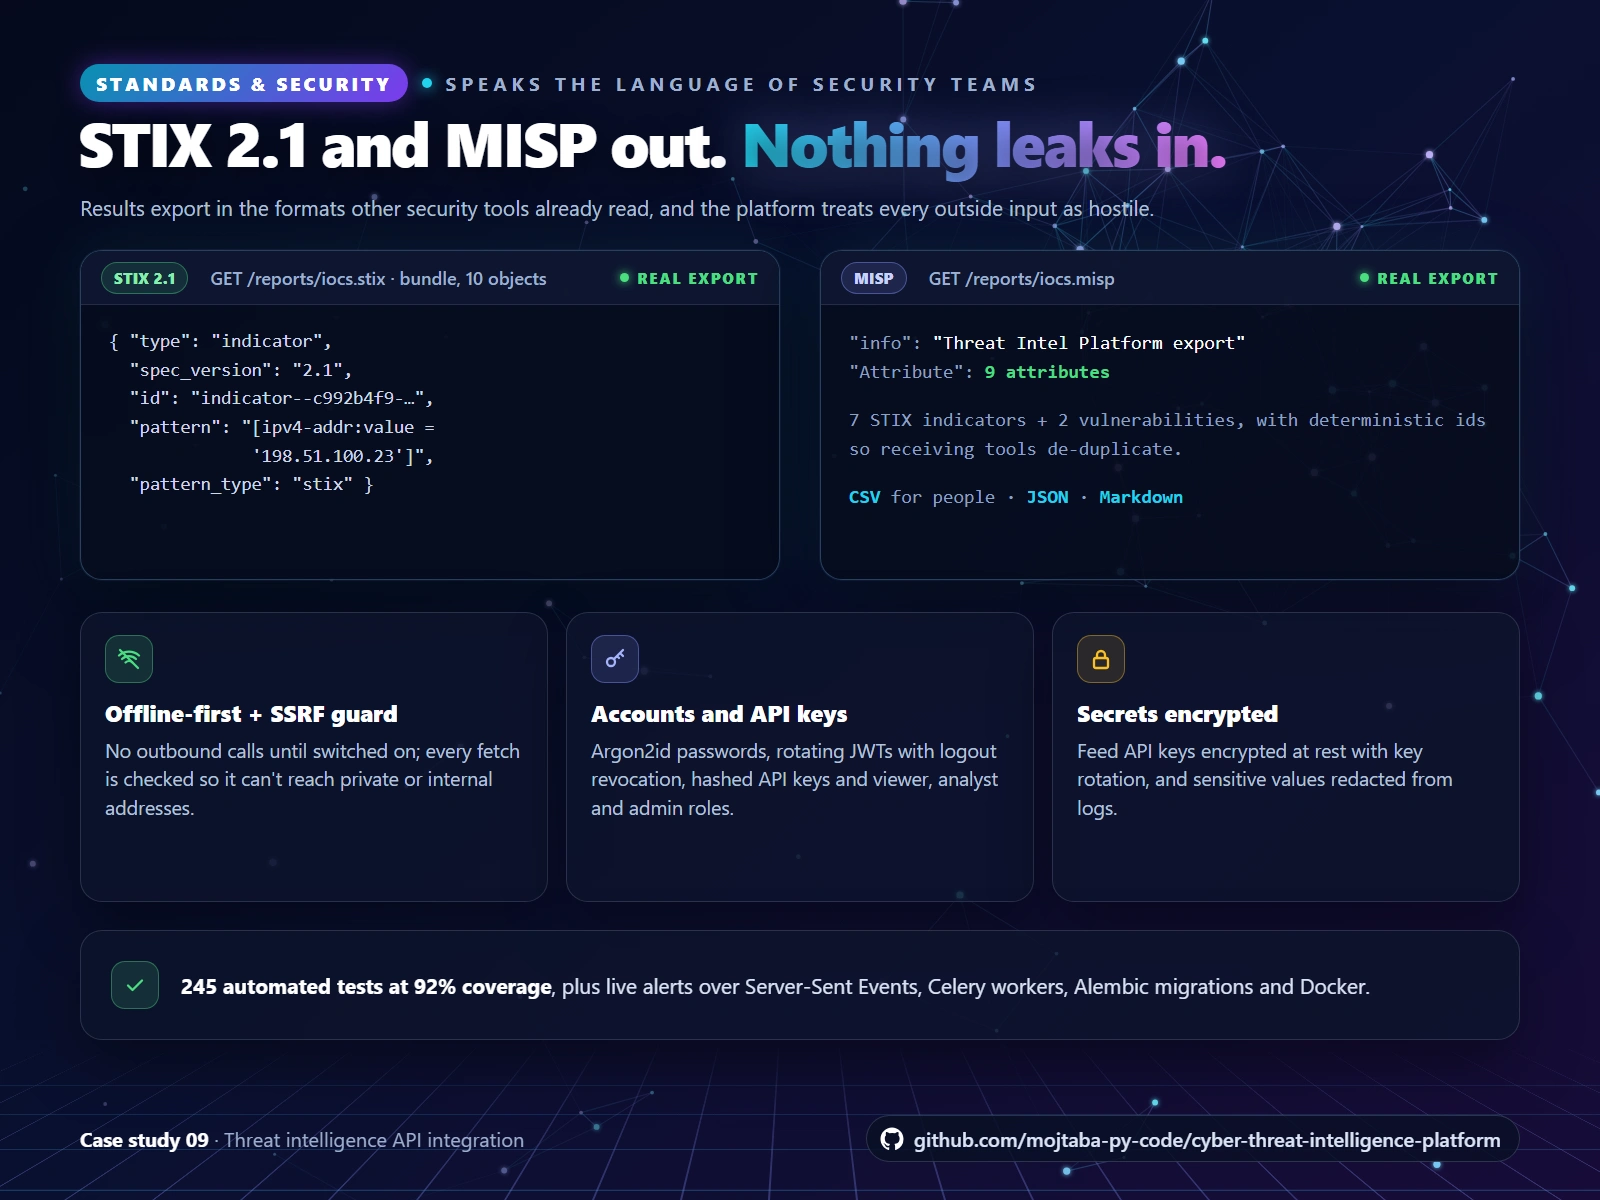
Real STIX 2.1 and MISP exports, offline-first collection behind an SSRF guard, and 245 tests at 92% coverage.
Standards and security
STIX 2.1 and MISP exports with deterministic ids, so receiving tools de-duplicate. The real export: a bundle of 10 STIX objects and a MISP event with 9 attributes.
Offline-first: no outbound calls until live feeds are enabled, and every fetch passes an SSRF guard that blocks private and internal addresses.
Accounts: Argon2id passwords, rotating JWTs with logout revocation, hashed API keys for automation, and viewer, analyst and admin roles.
Secrets encrypted at rest with key rotation, plus rate limiting, security headers and redacted logs.
245 automated tests at 92% coverage.
Tech stack: Python, FastAPI, async SQLAlchemy, PostgreSQL, Redis, Celery, networkx and Docker.
Need threat feeds or other security APIs combined into one tool? Send me a message with the sources you use today.
Like this project
Posted Oct 14, 2026
Collects indicators from 6 threat feeds, scores them 0-100 with clear reasons and shares them as STIX 2.1 or MISP. 245 tests, 92% coverage.