Small Business Cybersecurity Policy Pack

Almodther Amer Alfadel Khairallah

OVERVIEW
This sample demonstrates the structure of a practical cybersecurity policy pack for a fictional 25-person professional-services company using cloud email, laptops and remote work.
THE CHALLENGE
Small businesses often rely on generic templates that do not identify owners, approval steps or measurable implementation actions. The goal was to create clear operational policies that staff and managers could actually follow.
POLICY PACK STRUCTURE
Information Security Policy
Access Control, Password and MFA Policy
Acceptable Use Policy
Remote Work and BYOD Policy
Data Handling, Backup and Recovery Policy
Incident Response and Phishing Policy
Vendor Security and Patch Management Policy
Joiner-Mover-Leaver and Business Continuity Policy
SAMPLE ACCESS CONTROL REQUIREMENTS
Every user receives an individual account.
MFA is required for email, cloud storage, finance tools and remote administration.
Managers approve access before provisioning.
Privileged access uses a separate administrator identity and is reviewed quarterly.
Access is disabled promptly when a worker leaves.
INCIDENT RESPONSE STRUCTURE
The sample policy defines four severity levels, initial response targets, escalation owners, evidence-preservation steps and a lessons-learned review after closure.
IMPLEMENTATION TRACKER
The final pack converts policy into action by assigning owners and due dates for MFA completion, employee acknowledgement, backup restore testing, an incident tabletop exercise and privileged-access review.
DELIVERABLE FORMAT
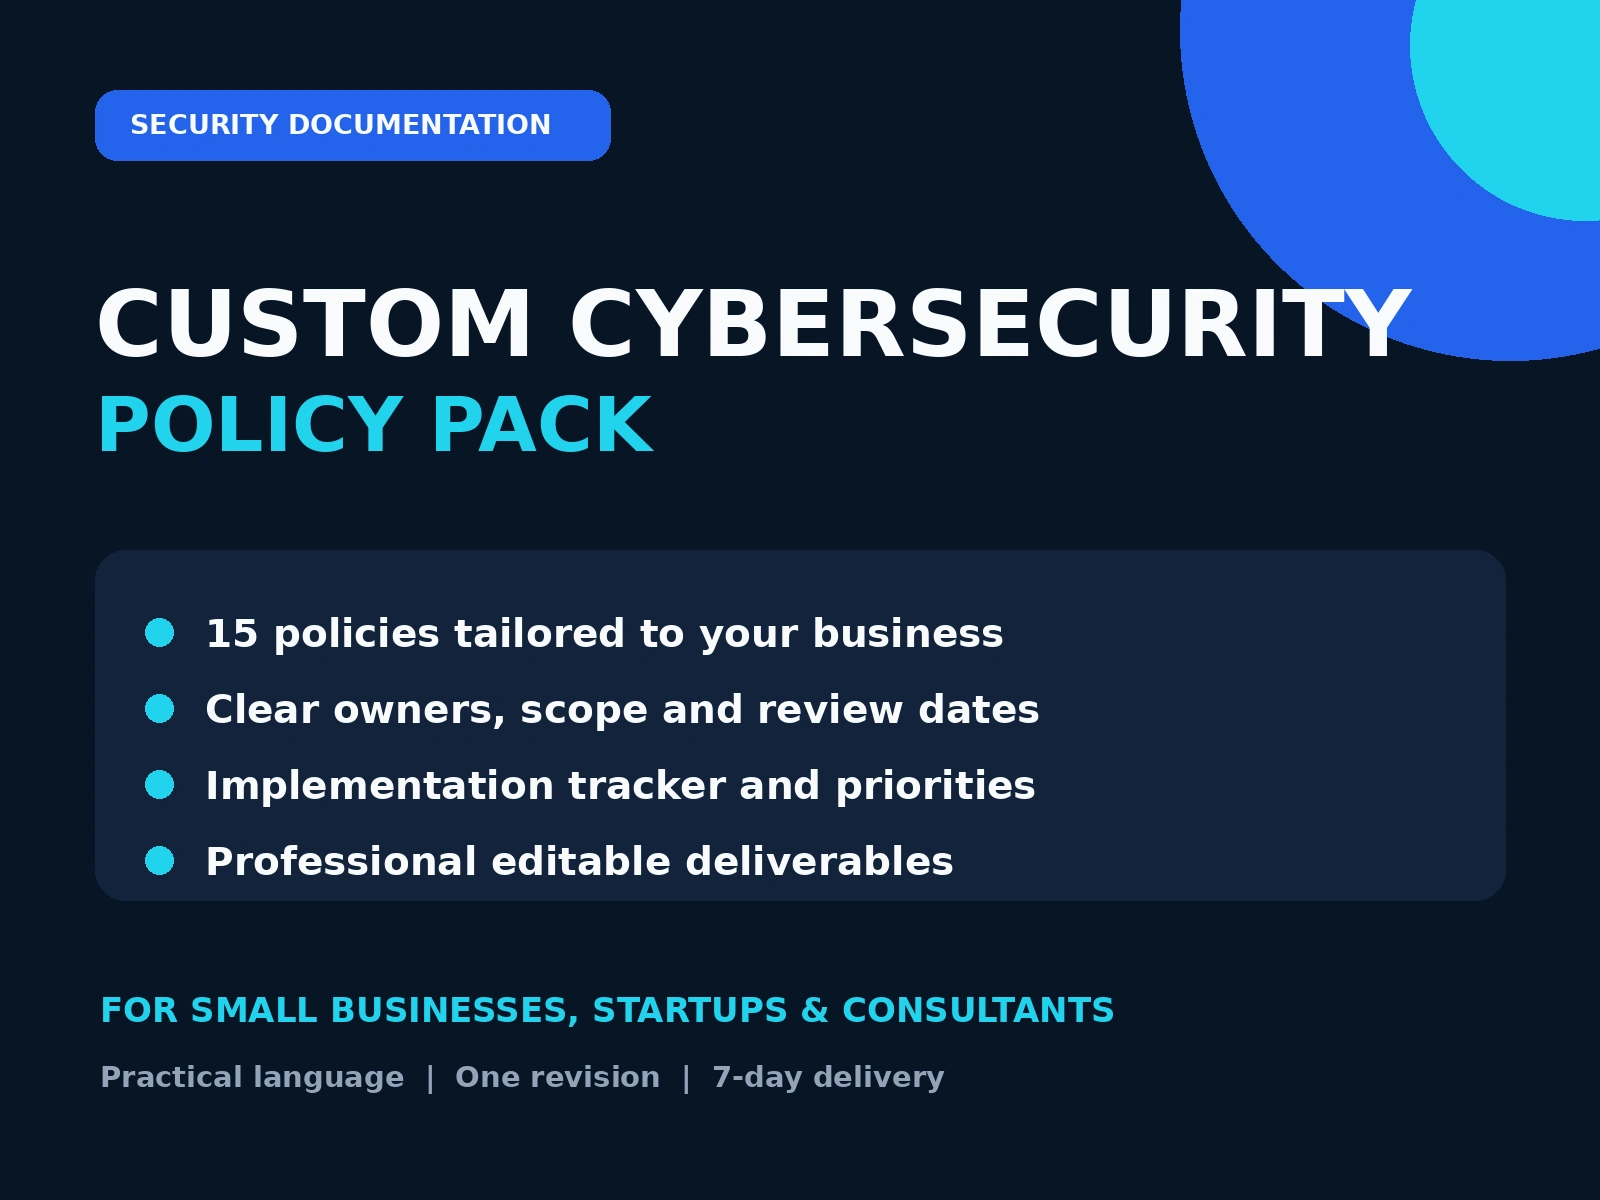
A client engagement can include up to 15 tailored policies, a policy register, an implementation tracker, editable Word files, PDF copies and one consolidated revision round.
SAMPLE NOTICE
This is a fictional portfolio demonstration. It is not legal advice, certification or evidence of work completed for a real client.
Like this project
Posted Sep 9, 2026
Sample policy pack with governance, access control, incident response and a practical 30-day implementation tracker.
Likes
0
Views
0