Linux Server Hardening: Security Review

Almodther Amer Alfadel Khairallah

OVERVIEW
This sample demonstrates a defensive security and health review for one fictional Ubuntu web server. It focuses on practical risk reduction without exploitation or destructive testing.
THE CHALLENGE
The server hosted a small company website but had accumulated avoidable exposure: password-based SSH access, an unused public database port, manual patching and an untested backup recovery process.
REVIEW SCOPE
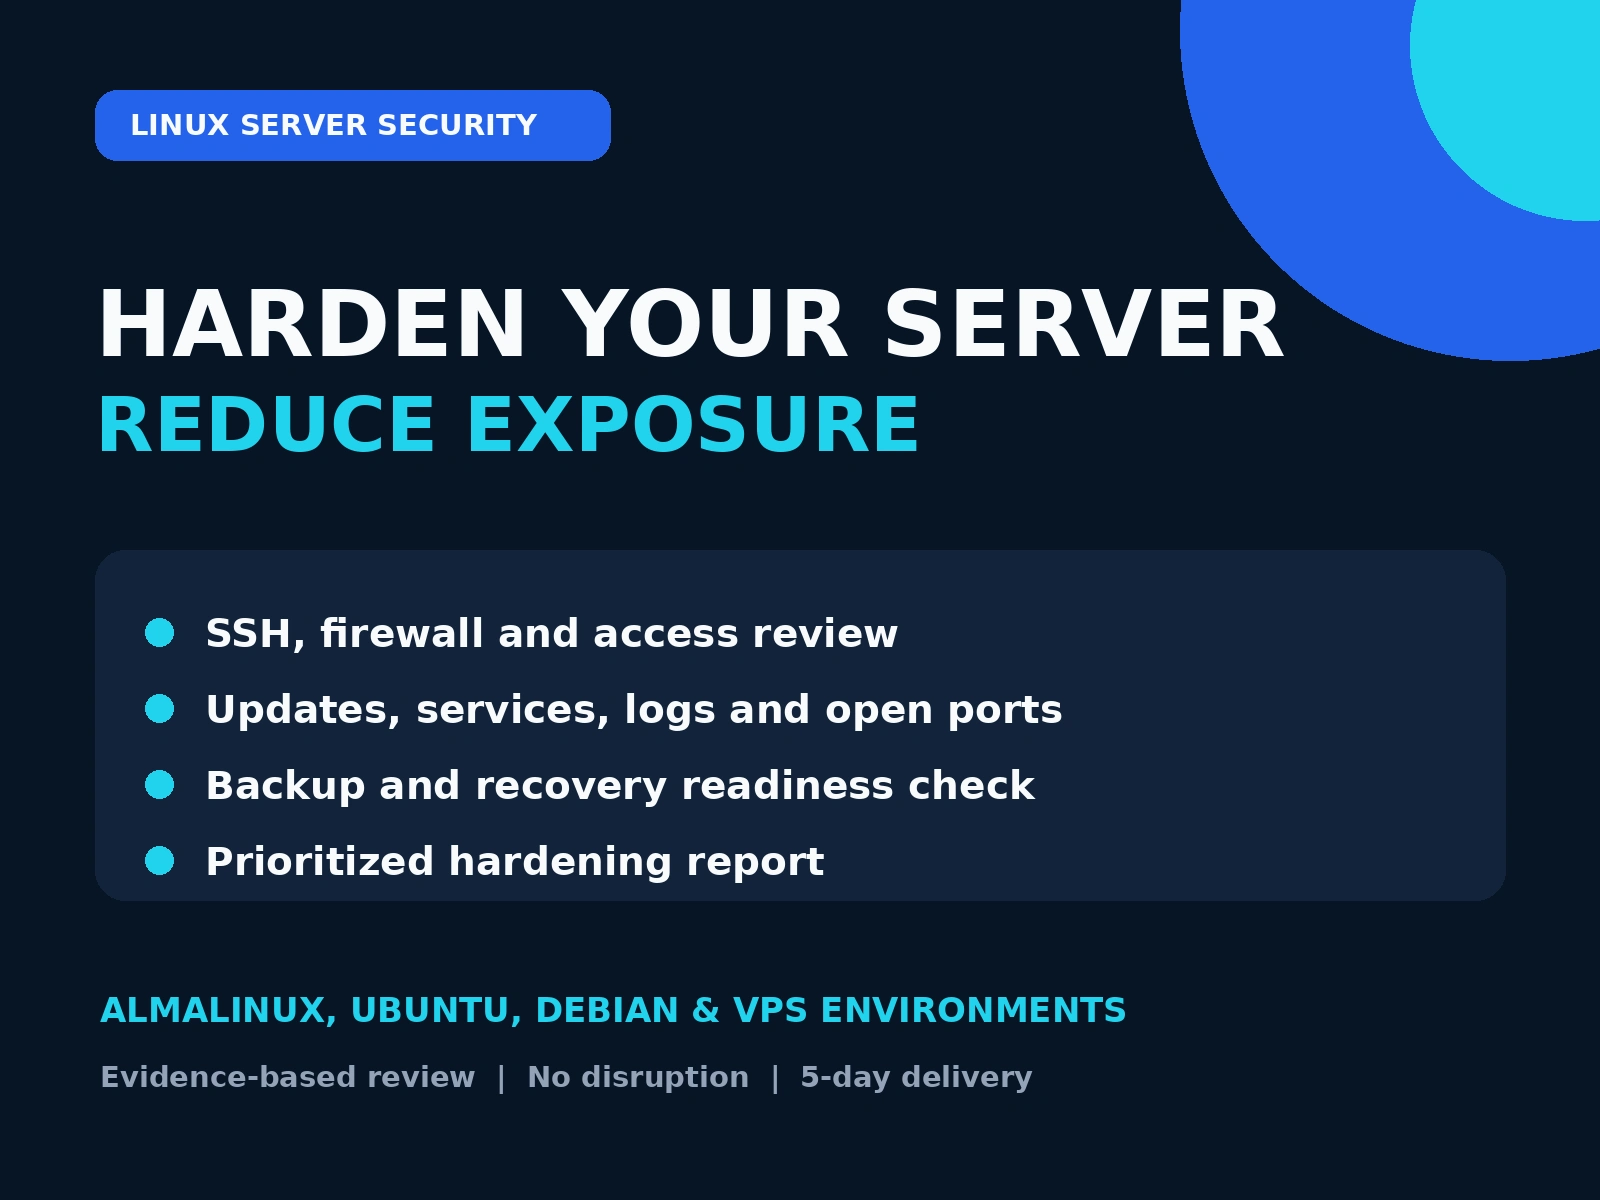
Operating-system update and support status
SSH, user, sudo and administrator access
Firewall rules, listening services and exposed ports
Web server and selected TLS settings
Authentication logs and failed-login activity
Backup and recovery readiness
PRIORITIZED FINDINGS
The fictional review identified two high-risk, three medium-risk and two low-risk findings. The highest priorities were administrative access controls and unnecessary public exposure.
APPROVED IMPROVEMENTS
Disabled SSH password login after confirming key access.
Restricted the unused public database port.
Enabled security-only automatic updates.
Added a failed-login alert threshold.
Documented active privileged accounts and owners.
VERIFICATION
Every change was reversible and discussed before implementation. Application health checks passed, a new SSH key session was tested before the original session closed, and rollback steps were documented.
30-DAY ACTION PLAN
The sample handover assigns owners and target dates for a backup restore test, privileged access review, monitoring verification and web security-header deployment.
SAMPLE NOTICE
This is a fictional portfolio demonstration. It shows my review process and reporting quality and is not presented as work completed for a real client.
Like this project
Posted Sep 9, 2026
Sample security review covering SSH, firewall exposure, patching, logs, backups and five approved hardening improvements.