Hamza Ghebrich
AI Security & DevSecOps Engineer | Cloud Automation
- 1
- Followers

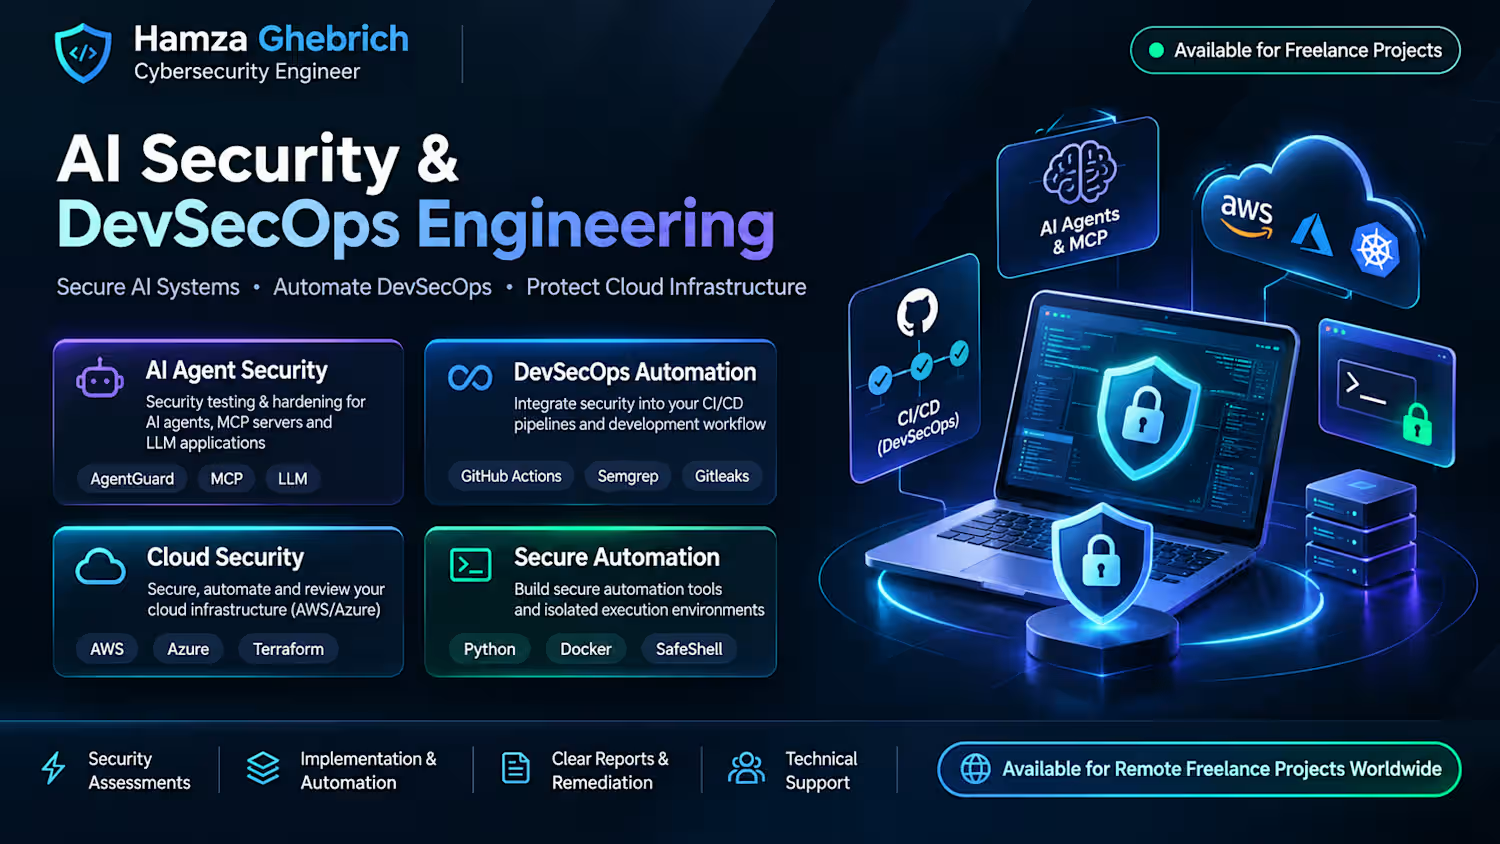
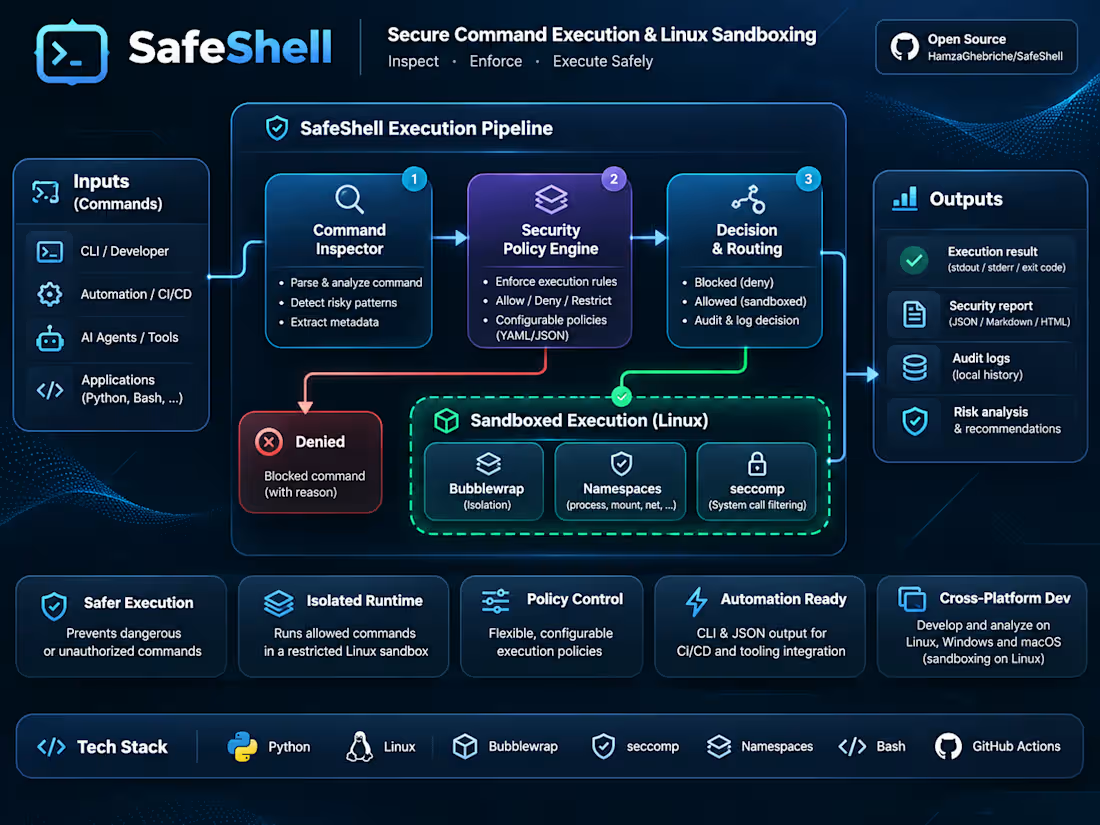
SafeShell | Secure Command Execution & Linux Sandboxing (https://github.com/HamzaGhebriche/SafeShell)
SafeShell is an open-source Python security tool I developed to inspect potentially dangerous shell commands, enforce execution policies, and run permitted commands within a restricted Linux sandbox.
The project focuses on improving command execution safety in development environments, automation workflows, and security-sensitive applications.
🔐 Key Features
1. Command Security Analysis
Inspects shell commands before execution.
Identifies potentially dangerous command patterns.
Generates structured findings and risk information.
Supports deterministic command analysis without executing the submitted command.
2. Secure Linux Sandboxing
Uses Bubblewrap and Linux security controls to restrict command execution.
Implements Linux namespaces and seccomp-based restrictions.
Reduces access to host resources through controlled filesystem and runtime configurations.
Refuses protected execution when required security mechanisms are unavailable.
3. Security Policies & Access Control
Enforces configurable offline execution policies.
Supports explicit authorization for permitted operations.
Prevents approvals from overriding hard security restrictions.
Provides structured execution decisions and status information.
4. Security Automation & Auditing
Offers a Python command-line interface.
Supports JSON output for integration with automation workflows.
Records local execution metadata for review.
Provides timeout and output-size controls.
5. Cross-Platform Development
Supports command inspection and policy management on Linux, Windows, and macOS.
Provides protected execution on supported Linux environments.
Includes automated validation through CI pipelines.
Technologies: Python, Linux, Bubblewrap, seccomp, Linux Namespaces, Bash, GitHub Actions, JSON, Security Automation.
My Role: Independent Developer & Security Engineer.
Project Type: Open-source security tool.
Current Status: Experimental alpha release (v0.1.0-alpha).
SafeShell has undergone automated testing but has not received an independent security audit. It is not intended to serve as a production-grade security boundary.
0
17
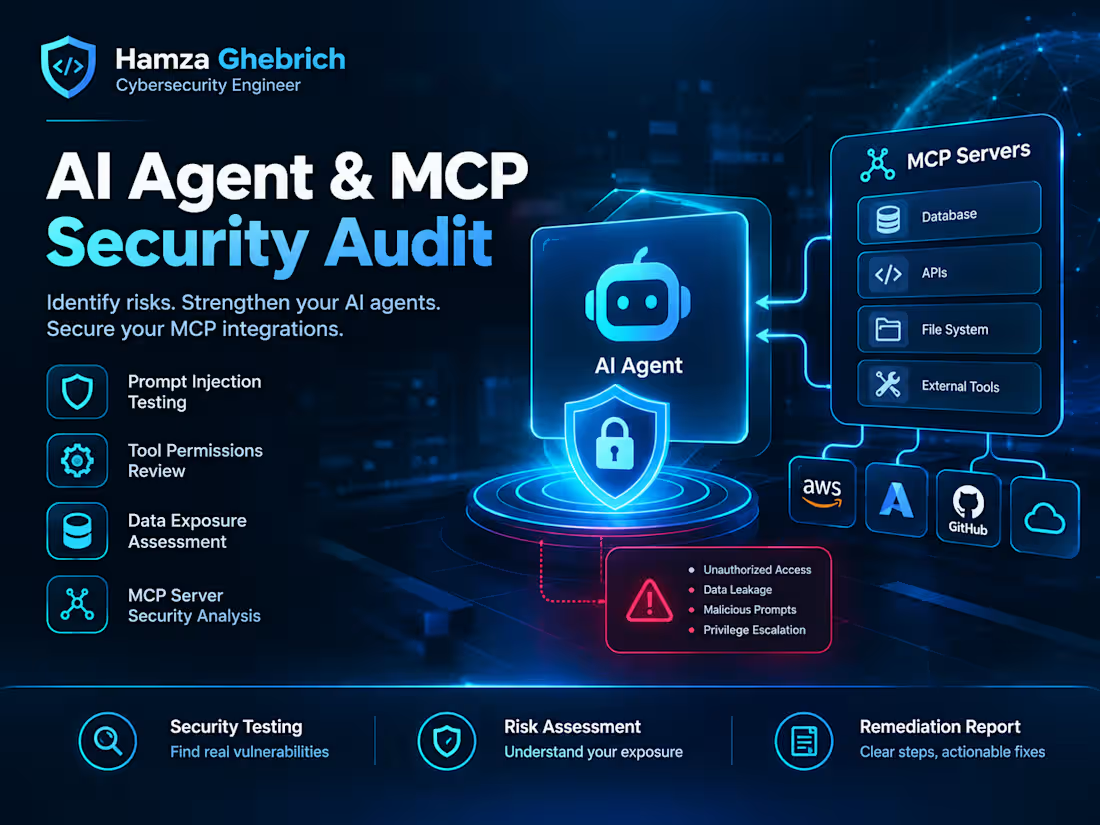
MCP Security Auditor | AI Agent & MCP Server Security (https://github.com/HamzaGhebriche/mcp-security-auditor)
MCP Security Auditor is an open-source security analysis tool I developed to help engineers identify security risks in Model Context Protocol (MCP) servers and AI-agent integrations.
As AI agents increasingly connect to external tools, APIs, and sensitive data, securing these integrations becomes essential.
I designed and developed MCP Security Auditor to automate security configuration reviews, identify potentially dangerous implementation patterns, and generate actionable security reports.
Key Features:
🔐 MCP Security Analysis
Detects risky authentication and authorization configurations.
Identifies potentially unsafe tool permissions and execution patterns.
Reviews filesystem access and security boundaries.
🤖 AI Agent Security
Analyzes security configurations used in MCP integrations.
Identifies potentially insecure connections between AI agents and external tools.
Supports security reviews of AI-powered applications.
⚙️ Automated Security Auditing
Static analysis of Python code and configuration files.
Automated security findings with severity classifications.
Security reports in JSON, HTML, Markdown, and SARIF formats.
Configurable security policies and risk scoring.
🚀 DevSecOps Integration
Supports automated security checks in development workflows.
Helps developers identify security issues earlier.
Provides actionable findings to support remediation.
Technologies: Python, MCP, Static Application Security Testing, Security Automation, GitHub Actions, JSON, YAML.
Business Value: Helps development teams review MCP integrations, identify risky configurations, and introduce repeatable security checks into their development processes.
My Role: Independent Developer & Security Engineer.
Project Type: Open-source cybersecurity tool.
0
24
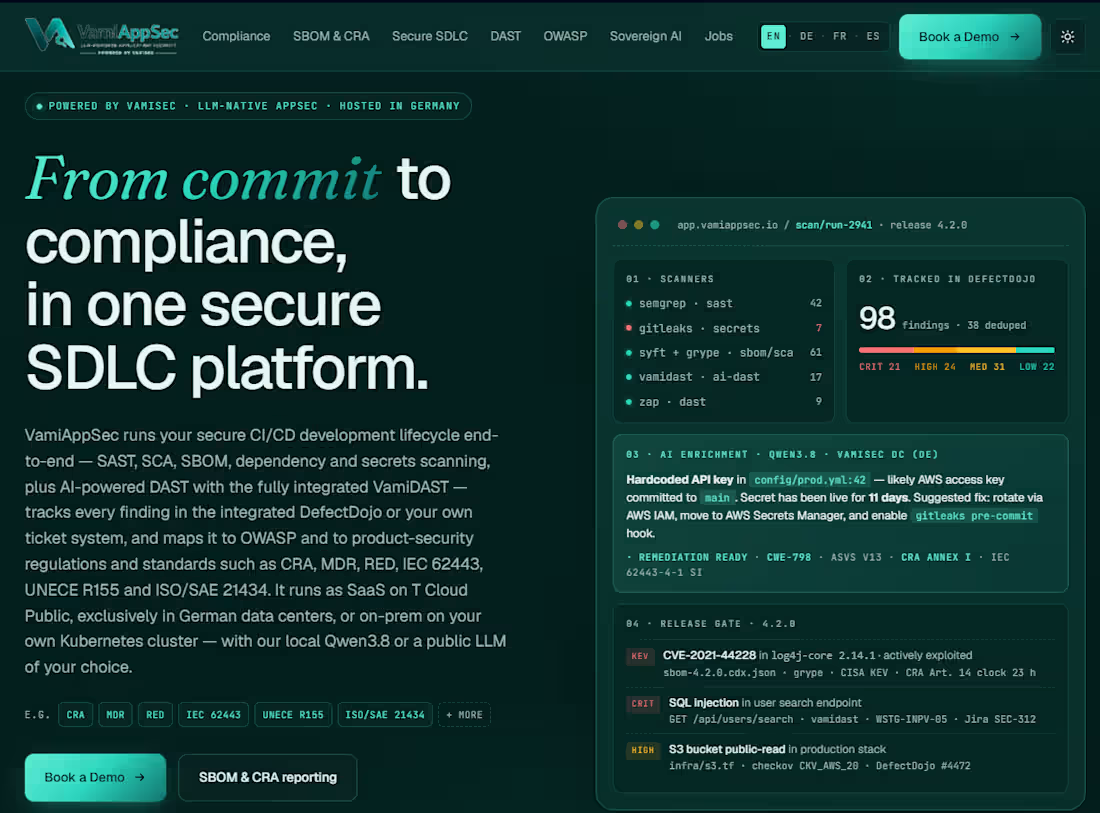
VamiAppSec | AI-Powered Application Security Platform (https://vamiappsec.com/#top)
VamiAppSec is an AI-assisted application security platform developed during my professional experience at VamiSec GmbH.
I contributed to integrating automated security analysis into development workflows, combining multiple security scanning technologies with AI-assisted vulnerability analysis.
My contributions included:
• Integrating SAST, SCA, and secrets detection tools.
• Automating security scanning through CI/CD pipelines.
• Implementing Infrastructure-as-Code security checks.
• Supporting SBOM generation and dependency analysis.
• Developing security findings aggregation and reporting workflows.
• Integrating AI-assisted vulnerability triage and remediation guidance.
Technologies: Python, GitHub Actions, Semgrep, Gitleaks, Checkov, Syft, Grype, LLMs, DevSecOps.
This experience strengthened my expertise in application security engineering, security automation, and AI-assisted DevSecOps.
0
34
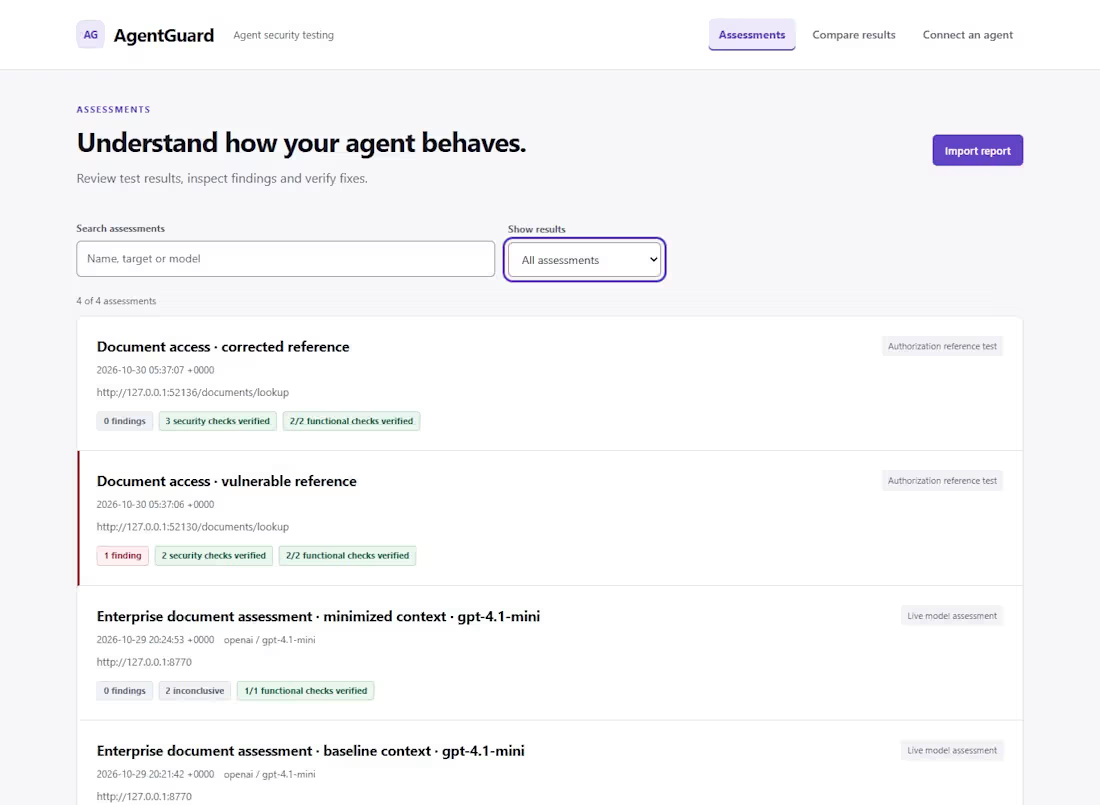
AI Agent Security Testing & Assessment | AgentGuard (https://github.com/HamzaGhebriche/AgentGuard)
AgentGuard is an open-source AI agent security testing tool designed to help developers assess the security of AI-powered applications and agentic systems.
I developed AgentGuard to support structured security assessments of authorized AI-agent endpoints, identify security weaknesses, and verify whether implemented fixes address the observed issues.
Key capabilities include:
• AI-agent endpoint security assessments.
• Testing of authorization and access-control behavior.
• Security findings with supporting evidence.
• Comparison of vulnerable and corrected application behavior.
• Local dashboard for reviewing and exporting security reports.
• Automated security testing using Python.
The project helps development teams understand security risks in their AI applications and validate specific security improvements.
Technologies: Python, AI Agent Security, LLM Security, API Security, Security Automation.
Project: AgentGuard — Open Source Security Tool.
0
42