

Microsoft 365 & Azure Solutions Architect
- $5k+
- Earned
- 2x
- Hired
- 5.0
- Rating
- 16
- Followers
Microsoft 365 & Azure Solutions Architect


Cloud Security Engineer · AWS, Azure & M365


Fusion UX Doctor is an AI-powered webpage auditor built entirely in Fusion by Builder.io (http://Builder.io). Paste any URL and instantly get a complete UX, Accessibility, and Performance analysis, followed by AI-generated layout improvements built as real Fusion components.
This project creatively uses Fusion’s visual canvas to turn audits into an interactive experience with animated cards, a clean Before/After comparison, and on-canvas component regeneration. The innovation lies in how AI doesn’t just evaluate a design, it rebuilds it directly in Fusion, proving what’s possible when design, code, and intelligence come together.
Live Project: https://b5b76db448604e6099a747c1f7beab26-main.projects.builder.my/
(https://b5b76db448604e6099a747c1f7beab26-main.projects.builder.my/)#builderchallenge #builtwithfusion
21
456


Expert cloud & platform consultant building AI platforms
Expert cloud & platform consultant building AI platforms

Architected an enterprise Kubernetes platform on Azure AKS for a fintech company running 40+ microservices. Traffic enters through Application Gateway with WAF v2 policies and Azure Firewall before reaching the AKS cluster inside a hub-spoke VNet. ArgoCD manages all deployments through GitOps with automatic drift detection and self-healing. ACR stores container images built by Azure DevOps Pipelines with integrated vulnerability scanning. Workloads connect to Cosmos DB, PostgreSQL Flexible Server, and Redis Cache through private endpoints. Azure ML handles fraud detection model inference called directly from within cluster pods. Entra ID with Managed Identities provides passwordless auth across all services.
0
107

Designed and deployed a multi-account AWS landing zone using Control Tower and Organizations for a healthcare SaaS company handling PHI data. The architecture separates management, security, network, and workload accounts with dedicated IAM boundaries. Traffic routes through CloudFront and WAF into a Transit Gateway hub before reaching production VPCs running ECS Fargate workloads. Security Hub aggregates findings from GuardDuty, Inspector, and AWS Config across all accounts. CloudTrail feeds into EventBridge for real-time alerting through SNS. All encryption managed through a centralized KMS account. Infrastructure provisioned entirely with Terraform and Terragrunt modules. Achieved SOC 2 Type II and HIPAA compliance within 90 days.
0
117

I built a production-ready serverless LLM API on GCP designed for low cost, strong security, and fast inference. Requests flow through CDN, load balancing, WAF, and API management before hitting a Cloud Run FastAPI service that handles prompts, session history, caching, and model routing. The system switches between Gemini 2.5 Pro for deep reasoning and Gemini Flash for fast responses, with RAG support using Vector Search over 768-dim embeddings. Data is stored in Firestore, cached in Redis, and logged to BigQuery. Everything is secured with VPC Service Controls, Workload Identity, KMS, Secret Manager, and DLP. CI/CD is fully automated with Terraform and Cloud Build using canary rollouts and auto-rollback on SLO violations. At around 50K requests per day, the platform runs at about $1K/month and scales to zero when idle.
0
118

Here's how I'd build a scalable ticketing backend with Supabase & Stripe.
The backend is where everything lives or breaks. Supabase handles auth and Row Level Security out of the box, Postgres enforces ticket inventory and access at the database level, and Stripe Checkout processes payments with webhooks that keep everything in sync. Capacity limits, discount logic, and user access all of it stay consistent when real traffic hits. Built to scale without needing a full rewrite six months down the road.
0
105

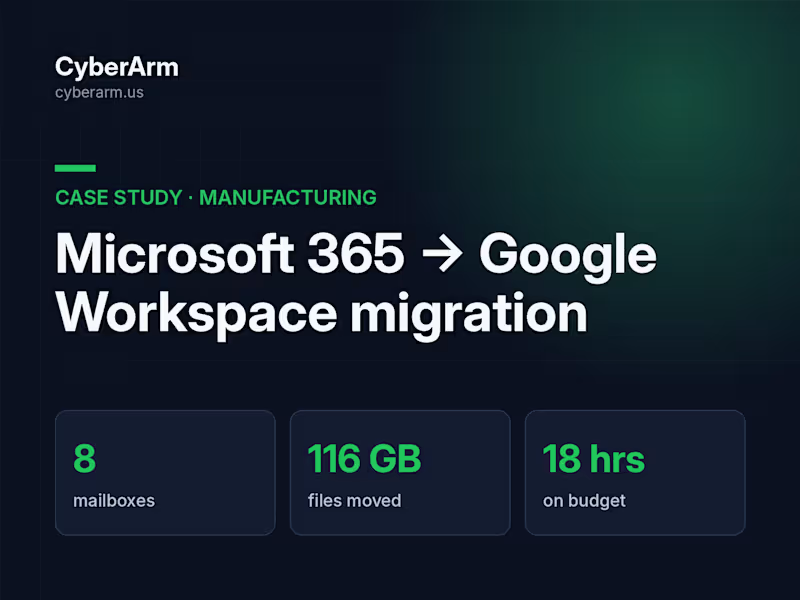
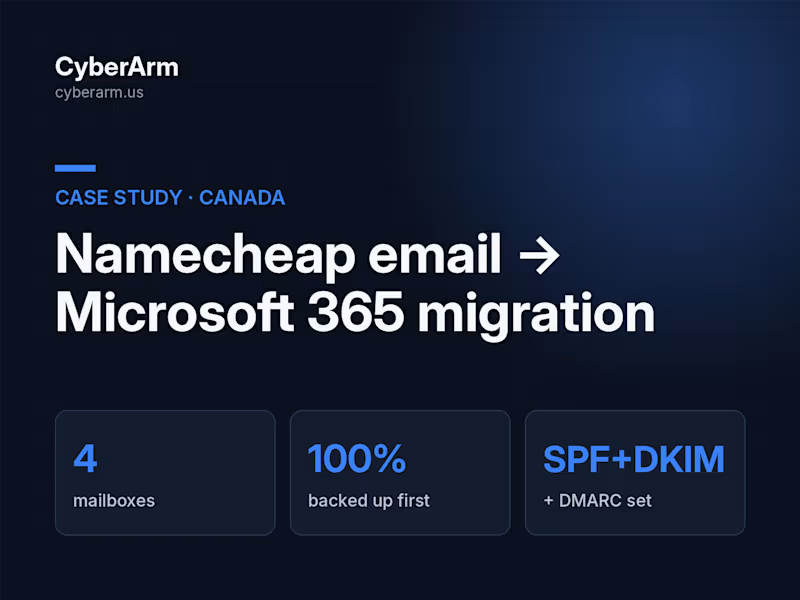
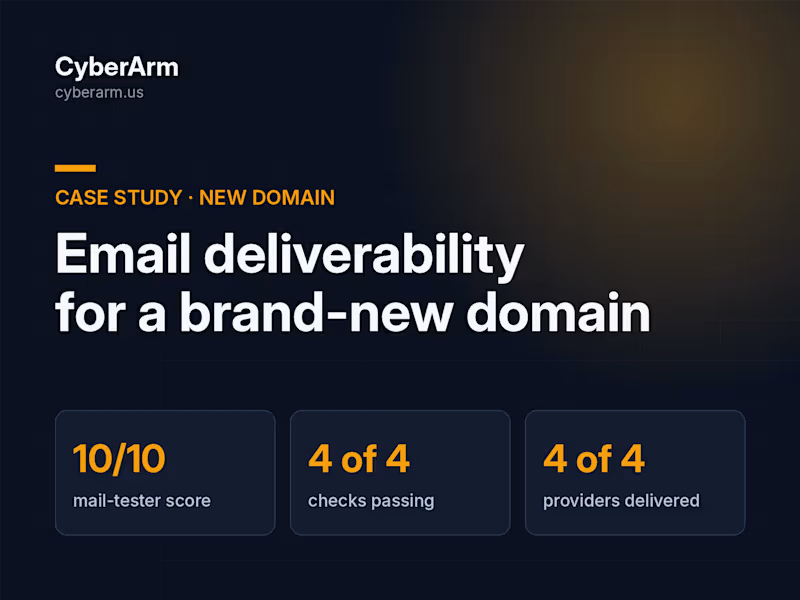
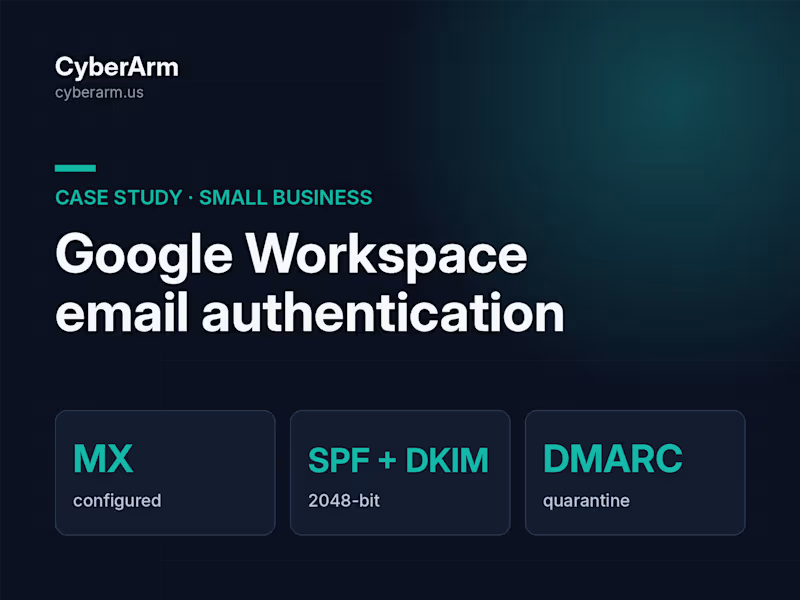
M365 & Google Workspace security engineer, Orlando FL


Full-Stack Developer & UX/UI Designer | Lovable Expert
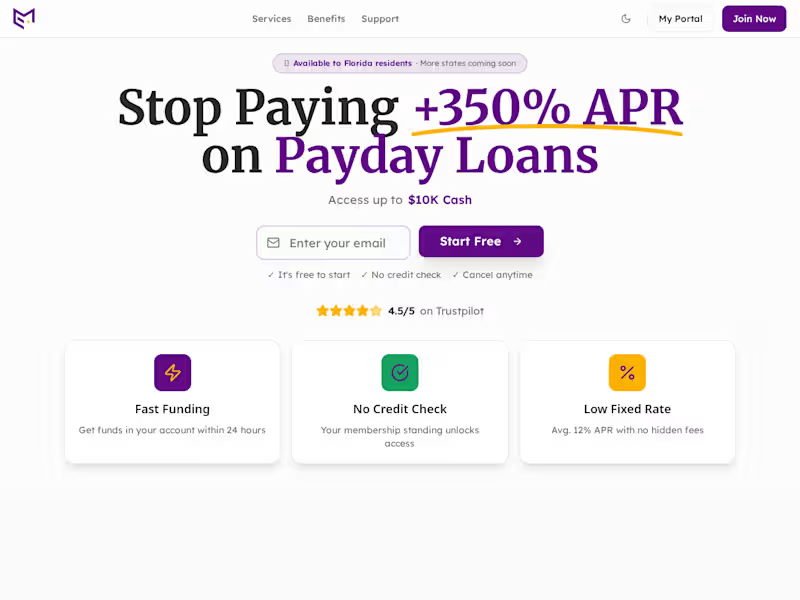
Makaya Equity is an end-to-end membership fintech and lending ecosystem engineered to automate member underwriting, identity verification, and capital workflows.
Core Technical Specs & Features:
Proprietary Underwriting Engine : Custom algorithmic risk-assessment model that ingests live banking data, cash-flow patterns, and repayment history to generate an instant, proprietary creditworthiness score.
Plaid Bank Integration & OAuth: Instant bank account verification, real-time balance checks, transaction categorization, and automated ACH transfer verification.
Payroll Direct Connect: Secure verification of member income and employment status via payroll API linking.
Conversational WhatsApp AI Assistant: In-chat AI concierge on WhatsApp capable of answering member queries, delivering payment reminders, checking loan status, and guiding applicants through onboarding.
Automated KYC & Identity Verification: Dual-layer identity verification with automated verification flows and an admin manual-review fallback pipeline.
Member Financial Dashboard: Interactive portal tracking active loans, contribution balances, payment schedules, transfer history, and membership benefits.
Admin Compliance & Risk Center: Granular back-office console for staff, compliance onboarding, disclosure management, and portfolio risk monitoring.
Security & Regulatory Safeguards: Strict role-based access control (RBAC), end-to-end data encryption for PII, and automated regulatory disclosure workflows.
1
296
What happens when your Gmail inbox meets luxury fashion resale?
The Problem:
The average consumer has thousands of dollars trapped in their closet, with all the original purchase data buried in messy email receipts. Cross-listing to resale marketplaces remains tedious, disjointed, and manual.
The Solution (MVP Prototype):
I designed and developed Reweave as an end-to-end MVP prototype to explore how automated receipt parsing, algorithmic wardrobe valuation, and multi-channel syndication can coexist inside an elevated, consumer-friendly interface.
What I Built (Design & Engineering Highlights)
🧪 1. Interactive Receipt-to-Listing Pipeline (MVP Core Flow)
Developed a tactile 3-stage scrubbing engine that simulates the ingestion lifecycle: raw email receipt → structured entity extraction (brand, retail price, fabric composition) → pre-populated listing drafts ready for marketplace syndication.
📐 2. Multi-State Item Architecture
Architected a comprehensive design system around item lifecycles, establishing visual patterns and UI states for:
Active Valuation: Real-time secondary market pricing & appreciation trends
Cross-Listed Sync: Multi-channel status badges & unified offer feeds
Demand-Driven Price Drops: Suggested discount thresholds based on market velocity
Sold & Settlement: Automated earnings reconciliation and buyer receipt generation
🧮 3. Dynamic Closet Net Worth Calculator
Engineered a responsive valuation model allowing users to adjust wardrobe volume and brand affinities to instantly project untapped portfolio value.
🎨 4. Elevated Editorial Design System
Intentionally broke away from generic tech-SaaS tropes. Built custom semantic design tokens featuring warm off-white tones, refined editorial typography, and high-fidelity micro-interactions suited for luxury fashion tech.
The Takeaway:
This MVP validates that complex data workflows (inbox scraping, marketplace taxonomy mapping, and valuation math) can be packaged into an intuitive, visually captivating consumer product.
🚀 Looking to validate an ambitious zero-to-one product idea or build an interactive MVP prototype for investors and users? Let’s talk.
0
28
Beyond the ordinary. A closer look at the brand identity and digital showcase for Kilter®.
We blended brutalist typography, electric editorial tones, and real-time chrome 3D to create an experience that feels tactile, fluid, and cinematic.
Let's connect 😍 !!
0
33
Maison Ambre — Luxury Fragrance E-Commerce (Concept Build)
A sleek, editorial-style e-commerce storefront for a fictional luxury fragrance house, built to demonstrate the aesthetic and functionality of high-end fashion and beauty sites like Maison Raksha and Material Good.
The design brief was luxury: generous whitespace, large product photography, serif display type, and a warm cream-and-espresso palette. Key features include a filterable product collection with sorting, detailed product pages (scent notes, ingredients, sizing), a persistent shopping bag, and a concierge-style purchase flow for brands that prefer off-site payment handling — common in the resale and luxury space. Fully responsive, with a dedicated mobile layout.
Delivered as a complete, working build: home, collection, product detail, cart/concierge checkout, and brand story pages, plus desktop and mobile showcase assets.
Live demo available on request.
0
34

Senior DevOps/SRE | AWS, Kubernetes & Terraform Expert


Designed and developed a Command Line Interface (CLI) security tool that leverages the Google Gemini API (gemini-2.5-flash) to perform advanced, AI-driven vulnerability analysis on Python codebases. This tool acts as an automated security engineer, scanning source code to detect critical flaws before they reach production.
The scanner parses Python files and evaluates them against a detailed security prompt to identify vulnerabilities such as SQL injection, hardcoded secrets (API keys and database passwords), weak cryptography (e.g., MD5 hashing), insecure deserialization, and improper input validation. It outputs a structured, color-coded terminal report assigning severity ratings (🔴 High, 🟠 Medium, 🟢 Low) to each finding. For every detected issue, the tool provides the vulnerability type, the exact line number, a concise explanation of the risk and potential impact, and actionable remediation advice with secure code fixes.
The architecture is built on a lightweight Python foundation using a virtual environment for dependency isolation. It utilizes the google-generativeai SDK for model interaction and python-dotenv for secure environment variable management, ensuring API keys are never hardcoded. This project demonstrates the ability to integrate cutting-edge Large Language Models (LLMs) into traditional DevSecOps workflows, providing enterprise-grade security scanning capabilities directly within the developer's terminal.
0
59

Architected and implemented a production-grade, fully automated DevOps platform on AWS, covering the entire software delivery lifecycle from code commit to live deployment. The platform integrates eight tightly coupled layers: a developer workflow built on Git, Docker Compose, and pull requests; a GitHub Actions CI/CD pipeline with dedicated workflows for continuous integration, deployment, Terraform provisioning, security scanning, and semantic releases; and a multi-tool security gate enforcing SAST, SCA, IaC scanning, container analysis, OWASP ZAP, and CodeQL checks before any artifact progresses.
Infrastructure is provisioned as code using Terraform, deploying a multi-AZ VPC, an EKS cluster, ECR repositories, RDS MySQL, an ALB with WAF, and IAM OIDC integration on AWS. Applications are packaged with Helm Umbrella Charts and deployed to Kubernetes with Horizontal Pod Autoscaling (2–8 replicas) and RBAC-enforced NetworkPolicies. GitOps state management is handled by ArgoCD, providing continuous reconciliation, drift detection, auto-sync, and self-healing across all application sets.
Observability is delivered through a dual-stack setup: a metrics pipeline (Prometheus → Grafana → Alertmanager → Slack) and a log aggregation pipeline (Filebeat → Logstash → Elasticsearch → Kibana). Releases are fully automated using Semantic Release with Conventional Commits, producing versioned GitHub Releases and Docker image tags without manual intervention.
0
105

Cloud Security specialist,AWS,AZURE,GCP,IAM,ENTRA ID,MFA
Cloud Security specialist,AWS,AZURE,GCP,IAM,ENTRA ID,MFA


View more →

"Fortifying digital defenses strategically."
"Fortifying digital defenses strategically."


View more →