
AI Security & DevSecOps Engineer | Cloud Automation
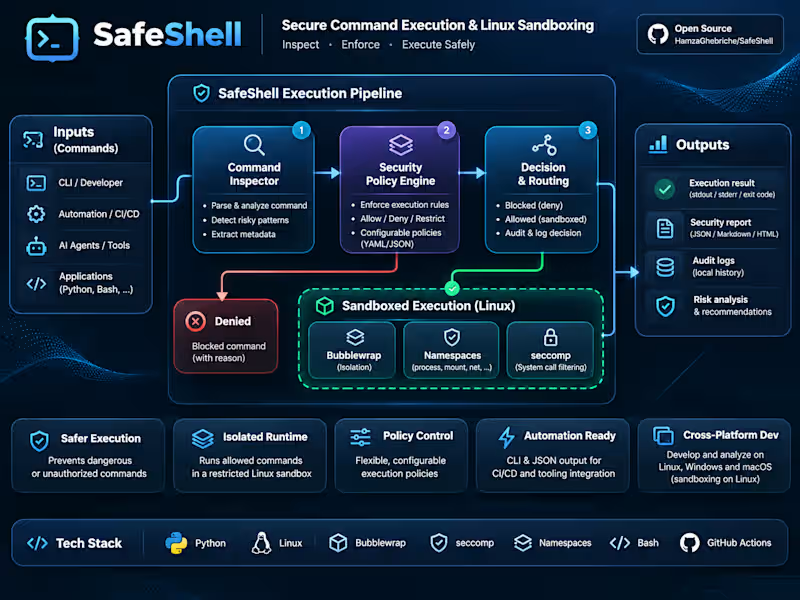
SafeShell | Secure Command Execution & Linux Sandboxing (https://github.com/HamzaGhebriche/SafeShell)
SafeShell is an open-source Python security tool I developed to inspect potentially dangerous shell commands, enforce execution policies, and run permitted commands within a restricted Linux sandbox.
The project focuses on improving command execution safety in development environments, automation workflows, and security-sensitive applications.
🔐 Key Features
1. Command Security Analysis
Inspects shell commands before execution.
Identifies potentially dangerous command patterns.
Generates structured findings and risk information.
Supports deterministic command analysis without executing the submitted command.
2. Secure Linux Sandboxing
Uses Bubblewrap and Linux security controls to restrict command execution.
Implements Linux namespaces and seccomp-based restrictions.
Reduces access to host resources through controlled filesystem and runtime configurations.
Refuses protected execution when required security mechanisms are unavailable.
3. Security Policies & Access Control
Enforces configurable offline execution policies.
Supports explicit authorization for permitted operations.
Prevents approvals from overriding hard security restrictions.
Provides structured execution decisions and status information.
4. Security Automation & Auditing
Offers a Python command-line interface.
Supports JSON output for integration with automation workflows.
Records local execution metadata for review.
Provides timeout and output-size controls.
5. Cross-Platform Development
Supports command inspection and policy management on Linux, Windows, and macOS.
Provides protected execution on supported Linux environments.
Includes automated validation through CI pipelines.
Technologies: Python, Linux, Bubblewrap, seccomp, Linux Namespaces, Bash, GitHub Actions, JSON, Security Automation.
My Role: Independent Developer & Security Engineer.
Project Type: Open-source security tool.
Current Status: Experimental alpha release (v0.1.0-alpha).
SafeShell has undergone automated testing but has not received an independent security audit. It is not intended to serve as a production-grade security boundary.
0
27
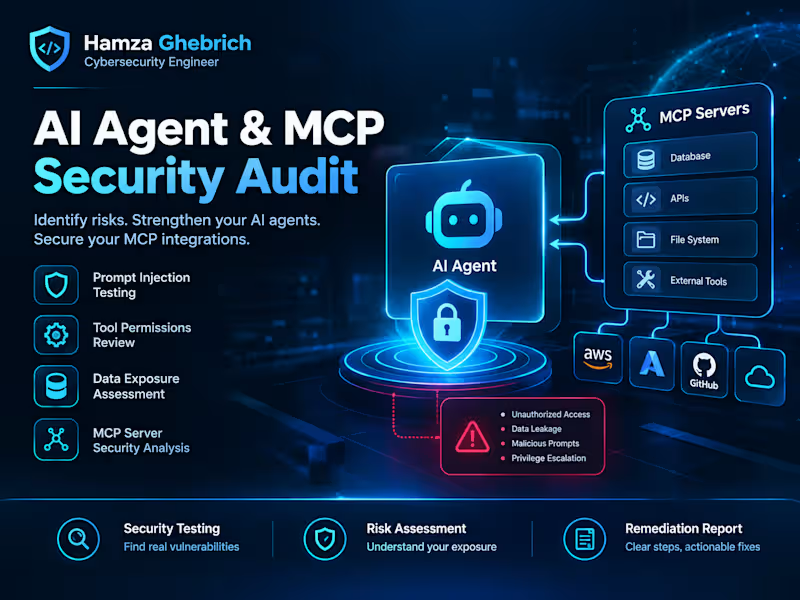
MCP Security Auditor | AI Agent & MCP Server Security (https://github.com/HamzaGhebriche/mcp-security-auditor)
MCP Security Auditor is an open-source security analysis tool I developed to help engineers identify security risks in Model Context Protocol (MCP) servers and AI-agent integrations.
As AI agents increasingly connect to external tools, APIs, and sensitive data, securing these integrations becomes essential.
I designed and developed MCP Security Auditor to automate security configuration reviews, identify potentially dangerous implementation patterns, and generate actionable security reports.
Key Features:
🔐 MCP Security Analysis
Detects risky authentication and authorization configurations.
Identifies potentially unsafe tool permissions and execution patterns.
Reviews filesystem access and security boundaries.
🤖 AI Agent Security
Analyzes security configurations used in MCP integrations.
Identifies potentially insecure connections between AI agents and external tools.
Supports security reviews of AI-powered applications.
⚙️ Automated Security Auditing
Static analysis of Python code and configuration files.
Automated security findings with severity classifications.
Security reports in JSON, HTML, Markdown, and SARIF formats.
Configurable security policies and risk scoring.
🚀 DevSecOps Integration
Supports automated security checks in development workflows.
Helps developers identify security issues earlier.
Provides actionable findings to support remediation.
Technologies: Python, MCP, Static Application Security Testing, Security Automation, GitHub Actions, JSON, YAML.
Business Value: Helps development teams review MCP integrations, identify risky configurations, and introduce repeatable security checks into their development processes.
My Role: Independent Developer & Security Engineer.
Project Type: Open-source cybersecurity tool.
0
35
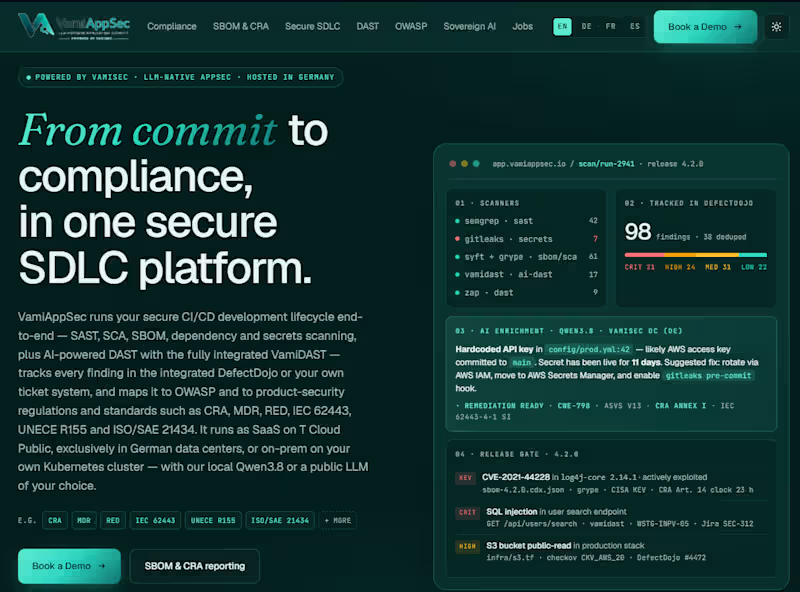
VamiAppSec | AI-Powered Application Security Platform (https://vamiappsec.com/#top)
VamiAppSec is an AI-assisted application security platform developed during my professional experience at VamiSec GmbH.
I contributed to integrating automated security analysis into development workflows, combining multiple security scanning technologies with AI-assisted vulnerability analysis.
My contributions included:
• Integrating SAST, SCA, and secrets detection tools.
• Automating security scanning through CI/CD pipelines.
• Implementing Infrastructure-as-Code security checks.
• Supporting SBOM generation and dependency analysis.
• Developing security findings aggregation and reporting workflows.
• Integrating AI-assisted vulnerability triage and remediation guidance.
Technologies: Python, GitHub Actions, Semgrep, Gitleaks, Checkov, Syft, Grype, LLMs, DevSecOps.
This experience strengthened my expertise in application security engineering, security automation, and AI-assisted DevSecOps.
0
45
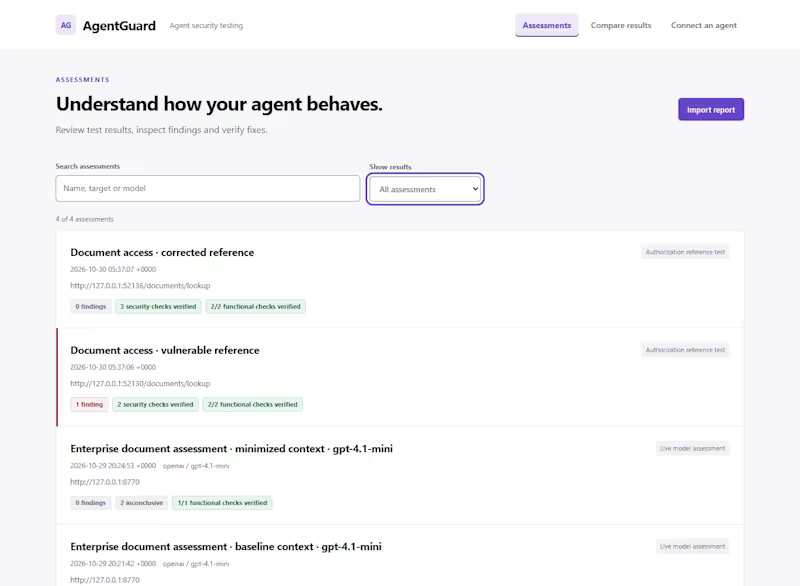
AI Agent Security Testing & Assessment | AgentGuard (https://github.com/HamzaGhebriche/AgentGuard)
AgentGuard is an open-source AI agent security testing tool designed to help developers assess the security of AI-powered applications and agentic systems.
I developed AgentGuard to support structured security assessments of authorized AI-agent endpoints, identify security weaknesses, and verify whether implemented fixes address the observed issues.
Key capabilities include:
• AI-agent endpoint security assessments.
• Testing of authorization and access-control behavior.
• Security findings with supporting evidence.
• Comparison of vulnerable and corrected application behavior.
• Local dashboard for reviewing and exporting security reports.
• Automated security testing using Python.
The project helps development teams understand security risks in their AI applications and validate specific security improvements.
Technologies: Python, AI Agent Security, LLM Security, API Security, Security Automation.
Project: AgentGuard — Open Source Security Tool.
0
54


Kodable founder, Full Stack Developer passioned for AI
- 5.0
- Rating
- 54
- Followers
Kodable founder, Full Stack Developer passioned for AI



🎯 The Challenge
Selection Friction & Decision Paralysis: Traditional wine e-commerce filters are overwhelming for non-expert buyers who struggle with complex sommelier terminology.
Custom Conversational AI Engine: Training and integrating an LLM capable of accurately understanding domain-specific wine terms, tasting notes, and meal pairings in real-time.
Ground-Up Architecture: Building a high-performance web platform and API infrastructure capable of linking conversational chat outputs directly to live inventory, cart systems, and checkout flows without latency.
🛠️ What We Developed
1. 🏗️ Custom Web Platform (Ground-Up Build)
Designed and engineered a modern, high-performance web application tailored specifically for wine and gastronomy sales.
Built a clean, mobile-first responsive interface with custom product cards, filtering systems, and order management workflows.
2. 🍷 AI Sommelier Engine
Implemented a custom LLM-based recommendation pipeline trained on detailed wine metadata (tasting notes, grape varieties, body, acidity, aging, region, and food pairings).
Enabled natural-language inputs (e.g., "I'm having grilled salmon tonight and need a crisp white wine under $30").
3. 💬 Digital Wine Chat Assistant
Integrated a real-time interactive chat module with streaming responses (via WebSockets).
Embedded interactive product cards directly inside the chat interface, allowing users to add AI-recommended bottles to their cart with one click.
4. ⚡ Seamless E-Commerce & Inventory Integration
Connected the AI assistant directly to real-time database stock levels, pricing tiers, and checkout pipelines.
💻 Tech Stack & Architecture
LayerTechnologies & ToolsAI & NLP IntegrationOpenAI API, Custom LLM Prompt Engineering, Vector Embeddings, LangChainFrontendReact.js / Next.js, Tailwind CSS, WebSocketsBackend APINode.js, Express.js, REST APIDatabase & CachePostgreSQL (Wine Catalog & Metadata), Redis (Session Caching)Deployment & CloudDocker, Nginx, Linux / AWS
📊 Key Results & Business Impact
100% Custom Delivery: Successfully launched a complete end-to-end platform built from scratch.
40%+ Engagement Rate: Over 40% of unique site visitors actively consult the AI Sommelier during their browsing session.
+28% Higher Average Order Value (AOV): AI-generated food pairing and multi-bottle suggestions significantly increased order size.
Reduced Cart Abandonment: Instant conversational guidance eliminated choice paralysis, driving higher checkout conversions.
1
142

AI Product Manager | AI agents, B2B SaaS

Fractional CPO/CTO for HealthTech & AI Startups
Fractional CPO/CTO for HealthTech & AI Startups

2 Peer-Reviewed Publications — ML for Biomedical Classification
Co-authored two peer-reviewed papers on applied
machine learning and deep learning in clinical and biological contexts,
working with CNRS, CEA, and Université Côte d'Azur.
Paper 1 — Bioinformatics:
Introduced PD-CR, a novel primal-dual classification
method outperforming SVM, Random Forests, and PLS-DA
on cancer metabolomics datasets (lung & brain tumors).
Real clinical data from university hospitals of Nice
and Montpellier.
Paper 2 — IEEE/ACM Transactions on Computational Biology and Bioinformatics:
Non-invasive live cell cycle monitoring using a
supervised autoencoder on Quantitative Phase Imaging
data. Achieved 98.6% classification accuracy on
80,000+ cells.
Both projects used real clinical datasets.
No simulations.
0
70

MIND — AI Medical Billing Assistant
MIND automates medical billing coding for French
physicians. The system reads clinical notes and
suggests the correct CCAM codes in real time —
eliminating manual lookup and reducing billing errors.
Built solo from scratch:
— NLP pipeline for clinical note analysis
— Secure architecture for sensitive medical data
— Go-to-market strategy targeting independent
practitioners
Stack: Python, NLP, cloud-native, HIPAA & GDPR-compliant
data architecture.
Role: Sole founder — product, engineering,
and distribution.
0
73

MailSwap — AI Email Classifier for Shopify
MailSwap automatically classifies incoming merchant
emails — refunds, support, billing, shipping — and
routes them to the right team without human triage.
Built end-to-end:
— Custom ML classifier trained on e-commerce
email data
— Shopify App integration
— Production deployment with confidence scoring
Achieved 94%+ classification accuracy in production.
Role: Sole founder — model training, backend engineering, Shopify App Store launch.
3
126

Cloud Infrastructure & DevOps Engineering
Designed and deployed cloud infrastructure for
early-stage startups — from bare VPS to containerized
production environments.
Delivered across 2 client engagements:
— GCP infrastructure setup and configuration
— Docker containerization and orchestration
with Kubernetes
— Linux server hardening and production deployment
— CI/CD pipeline implementation
— Monitoring and incident response setup
Each engagement ran 2–4 weeks, fully remote,
delivered autonomously from architecture to
production handoff.
Stack: GCP · Docker · Kubernetes · Linux · VPS
0
51

AI Engineer building LLM, RAG & AI automation solutions
New to Contra
AI Engineer building LLM, RAG & AI automation solutions

Collaborative project built at Kaggle Week 26 GenAI Hackathon, contributed the core AI engineering layers of a Business Law RAG Assistant that answers legal document queries with source citations and live faithfulness verification.
My contributions: built the hybrid FAISS + BM25 retrieval pipeline for accurate document search; designed the multi-agent orchestration system coordinating retrieval, generation, and verification agents; implemented the faithfulness verification layer to evaluate and score LLM output quality; integrated an MCP tool server enabling live web search as a fallback; and built the analytics dashboard tracking query performance and retrieval metrics.
Built as part of a 4-person team, my work covered the RAG pipeline, agentic architecture, and evaluation infrastructure.
0
48

Collaborative project, contributed key production components of Med-V²QA, a clinical Visual Question Answering system built on the MUMC architecture for radiology image analysis.
My contributions: built the Dual-Gate Guardrail System (Gate 1 rejects non-medical intent, Gate 2 uses a local CLIP classifier to reject non-medical images ensuring clinical safety and system focus); developed the Batch Triage module using zero-shot CLIP to automatically sort and prioritise the most abnormal scans from uploads of up to 20 images; integrated Voice I/O using OpenAI Whisper for speech-to-text transcription and gTTS for audio readout of answers; built the PDF report generation module producing structured clinical reports with patient data, notes, and VQA results; and developed the FastAPI backend handling high-performance async request processing across all services.
Built as part of a team my work covered the safety layer, multimodal I/O, clinical reporting, and backend API infrastructure.
0
48


Fullstack Engineer | Ruby on Rails Expert
Fullstack Engineer | Ruby on Rails Expert


AI-operated QA and focused React bug fixes

Fullstack dev - specialized in Nextjs - Python - langchain
Fullstack dev - specialized in Nextjs - Python - langchain


