Freelancers using AWS in Pakistan
Sign Up
Post a job
Sign Up
Log In
Filters
2
Projects
People
Abubakar Chan
pro
Lahore, Pakistan
AI Automation Engineer | Full-Stack Apps & Integrations
66x
Hired
4.9
Rating
155
Followers
Expert
Expert
+2
Follow
Message
AI Automation Engineer | Full-Stack Apps & Integrations
4
Provider Portal for Healthcare MSO
4
46
1
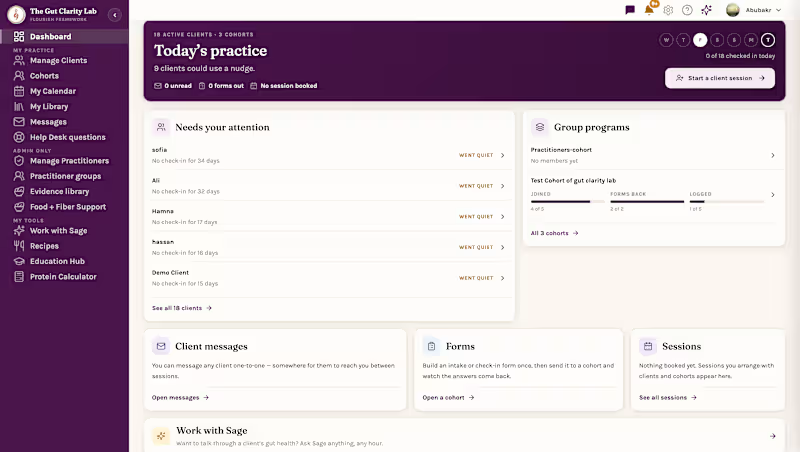
Gut Health SaaS Platform Development
1
17
6
Magnai | UK Public Affairs
6
88
7
Humoni - secure housing in under 72 hours
7
146
AWS
(1)
Follow
Message
Umar Abdullah
max
Lahore, Pakistan
Full-Stack Dev (Web, Mobile, Desktop) & Chromium Browser Dev
8x
Hired
5.0
Rating
159
Followers
Follow
Message
Full-Stack Dev (Web, Mobile, Desktop) & Chromium Browser Dev
1
Chrome Extension Development for school's student Monitoring
1
14
7
Full-Stack Developer | Chromium Expert | Chrome Extension
7
83
7
Chromium Browser Development for enterprise
7
66
1
Real Estate Authority Modern Website Development
1
34
AWS
(1)
Follow
Message
Devowise Studios
pro
Pakistan
Web Design Studio | Brand Identity | Framer & AI Solutions
$5k+
Earned
4x
Hired
5.0
Rating
132
Followers
expert
Expert
+4
Follow
Message
Web Design Studio | Brand Identity | Framer & AI Solutions
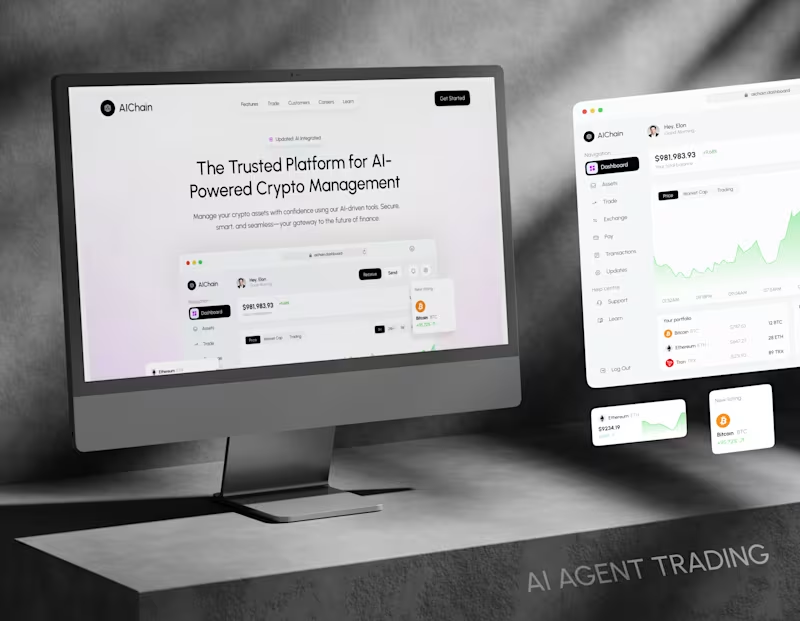
1
AI-Powered Crypto Trading Platform
1
16
1
ActiveMentor - AI Based Fitness Application
1
34
1
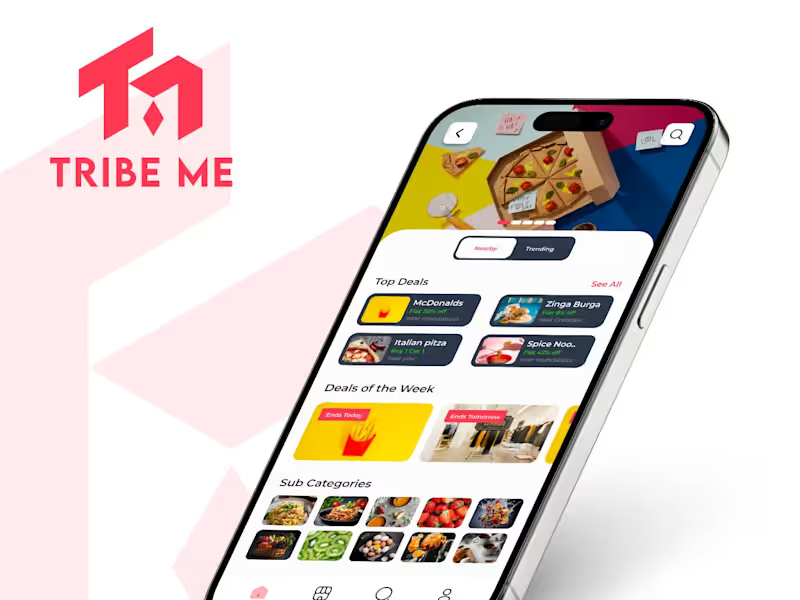
E-commerce Application - TribeMe
1
47
2
Outdoor Sports Booking Application - GoPlay
2
55
AWS
(6)
Follow
Message
Salman Inayat
Islamabad, Pakistan
Full-stack developer building high-impact web products.
$25k+
Earned
3x
Hired
5.0
Rating
52
Followers
Follow
Message
Full-stack developer building high-impact web products.
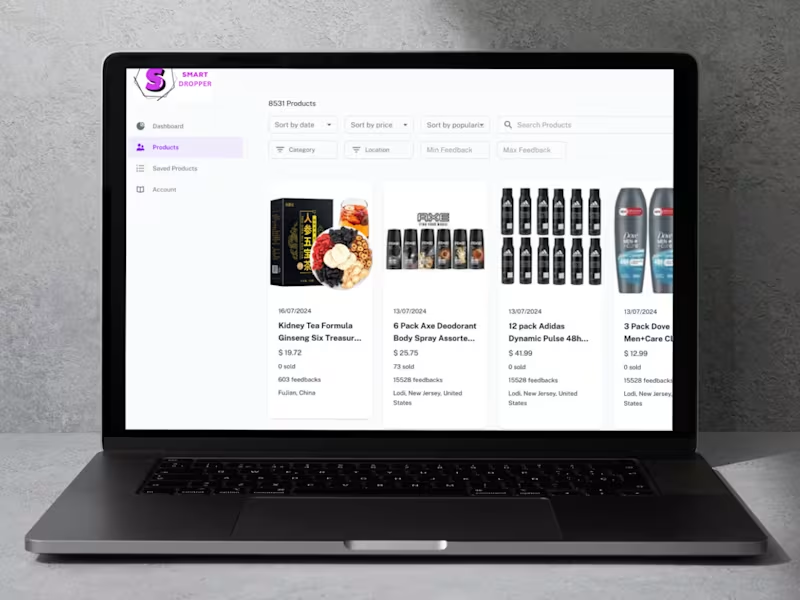
$14K+ earned
2
AX3 Sonic – Your Podcast Hub for Teams & Audiences
2
48
1
Smart Dropper
1
15
1
AX3 Music Platform
1
24
1
1-800-FlyFish
1
31
AWS
(3)
Follow
Message
Muhammad Usama
pro
Islamabad, Pakistan
Full-Stack Mobile & AI App Developer
5.0
Rating
25
Followers
Partner
Follow
Message
Full-Stack Mobile & AI App Developer
1
Fate Dating App — AI-Powered Matchmaking
1
1
28
1
Chatbox AI: Multi-Model AI Platform (Web + Mobile)
1
21
1
Crypto & Stock Trading App (React Native + Node.js)
1
25
1
AI Skincare Scanner App (Computer Vision + TensorFlow)
1
20
AWS
(12)
Follow
Message
Usama Idrees
Islamabad, Pakistan
Enterprise Cloud · DevOps · AI/ML · Email · Marketing Expert
13x
Hired
4.4
Rating
41
Followers
Follow
Message
Enterprise Cloud · DevOps · AI/ML · Email · Marketing Expert
30
I’m Usama Idrees, IT & AI Specialist based in Islamabad, Pakistan. Thrilled to be part of this amazing community and to connect with talented Professionals from around the world! 🚀 A little about me: What I do: I lead tech and product strategy, focusing on building innovative solutions that empower businesses and individuals. Passion: Creativity meets technology — I love turning ideas into impactful products. Looking for: Collaborations with designers, developers, and creative minds who want to build something extraordinary. Excited to learn, share, and grow together here. If you’re working on something cool or looking for a tech partner, let’s connect! 💡 What’s your current creative project? Drop it below — I’d love to check it out. 👇
2
30
866
0
Serverless Architecture for Scalability & Efficiency at VMLA
0
37
2
Legacy System Scalable and Secure Modernization
2
27
2
Implementing DevOps Practices; Enterprise-Level Transformatios
2
67
AWS
(5)
Follow
Message
Muhammad Usman
Islamabad, Pakistan
End-to-End IoT, AI & Web3 Solutions | REPLA Tech
5.0
Rating
29
Followers
Follow
Message
End-to-End IoT, AI & Web3 Solutions | REPLA Tech
0
ELD Software | IoT Fleet Compliance Platform
0
15
0
Smart Home — IoT Home Automation Platform
0
13
0
Nexus Health AI Telehealth Mobile Application
0
23
0
TCI LMS | SaaS Platform for Tutors & Students
0
15
AWS
(3)
Follow
Message
Ehtasham Ali
pro
Karachi, Pakistan
Production-ready AI agents and SaaS built to scale reliably.
$25k+
Earned
2x
Hired
108
Followers
Follow
Message
Production-ready AI agents and SaaS built to scale reliably.
2
KovaRisk: When the Interface Knew More Than the System ────────────────────────────────────────── The Expert in the Room Compliance officers don't struggle to understand risk. They struggle to act on it fast enough. The team behind KovaRisk understood this precisely. They had spent years inside financial institutions watching the same dysfunction repeat: alerts buried in spreadsheets, investigations tracked in email threads, audit trails reconstructed after the fact. They knew what the interface needed to feel like because they'd lived with the one that didn't. So they built it. Fast. Exactly as they'd imagined it. What emerged was sharp: a risk monitoring dashboard with filterable alert feeds, entity profiles with 12-month risk trajectories, a rule engine with toggle controls, and an audit log that felt immutable. The scenario switcher let compliance teams stress-test different alert load states. The side panel made investigations feel contained and intentional. It looked like a system that had survived production. It hadn't been asked to yet. ────────────────────────────────────────── What Existed Was a Strong Interface - Not a System Every alert in KovaRisk was generated at startup. Every risk score was computed by a random seed function. Every status change - Investigating, Resolved, Escalated - lived in component state. Every timeline event was appended to an in-memory array. Every rule toggle disappeared on refresh. The audit log recorded nothing. The export downloaded a snapshot of what React was holding at that moment. The entity risk history was a curve drawn from a formula, not a record. The logic was there. But it had nowhere to live. A compliance officer investigating a high-risk wire transfer would open the side panel, read the plain-English rule explanation, mark the alert as Investigating, add an internal note - and lose every one of those actions the moment they refreshed the browser. No colleague could see what they'd done. No regulator could verify it had happened. In financial compliance, that's not a UX problem. It's a liability. The prototype validated the workflow brilliantly. It exposed exactly how a compliance team would move through their day. But three things were missing: a source of truth, a coordination layer, and a trail that could be audited under pressure. ────────────────────────────────────────── They Didn't Need More Features - They Needed a System Behind the Interface The team came with a clear idea and a working prototype. What they needed was the architecture that made the prototype a product - the layer that turned interface actions into durable facts. Not a rebuild. A foundation. ────────────────────────────────────────── The Layer That Made It Dependable Data Models: Giving State a Home The first thing to reconstruct was where the data should actually live. KovaRisk's frontend implied a clear schema - alerts, entities, rules, audit events - but none of it persisted. The production system needed a PostgreSQL core with five primary entities: • Alert — with foreign keys to Entity, Rule, Transaction, and a JSONB timeline column for ordered event history • Entity — with risk tier, jurisdiction metadata, and a one-to-many relationship to RiskScore snapshots • Rule — with active/disabled state, trigger thresholds, false-positive tracking, and a versioning mechanism so changes to rules didn't retroactively alter historical alerts • AuditEvent — append-only, with actor ID, action type, target reference, and a server-generated timestamp that clients cannot modify • InternalNote — owned by an alert, with authorship and a soft-delete flag to preserve compliance integrity Every status change, note, escalation, and flag the UI handled ephemerally became a write to this schema. The Alert Generation Engine: Replacing the Seed Function In the prototype, 85 alerts appeared because a loop ran 85 times at startup. In production, alerts are the output of a Transaction Monitoring Service - a background process that runs continuously against incoming transaction streams. This service: • Evaluates each transaction against every active Rule definition • Computes a risk score using rule weights, entity risk tier, jurisdiction flags, and behavioral baselines • Creates an Alert record only when a threshold is breached • Emits an event to a notification queue for high-risk triggers The rule engine the UI let users toggle wasn't decorative. Each rule mapped to an evaluation function in the monitoring service. Disabling a rule didn't just grey out a card - it removed it from the active evaluation set. Re-enabling it didn't retroactively generate alerts it would have caught; it resumed from the point of activation. That distinction mattered for regulatory defensibility. ────────────────────────────────────────── Async Workflows: The Operations the UI Implied But Couldn't Sustain Several interactions in the prototype implied workflows that couldn't complete synchronously. Escalation - When an alert was escalated, the UI changed a status badge. In production, escalation triggers a queue job that: notifies the senior compliance officer via a configured channel, creates a case record linking the alert, and starts a response SLA timer. The UI reflects the outcome - it doesn't produce it. Scheduled Screening - The Sanctions Screening Match rule in the prototype was static. In production, it's a nightly job that re-screens all active entities against updated OFAC, EU, and UN sanctions lists - generating new alerts if a previously clean entity now appears. The results feed back into the alert pipeline. Report Export - The dashboard's Export Report button downloaded a text file of whatever React was holding in memory. In production, report generation is an async job: the user requests the report, the job runs server-side against the live database, and a download link is returned when ready. The content is a verifiable, timestamped record - not a UI snapshot. ────────────────────────────────────────── The Audit Log: From Feed to Fact The prototype's audit log was populated by a generateAuditLog function. It looked comprehensive and immutable. It was neither. Production audit events are written by the API layer on every state-modifying operation - before the response is returned to the client. The table is append-only. No update operations are permitted on AuditEvent records. Timestamps are server-generated in UTC and stored with full precision. Actor identity comes from the authenticated session, not from a string the client sends. The audit log the interface displayed was a simulation of accountability. The production version is the accountability. ────────────────────────────────────────── Tech Stack 1. Frontend: React + Vite, React Router v6, Recharts, React Context + local state, TanStack Query 2. Backend: Node.js + TypeScript, Fastify, Prisma, PostgreSQL, Redis, BullMQ, Passport.js + express-session 3. Infrastructure: AWS ECS / Railway / Render, S3, AWS Secrets Manager / Doppler, Sentry + Datadog, GitHub Actions 4. External Integrations: OFAC / ComplyAdvantage, Refinitiv World-Check, SendGrid / SMTP, Webhooks ────────────────────────────────────────── From Interface to System The prototype answered the right questions. It proved the workflow was sound, the information hierarchy was correct, and the alert investigation pattern worked the way compliance officers needed it to. What it couldn't answer was: what happens when two investigators open the same alert simultaneously? What happens when a rule change needs to take effect immediately across 200 pending alerts? What happens when a regulator asks for every action taken on a specific entity over the past 18 months? Those questions don't live in the interface. They live in the system. KovaRisk's interface was always strong. What it needed was the architecture to make it real - persistent, coordinated, auditable, and defensible under scrutiny. The logic existed from the beginning. We gave it somewhere to live.
2
1.9K
2
Case Study: From Prototype to Production — Building a Credit Management Platform for Ad Operations The Starting Point The founder wasn't guessing the problem. They had spent years inside the ad-credit ecosystem, managing wallet balances across regions, reconciling top-ups via bank wire and stablecoin, chasing compliance documents, and watching campaigns stall because a pixel stopped firing at 2am. They knew exactly what a credit management platform needed to look like. So they built one. Using Figma wireframes translated directly into a React frontend, they shipped a working prototype in days. Two portals were created. One for clients managing wallets and ad accounts, and one for internal operators handling treasury, compliance, and risk. It included real-time spend charts, AI-driven anomaly detection banners, a work queue for ops teams, and an embedded AI assistant that could answer questions about balances, compliance status, and pixel health. The prototype proved the concept. Clients could see their wallet balances, request top-ups, allocate funds to ad accounts, and track campaign performance. Admins could manage treasury operations, review KYB pipelines, monitor risk scores, and process a prioritized work queue. The domain logic was sound. The UX was sharp. But the system was never designed to survive real load. What Started Breaking The prototype worked on mock data. Every API call returned hardcoded arrays after a random delay. There was no backend. No database. No real authentication. The login screen accepted any email and assigned a role based on a toggle switch. Session state lived in localStorage as a raw JSON blob. This was fine for demos. It stopped being fine the moment real money entered the picture. The specific fractures: 1. No transactional integrity. Wallet balances, top-ups, fund transfers, and ad account allocations were all simulated. In a live system, a transfer of $25,000 from a master wallet to a regional sub-wallet is not a UI state change. It is a financial transaction that requires atomicity, audit trails, and rollback capability. The prototype had none of this. 2. Compliance was cosmetic. KYB document statuses were static labels. In production, document verification involves third-party identity providers, expiration tracking, automated re-upload reminders, and regulatory audit logs. The prototype rendered badges like "Verified", "Pending", and "Missing", but nothing enforced the state machine behind them. 3. Risk scoring was decorative. The AI risk badges showed tooltips like "Large P2P transfer detected, document expiring", but these were string literals, not outputs from a scoring model. Real risk assessment requires transaction pattern analysis, velocity checks, cross-referencing compliance status, and escalation workflows that route to the right ops agent. 4. The work queue had no backend. Urgent items like "$45,000 P2P transfer anomaly" appeared in the queue, but resolving them was just a frontend state toggle. There was no case history, no assignment logic, no SLA tracking, and no integration with the compliance or treasury systems that actually needed to act on these events. 5. Multi-tenancy was absent. The platform served one mock client and one mock admin. Scaling to dozens of clients, each with their own wallets, sub-wallets, ad accounts, compliance profiles, and credit limits, required data isolation, permissioning, and tenant-aware queries that did not exist. 6. Ad platform integration was faked. TikTok metrics like impressions, clicks, ROAS, and pixel health were all static datasets. Production requires OAuth-based API integrations, rate-limited data syncing, webhook listeners for pixel status changes, and graceful degradation when platform APIs go down. The founder understood all of this. The prototype was never meant to be the product. It was meant to prove that the product was worth building. Why They Brought In a Team The gap between the prototype and production was not a matter of fixing bugs. It was an architecture problem. The founder needed: - A real backend with transactional guarantees for financial operations - A compliance engine that could enforce document workflows across jurisdictions - A risk system that could ingest transaction data and surface actionable alerts, not static strings - Multi-tenant data architecture with proper isolation and access control - Ad platform integrations that could handle real API contracts, rate limits, and failures - Observability including logging, monitoring, and alerting so the ops team could trust the system under load They did not need someone to rewrite the frontend. They needed someone to build the system underneath it. What We Delivered Financial Operations Layer We replaced the mock API with a transactional backend. Every wallet operation, including top-ups, transfers, allocations, and refunds, now runs through an auditable pipeline with: - Atomic balance updates with optimistic locking - Double-entry ledger for every fund movement - Idempotent transaction processing to prevent duplicate charges - Full audit trail with actor, timestamp, and before and after state Top-up requests now flow through a verification pipeline with submission, proof-of-payment upload, approval, and balance credit. Each step is recorded and reversible. Compliance and KYB Engine - We built a document lifecycle system that replaces static badges with enforced state transitions: - Documents move through missing → uploaded → under_review → verified → expired with rules governing each transition - Expiration monitoring triggers automated client notifications before deadlines - Third-party identity verification integration for director ID matching - Jurisdiction-aware requirements where different regions require different document sets - Audit-grade logging for every status change, reviewer action, and override The KYB pipeline now routes cases to specific compliance agents based on workload, region, and verification type. Risk and Anomaly Detection We replaced hardcoded risk labels with a scoring system that evaluates: - Transaction velocity based on spend acceleration versus historical baseline - P2P transfer patterns and threshold breaches - Compliance status correlation, such as expired documents combined with high spend - Account dormancy detection where inactivity triggers review Risk scores update in near real time. High-risk events automatically generate work queue items with priority, context, and suggested actions. Work Queue and Case Management We transformed the frontend-only task list into an event-driven operations system: - Events from treasury, compliance, and risk systems automatically create queue items - Assignment logic routes items to the right agent based on type, region, and capacity - SLA tracking with escalation rules for overdue items - Case history that records every action, note, and resolution - Enforced status transitions so items cannot be resolved without required actions Multi-Tenant Architecture We designed the data layer for tenant isolation from the ground up: - Each client organization has isolated wallets, documents, ad accounts, and transaction histories - Role-based access control separates client-facing and admin-facing data - API endpoints are tenant-scoped to prevent cross-tenant data leakage - Admin views aggregate across tenants with proper permissioning Ad Platform Integration We built a sync layer for TikTok Ads with an architecture that supports additional platforms: - OAuth-based account linking with token refresh management - Scheduled metric pulls with rate limit awareness and backoff - Pixel health monitoring via event signal tracking instead of static labels - Graceful degradation where stale data is clearly labeled if APIs fail Observability We added the infrastructure the ops team needs to trust the system: - Structured logging for every financial operation, compliance action, and API call - Health dashboards for backend services, integration sync status, and queue throughput - Alerting on anomalies such as failed transactions, sync delays, and SLA breaches - Error tracking with business context, not just stack traces The Outcome The system went from a prototype that could demo well to a platform that could process real money, enforce real compliance, and surface real risk under real load. What changed: - Financial operations now run with transactional guarantees. Wallet balances are accurate, auditable, and reconcilable. - Compliance is enforced, not displayed. Document workflows follow regulated state machines with full audit trails. - Risk detection is continuous and contextual. The ops team acts on scored alerts instead of static labels. - The work queue drives operations. Events flow in automatically, route correctly, and track resolution against SLAs. - Multi-tenancy works. New clients onboard into isolated environments without architectural changes. - Ad integrations sync reliably. When they fail, the system clearly shows it instead of masking stale data. The founder’s instinct was right from the start. The domain model, the UX, and the operational workflows all held up. What we built was the engineering foundation that made it dependable. The system worked until it didn’t. Not because the idea was flawed, but because it was never designed to handle this level of complexity. The prototype proved the product. The production system proved it could scale. Tech Stack Overview 1. Backend: Node.js (NestJS) 2. API: GraphQL 3. Auth: Auth0 4. Database: PostgreSQL 5. Cache/Queue: Redis 6. Search: Elasticsearch 7. Infrastructure: AWS 8. Containers: ECS Fargate 9. CI/CD: GitHub Actions 10. IaC: Terraform 11. Integrations: Stripe 12. Risk Engine: Python (FastAPI) 13. ML Pipeline: scikit-learn 14. AI Assistant: OpenAI GPT-4 15. Vector Store: Pinecone
2
1.9K
4
😍 This the best I have done in health industry - A SaaS platform: https://treatmentnotes.com/ 🚀 Built an AI-powered behavioral health documentation platform designed for real clinical workflows. The system supports AI generated notes from live conversations, uploaded transcripts, and custom knowledge-base logic tailored to mental health and addiction treatment. It was designed for secure, scalable healthcare use with HIPAA ready architecture and EMR integration support. 💯 Complete Tech Stack: AI Summarization, Clinical Nuance Detection, FastAPI, Vite, React, AWS Bedrock, Anthropic Claude, PostgreSQL, pgvector, Vector Database, Retrieval-Augmented Generation (RAG), AI Agent Architecture, HIPAA Compliant Cloud, Speech-to-Text API, LLM Fine-tuning, Healthcare Interoperability, HL7/FHIR Integration, Serverless Backend, Semantic Search, Private LLM Deployment, Encryption at Rest, Python Backend Development. 🧠 What do you say Contra Community?
1
4
1.7K
2
Turning Interview Prep into Structured, Real-Time Coaching
2
23
AWS
(4)
Follow
Message
Explore people