Freelancers using OpenAI in Nairobi
Freelancers using OpenAI in Nairobi
Sign Up
Post a job
Sign Up
Log In
Filters
2
Projects
People
Vincent Pasili
pro
Nairobi, Kenya
Turning your fintech and web3 ideas into shipped products
$50k+
Earned
45x
Hired
5.0
Rating
244
Followers
expert
expert
+2
Follow
Message
Turning your fintech and web3 ideas into shipped products
3
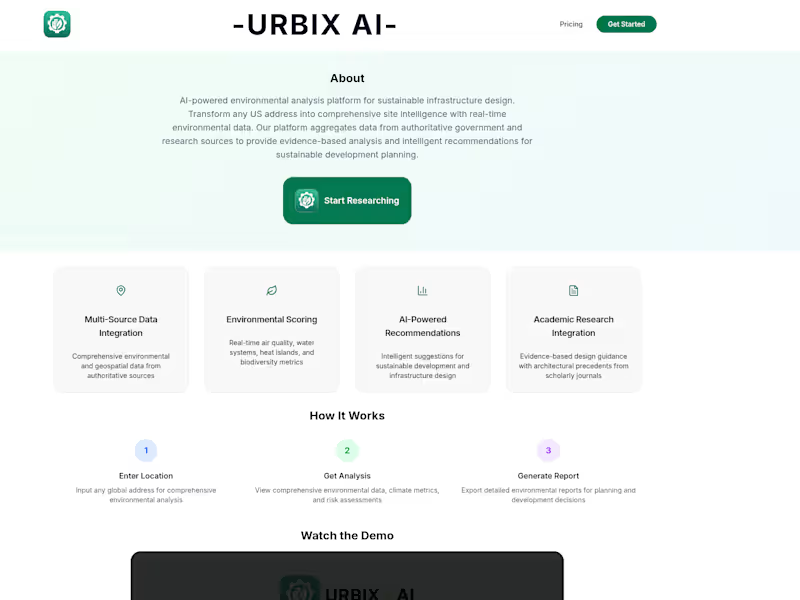
AI-powered Environmental Analysis Platform
3
21
0
Fiberwave Website Redesign and SEO Migration
0
46
0
Epic Surf Discovery Platform Design
0
73
0
Magarifiles Car Archive Web Design
0
63
OpenAI
(1)
Follow
Message
Stephen Kisong'e
Nairobi, Kenya
Cyber Security Analyst
Follow
Message
Cyber Security Analyst
0
Conducted an automated security assessment of a locally-hosted large language model, Dolphin 3.0 (Llama 3.1 8B), using Garak, NVIDIA's open-source LLM vulnerability scanner. The model was served through LM Studio's OpenAI-compatible REST API and tested from a Parrot OS environment running in VirtualBox. Configured Garak to target the model via a custom REST generator configuration, handling endpoint routing, Bearer token authentication, JSON response parsing, and extended timeouts for local inference. Executed nine distinct probe categories against the model, covering DAN jailbreaks, prompt injection, encoding-based bypass, malware generation, latent injection, real toxicity prompts, continuation attacks, grandma exploits, and package hallucination. The assessment identified that Dolphin 3.0, an uncensored model with no built-in safety guardrails, was vulnerable across the majority of probe categories. Findings were documented per probe, distinguishing where the model resisted versus complied, and translated into a clear, layered explanation of each attack type and its real-world security implications. Delivered the work as a complete, reproducible walkthrough, including environment setup, tool configuration, probe execution, and results interpretation, suitable for both technical practitioners and stakeholders newer to AI security.
0
170
0
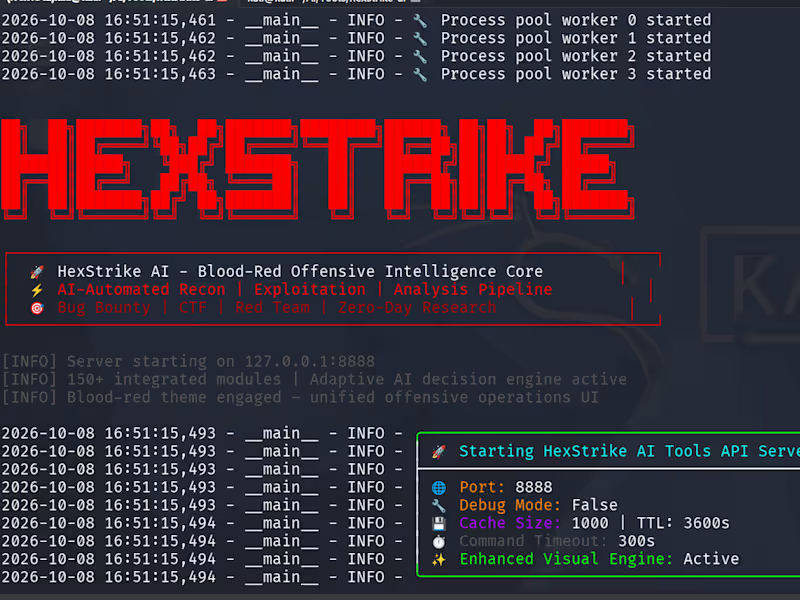
AI-Assisted CTF Solving and Bug Bounty Hunting I integrated Cyber-Ornith Obliterated, an uncensored cybersecurity model running locally in LM Studio, with HexStrike AI through MCP to execute tools on Kali Linux. I demonstrated the setup by solving Root-Me’s HTML source-code CTF challenge. The model retrieved the page, inspected its HTML and identified a password exposed in a comment. I verified the command output and submitted the answer, successfully completing the challenge. Beyond CTFs, I built this project to support AI-assisted bug bounty hunting, including web response analysis and vulnerability investigation within authorized scope, with human oversight and verification of findings.
1
0
21
0
AI Agent Hacking & Security Testing Explored how an AI agent can be manipulated through adversarial interactions, with a focus on AI agent hacking, prompt injection, sensitive data exposure, and unsafe agent behavior. The lab uses an AI agent connected to controlled internal data and tools, creating a realistic environment for testing how the agent responds when an attacker attempts to bypass its instructions, access information it should not reveal, or influence how it uses its capabilities. The assessment demonstrates the practical attack surface of modern AI agents and how seemingly simple interactions can become security issues when an agent has access to sensitive data or external capabilities. The testing was performed against fictional data in an isolated environment for authorized security research.
0
27
0
Designed and implemented a hands-on AI red teaming environment using Microsoft PyRIT to evaluate the security of a local Retrieval-Augmented Generation application. The project connected a Parrot OS testing environment to a Windows-based AnythingLLM RAG application, with DeepSeek running locally through LM Studio. I configured PyRIT to communicate with the AnythingLLM workspace through a custom HTTP target and used controlled adversarial objectives to examine how the application handled requests involving financial records, customer information, payroll data, and restricted credentials. The testing workflow included API connectivity validation, isolated Python environment setup, automated prompt execution, response collection, and evidence review. The lab was built entirely around fictional Kiso Secure business data, allowing realistic sensitive-data disclosure scenarios to be tested without using real customer information or credentials. The resulting workflow demonstrates how automated AI red teaming can be used to identify potential data leakage, retrieval-boundary weaknesses, and unsafe handling of sensitive information in AI-powered applications.
2
0
77
OpenAI
(1)
Follow
Message
Kelvin Mburu
Nairobi, Kenya
A software developer
Follow
Message
A software developer
0
Hostkeeping — Guest Services Platform for Premium Rentals
0
129
0
Nimbus Studio — Logo & Brand Identity (Kittl)
0
1
0
Solace Coffee Co. — Logo & Brand Identity (Kittl)
0
3
1
Hostkeeping — Guest Services Platform
1
1
OpenAI
(1)
Follow
Message
Explore people