
🚀 Excited to share my latest full-stack project: LUXO E-Commerce Admin Dashboard — built entirely with ASP.NET Core MVC!
This system includes:
✅ Admin Dashboard with real-time revenue & order analytics
✅ Complete Order Management (Pending → Confirmed → Shipped → Delivered)
✅ Product Catalog & Inventory Management
✅ Multi-payment method support (Credit Card, JazzCash, Easypaisa, Bank Transfer)
✅ Fully responsive design — works perfectly on all screen sizes
Working on this helped me strengthen my skills in .NET Core, MVC architecture, database design, and UI/UX implementation.
#DotNetCore #ASPNETMVC #EcommerceProject #WebDevelopment #Coding #PortfolioProject #PakistanDevelopers
8
1.5K
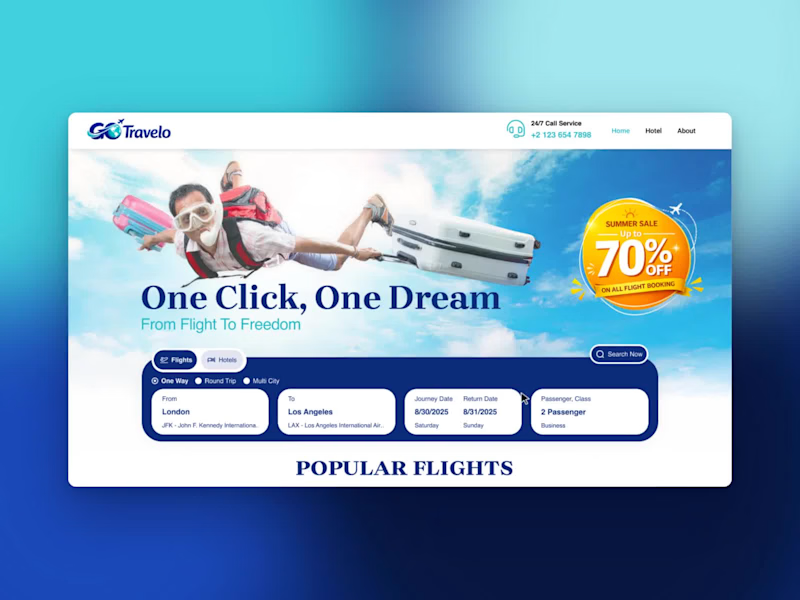
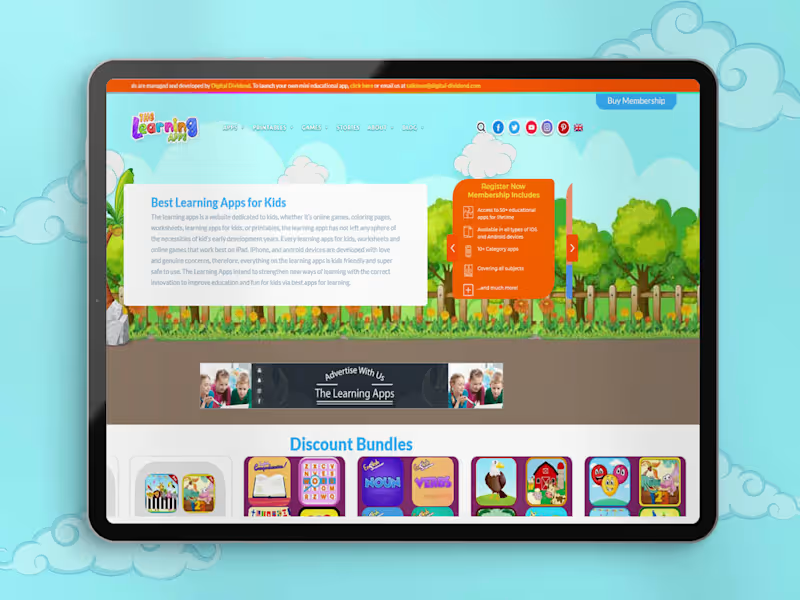

Practical Golf is a premium golf education and lifestyle brand focused on helping players improve performance, lower scores, and enjoy the game through expert-driven content and modern digital experiences. The brand combines trusted instruction, product insights, and community engagement for golfers who value both skill development and a smarter approach to the game.
The platform offers a wide range of resources including golf guides, equipment reviews, training tips, newsletters, books, and podcast content designed for players of all skill levels. Practical Golf is recognized for delivering practical strategies, honest recommendations, and data-driven advice that helps golfers make better decisions on and off the course.
The website experience emphasizes clean design, bold visual storytelling, and easy content discovery, featuring recent articles, curated product selections, educational resources, and membership-focused call-to-actions that build long-term audience loyalty.
Overall, Practical Golf represents a growth-focused sports media brand dedicated to improving the modern golfer’s experience through education, trusted content, and premium digital presentation.
0
53
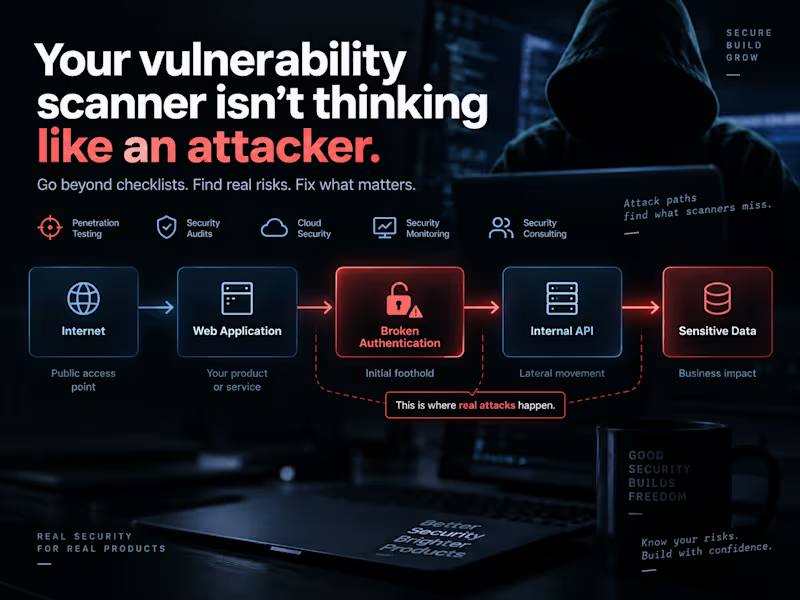
Most companies don't need another 80-page security report.
They need someone to tell them:
What can actually be exploited?
What could it cost us?
And what should we fix first?
That's the difference between checking a cybersecurity box and actually improving your security.
When I assess an application or infrastructure, I'm not interested in filling a report with 50 low-impact findings just to make it look impressive.
I care about attack paths.
→ Can authentication be bypassed?
→ Can one compromised account lead to something bigger?
→ Are APIs exposing data they shouldn't?
→ Can permissions be chained into privilege escalation?
→ Are cloud or infrastructure misconfigurations creating an easy entry point?
→ Would your monitoring actually notice an attacker?
And most importantly:
What should your team fix first?
That's the approach I bring to cybersecurity work — whether it's penetration testing, security audits, SOC/security monitoring, or security consulting.
I'm currently taking on new projects through Contra.
If you're building a SaaS product, web application, API, or growing infrastructure and you're unsure how it would hold up against a real attack, send me a message.
I'll happily take a look at what you're building and tell you where I'd start.
0
62
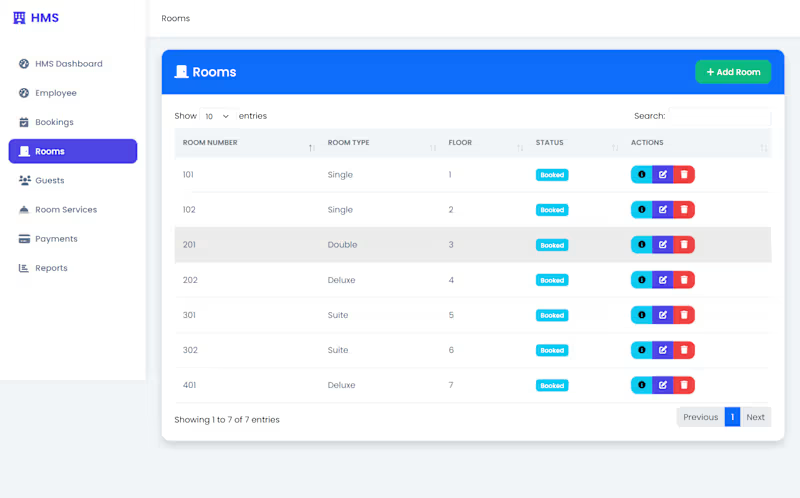
Hotel Management System
A complete and user-friendly Hotel Management System designed to streamline daily hotel operations and improve overall efficiency. The system helps manage rooms, guests, reservations, room services, billing, and other essential hotel operations from a centralized platform.
Key Features:
🏨 Room & Room Type Management
📅 Reservation & Booking Management
👤 Guest Management
🛎️ Room Service Management
💳 Billing & Payment Management
📊 Reports & Dashboard
🔄 Room Availability & Booking Status
⚙️ Easy-to-use Management Interface
The system reduces manual work, keeps hotel operations organized, and provides staff with quick access to important information—making day-to-day hotel management faster, simpler, and more efficient.
0
97


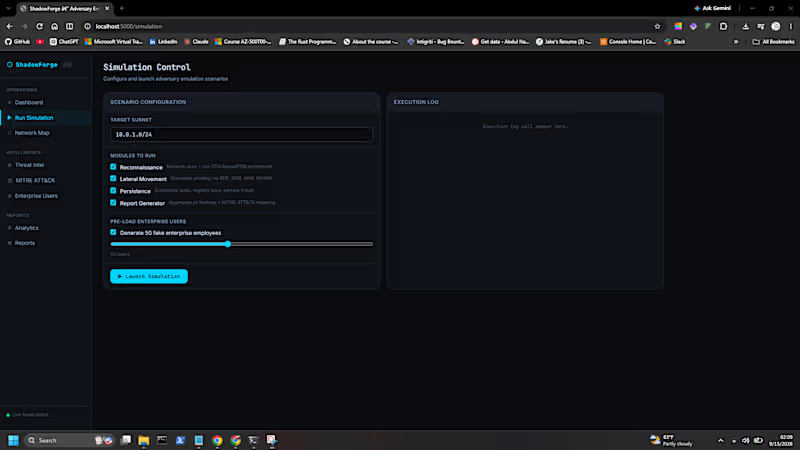
ShadowForge is an adversary-emulation and security-validation platform I built to help security teams model attack scenarios, visualize activity, correlate threat intelligence, and evaluate defensive visibility from a single operations interface.
The platform brings together scenario orchestration, network visualization, threat intelligence, MITRE ATT&CK mapping, enterprise identity simulation, analytics, and reporting into one unified workflow.
I designed the application around modular simulation components so authorized lab and security-validation exercises can be configured, observed, and translated into useful defensive findings rather than scattered logs and manual notes.
Key engineering work included:
Centralized security operations dashboard
Configurable adversary-emulation scenarios
Reconnaissance and environment-discovery simulation
Lateral-movement and persistence scenario modeling
Live execution-event visualization
Network topology and host mapping
MITRE ATT&CK technique mapping
Threat-intelligence and IOC enrichment
Enterprise user simulation for realistic lab scenarios
Security analytics and severity tracking
Automated findings and report generation
Modular architecture designed for controlled security testing
ShadowForge turns an authorized security exercise into something measurable: operators can configure a scenario, observe activity as it happens, correlate findings with threat intelligence and ATT&CK techniques, and produce structured results for defensive analysis.
Built for controlled labs, security validation, and authorized adversary-emulation environments.
0
92