Results that are similar to your search
Similar results

Expert AWS consulting, AI solutions, and machine learning.
- $100k+
- Earned
- 1x
- Hired
- 24
- Followers
Expert AWS consulting, AI solutions, and machine learning.


View more →


AWS DevOps Engineer | Terraform, CI/CD & Automation
AWS DevOps Engineer | Terraform, CI/CD & Automation
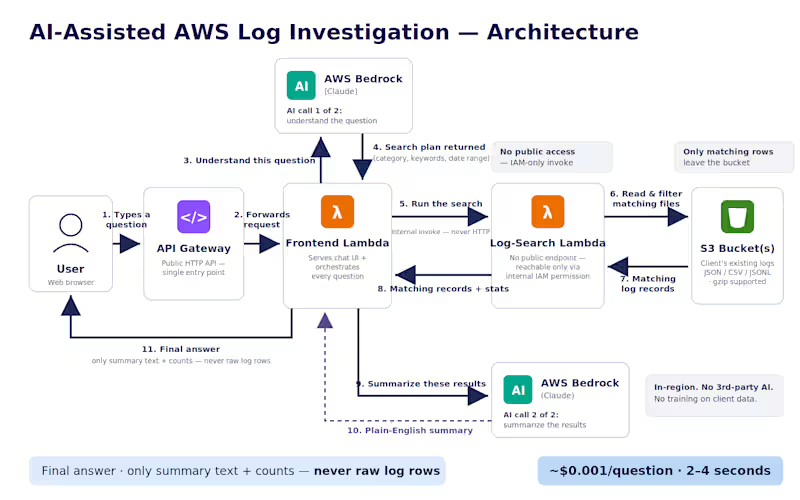
I built an AI-powered AWS log investigation system that allows teams to query logs stored in their existing S3 buckets using natural language.
The solution uses AWS Lambda, API Gateway, S3, Bedrock, and Terraform to:
- Convert natural-language questions into structured log searches
- Automatically discover and filter JSON, CSV, JSONL, and compressed log files
- Search across multiple S3 buckets without migrating log data
- Use Bedrock to summarize results and provide actionable insights
- Keep the log-search function private with IAM-based access control
The serverless architecture delivers typical queries in 2–4 seconds at approximately $0.001 per query, while keeping log data within the AWS environment.
Technologies:- AWS Lambda · API Gateway · S3 · AWS Bedrock · Terraform · IAM · Python
1
96

Automated Windows AMI Patching & AWS Infrastructure Automation
I built an automated AWS pipeline to eliminate the manual process of patching Windows servers and updating the AMI used by an Auto Scaling Group.
The solution uses AWS Image Builder, SSM Patch Manager, CloudWatch, EventBridge, Lambda, and CloudFormation to automate the complete patching lifecycle.
Automated Windows patch scanning and installation
Automated Sysprep and patched AMI creation
CloudWatch logging for patching and audit visibility
Automatic Launch Template and ASG updates
Preserved existing production configuration
The infrastructure is deployed through a single CloudFormation template, creating a repeatable and auditable workflow with minimal manual intervention.
My Role: AWS DevOps / Cloud Automation Engineer
Technologies: AWS Image Builder, SSM Patch Manager, EC2, Auto Scaling, Lambda, EventBridge, CloudWatch, CloudFormation, IAM, Windows Server, PowerShell
1
118

Designed and implemented an AI-powered AWS SRE automation platform to reduce manual infrastructure monitoring and security reporting.
The solution included two independent workflows:
• AI-powered EC2 monitoring that detects CPU usage patterns, analyzes them with AWS Bedrock, and generates scaling recommendations with an approval-based remediation workflow.
• Automated vulnerability reporting using AWS Inspector, Lambda, S3, Glue, Athena, Bedrock, and QuickSight to generate monthly security insights and executive dashboards.
Built the infrastructure using Terraform with an event-driven, serverless AWS architecture.
The solution improved infrastructure visibility, reduced manual operational effort, accelerated incident detection, and automated security reporting.
1
126

AI Content Automation on AWS | GitHub + Slack + Bedrock
Description:-
I built a production-grade AI content automation system that transforms GitHub commits and Slack conversations into authentic LinkedIn posts.
The solution uses AWS, Terraform, ECS Fargate, and EventBridge to automate content generation, approval, and scheduling.
- Automated content generation from GitHub and Slack activity
- Human-in-the-loop Slack approval workflow
- Security filtering to reduce sensitive data exposure
- Scheduled content publishing with EventBridge
- Production-ready AWS infrastructure managed with Terraform
The result is a reliable, scalable automation pipeline that eliminates repetitive content creation while maintaining human control over what gets published.
My Role: AWS DevOps Engineer
Technologies: AWS ECS · Fargate · Terraform · Docker · CI/CD · EventBridge · GitHub · Slack · AWS Bedrock
1
103

AWS Cloud Engineer | Serverless & Containers | IaC
AWS Cloud Engineer | Serverless & Containers | IaC
View more →

Experienced multi-discipline engineer
Experienced multi-discipline engineer


Senior FullStack & AI Engineer | Product-Driven Solutions


Senior Full-Stack (Mobile, Web) & AI Engineer
- $10k+
- Earned
- 1x
- Hired
- 5.0
- Rating
- 72
- Followers
Senior Full-Stack (Mobile, Web) & AI Engineer


Excited to share some of the backend work I've been doing lately with Supabase! 🚀
Here's a look at what went into building a production-ready backend from scratch:
🗄️ Database Schema Design
Designed a relational schema with multiple interconnected tables: profiles, notes, reminders, conflicts, and a dedicated user_keys table for encryption key management. Every table has proper foreign key relationships, timestamps, and nullable/non-nullable constraints enforced at the DB level.
🔒 Row Level Security (RLS)
Every single table has RLS enabled with two policies: users can only access their own rows, and anonymous access is blocked entirely. No exceptions. Security is enforced at the database layer, not just the application layer.
🔑 Auth & Email Flows
Set up Supabase Auth with email + OAuth support, including full PKCE flow for secure token exchange. Configured deep link redirects for email confirmation and password reset flows, all tested end to end.
⚡ Edge Functions
Built and deployed multiple Supabase Edge Functions handling AI processing pipelines, including JWT validation at the top of every function before any processing begins. The OpenAI API key lives exclusively in Supabase secrets, never in the app or any config file.
🔄 Merge Pipeline
Built a follow-up note merge pipeline as an Edge Function. New facts are appended to existing profiles, duplicates are detected and skipped, conflicts are logged, and resolved reminders are handled gracefully.
📦 Migrations
All schema changes go through versioned migration files under source control. No manual dashboard changes. CI/CD triggers migrations automatically on merge to main.
🔐 Encryption Architecture
Client-side AES-GCM encryption via CryptoKit. Plaintext never sits in the database. Encryption keys are stored in a dedicated RLS-scoped table, fetched after login, and held in memory only for the session duration.
Still a lot more to share about this project. Excited to talk about it publicly when it launches! 👀
5
5
2.5K


Founding AI Engineer, Agents, Automation, Cloud, Full-Stack
- $1k+
- Earned
- 9x
- Hired
- 4.7
- Rating
- 61
- Followers
Founding AI Engineer, Agents, Automation, Cloud, Full-Stack


Website & Agent Experience Design | Framer Enterprise Expert


Website & Agent Experience Design | Framer Enterprise Expert