The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Deployed a cloud-native SIEM integrating Microsoft Azure infrastructure, Windows endpoints, Microsoft 365, and Defender XDR telemetry into a unified detection and response platform.
Wrote KQL analytics rules for real-time threat detection covering: privilege escalation, suspicious PowerShell execution, lateral movement via RDP and SMB, anomalous Azure AD sign-ins, and malware execution patterns. Automated incident response using Azure Logic Apps.
Reduced log ingestion costs by 20% through optimised data collection, balancing coverage against cost without losing detection fidelity.
Published full write-up on Medium: medium.com/@babsib2dk


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started






Related posts

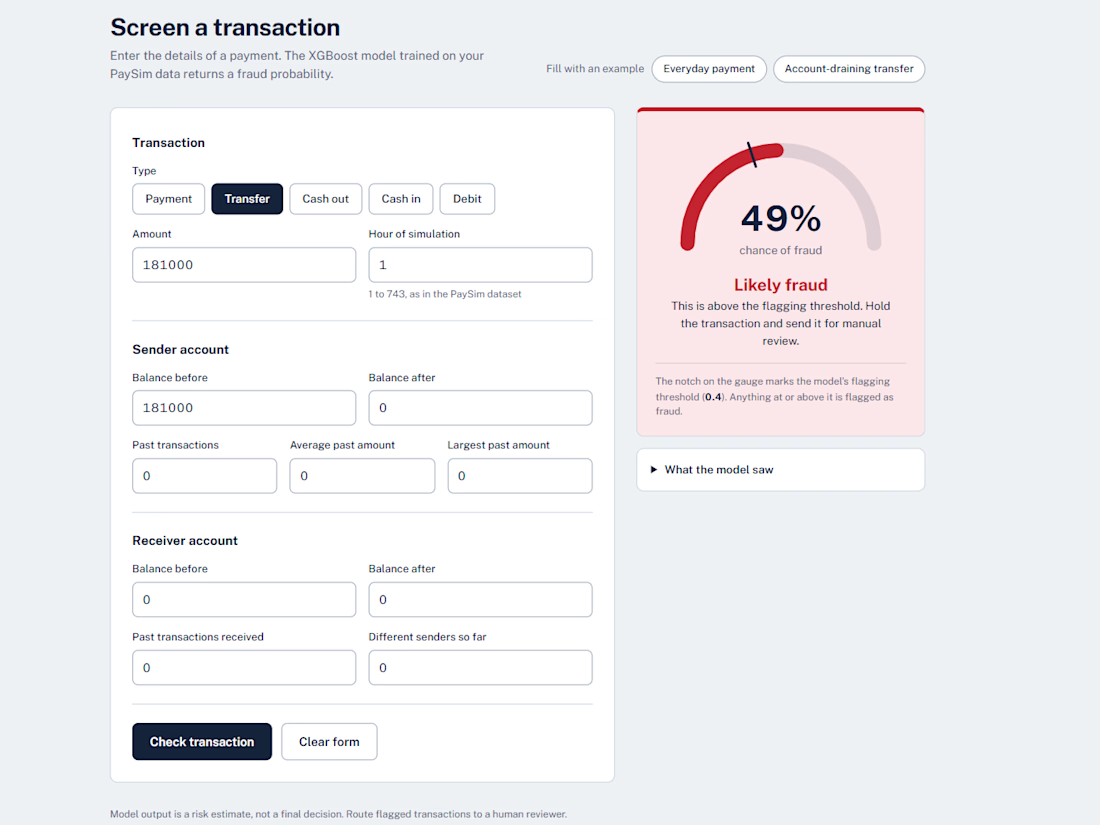
An end-to-end machine learning project for detecting fraudulent financial transactions using the PaySim synthetic transaction dataset.
The project focuses not only on training an XGBoost classifier, but on the complete ML journey: baseline modeling → feature engineering → hyperparameter tuning → threshold tuning → evaluation → live deployment.



SaaS application I designed that leverages Google's speech-to-text API to provide a few basic features that allow users to create audio files using a variety of voice from text.


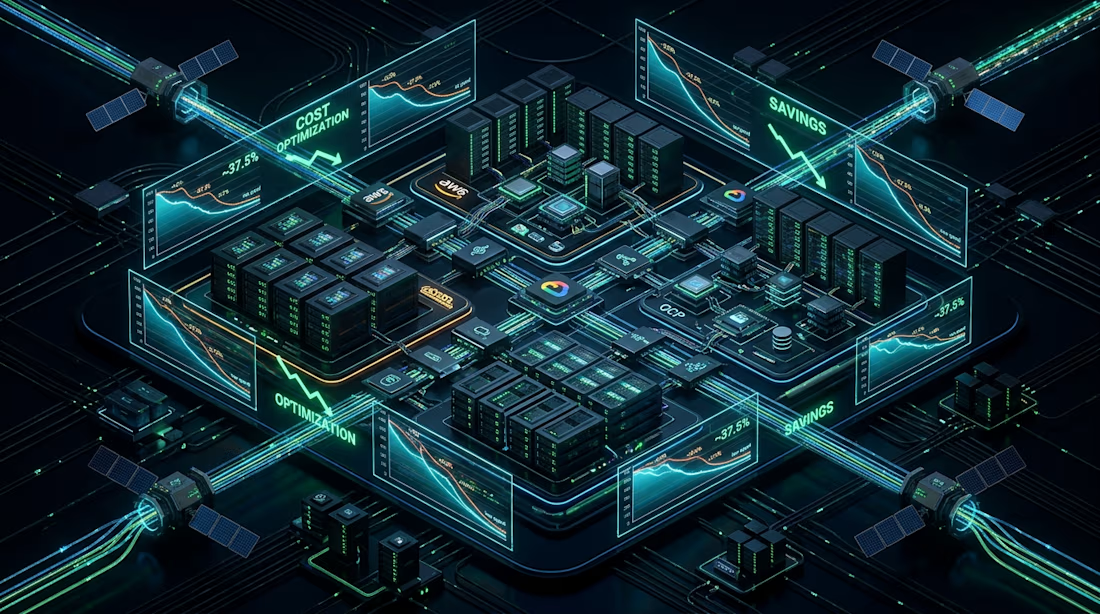
The $3,000/Month Zombie Cloud Storage Drain you don't even know you're paying for.
When engineering teams spin down cloud instances—whether during CI/CD test runs, developer staging teardowns, or microservice migrations—they often assume deleting the virtual machine stops the billing meter.
In reality, default cloud configurations quietly leave the persistent SSD attached to nothing. That unattached 500GB volume sits in your cloud account billing you $85/month indefinitely. Multiply that by dozens of team members and two years of operations, and you have thousands in monthly recurring financial waste.
During our cloud infrastructure audits, here are the three silent money drains we consistently uncover:
1. Orphaned Persistent Disks: Storage volumes detached from defunct compute nodes that continue accumulating high-tier SSD charges every hour.
2. Infinite Snapshot Trees: Backup scripts that trigger daily snapshots but lack automated expiration or retention policies, leaving years of differential disk blobs accumulating compound storage fees.
3. Inter-Zone Egress Gouging: Services in the same cloud region communicating via external public IP addresses or un-peered VPCs, forcing every gigabyte of internal data transfer through expensive external cloud NAT gateways.
At AdvantageMLS, uncovering and automating these exact failure modes—paired with empirical p99 compute rightsizing and CDN edge caching—slashed monthly GCP spend by 35%, delivering $45,000+/year in permanent annualized savings.
Cost governance isn't about telling developers to work slower. It's about eliminating silent architectural waste and codifying lifecycle rules in declarative OpenTofu code.
Audit your cloud footprint with our 2-week Cloud FinOps & Infrastructure Optimization Sprint on Contra: https://contra.com/s/rLYsZ2vY-cloud-fin-ops-and-infrastructure-cost-optimization-sprint
#Cloud #FinOps #AWS #GCP #Terraform #OpenTofu #DevOps #Infrastructure