The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Most small IT teams collect logs but never actually investigate them. That's exactly what attackers count on.
Over the past several months, I've been building hands-on SOC skills — analyzing Windows Event Logs, running SIEM investigations in Splunk and Wazuh, and reconstructing full attack timelines across ransomware, brute-force, and phishing scenarios.
Here's what I've learned: logs don't lie. Every failed login attempt, every unauthorized account creation, every suspicious process execution leaves a trace. The challenge is knowing where to look and how to connect the dots.
Some things I can help you identify from your logs:
• Brute-force attack patterns and successful compromise indicators
• Unauthorized account creation and credential manipulation
• Suspicious authentication anomalies and privilege escalation attempts
• Attack timelines mapped to MITRE ATT&CK techniques
I deliver structured investigation reports that turn raw log data into clear, actionable findings — so you know exactly what happened and what to do next.
If your team is sitting on unreviewed logs or needs support investigating a security event, I'd love to help.
👉 Check out my service below — starting at $30.
https://contra.com/s/7FecLZcc-soc-analyst-log-investigation-and-threat-detection-support?r=alkhal_vio107rc


contra.com
SIEM Log Investigation | Splunk · Wazuh · MITRE ATT&CK by Aaliya Khalil
Read more about SIEM Log Investigation | Splunk · Wazuh · MITRE ATT&CK by Aaliya Khalil on Contra.
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started


Related posts

Some products are hard to explain on a website. Drones that watch forests at night. Sensors on power lines. Software that only matters in the minutes before something goes wrong.
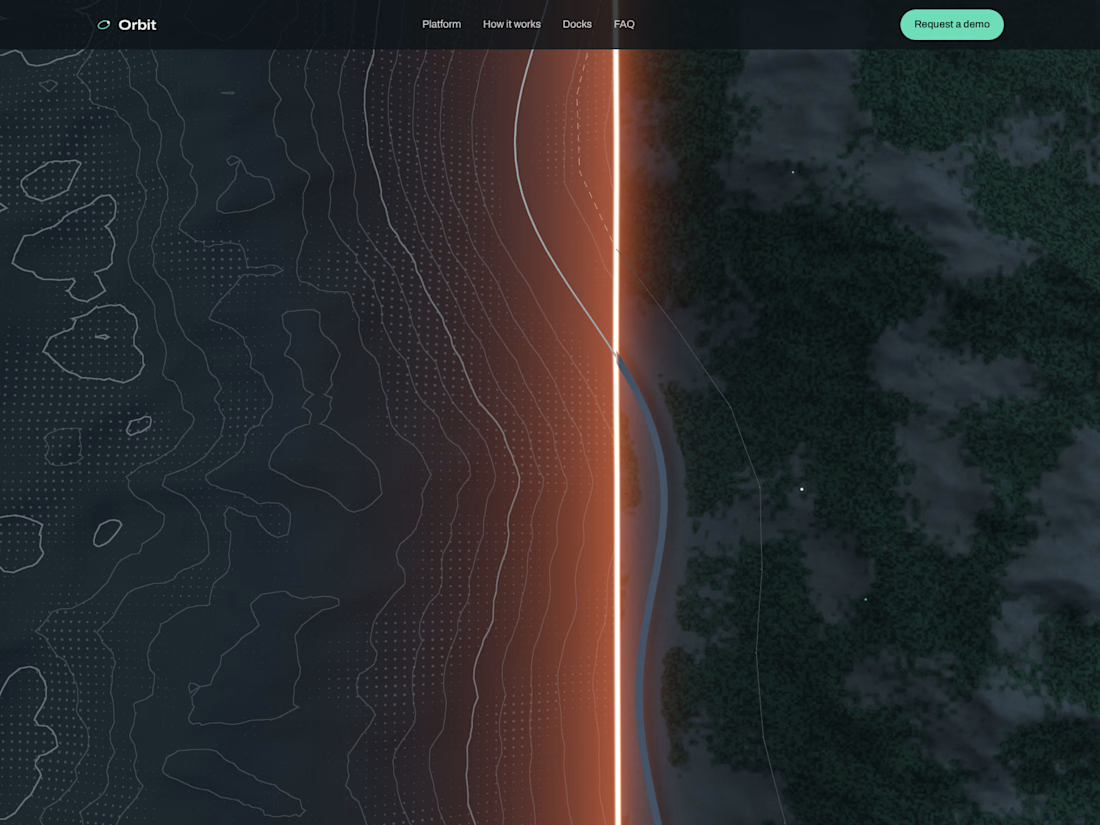
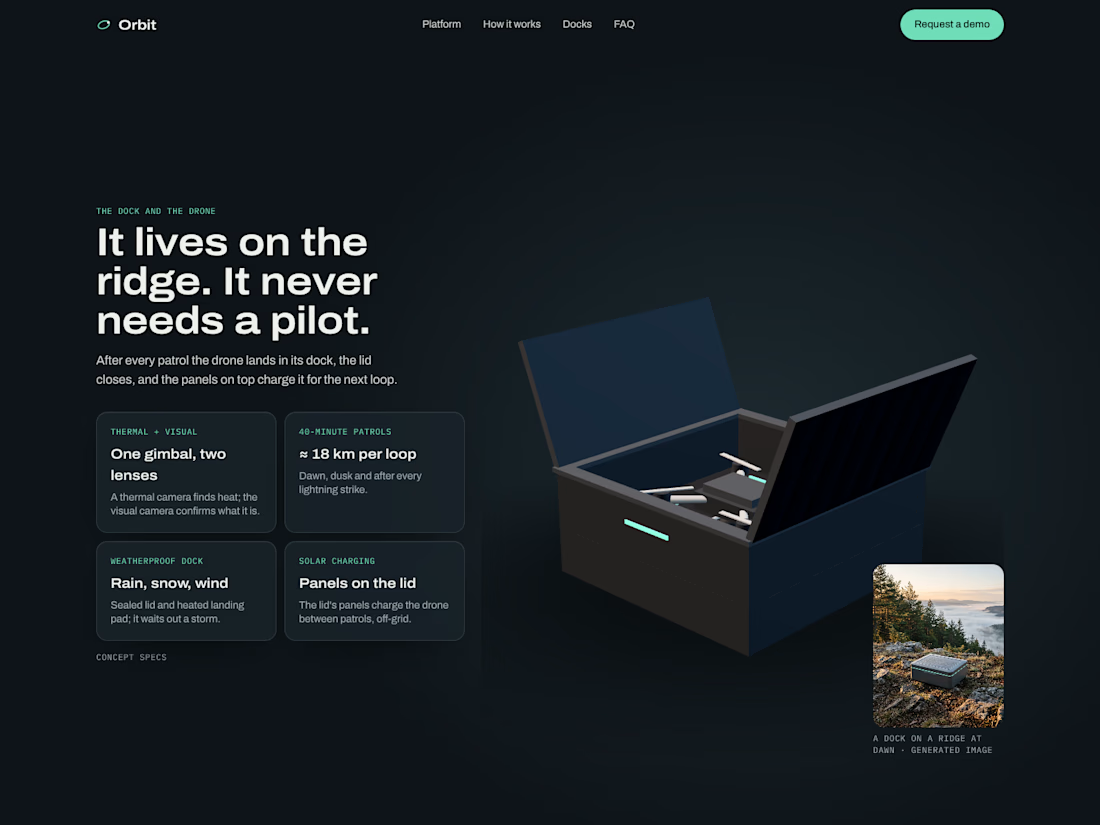
That was the challenge with Orbit, a concept I built for a fictional wildfire detection company. Instead of a page of features, the site shows the product working: you scroll over a valley at dusk, it turns into the live map the operators would use, and you watch one alert happen, from the first hotspot to the crew being sent out.
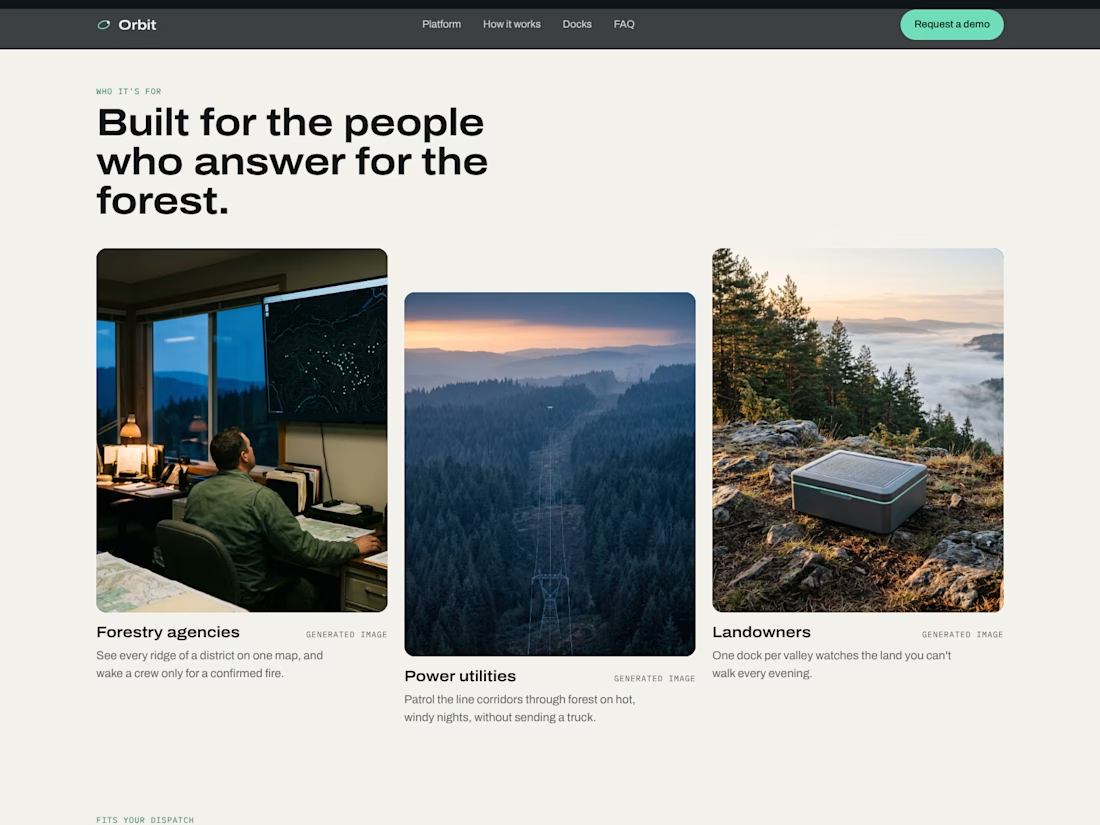
This kind of site works for any company whose product is easier to show than to explain: drone and robotics startups, climate and energy tech, utilities, logistics and fleet software, monitoring and safety platforms. It does the job of a live demo before the first sales call, and it gives investors and buyers the "now I get it" moment in under a minute.
If your product is like that, I'd be happy to talk about what yours could look like.
Full case study on my profile.

What did you use for the valley?

MySecret: Zero-Knowledge Encryption Engine & Biometric Security for Obsidian


The green accents work so well.