The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

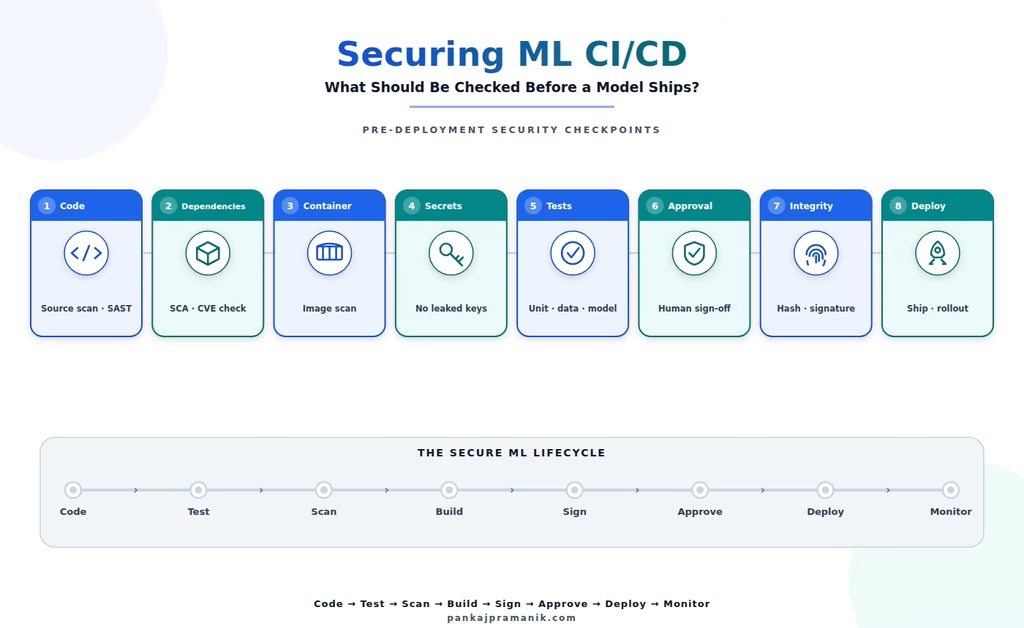
𝗦𝗲𝗰𝘂𝗿𝗶𝗻𝗴 𝗠𝗟 𝗖𝗜/𝗖𝗗: 𝗪𝗵𝗮𝘁 𝗦𝗵𝗼𝘂𝗹𝗱 𝗕𝗲 𝗖𝗵𝗲𝗰𝗸𝗲𝗱 𝗕𝗲𝗳𝗼𝗿𝗲 𝗮 𝗠𝗼𝗱𝗲𝗹 𝗦𝗵𝗶𝗽𝘀?
Shipping an ML model is not only about model accuracy.
Before a model reaches production, the entire CI/CD pipeline should be checked for security, reliability, and integrity.
■ 𝗗𝗲𝗽𝗲𝗻𝗱𝗲𝗻𝗰𝗶𝗲𝘀
• Scan Python packages and libraries for known vulnerabilities.
• Pin dependency versions where possible.
• Avoid unnecessary or outdated packages.
■ 𝗖𝗼𝗻𝘁𝗮𝗶𝗻𝗲𝗿 𝗜𝗺𝗮𝗴𝗲𝘀
• Scan Docker images before deployment.
• Use trusted and minimal base images.
• Remove unnecessary tools and packages from production images.
■ 𝗦𝗲𝗰𝗿𝗲𝘁𝘀
• Never store API keys, database credentials, cloud tokens, or passwords directly in source code.
• Keep secrets outside repositories and container images.
• Use a secure secrets management solution.
■ 𝗔𝘂𝘁𝗼𝗺𝗮𝘁𝗲𝗱 𝗧𝗲𝘀𝘁𝘀
A production ML pipeline should validate more than whether the application simply runs.
• Unit tests
• Integration tests
• Data validation
• Model performance tests
• Security checks
• Deployment validation
■ 𝗔𝗽𝗽𝗿𝗼𝘃𝗮𝗹𝘀
• Add approval gates before sensitive production deployments.
• Review major model, infrastructure, and configuration changes.
• Keep production deployment permissions controlled.
■ 𝗔𝗿𝘁𝗶𝗳𝗮𝗰𝘁 𝗜𝗻𝘁𝗲𝗴𝗿𝗶𝘁𝘆
The model deployed to production should be the exact artifact that passed testing and validation.
• Version model artifacts.
• Verify checksums or signatures.
• Track container versions.
• Protect artifacts from unauthorized modification.
• Maintain traceability from training to deployment.
𝗔 𝘀𝗲𝗰𝘂𝗿𝗲 𝗠𝗟 𝗱𝗲𝗹𝗶𝘃𝗲𝗿𝘆 𝗳𝗹𝗼𝘄:
Code → Test → Scan → Build → Sign → Approve → Deploy → Monitor
MLOps helps us ship models reliably.
DevSecOps helps us make sure they are shipped securely.
What security checks do you include in your ML CI/CD pipeline?
#MLOps #DevSecOps #CICD #MLSecurity #MachineLearning #CloudSecurity #Docker #CyberSecurity #SoftwareEngineering #OpenToWork
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts



making your venture ready for agency-level work while you focus on building.
for funded data, AI & tech startups.

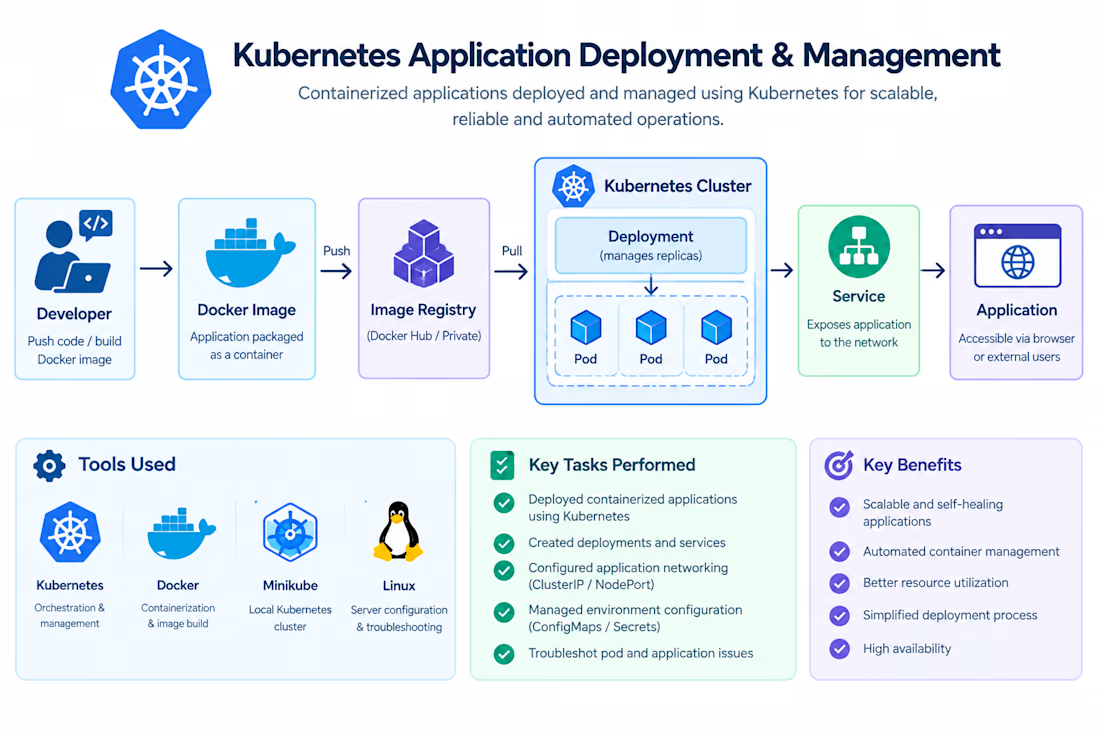
Worked on deploying and managing containerized applications using Kubernetes.
The deployment workflow involved creating Kubernetes Deployments and Pods, exposing applications through Services, and managing application configuration. I also worked with Docker and Minikube for containerized application testing and deployment.