The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost
The Cloud NAT bill shock: Why downloading backups and container images from object storage quietly drains thousands of dollars in managed NAT processing fees.
When auditing AWS or GCP monthly cloud bills, engineering leaders are frequently stunned by one line item that outpaces their EC2 compute or database spend: **Managed NAT Gateway Processing Fees**.
A common architecture in private cloud VPCs places application containers and backend worker nodes in private subnets with no public IPs. To access the internet, outbound traffic is routed through an AWS NAT Gateway or GCP Cloud NAT.
The silent financial drain occurs when these private workloads interact with their cloud provider's own object storage: 1. The Double-Billed Traffic Loop: A backup job archives a 10TB database to Amazon S3 or Google Cloud Storage. Or a CI/CD runner downloads 50GB of container base images every morning. Because S3 and GCS use public IP addresses, the cloud routing table sends this multi-terabyte internal traffic through the managed NAT Gateway. 2. The $0.045/GB Processing Surcharge: AWS charges ~$0.045 per GB for NAT Gateway data processing, *in addition* to standard data transfer fees. Moving 20TB of database backups and images through a NAT Gateway costs $900 every month—for traffic that never leaves the cloud provider's physical datacenter! 3. Artificial Bandwidth Throttling: Managed NAT gateways enforce throughput caps. During major data transfers, the gateway throttles, causing build pipelines to stall and backups to run for hours.
The FinOps remediation is simple, immediate, and 100% free: • Deploy Gateway VPC Endpoints for S3 & DynamoDB: In AWS, configure a Gateway VPC Endpoint for Amazon S3 and DynamoDB. This updates your subnet route tables with an internal prefix list, routing all S3 traffic over the internal AWS backbone with **zero NAT processing fees**. • Enable Private Google Access: In GCP, enable Private Google Access on every private subnet. Internal instances can now reach all Google APIs (Cloud Storage, BigQuery, Artifact Registry) directly over private routing, bypassing Cloud NAT entirely. • Restrict NAT Strictly to Public Internet APIs: Ensure your NAT gateway processes only genuine external outbound requests (third-party webhooks, GitHub API, external payment processors). • Automate Route Audits with OpenTofu: Embed VPC endpoint verification directly into your IaC pipelines, preventing newly provisioned subnets from routing internal traffic through NAT gateways.
Eliminate useless cloud surcharges and keep your network data transfers on private, zero-cost cloud backbones.
Slash wasteful cloud expenditures by 30%–50% with our 2-week Cloud FinOps & Infrastructure Cost Optimization Sprint on Contra: https://contra.com/s/rLYsZ2vY-cloud-fin-ops-and-infrastructure-cost-optimization-sprint
#FinOps #Cloud #AWS #GCP #Infrastructure #DevOps #Architecture

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Challenges
View all


Related posts

The Let's Encrypt 429 lockout: Why automatic ACME issuance in ephemeral testing environments paralyzes releases and how centralized storage prevents outages.
Modern web servers like Caddy have revolutionized HTTPS by enabling automatic, zero-configuration TLS certificate issuance through Let's Encrypt and ZeroSSL. You point a domain name to your server, start the daemon, and within seconds, production-grade TLS 1.3 certificates are provisioned and renewed automatically.
However, when engineering teams introduce automated ACME servers into dynamic CI/CD staging environments, ephemeral Kubernetes clusters, or multi-node container stacks, a catastrophic failure mode frequently occurs: **the Let's Encrypt rate limit lockout**.
1. The Ephemeral Container Trap: In ephemeral staging or testing clusters, containers spin up and tear down constantly. If certificate storage is not persistently mounted to disk, every newly spawned container requests fresh certificates from Let's Encrypt production endpoints upon startup. 2. The 5-Certificate-per-Week Ceiling: Let's Encrypt enforces strict production rate limits: a maximum of 5 duplicate certificates per exact domain per week, and 50 new certificates per registered domain per week. Once exceeded, Let's Encrypt returns HTTP 429: ``too many certificates already issued for exact set of domains``. 3. Blocked Production Deployments: The rate limit cannot be manually reset or cleared by support tickets. Your domain is locked out for an entire 7-day rolling window. If this happens to a production domain or wild-card sub-domain during a scheduled release, the deployment halts completely.
Hardened enterprise TLS architecture isolates staging environments and centralizes certificate storage: • Use the Let's Encrypt Staging Environment for Testing: Configure test environments, PR preview apps, and staging clusters to point explicitly to the ACME staging endpoint (in Caddy: ``acme_ca https://acme-staging-v02.api.letsencrypt.org/directory``). Staging endpoints enforce massively higher rate limits, allowing unlimited test deployments without consuming production quotas. • Shared Storage Backends for Clustered Ingress: In multi-node proxy deployments, never allow individual instances to request certificates independently. Configure shared storage modules (e.g., PostgreSQL, Redis, or S3 storage plugins) so that all proxy instances share a single authoritative certificate cache and distributed mutex lock. • Implement Internal Enterprise CA for Staging: For non-public internal domains and staging environments, bypass public ACME entirely. Issue certificates using an internal FreeIPA or step-ca Private PKI, eliminating third-party rate limits and external dependency risks. • Graceful Fallback Strategies: Ensure ingress proxies maintain valid fallback certificates and cache existing valid keys on disk before attempting renewal.
Eliminate TLS lockout risks and guarantee seamless, automated certificate lifecycles across all environments.
Deploy hardened, high-availability ingress with our 1-week High-Availability Ingress & Hardened Reverse Proxies Sprint on Contra: https://contra.com/s/Ec6sEAUW-high-availability-ingress-and-hardened-reverse-proxies-ha-proxy-and-caddy
#Security #Infrastructure #DevOps #Architecture #SRE #Networking #Cloud

Same 2s loop, 80x60 fixed, 3 diamonds at 0s / 1s / 2s — just re-skinned from Gold / BLACK EAGLE INDUSTRIES 1677877 to Purple-Blue / CLI Ghost with dot grid. You don't have to win, just be present.


Love the "just be present" attitude 🤟 Showing the same ghost reskinned is a good start. When you post the full submission, keep going with that idea!

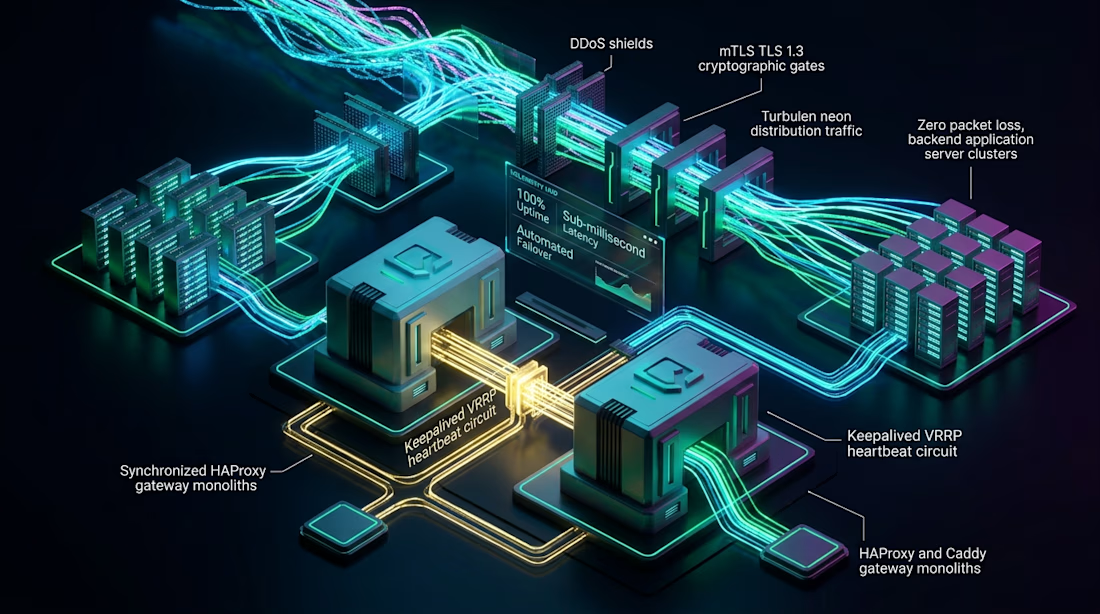
Water Infrastructure & Spatial Resource Mapping
3D Infrastructure Visualizer / Spatial Designer
Overview:
Comprehensive, enterprise-grade isometric vector asset library and spatial infographic mapping the full lifecycle of industrial, agricultural, and urban water management infrastructure. Unified 14 distinct engineering sectors into a clear, high-fidelity presentation framework.
Key Deliverables:
1) High-fidelity vector visualizations of power generation plants, heavy wastewater treatment facilities, and agricultural matrices.
2) Formulated a dynamic multi-zone terrain overlay, from mountain reservoirs to coastal filtration hubs.
3) Standardized corporate color system optimized for environmental SaaS software and regional planning dashboards.