The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

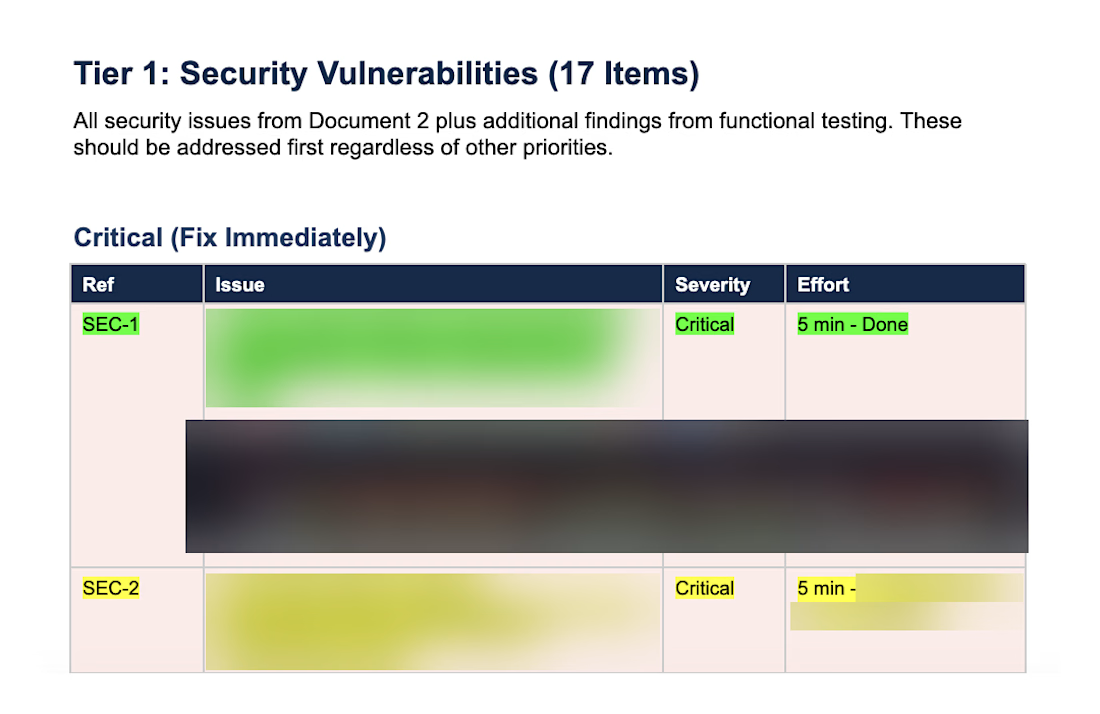
Anyone on the internet could spend my client's money.
No login. No limit. One AI endpoint in his Replit-built app, wide open, running on his OpenAI and Gemini bill.
The fix took 5 minutes. Finding it took a full audit.
It was one of 17 security issues in an app that "worked fine."
That's vibe coding. A study of 200 live vibe-coded apps found 91% had at least one vulnerability. The app works. That's exactly why nobody looks.
Here's the part people get wrong though. We didn't rebuild it. His idea wasn't validated yet and the budget was tight. So we fixed security first, then the code vulnerabilities, then brought in QA to hunt bugs one by one.
Another founder came to us with a Bolt app and two months of proven demand. We opened the codebase and didn't patch a thing. We started over. Me, a dev, a QA, 15 weeks, production-ready.
Same problem. Opposite calls. Both right.
Unvalidated idea? Fix what can hurt you and go find customers. Validated idea? Rebuild it properly.
Built something on Lovable, Bolt, Replit or Cursor and not sure which camp you're in? DM me.
The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started








Related posts

AI made exploration much cheaper for me
i'm not sure it made the work more enjoyable.
i enjoyed manually exploring different directions
even when it took a lot of effort
once i had a solid foundation,
new screens came together pretty easily
now i can generate a dozen directions and get something functional quickly
but it's often almost unusable.
most of my work comes afterward:
rearranging things,
discarding bad ideas,
removing generated slop...
feeling like this limping little guy
protecting you from the slop

That limping little guy protecting us from the slop is painfully relatable, Anton. I feel the same: generating a dozen directions is cheap now, but the rearranging, discarding and de-slopping afterward is where the real craft lives.

Your MVP doesn’t need to be tested by 1,000 people. It needs to be tested by 5 the right ones.
Find 5 people who actually have the problem, put the app in their hands, and watch them use it without helping. Don’t explain, don’t hint, just stay quiet. 👀
You’ll see the same confusion repeat by person 3. That’s your top fix, and it costs you one afternoon instead of one failed launch ☕
Early feedback isn’t about volume. It’s about watching real people get stuck



A new case study shouldn't need a new build.
Every project on The Offsite Agency's site runs on one template, so adding work is just content. Visitors grew six times in under eight weeks after the new site launched.
Designed by The Offsite Agency, built by Displace. Full case study on our profile.
How much of your work never made it onto your site?


Nice work!!