The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

I conducted an authorized AI security assessment of Lily Cybersecurity 7B to evaluate how effectively a hardened system prompt could resist jailbreak and prompt injection attacks.
Using Prompt Fuzzer, I ran 15 attack techniques against the model. The system prompt successfully blocked 8 attempts, including most roleplay and social engineering attacks. The successful bypasses mainly used translated or altered wording to disguise the intent of the request.
This project demonstrates why system prompts should be supported by input validation, moderation, output filtering, and continuous AI red team testing.


The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

🚀 Building in Public — Paresh Textile
Today, I recorded a walkthrough of one of my projects — Paresh Textile — and shared the project on GitHub.
It’s always satisfying to look back at something you’ve built and see how much you’ve learned along the way.
🎥 In this recording, I’m showcasing the project, its implementation, and the work behind it.
One project at a time. One improvement at a time.
Keep building. Keep learning. 🚀


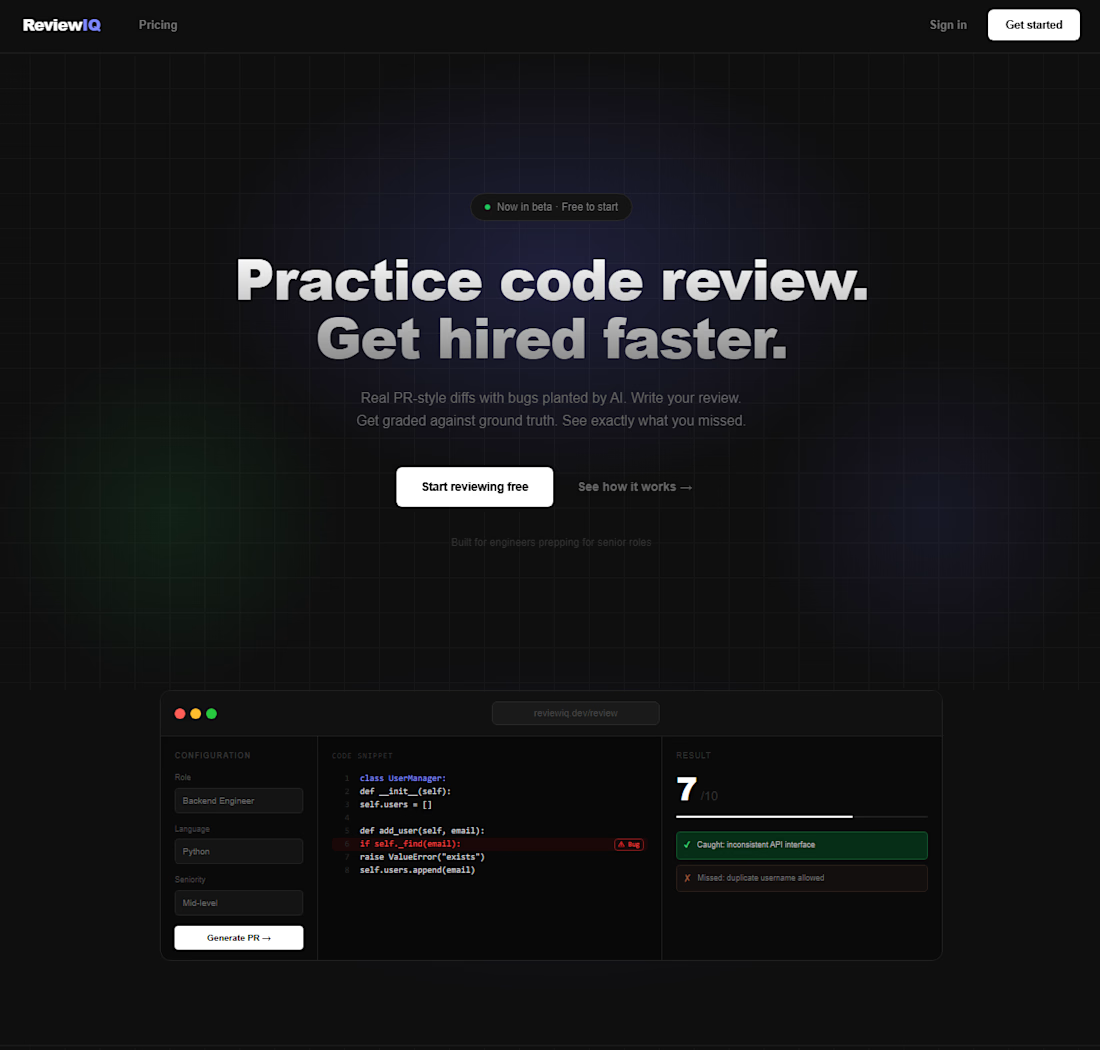
I built ReviewIQ because technical interviews don't always test whether you can actually review code.
ReviewIQ is an AI-powered code review interview trainer built for software engineers.
You pick a role, language, and seniority, then get a realistic PR diff with bugs intentionally planted in it.
You write your review.
Then the system grades it against the actual bugs, shows what you caught, what you missed, and gives you feedback on how a stronger reviewer would approach it.
The interesting part was building the grading system so it isn't just "AI thinks your answer is good." The bugs have a known ground truth, so the review can be evaluated against something concrete.
Built with Next.js, Supabase, PostgreSQL, OpenAI, and Lemon Squeezy.
I'm interested in building more products where AI isn't just a chat box, but an actual part of the product experience.

The known-ground-truth approach is a great product decision—it makes the feedback feel earned rather than like an opaque AI verdict. I also like that the flow tests the actual review skill instead of rewarding pattern-matching in interviews.

Big thanks for sharing the prompt, I'm gonna try it now.
