Public-Source CTI & Detection Evidence Framework

Andrey Pautov

Public-Source CTI & Detection Evidence Framework
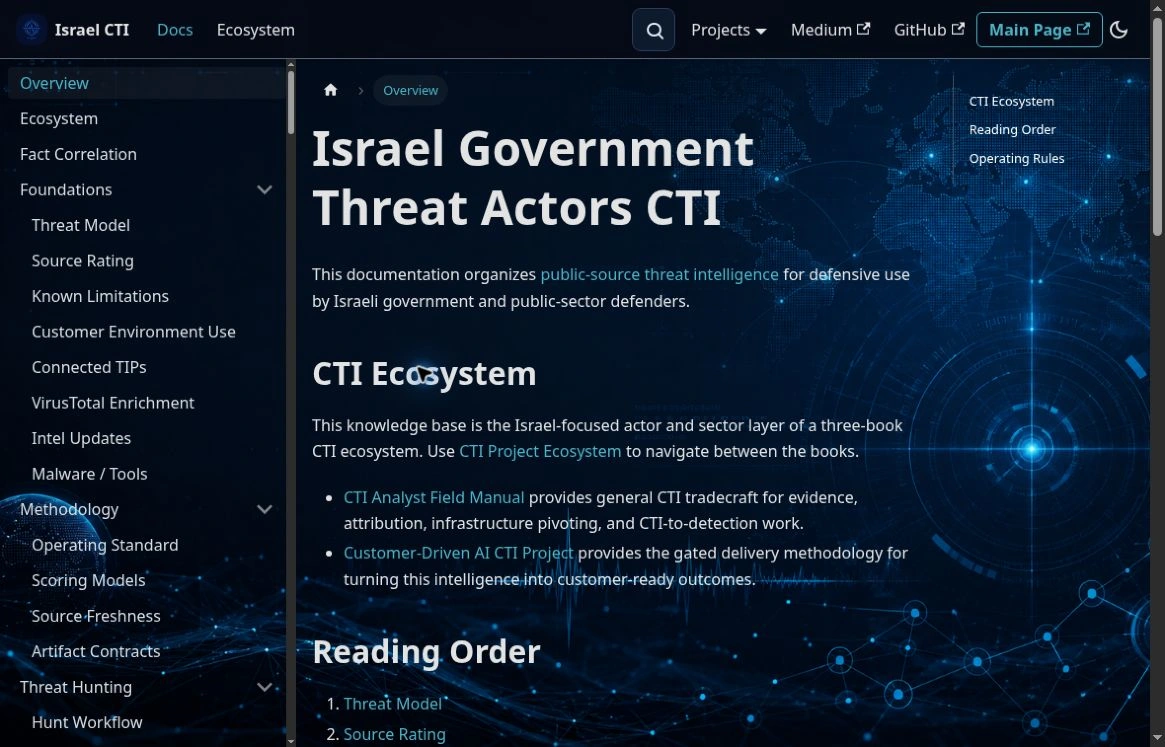
I built a public-source CTI research framework to make the reasoning behind defensive security decisions inspectable. It organizes reporting relevant to Israeli government, public-sector, municipal, critical-infrastructure and supplier exposure.
My contribution
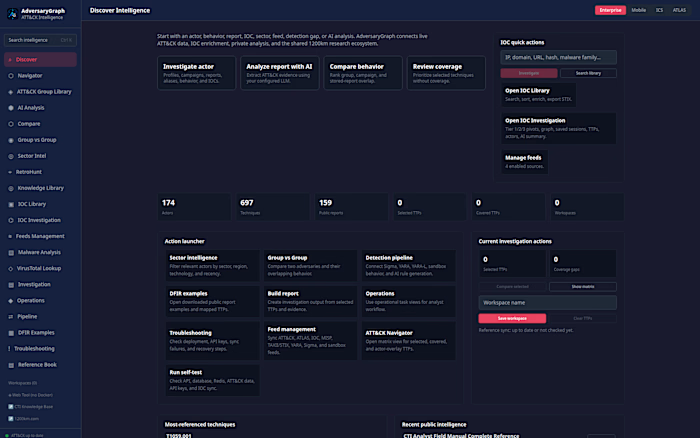
My contribution connects actor and tool research with source registers, confidence notes, ATT&CK mappings, worked cases, hunt templates, Sigma examples, KQL queries and telemetry requirements. The methodology separates source reliability, analytical confidence and missing evidence. Attribution stays tied to the cited reporting and its limits.
Scope and limitations
This is independent public research, not a commissioned government engagement or affiliation. Synthetic tests support limited checks of sample rule behavior; they do not establish production false-positive rates or operational effectiveness. Operational use requires local field mapping, historical replay, benign-baseline review and owner approval.
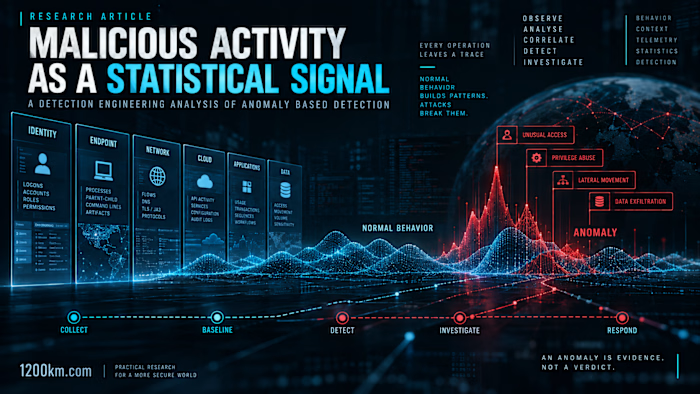
Cover: public-source CTI knowledge base and methodology documentation.
Like this project
Posted Oct 1, 2026
Built a defensive research framework connecting public threat reporting, traceable evidence, ATT&CK mappings, hunts and detection examples.
Likes
0
Views
0