AdversaryGraph: CTI-to-Detection Workbench

Andrey Pautov

AdversaryGraph: CTI-to-Detection Workbench
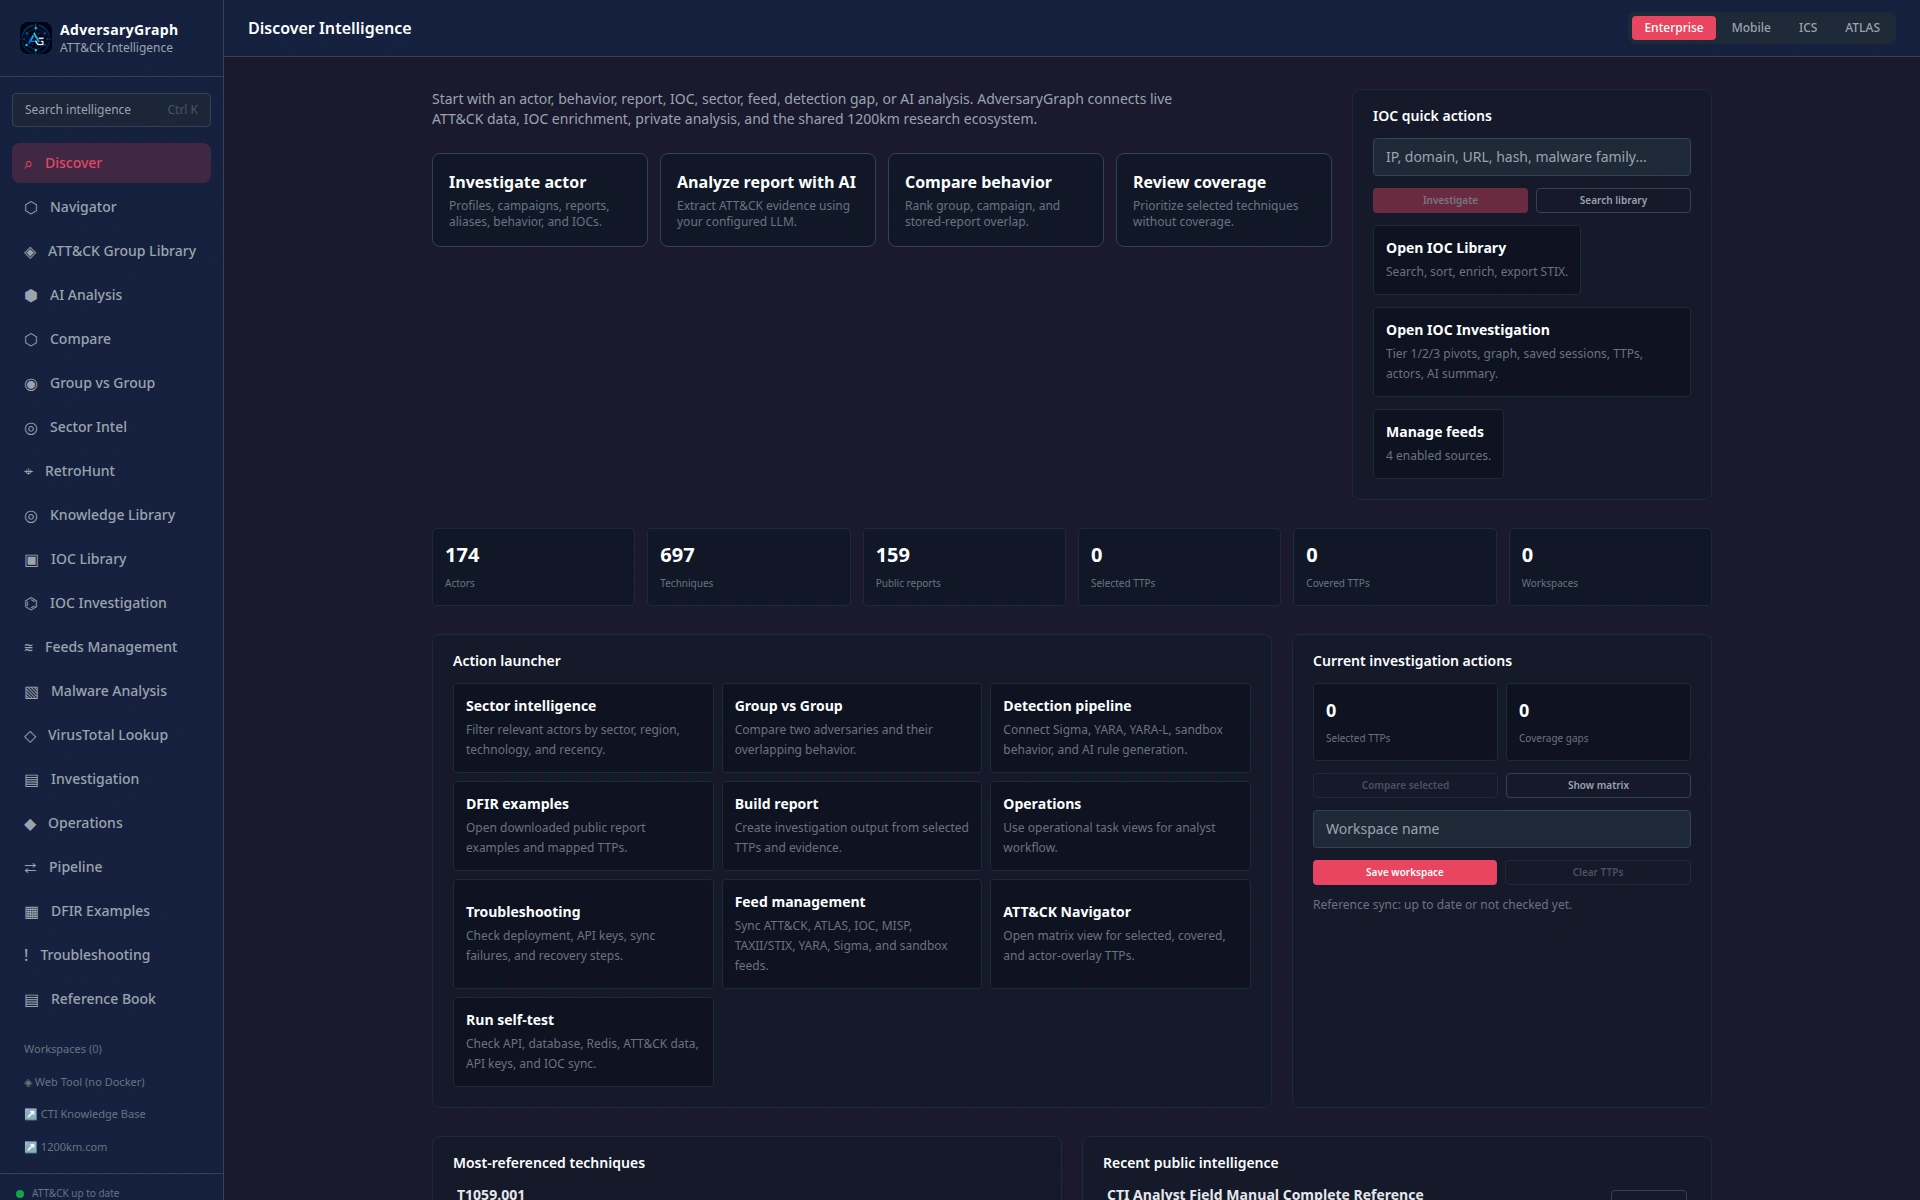
I built AdversaryGraph to make the path from a threat-intelligence claim to a detection hypothesis easier to inspect. The workbench connects source evidence, ATT&CK-aligned behavior, required telemetry, candidate detection logic, validation records and analyst decisions.
My contribution
My contribution includes the application workflow, evidence model and research-oriented interfaces that keep source claims and testing limits visible. Reviewers can inspect the public repository, documentation and demonstrations to understand how evidence supports a proposed hunt or detection.
Scope and limitations
This is an independent research project. Demonstrations and fixtures do not establish production effectiveness, customer adoption or validated detection coverage. Operational use requires environment-specific telemetry checks, testing and analyst review. The source is available under the repository’s Personal Use License.
Cover: published AdversaryGraph product screenshot; historical interface. It is not a claim about the current version or detector effectiveness.
Like this project
Posted Oct 1, 2026
Built a self-hosted workbench connecting threat-intelligence evidence, ATT&CK behavior, telemetry needs and detection hypotheses.
Likes
0
Views
0