
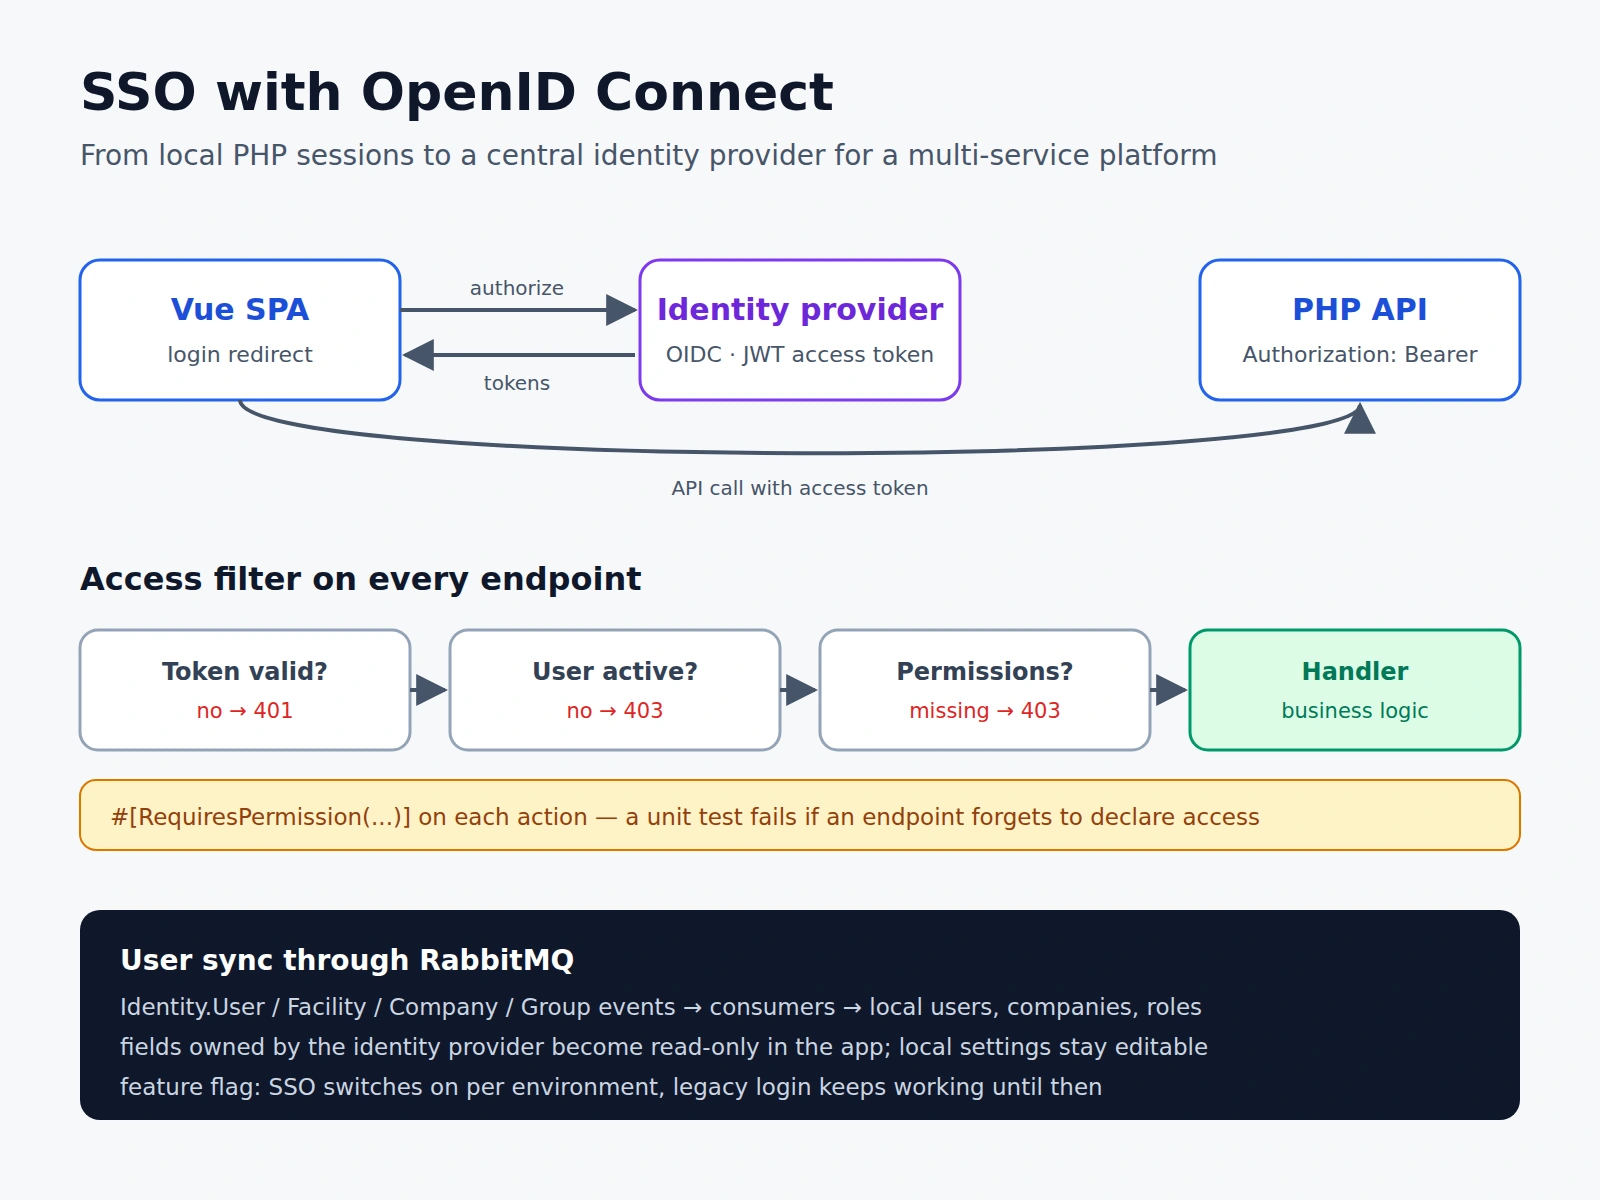
Moved login from local PHP sessions to a central identity provider (OpenID Connect).
What I did: Bearer-token access for new API endpoints with an access filter (valid token, active user, required permissions declared on each action, a unit test that fails if an endpoint forgets to declare access); synchronisation of users, companies and permission groups from the identity provider through RabbitMQ; provider-owned fields read-only, local settings editable.
SSO switches on per environment behind a feature flag, legacy login keeps working until then.
0 likes · 0 views · Nov 20, 2026
Login through a central identity provider, Bearer-token API access with declared permissions, user sync over RabbitMQ.


