Aegis: AI Vulnerability Reporting Portal

Rimon Debnath


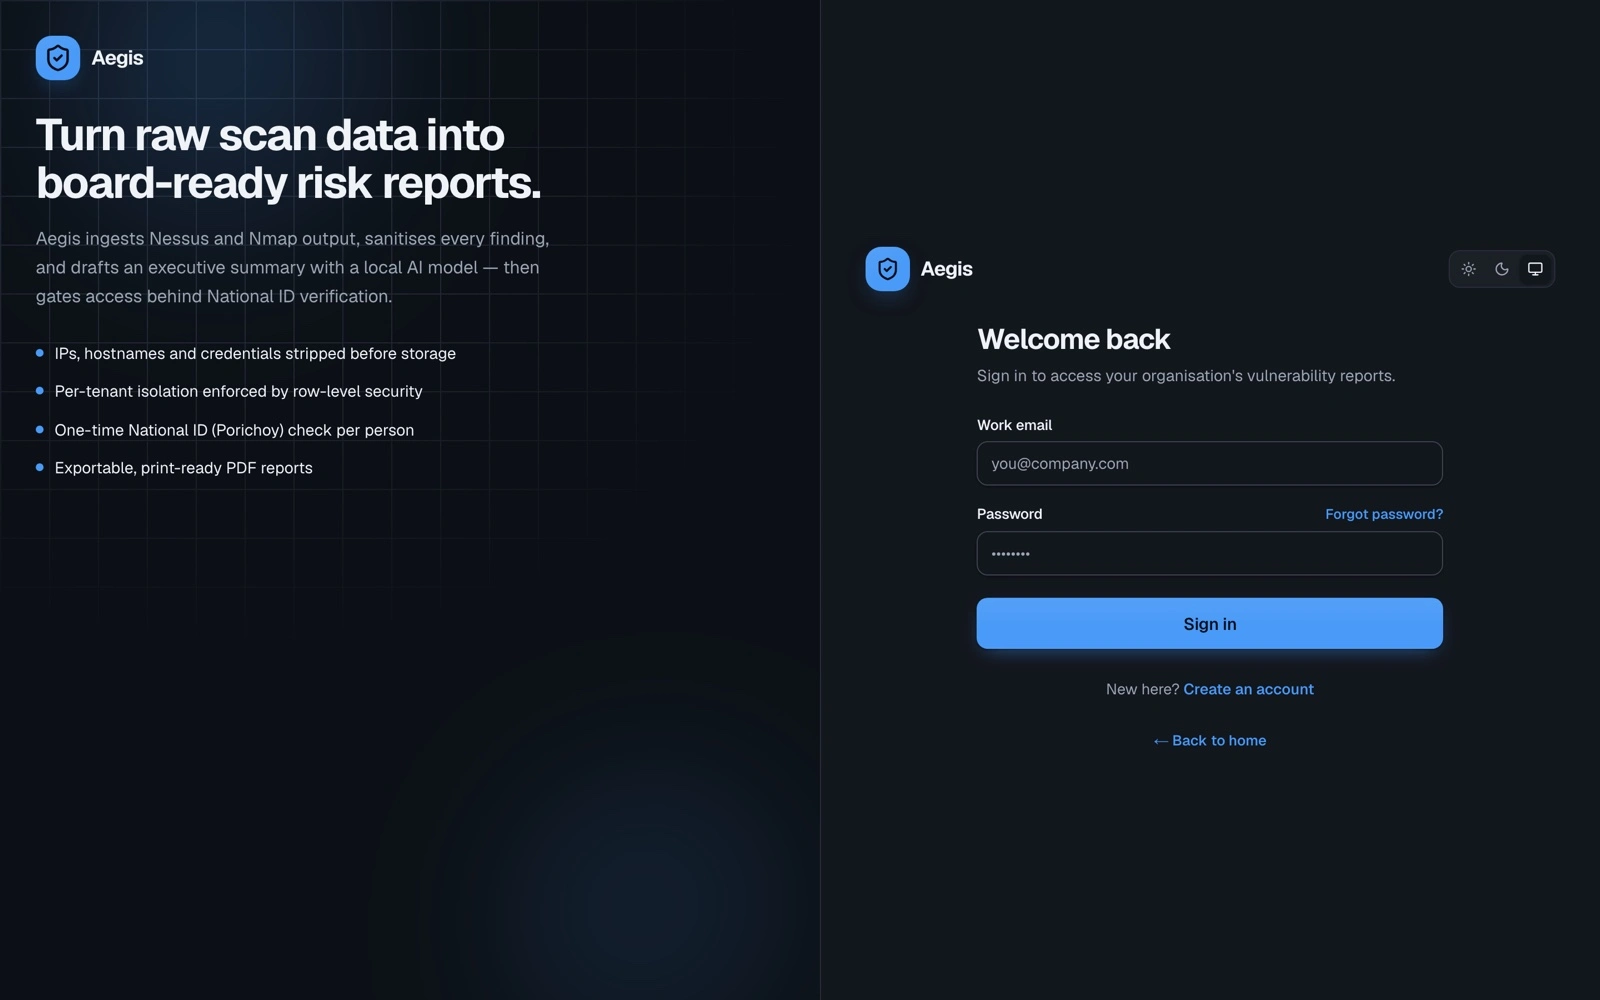
Aegis is a multi-tenant vulnerability reporting portal I designed and built solo as my own product (not client work). Security teams upload raw Nessus or Nmap scan exports, and their clients get a clean, executive-ready risk report.
Live: aegis-portal-navy.vercel.app · Code: github.com/Rimonok12/Vapt_Aegis
How it works
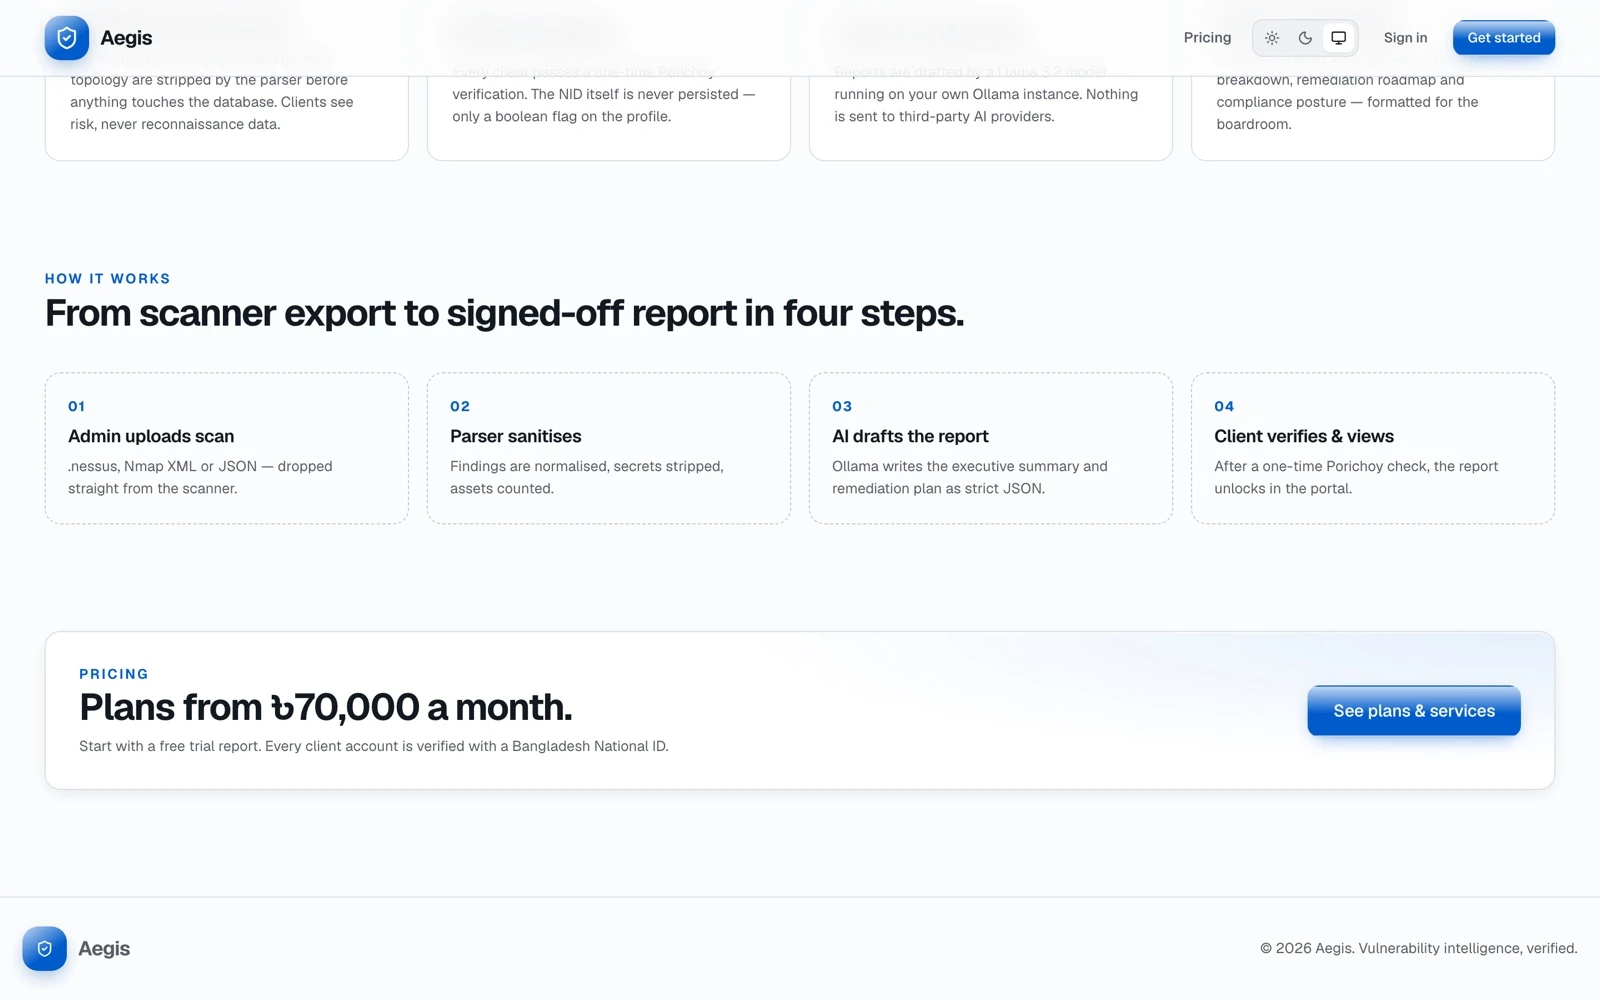
A Python FastAPI service parses each scan and strips IPs, hostnames, MAC addresses, credentials and emails before anything is stored. Raw files are never saved.
A local Llama 3.2 model (Ollama) drafts the executive summary and remediation plan as strict JSON, so scan data never goes to a third-party AI provider. A rules engine takes over when no model is reachable.
Next.js 16 and Supabase row-level security keep every organisation's data isolated.
Client access is gated by a one-time Bangladesh National ID check; the ID itself is never stored.
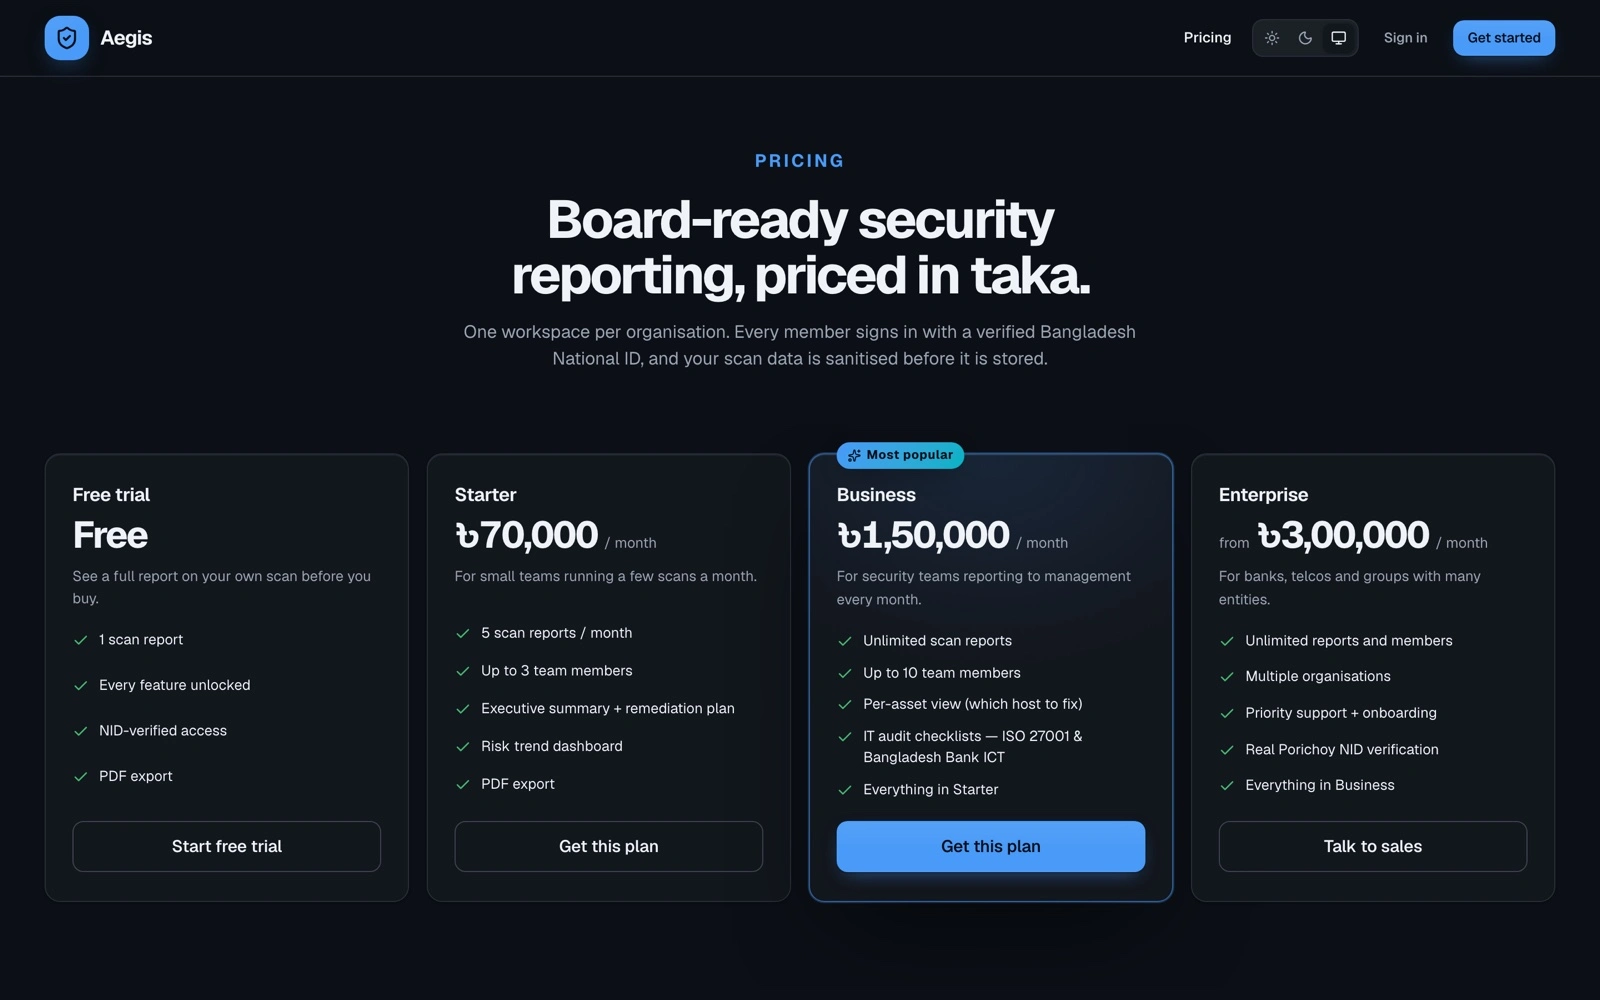
Severity charts, risk trend, one-click PDF export, an AES-256-GCM encrypted per-asset view, ISO 27001 and Bangladesh Bank ICT audit checklists with weighted scoring, and plan quotas.
Stack: Next.js 16, React 19, TypeScript, Supabase (Postgres, Auth, RLS), FastAPI, Python 3.12, Ollama, React-PDF, Recharts, Vercel.
Like this project
Posted Nov 1, 2026
Built solo: a multi-tenant portal that turns raw Nessus/Nmap scans into executive risk reports with a local LLM. Next.js, FastAPI, Supabase.
Likes
0
Views
0