
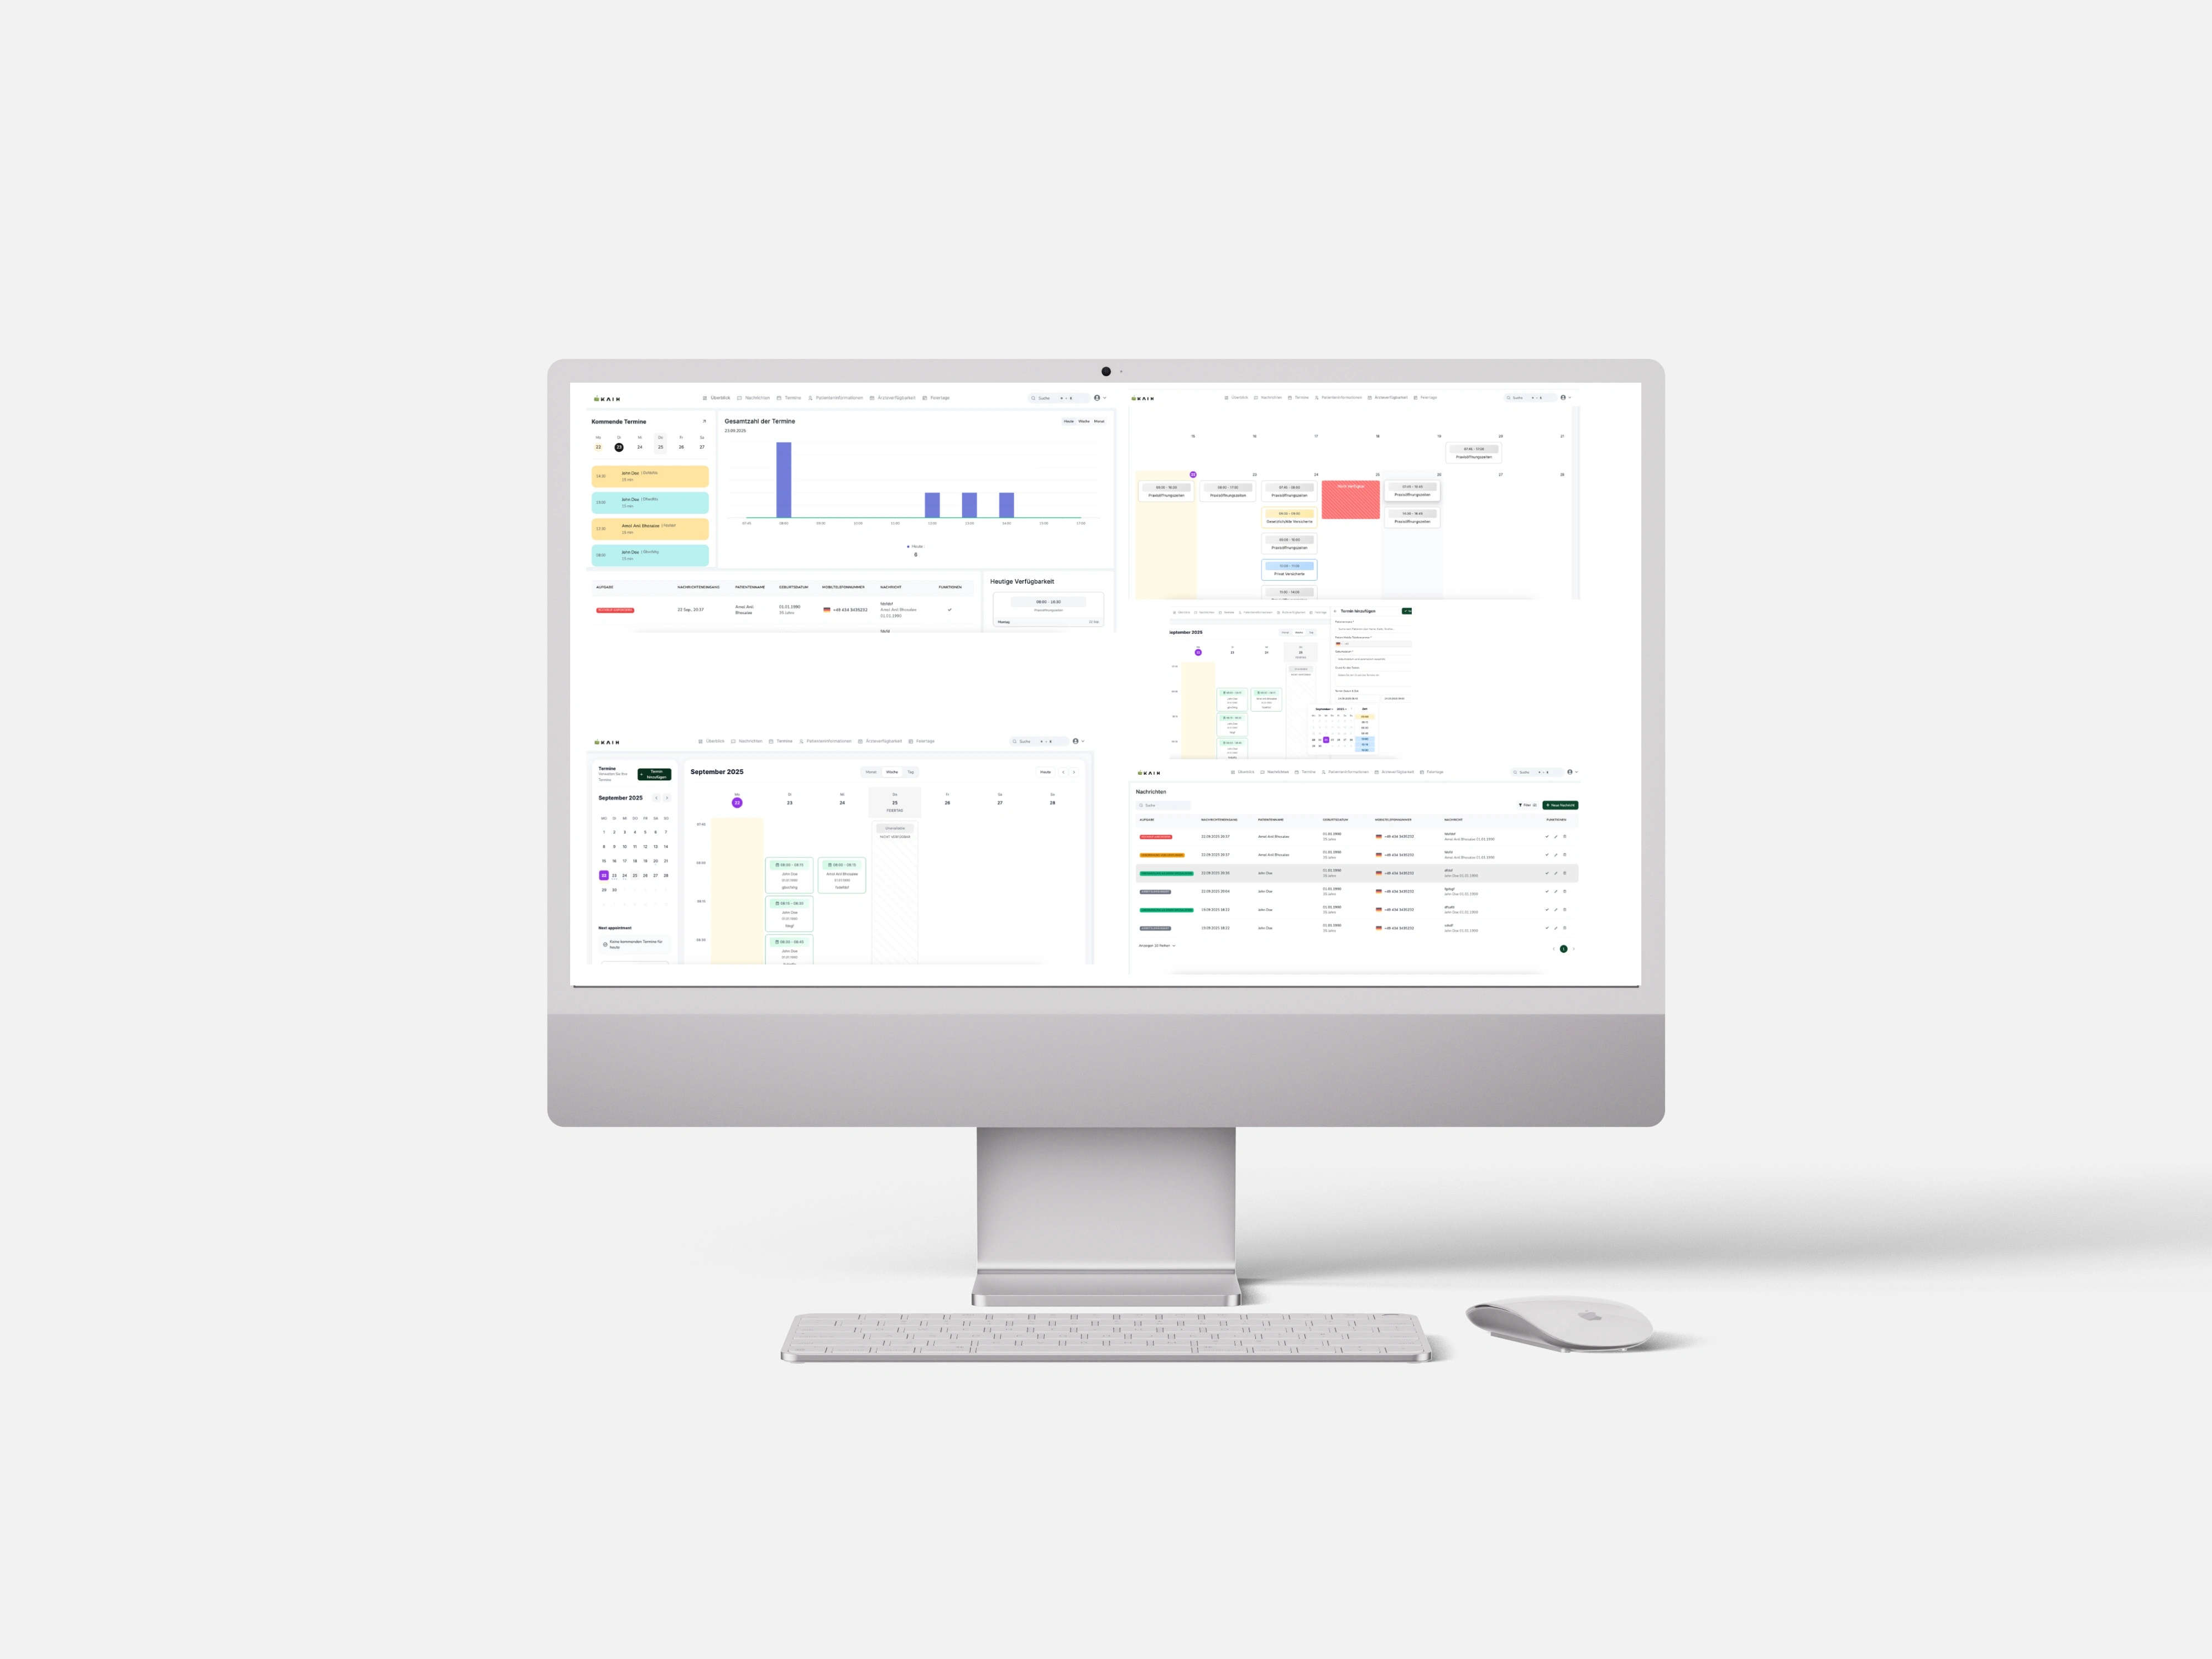
GDPR-Compliant AI Appointment Scheduling Healthcare SaaS
IndustryHealthcare / HealthTechLocationGermanyCompliance FrameworkGDPR-Compliant, Consent-Driven Data ModelPlatform TypeHealthcare Appointment Scheduling SaaSTimeline8 months, spec to productionTech StackReact · Node.js · TypeScriptInfrastructureAWS ECS · Docker · EncryptedKey IntegrationWhatsApp automation + AI chatbotKey Result70% less manual handling · 24/7 booking · ~2mo rework saved
The founder arrived with Node.js + Handlebars already chosen. In the first conversation, before any contract, I recommended React + Node, not on preference, but because consent-driven UI and real-time WhatsApp would have broken the template approach by month 3.
The principle: the regulatory layer comes first. GDPR isn't a compliance checkbox, it's a data model. Consent, residency and audit logging were designed into the schema from day one, avoiding the 3 to 4 months of rework a compliance-as-afterthought build incurs.
Outcomes delivered
70% less manual appointment handling
24/7 booking via WhatsApp
~2mo rework saved by one architecture decision
0 likes · 26 views · Sep 22, 2025
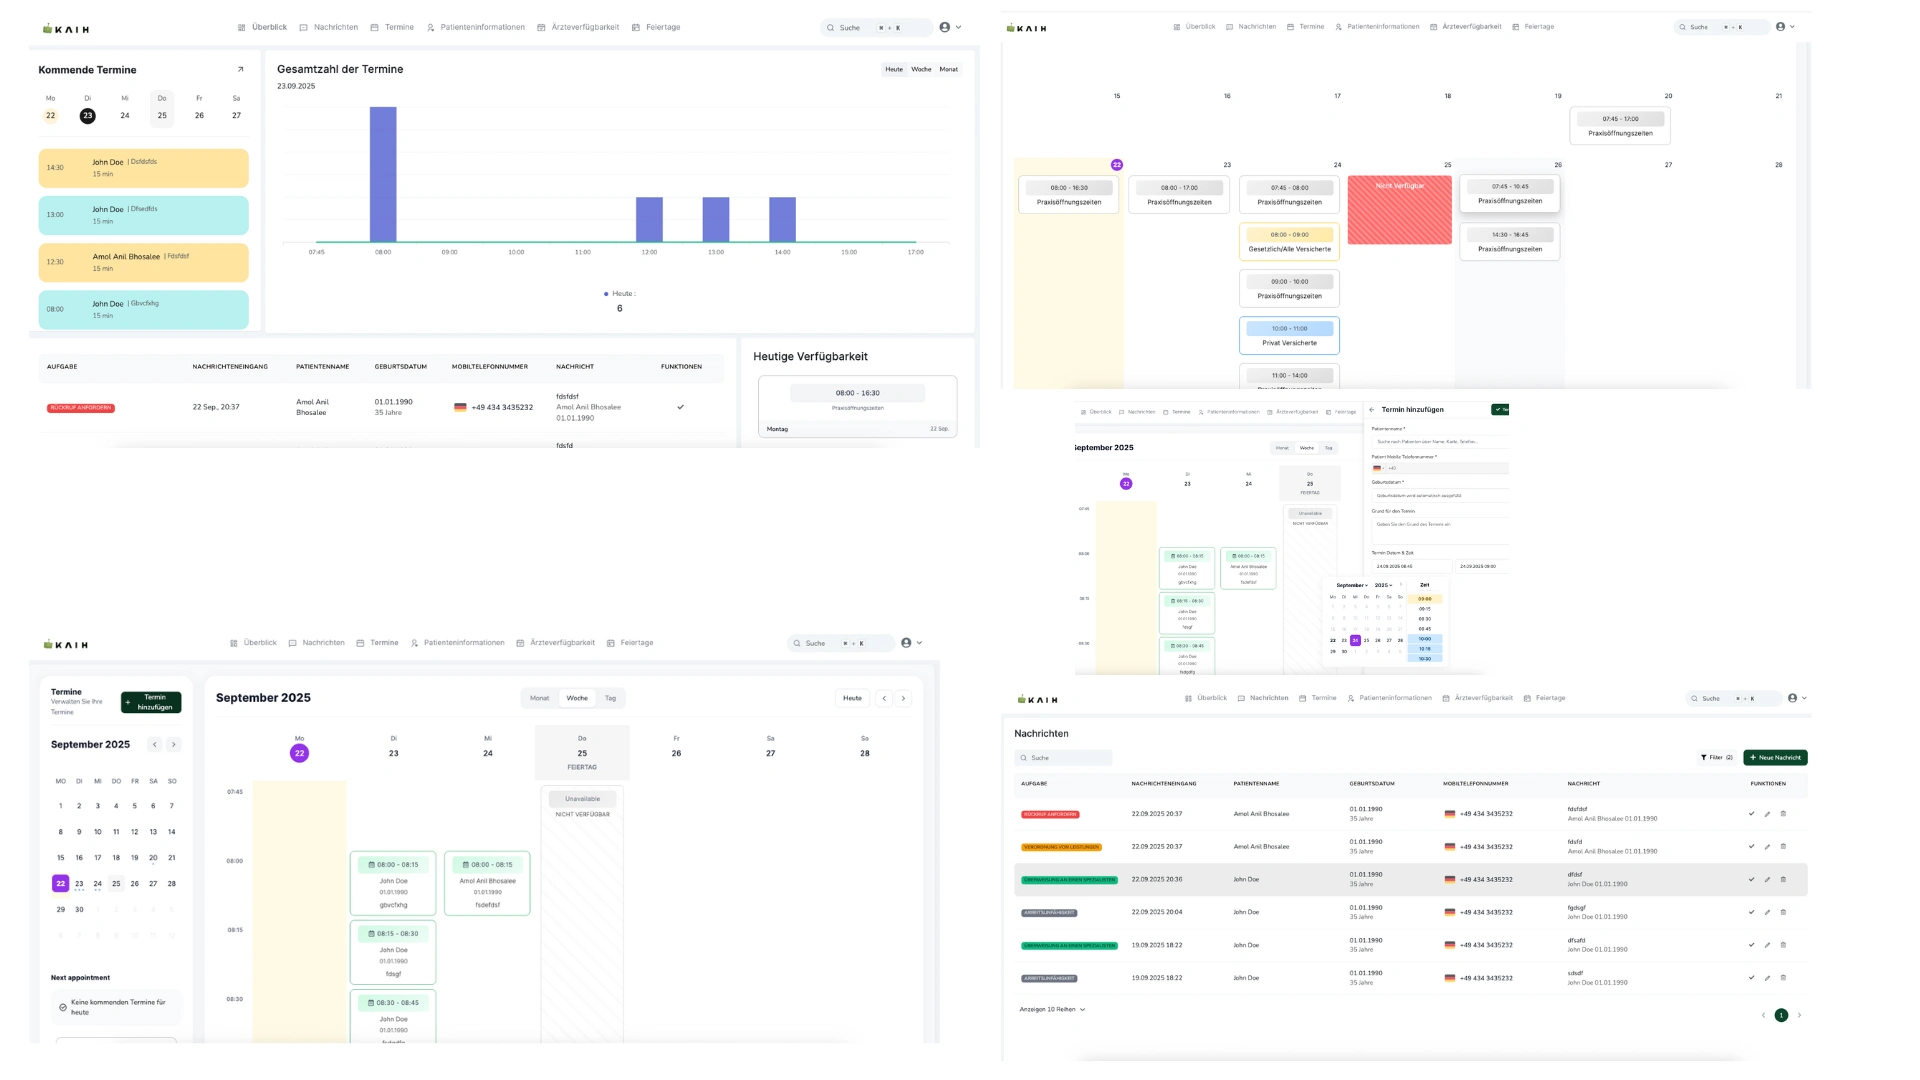
Built a GDPR-compliant appointment scheduling SaaS for a German healthcare practice.
Timeline
Feb 28, 2025 - Oct 31, 2025


