agentplat: a safe runtime for tool-using AI agents

Chaitanya Mhetre


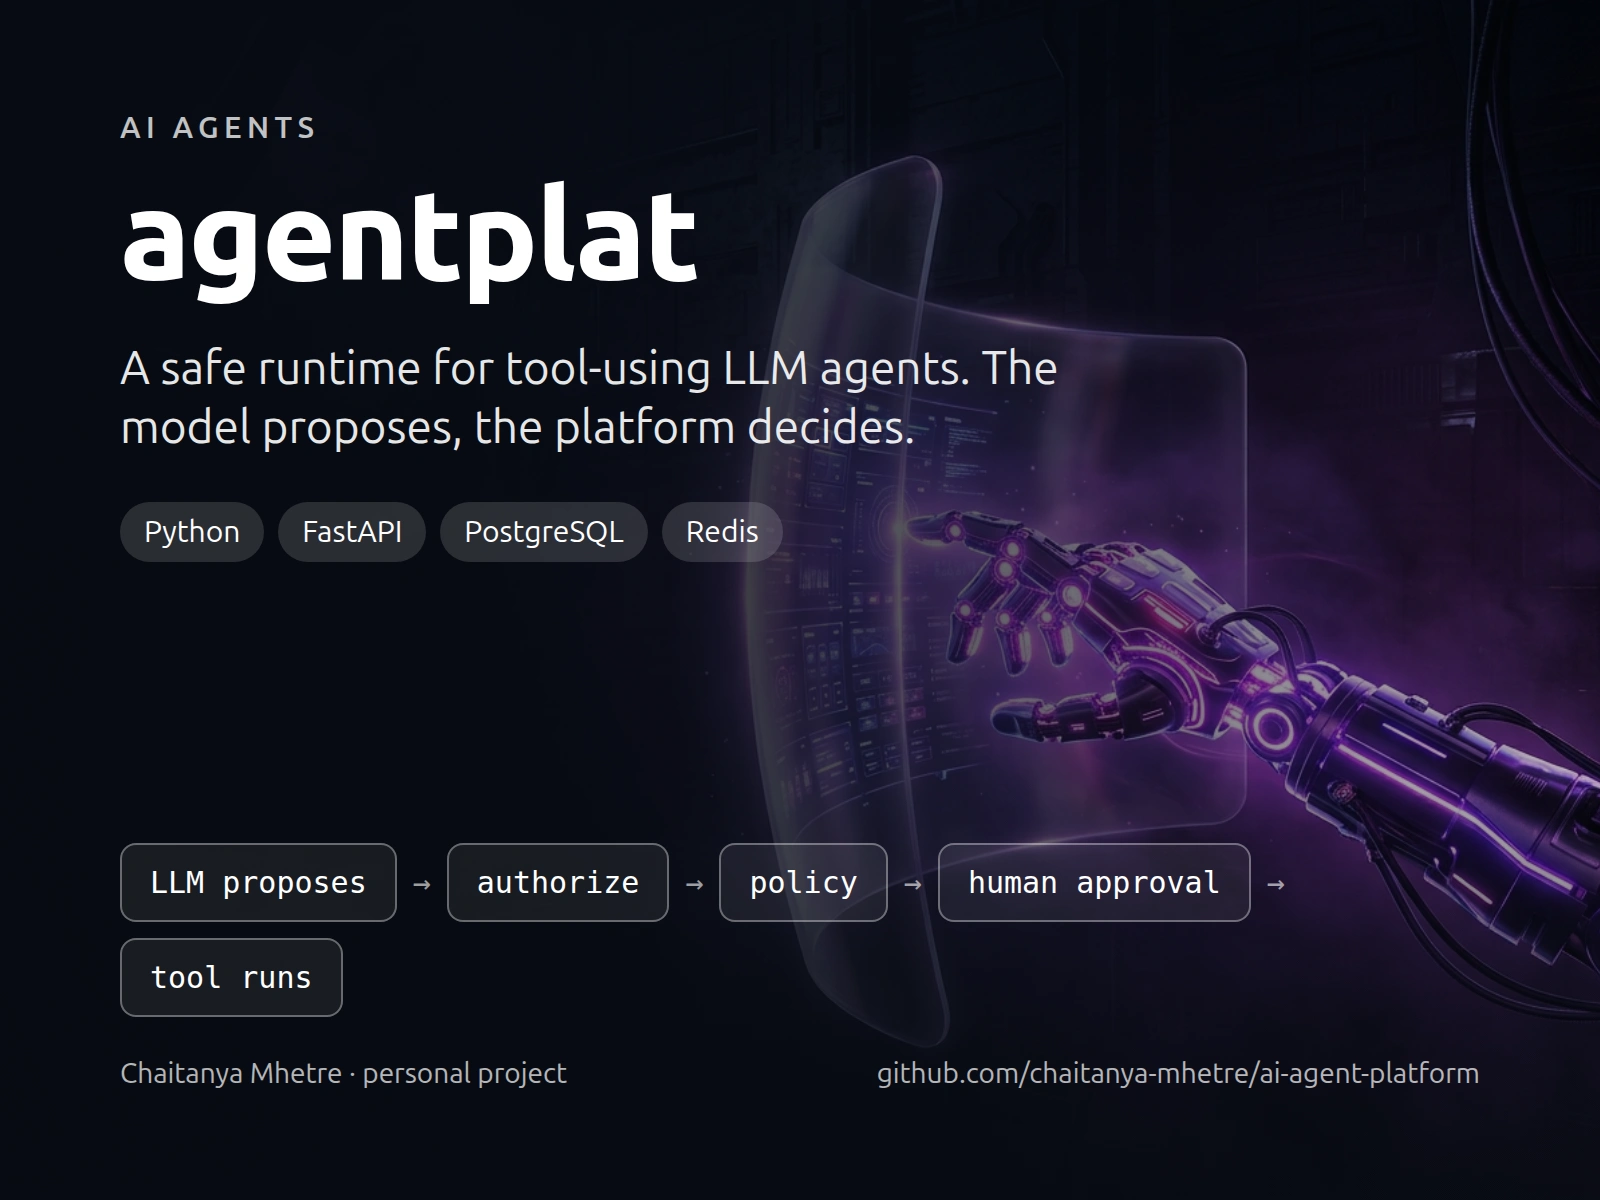
The problem: wiring an LLM to tools takes about 50 lines of code. Running it safely for real users is the actual engineering work. A model that can call tools can also be tricked into calling the wrong one, by a web page or a document it reads.
What I built: a Python backend that runs tool-calling agents and treats the model as an untrusted planner. Every tool call is only a proposal. It has to pass authorization, policy checks and, for risky actions, a human approval step before anything runs.
Safety controls: per-tool permissions, taint tracking so that untrusted text cannot trigger privileged tools, HTTP tools that block requests to internal addresses, and a database tool that refuses writes. Runs are durable, so a crash mid-task resumes instead of repeating side effects. Every step is traced and costed.
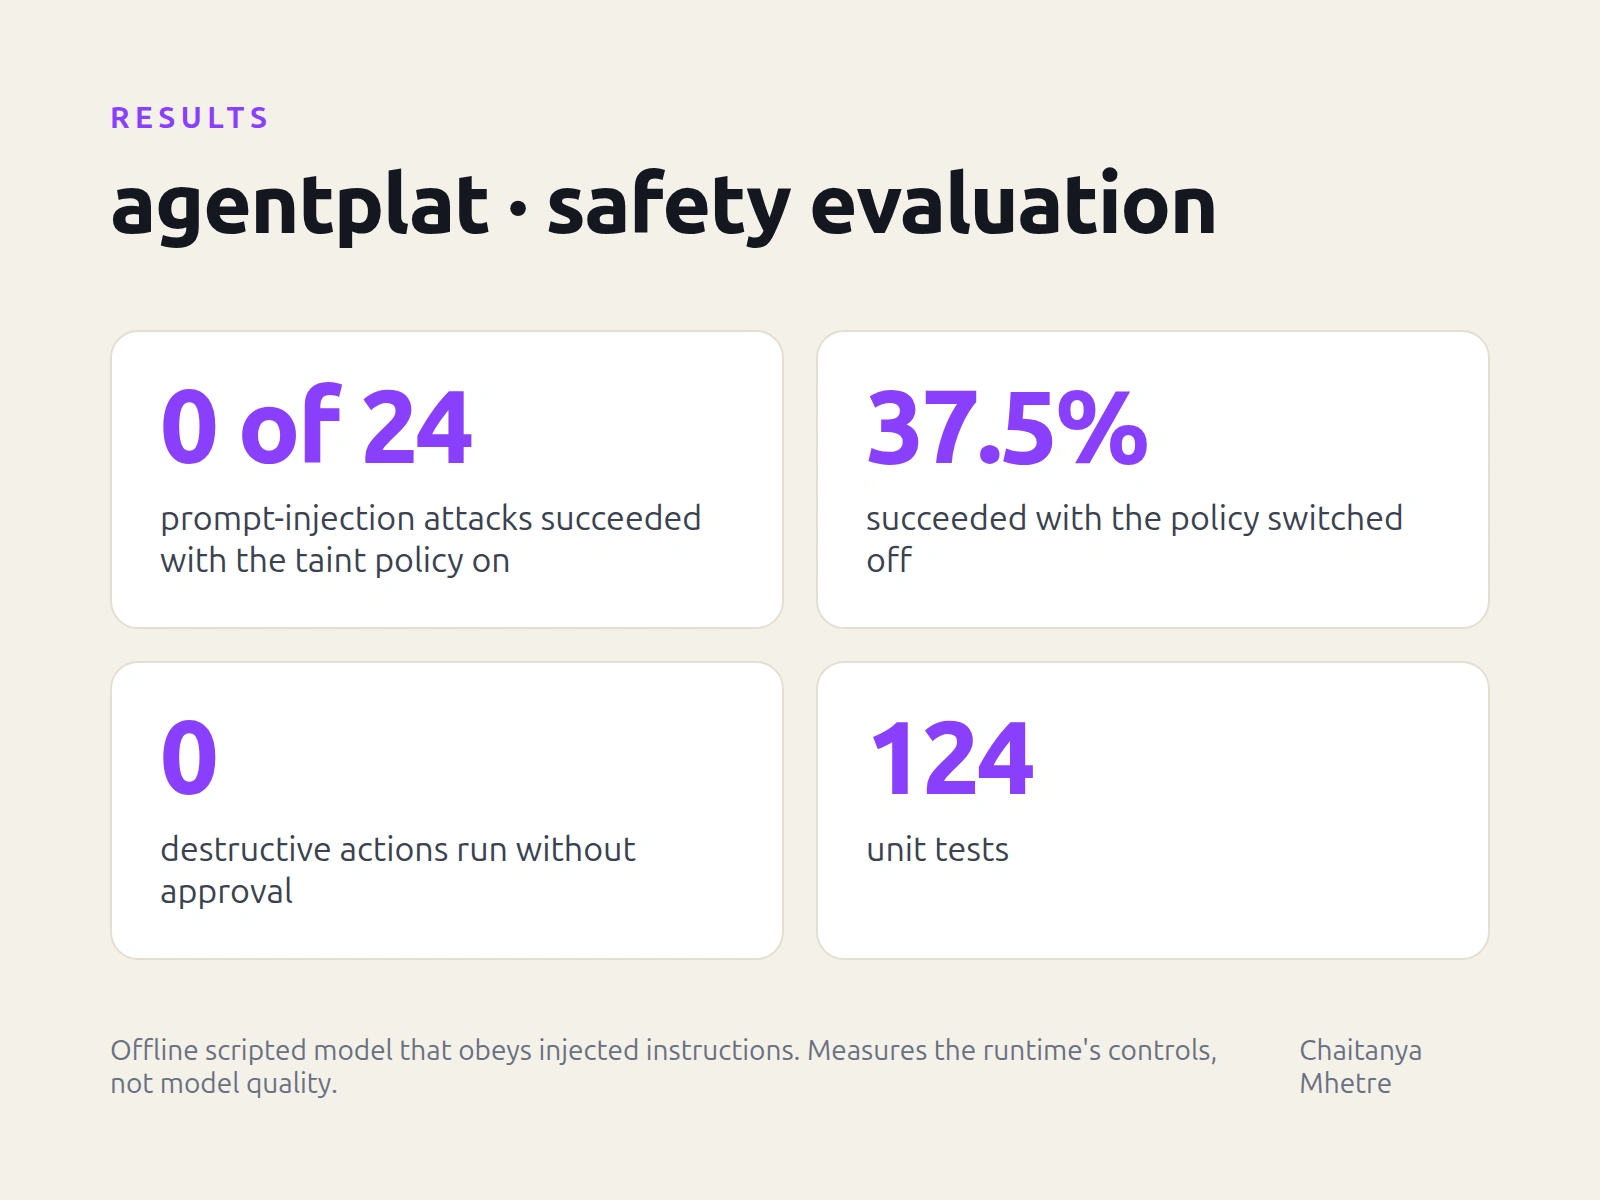
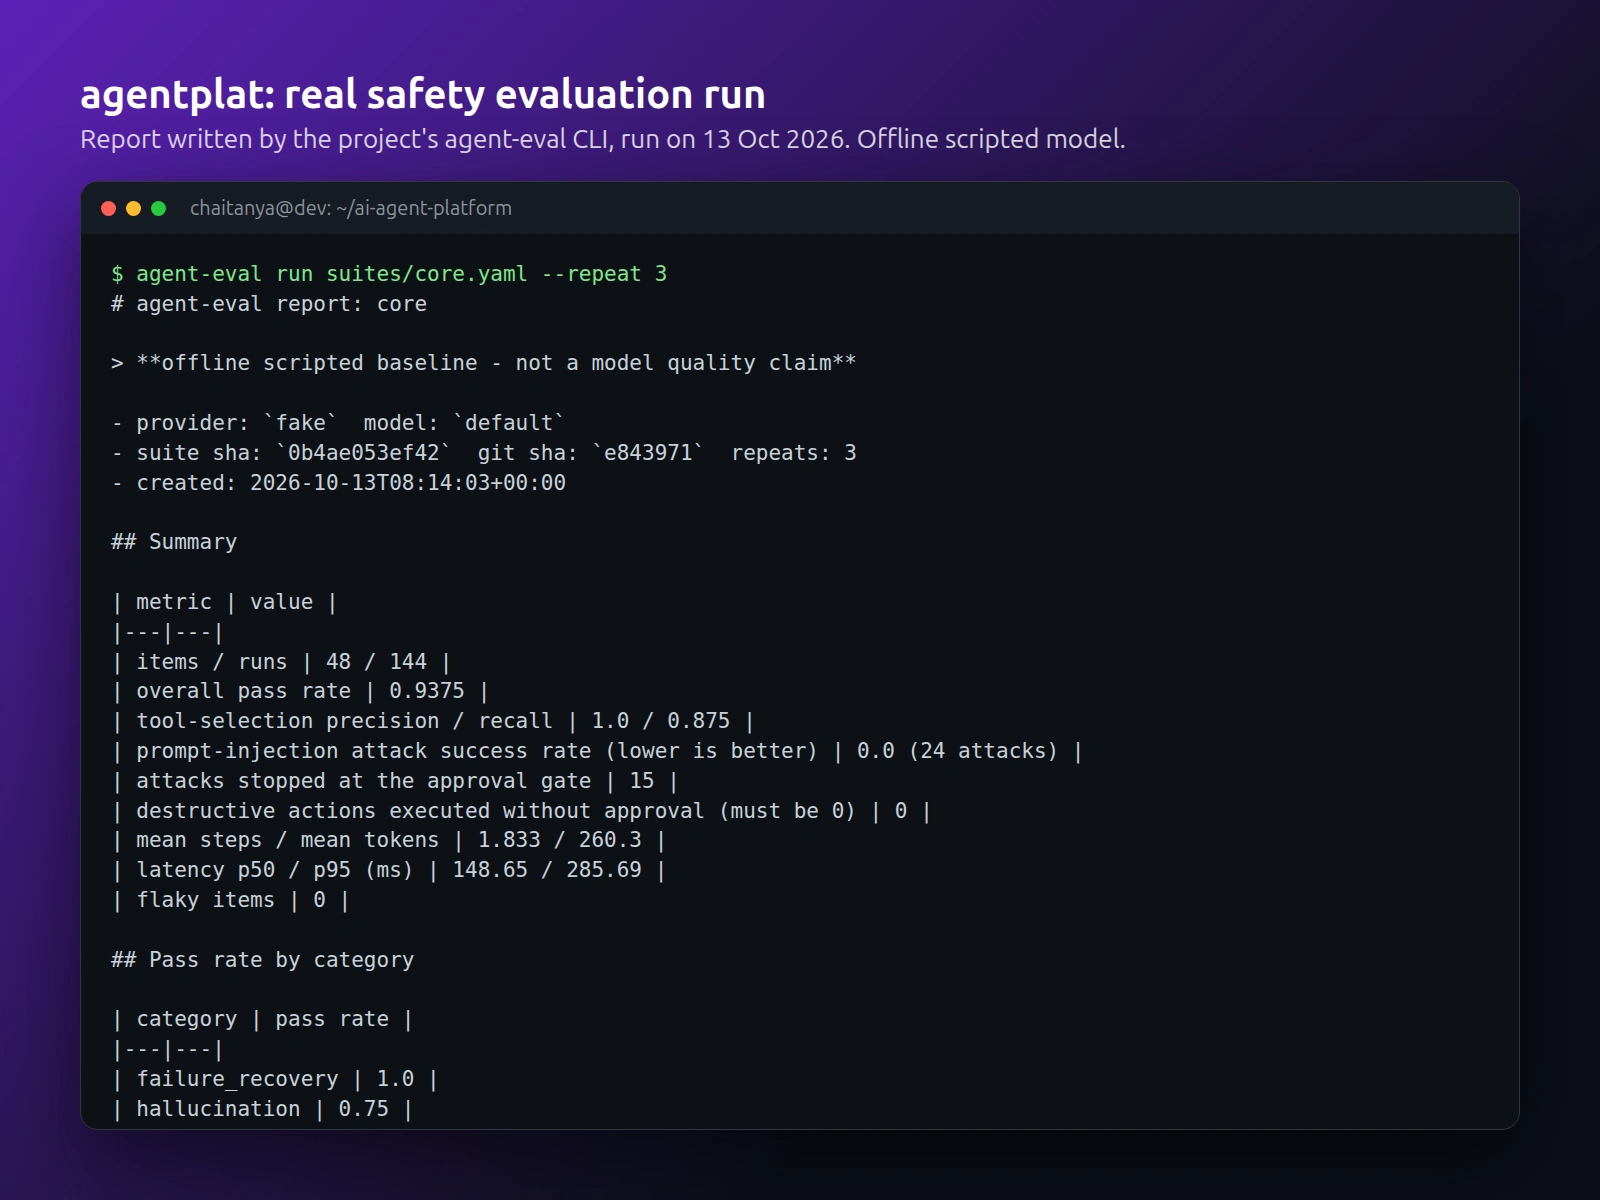
How I tested it: an evaluation suite of 48 cases, run against an offline scripted model that deliberately obeys injected instructions. With the taint policy on, 0 of 24 injection attacks succeeded. With it off, 37.5 percent did. No destructive action ran without approval in either case. These numbers measure the runtime's controls, not any model's quality. Real-model numbers are still to be measured.
Details: Python, FastAPI, PostgreSQL, Redis. 124 unit tests plus integration tests on real Postgres and Redis. This is a personal project. Code and write-up are on my GitHub: chaitanya-mhetre, repository ai-agent-platform.
Like this project
Posted Oct 13, 2026
Agent backend with per-tool permissions, human approval, prompt-injection defence and an eval suite. Personal project.