Regulatory Compliance in Corporate Content

Fabio Smiraglia


Independent editorial sample · White paper · Series B, 06
A strategic guide to strengthening governance and reputation. Written for legal teams, compliance officers and internal auditors.
Thesis. Compliance in corporate communication is not a bureaucratic constraint but a pillar of governance. It reduces legal risk, builds credibility and keeps messaging consistent across jurisdictions.
Covers. The GDPR, DSA and AI Act framework with its application calendar; the risks of non-compliance across five dimensions; a three-role system; a three-tier control workflow; RegTech and explainable AI; ten operational recommendations.
Sources cited. European Commission, Eurostat, Deloitte, PwC, OECD, CONSOB, Banca d'Italia.
Method. Source-anchored research, architecture before writing, a model-agnostic AI-assisted workflow with human review and claim verification.
Not client-commissioned work. Figures quoted in the text are attributed third-party findings, not results of my work. The image below shows the opening, translated from the Italian original. Full Italian text available on request.
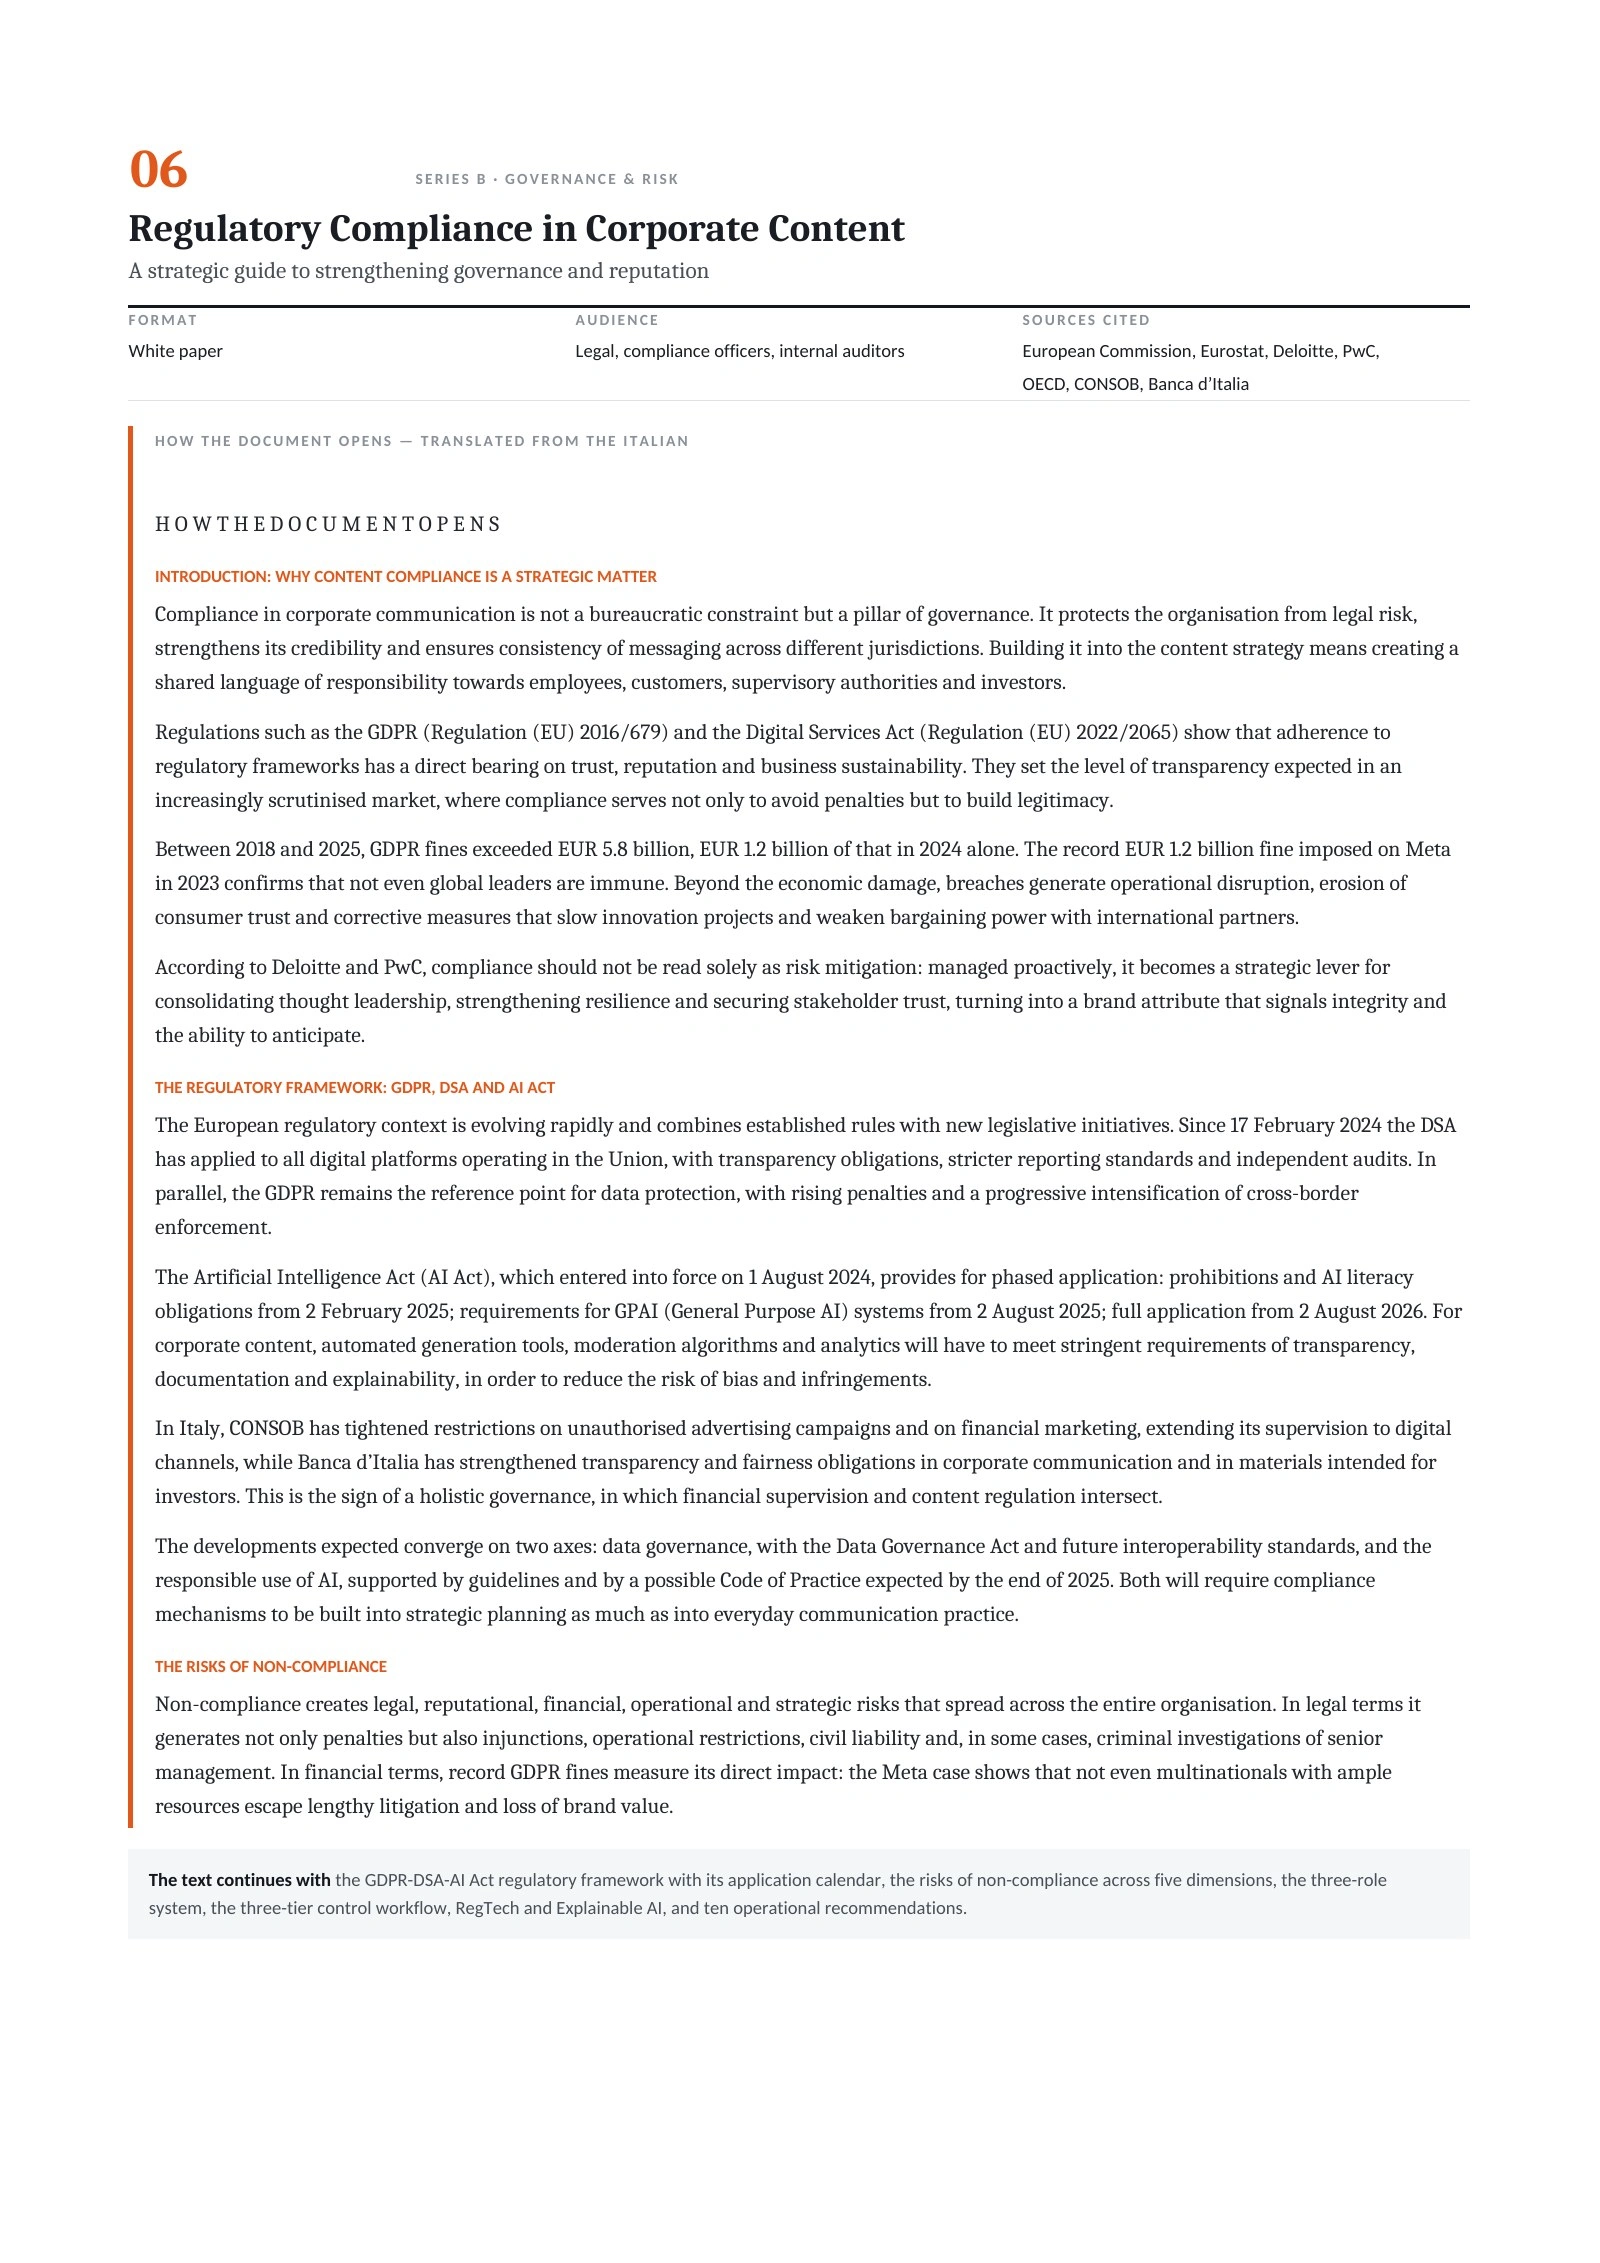
How the document opens, translated from the Italian original.
Like this project
Posted Oct 19, 2026
Independent white paper sample for legal and compliance teams: GDPR, DSA and AI Act as governance levers for corporate content.