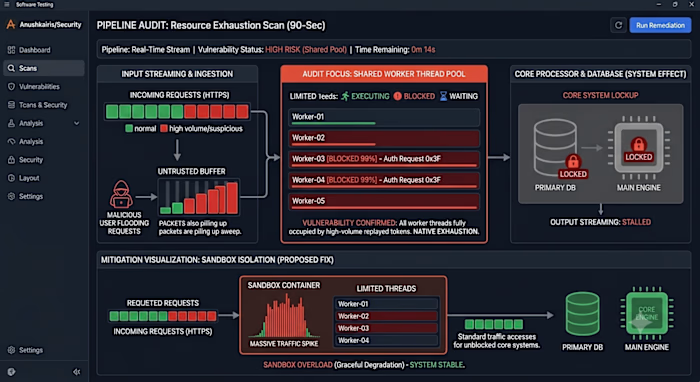
Parsing Hexadecimal Payload Injections & Session Hijacking

Anushkairis .


Analyzing Advanced Exfiltration: Parsing Hexadecimal Payload Injections and Session Hijacking inside Encrypted Streams
Overview
A technical guide highlighting why TLS 1.3 transport security alone is insufficient, detailing how attackers hide malicious shellcode injections and stolen sessions inside encrypted streams, and offering practical mitigation strategies in code.
Key Skills
Systems Architecture & Security Operations
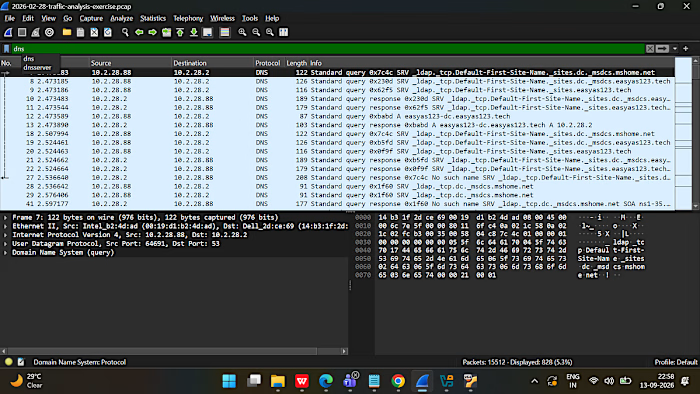
Packet Payload Analysis & Shannon Entropy Calculation
Shellcode & NOP Sled Detection
Session Hijacking Defense & Token Binding
Python (Flask / Cryptographic Validation)
Outcome
Teaches developers and security engineers how to inspect data within encrypted channels by implementing Shannon entropy checks in Python to block raw hex/shellcode injections and using dynamic environment binding to prevent stolen JWT session replays.
Link
Like this project
Posted Sep 29, 2026
A guide on decrypting attacks in TLS 1.3 encrypted channels and mitigating threats.
Likes
1
Views
0