Wireshark Threat Hunting: Identifying Network Attacks

Anushkairis .

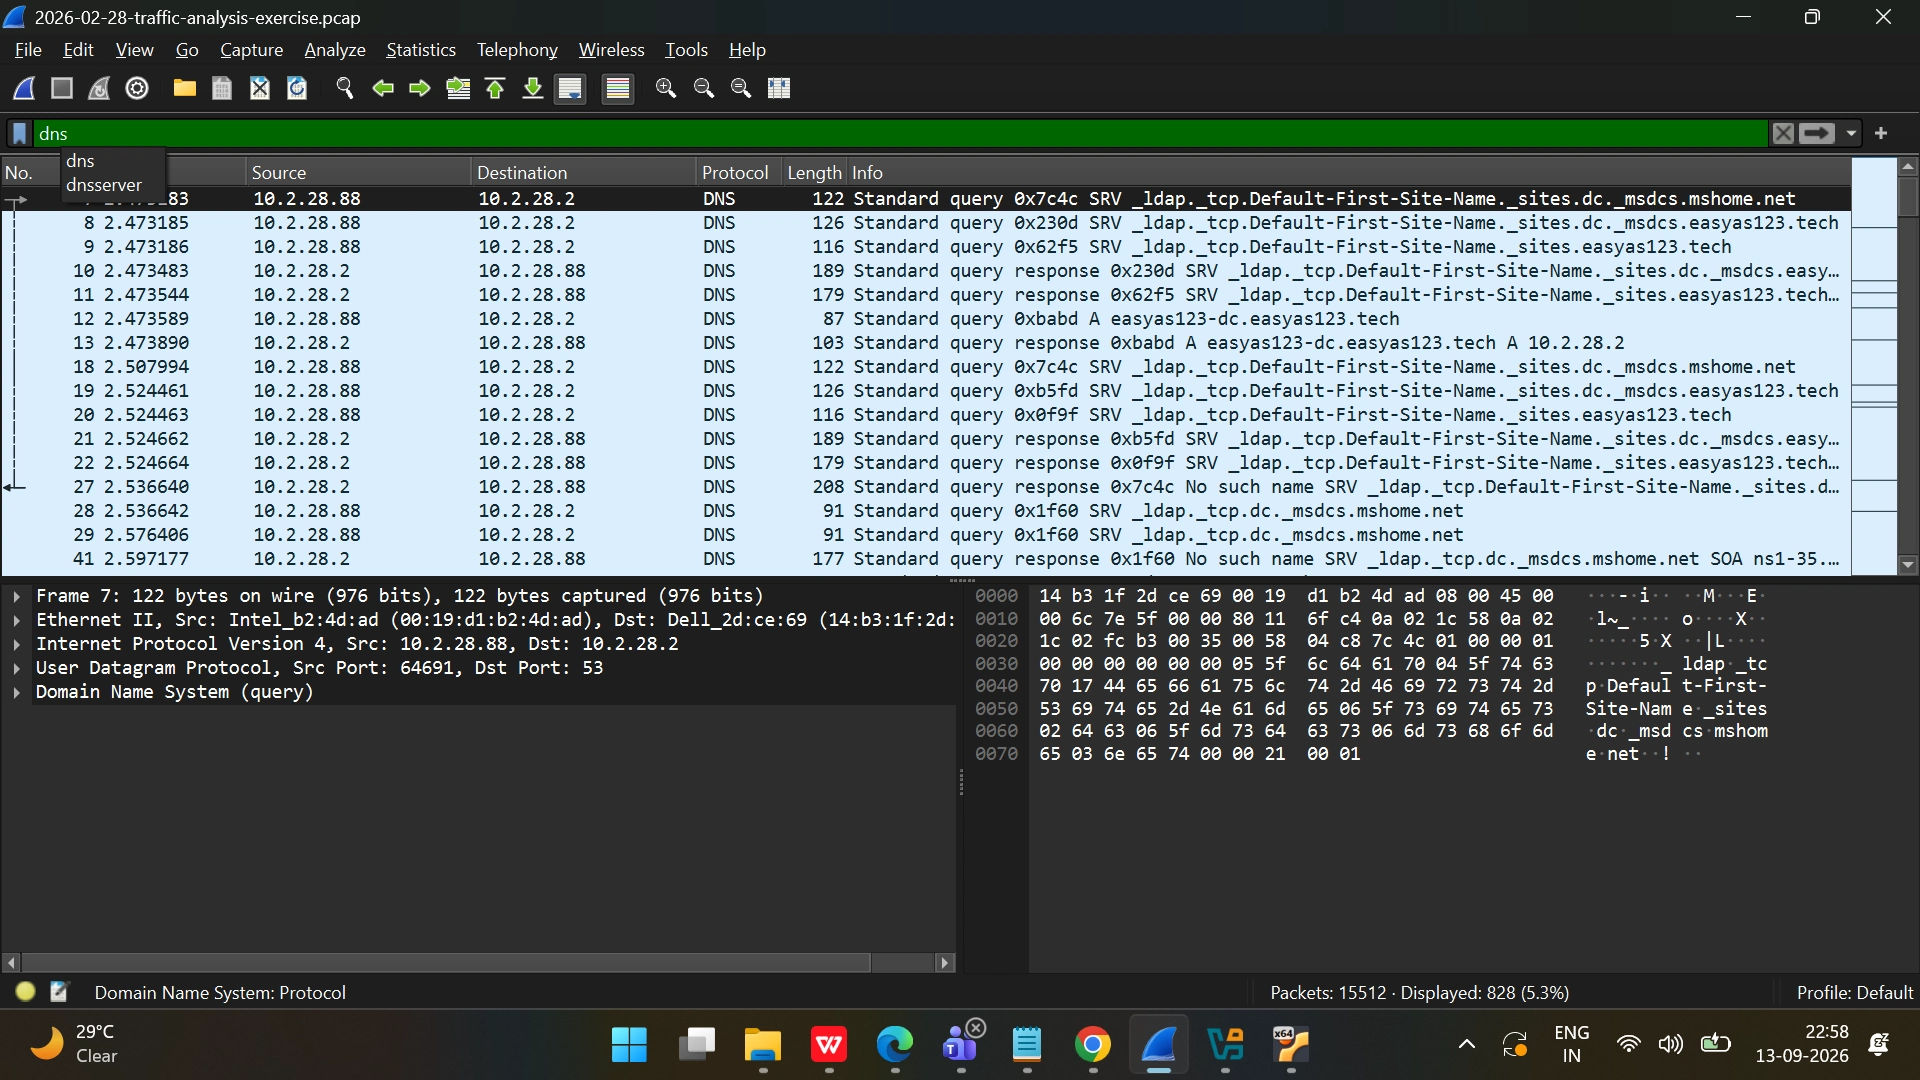
Wireshark Threat Hunting: Spotting Brute-Force Attacks and DNS Tunneling in PCAP Data
Overview
A hands-on technical guide detailing how security analysts use Wireshark PCAP analysis to detect, filter, and verify active SSH brute-force attacks and covert DNS tunneling exfiltration.
Key Skills
Network Packet Analysis (Wireshark)
Threat Hunting & Incident Response
Display Filtering & Pattern Recognition
SIEM & EDR Log Correlation
Network Security
Outcome
Teaches analysts how to isolate suspicious network traffic, identify brute-force login patterns via TCP flag analysis, spot high-entropy DNS tunneling queries used for data exfiltration, and trace compromises back to patient zero endpoints.
Link
Like this project
Posted Sep 29, 2026
Guide on using Wireshark to detect brute-force attacks and DNS tunneling.
Likes
1
Views
1