Nikhil Yadav
Flutter + Firebase developer for real-time & location apps
New to Contra
Nikhil is ready for their next project!
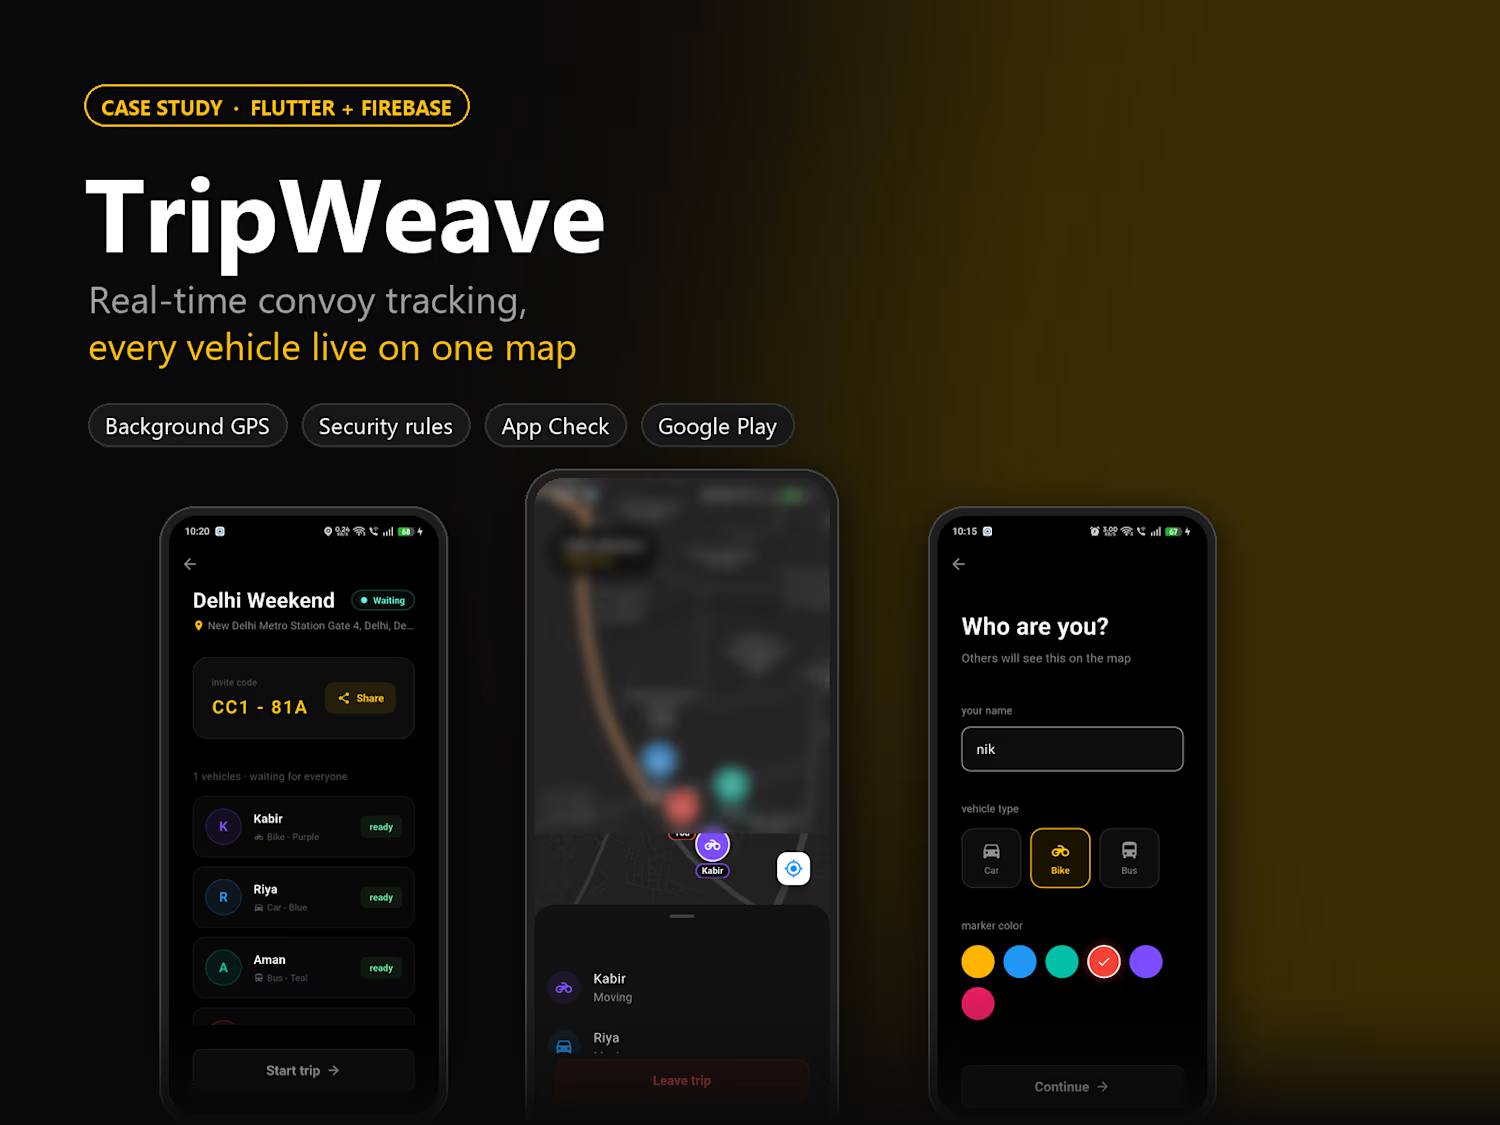

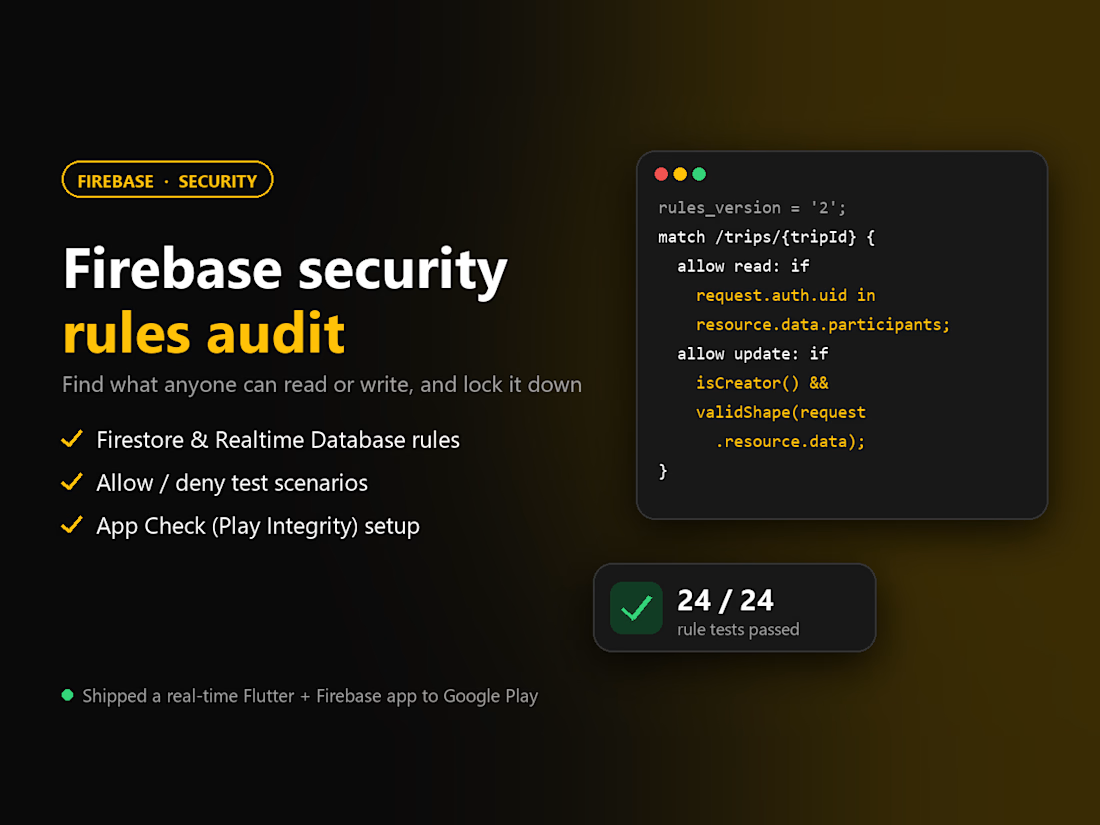
Firebase security rules for TripWeave (my own app). I wrote server-side rules for Cloud Firestore and the Realtime Database that check every write: field names, types, ranges and ownership. Only members can read a trip, joining can only add yourself, only the creator can start...


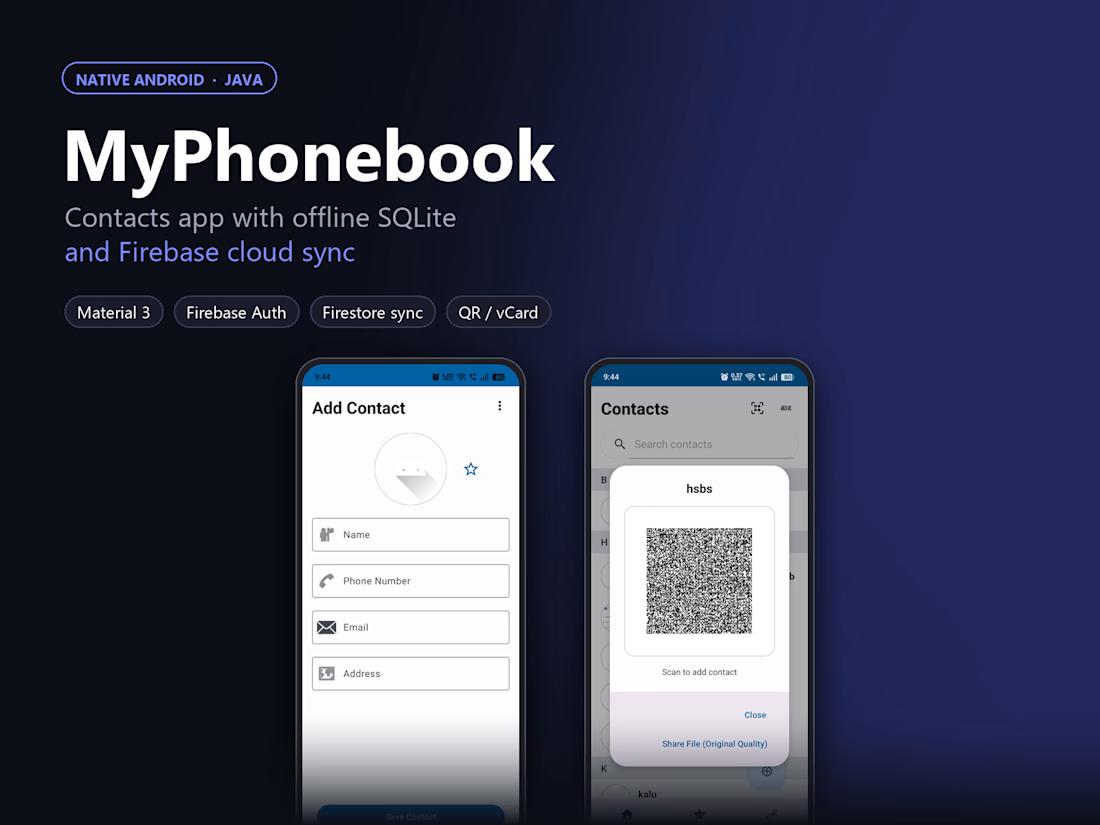
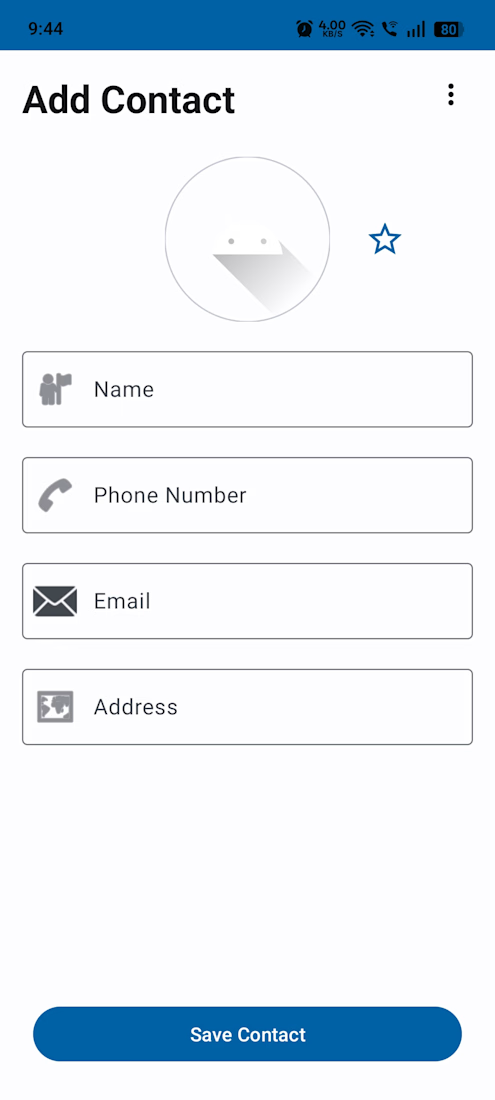
MyPhonebook: a native Android contacts app I built in Java with Material Design 3. Contacts are stored offline in SQLite and sync to Firebase Firestore after Google or email sign-in, with photos in Firebase Storage. It covers full CRUD, favourites, live search, alphabetical...


Live Convoy Kit: a Flutter + Firebase starter kit I packaged and sell on Gumroad. Join a group by code, see every vehicle on a live map, keep tracking in the background, and lock it down with membership-gated security rules and a Cloud Function. It ships with 13 end-to-end tests...

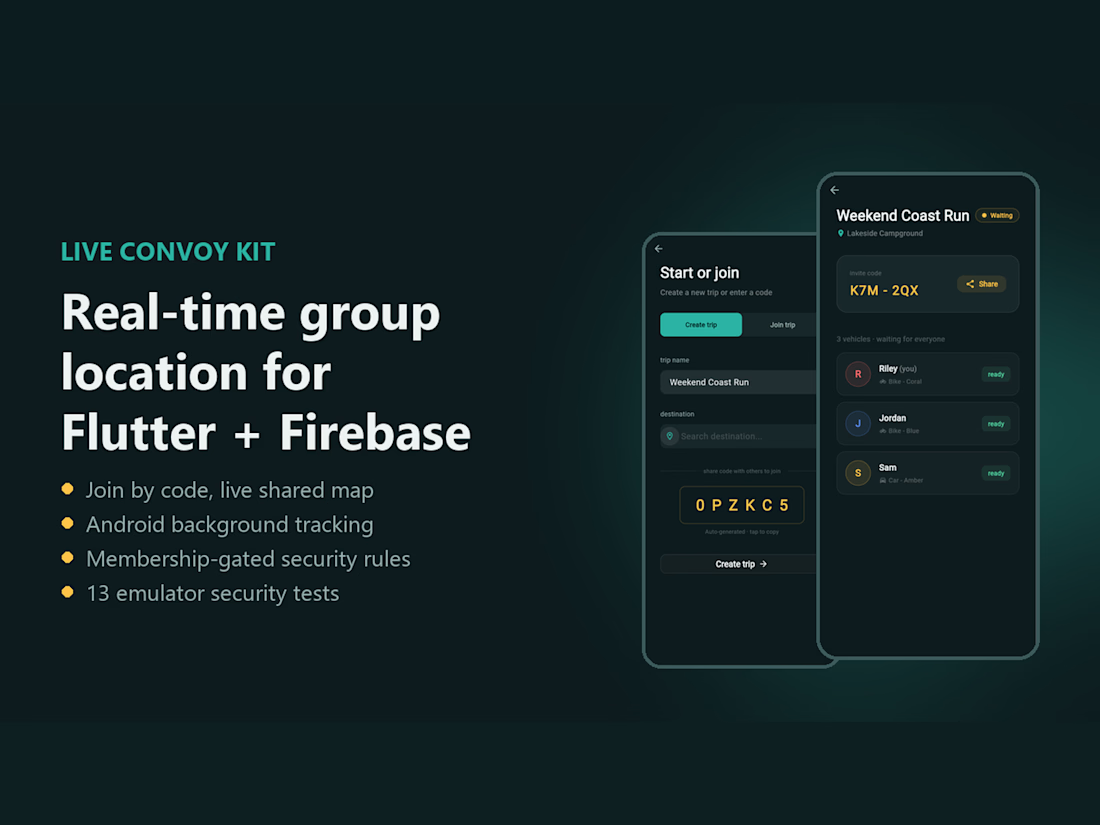
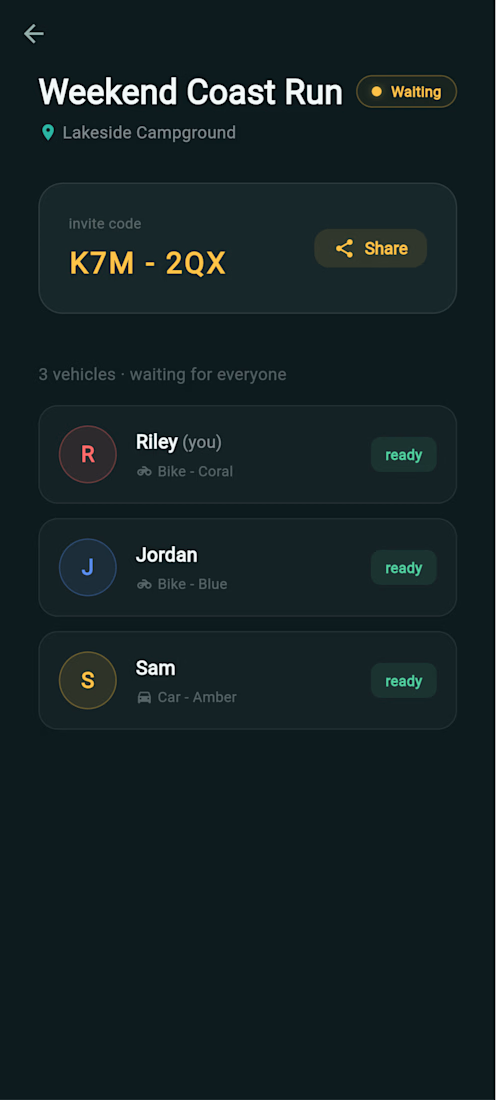
TripWeave: a real-time convoy tracking app I designed and built on my own in Flutter + Firebase. Friends driving separately join a trip with a 6-character code and see every vehicle live on one map, with the route to a shared destination. Background GPS keeps working with the...