Freelance Security EngineersFreelance Security Engineers
AI Automation Engineer | Full-Stack Apps & Integrations
$100k+
Earned
66x
Hired
4.9
Rating
147
Followers
AI Automation Engineer | Full-Stack Apps & Integrations
Ship your SaaS MVP in weeks - web, mobile, payments.
$25k+
Earned
14x
Hired
4.9
Rating
103
Followers
Ship your SaaS MVP in weeks - web, mobile, payments.
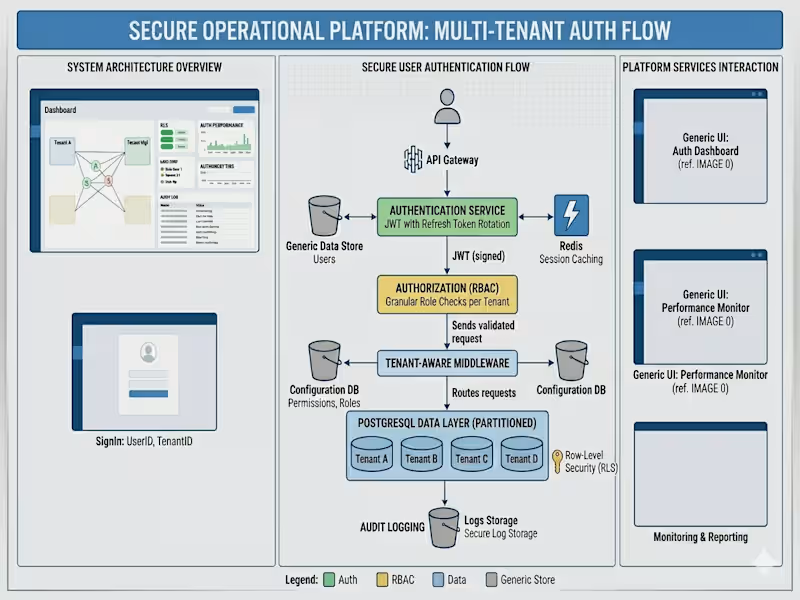
Helping founders turn Replit MVPs into secure, scalable SaaS
13x
Hired
5.0
Rating
46
Followers
Helping founders turn Replit MVPs into secure, scalable SaaS
Cyber expert specialising in Azure Security Services.
$10k+
Earned
4x
Hired
5.0
Rating
22
Followers
Cyber expert specialising in Azure Security Services.
UI/UX Designer & Developer
5.0
Rating
16
Followers
UI/UX Designer & Developer
Cyber Security Analyst
Cover image for Performed a manual, black-box security
Performed a manual, black-box security assessment of a locally-hosted large language model served through LM Studio, using Burp Suite as the primary testing tool. The engagement began with no prior knowledge beyond a single IP address, mirroring how an external attacker would approach an exposed AI server discovered on a network. Worked through a full discovery-first methodology: confirming the target was live, enumerating the server's exposed endpoints by probing and reading response codes, extracting the loaded model name directly from the API, and proving the expected request format through the server's own error responses rather than assuming it. This reconnaissance phase converted an unknown target into a complete map of its attack surface. With the attack surface established, executed a series of manual techniques through Burp's Repeater and Intruder tools, including prompt injection, system prompt extraction, role and system-message injection, parameter manipulation, error-message disclosure, and authentication testing. Demonstrated additional Burp capabilities relevant to AI systems, including response comparison to prove behavioral changes under attack, randomness testing of server-generated identifiers, and live request tampering to illustrate a man-in-the-middle scenario against AI traffic. Organized all findings into a structured vulnerability map aligned to OWASP LLM risk categories, recording each technique's result, severity, and supporting evidence. Delivered the work as a complete, reproducible, beginner-accessible walkthrough covering environment setup, discovery, exploitation, and reporting.
0
125
AI Agent Security Auditor | Fast, evidence-based reviews
New to Contra
AI Agent Security Auditor | Fast, evidence-based reviews