
Lead Full Stack Developer | AI/ML Engineer | Data Scientist
New to Contra
Lead Full Stack Developer | AI/ML Engineer | Data Scientist


Senior Lead Graphic Designer | UI/UX & Product Engineer
New to Contra
Senior Lead Graphic Designer | UI/UX & Product Engineer


.NET Developer building scalable APIs, SaaS & business apps
New to Contra
.NET Developer building scalable APIs, SaaS & business apps
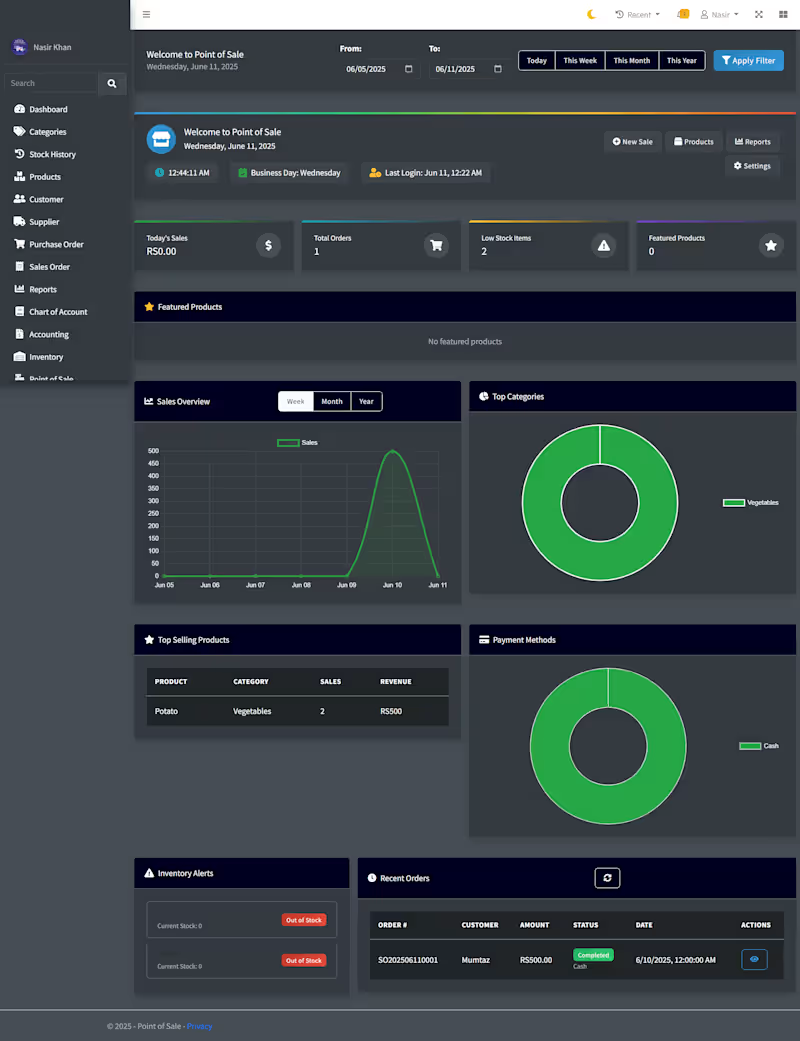
Inventory Management System to help businesses manage stock and operations with ease. The system includes modules for categories, products, stock history, customers, and suppliers, along with purchase and sales orders to keep track of transactions. It also features detailed reports and analytics, plus a chart of accounts and accounting tools to manage finances in one place. A smart assistant is included to answer queries, generate quick reports, and provide useful suggestions. This system brings everything together to save time, improve accuracy, and make day-to-day management simpler.
0
128
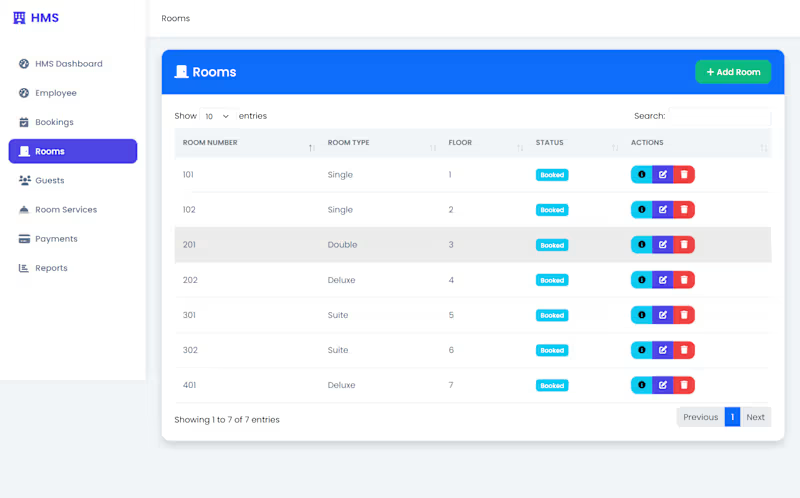
Hotel Management System
A complete and user-friendly Hotel Management System designed to streamline daily hotel operations and improve overall efficiency. The system helps manage rooms, guests, reservations, room services, billing, and other essential hotel operations from a centralized platform.
Key Features:
🏨 Room & Room Type Management
📅 Reservation & Booking Management
👤 Guest Management
🛎️ Room Service Management
💳 Billing & Payment Management
📊 Reports & Dashboard
🔄 Room Availability & Booking Status
⚙️ Easy-to-use Management Interface
The system reduces manual work, keeps hotel operations organized, and provides staff with quick access to important information—making day-to-day hotel management faster, simpler, and more efficient.
0
97
Tracking Management System that helps businesses monitor vehicles in real time and streamline job dispatching. The system provides live GPS tracking, route history, and status updates for every vehicle, giving complete visibility of fleet operations.
Along with tracking, There is dispatch module where dispatchers can create, allocate, and monitor jobs from start to finish. The platform includes alerts and notifications for events such as Arrived, On Route, and completed jobs, ensuring quick response and smooth coordination.
0
121
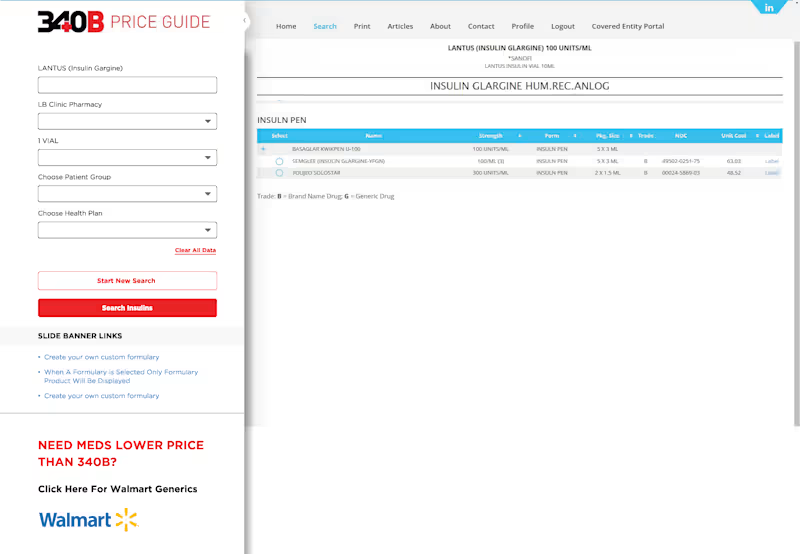
The 340B Price Guide will be a simple and reliable tool that helps hospitals, clinics, and pharmacies keep track of drug prices under the 340B program. It’s designed to make it easier for healthcare teams to see the right prices, compare costs, and stay compliant with program rules without spending hours digging through spreadsheets or confusing data.
0
96

Cybersecurity engineer and software developer building robus
New to Contra
Cybersecurity engineer and software developer building robus
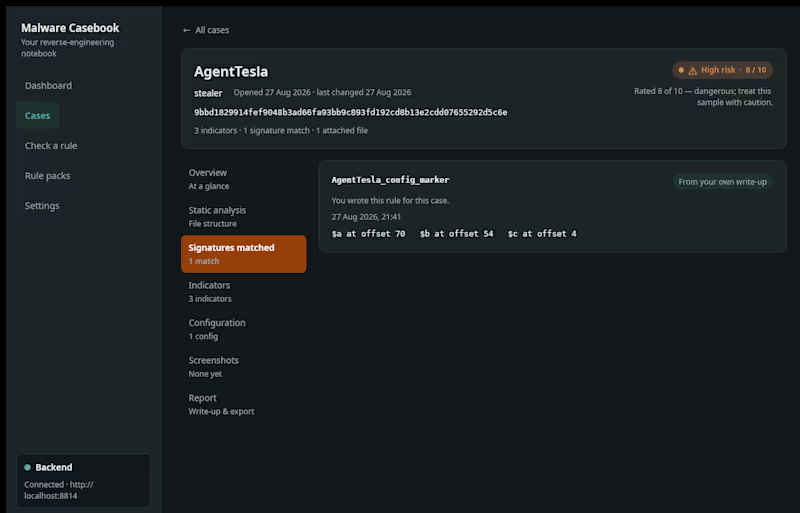
Grim Lens is a local-first malware intelligence and threat-hunting workbench I built for security teams that need to analyze evidence without sending sensitive samples to the cloud.
The platform ingests static artifacts such as PE metadata, strings, YARA matches, decoded configurations, PCAP summaries, and screenshots, then organizes them into investigation cases with risk scoring, enrichment, reporting, and cross-case intelligence.
I designed the system around a strict security boundary: no sample execution, no automatic uploads, and no outbound enrichment unless explicitly requested.
The backend is built in Rust using Axum, Tokio, SQLx, SQLite, YARA-X, and structured analysis modules, while the desktop interface is built with Avalonia/.NET 10 using MVVM and interactive charts.
Key engineering work included:
Local-first malware case management
Static PE analysis and entropy inspection
YARA rule matching and rule-pack management
Threat-intelligence enrichment using services such as VirusTotal, abuse.ch (http://abuse.ch), and AlienVault OTX
Rate limiting and TTL caching for external enrichment
Cross-case indicator correlation
Automated Markdown and PDF report generation
Risk distribution, family, and category dashboards
Rust REST API with structured validation and errors
SQLite-backed local storage and migrations
Cross-platform Avalonia desktop application
CI builds and packaged Windows/Linux releases
The result is a practical analyst workbench that turns scattered malware artifacts into a structured, searchable casebook while keeping control of sensitive data on the analyst’s own workstation.
0
111
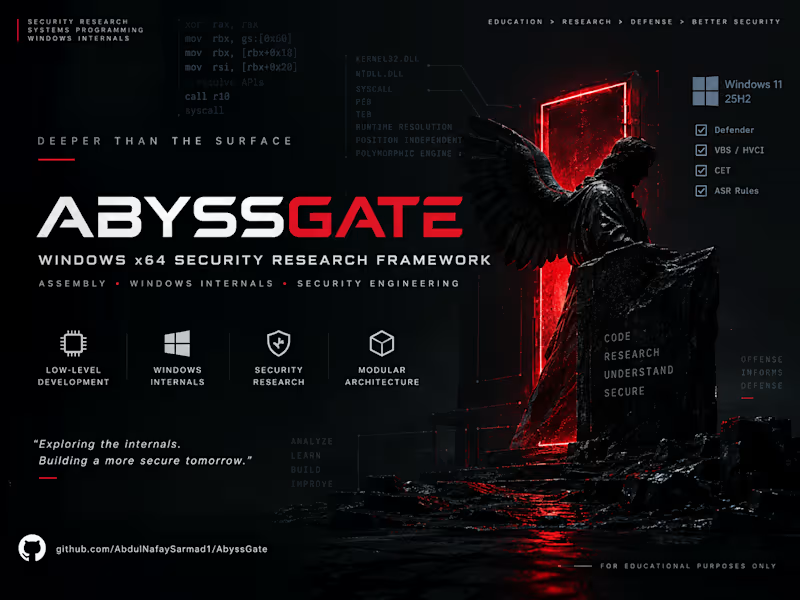
AbyssGate is an educational x64 assembly security research project built to explore low-level Windows internals and defensive security concepts. The project demonstrates position-independent assembly, Windows API resolution, memory management, system-call research, and modular framework design. It showcases my ability to work close to the operating-system layer, understand Windows security architecture, and build security-focused tooling from the ground up
0
100
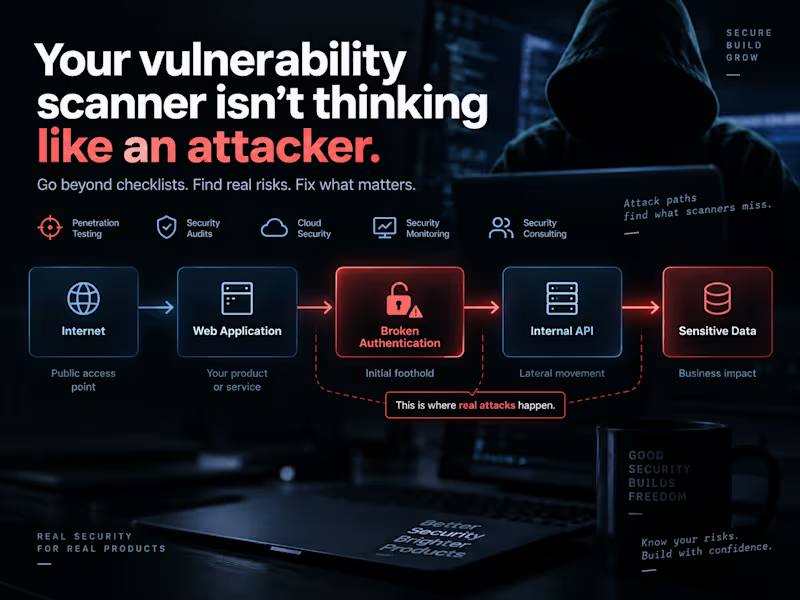
Most companies don't need another 80-page security report.
They need someone to tell them:
What can actually be exploited?
What could it cost us?
And what should we fix first?
That's the difference between checking a cybersecurity box and actually improving your security.
When I assess an application or infrastructure, I'm not interested in filling a report with 50 low-impact findings just to make it look impressive.
I care about attack paths.
→ Can authentication be bypassed?
→ Can one compromised account lead to something bigger?
→ Are APIs exposing data they shouldn't?
→ Can permissions be chained into privilege escalation?
→ Are cloud or infrastructure misconfigurations creating an easy entry point?
→ Would your monitoring actually notice an attacker?
And most importantly:
What should your team fix first?
That's the approach I bring to cybersecurity work — whether it's penetration testing, security audits, SOC/security monitoring, or security consulting.
I'm currently taking on new projects through Contra.
If you're building a SaaS product, web application, API, or growing infrastructure and you're unsure how it would hold up against a real attack, send me a message.
I'll happily take a look at what you're building and tell you where I'd start.
0
64
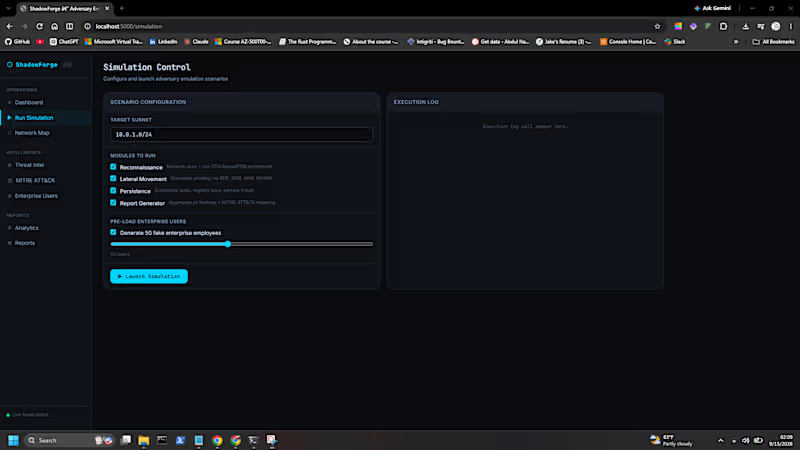
ShadowForge is an adversary-emulation and security-validation platform I built to help security teams model attack scenarios, visualize activity, correlate threat intelligence, and evaluate defensive visibility from a single operations interface.
The platform brings together scenario orchestration, network visualization, threat intelligence, MITRE ATT&CK mapping, enterprise identity simulation, analytics, and reporting into one unified workflow.
I designed the application around modular simulation components so authorized lab and security-validation exercises can be configured, observed, and translated into useful defensive findings rather than scattered logs and manual notes.
Key engineering work included:
Centralized security operations dashboard
Configurable adversary-emulation scenarios
Reconnaissance and environment-discovery simulation
Lateral-movement and persistence scenario modeling
Live execution-event visualization
Network topology and host mapping
MITRE ATT&CK technique mapping
Threat-intelligence and IOC enrichment
Enterprise user simulation for realistic lab scenarios
Security analytics and severity tracking
Automated findings and report generation
Modular architecture designed for controlled security testing
ShadowForge turns an authorized security exercise into something measurable: operators can configure a scenario, observe activity as it happens, correlate findings with threat intelligence and ATT&CK techniques, and produce structured results for defensive analysis.
Built for controlled labs, security validation, and authorized adversary-emulation environments.
0
94

Expert Full Stack Developer
Expert Full Stack Developer


Frontend design with attention to detail
Frontend design with attention to detail


Versatile Software & Web Solutions Pro
Versatile Software & Web Solutions Pro


