The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

Enterprise iOS pipeline on Bitrise — Demo of an enterprise iOS CI path on Bitrise using Fastlane and TestFlight-oriented delivery. Same problem as the GitHub Actions offer, different runner. Useful if a client already lives on Bitrise. https://github.com/lamtalaa/BitriseEnterprisePipelineDemo

The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started

Challenges
View all


Related posts

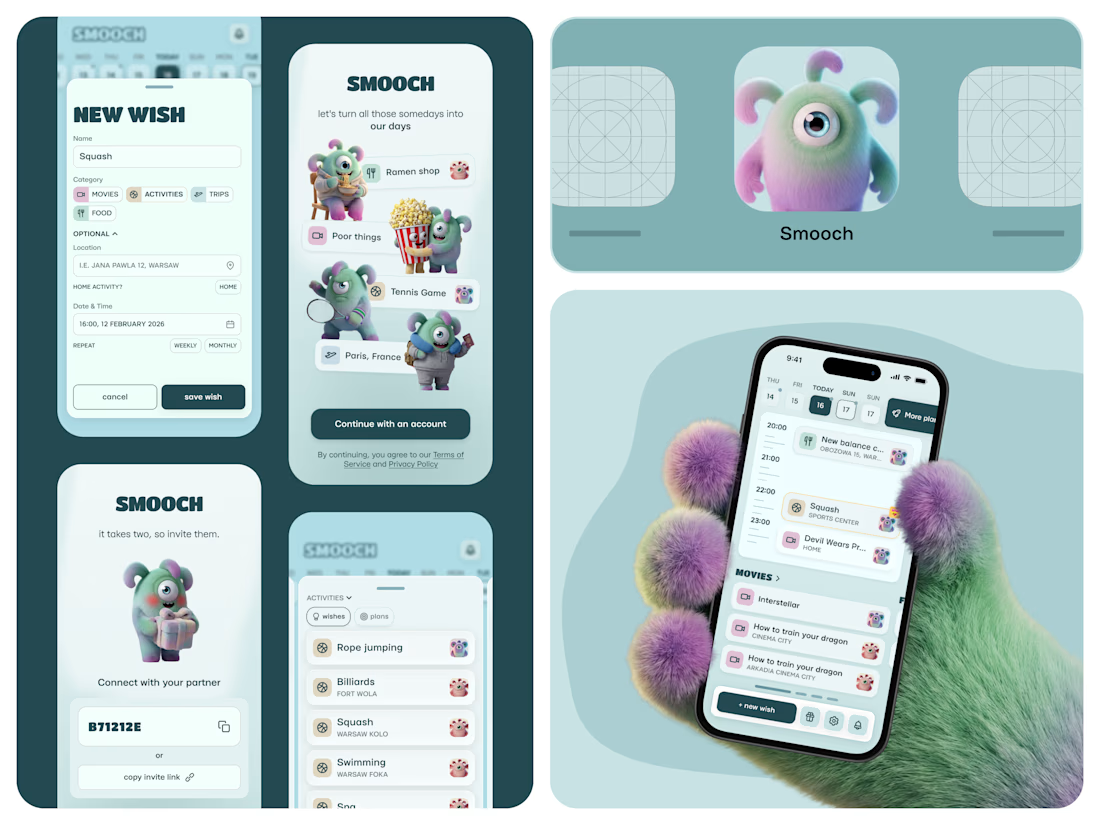
Smooch is live on the App Store 🥹
It started in January. My partner and I were planning trips for March and May, and suddenly realised we’d forgotten a movie we wanted to watch and a new Korean place we wanted to try. Big plans: fine. Small ones: gone.
So I built us a shared space for all those “we should try this someday” ideas. You save them together, drag one onto a day, and it becomes an actual plan.
I made it on my own: product, design, the build with Lovable, the website and the blog - Framer. 60 builds, a few App Store rejections, and one timezone bug that sent us to squash at 2am instead of 2pm xD
And there are no photos inside, just Smooches characters. Because who calls their person by their actual name anyway? (or it's just me there, huh)
The whole story is in the case study 🦄

That furry hand holding the phone is a scroll-stopper. These characters would be so fun animated, even just a little wiggle when a wish turns into a plan. Huge congrats on the launch.

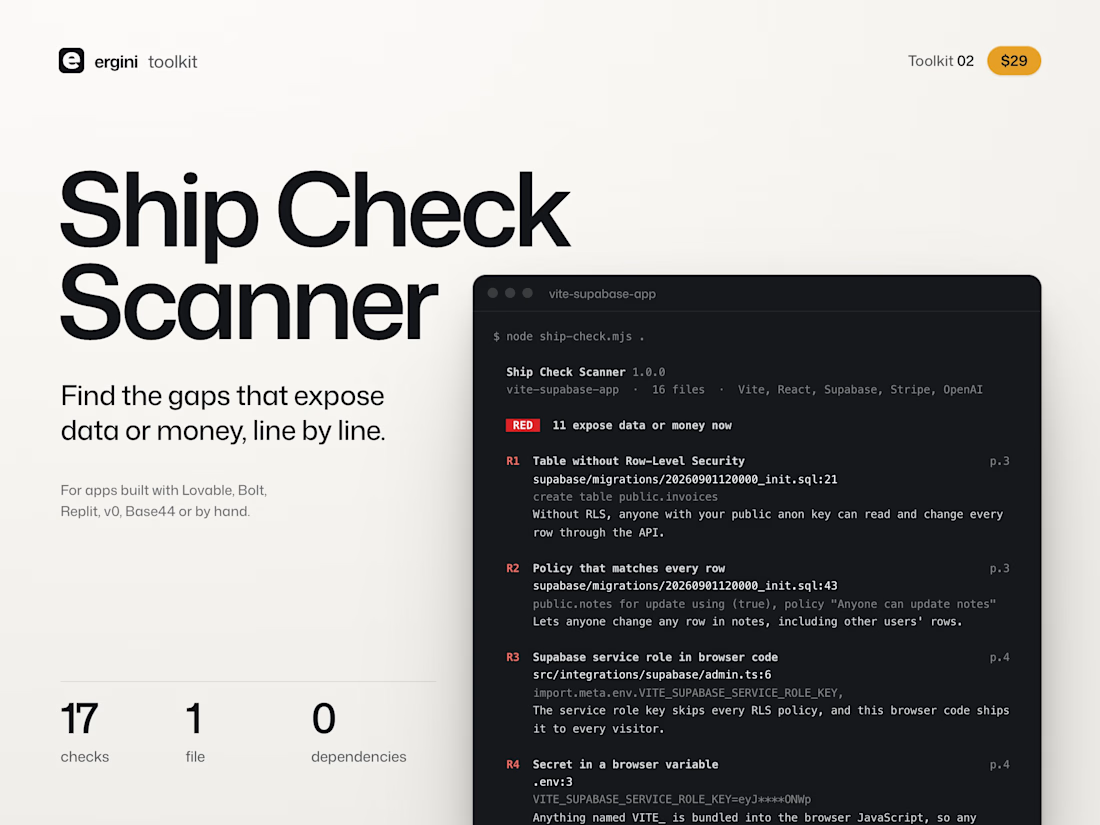
I turned the checks I run on Lovable, Bolt and Replit apps into a small scanner.
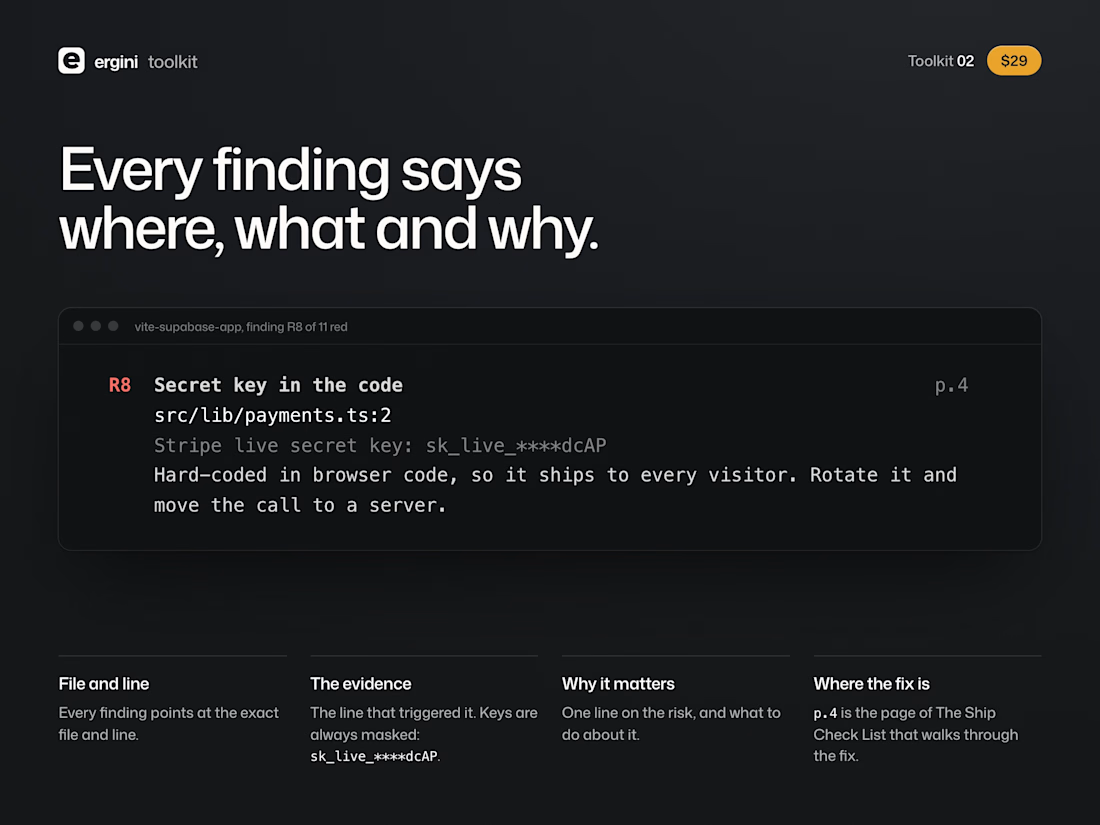
Run one command in your app's folder and it lists the gaps that expose data or money, file by file: keys that end up in the browser, the Supabase service role in client code, tables without row-level security, Stripe webhooks nobody verifies, AI routes anyone can call.
It runs locally, has no dependencies, never uploads your code, and masks every key it finds. Add --ci and it fails the build when anything is red.
It is heuristics, not a guarantee. But it catches the things I look for in the first hour of an audit.
The checklist it is built on is free: https://contra.com/products/cTLDQhiJ-the-ship-check-list-what-to-check-before-real-users-pay
What is the first thing you check before a launch?



Landing page for an AI-native terminal platform