The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started
Back to feedPost

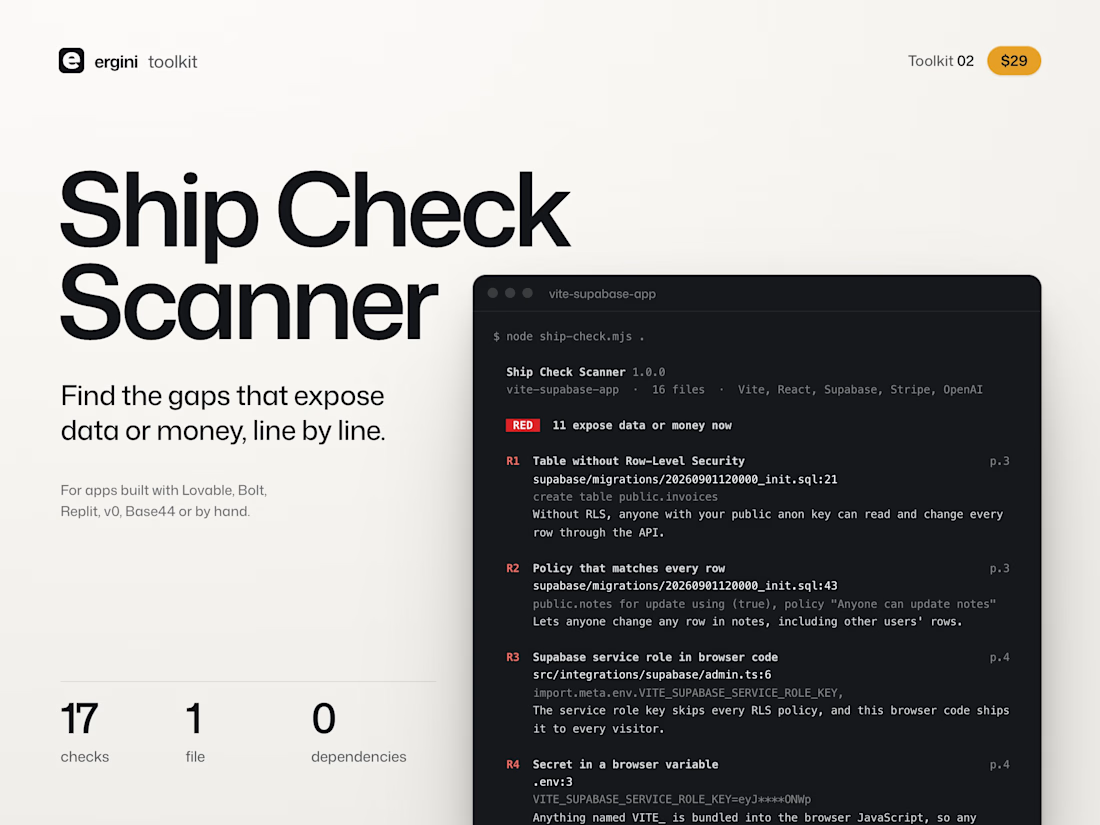
I turned the checks I run on Lovable, Bolt and Replit apps into a small scanner.
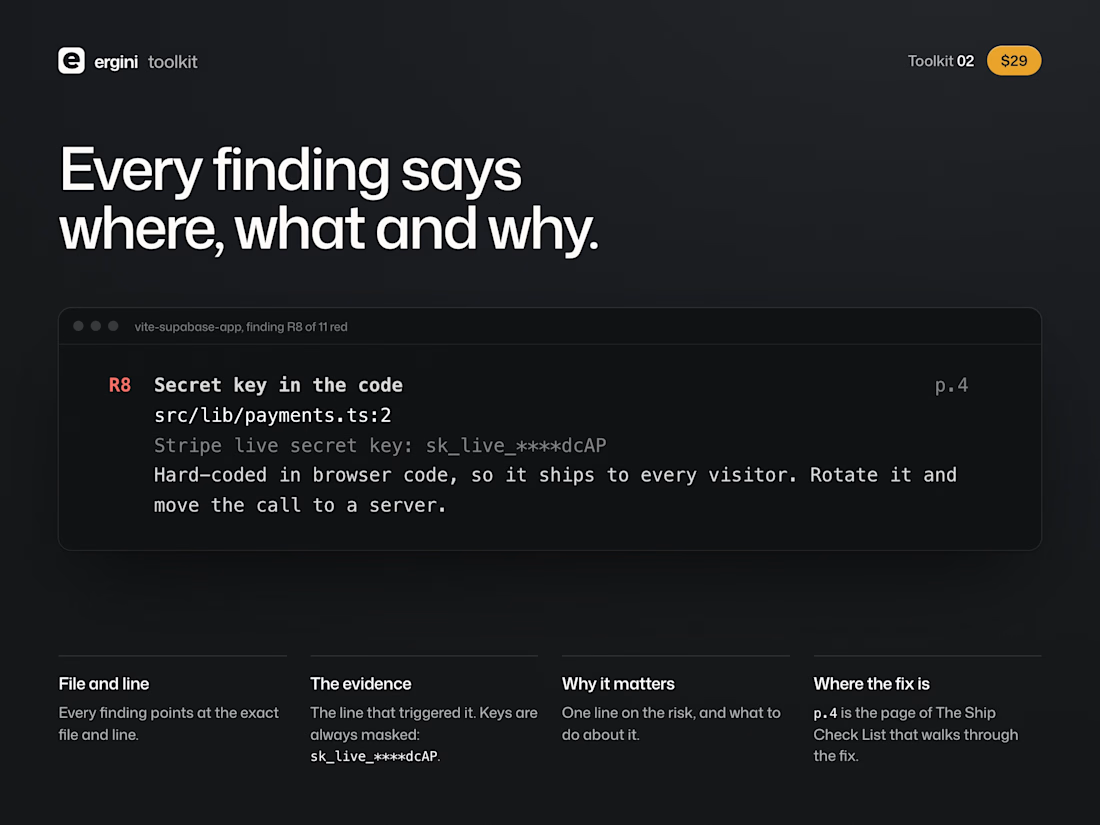
Run one command in your app's folder and it lists the gaps that expose data or money, file by file: keys that end up in the browser, the Supabase service role in client code, tables without row-level security, Stripe webhooks nobody verifies, AI routes anyone can call.
It runs locally, has no dependencies, never uploads your code, and masks every key it finds. Add --ci and it fails the build when anything is red.
It is heuristics, not a guarantee. But it catches the things I look for in the first hour of an audit.
The checklist it is built on is free: https://contra.com/products/cTLDQhiJ-the-ship-check-list-what-to-check-before-real-users-pay
What is the first thing you check before a launch?



The network for creativity
Join 1.25M professional creatives like you
Connect with clients, get discovered, and run your business 100% commission-free
Creatives on Contra have earned over $150M and we are just getting started





Related posts


The app looks amazing, but do you think the number font might be a bit hard for people to read quickly when checking their money?

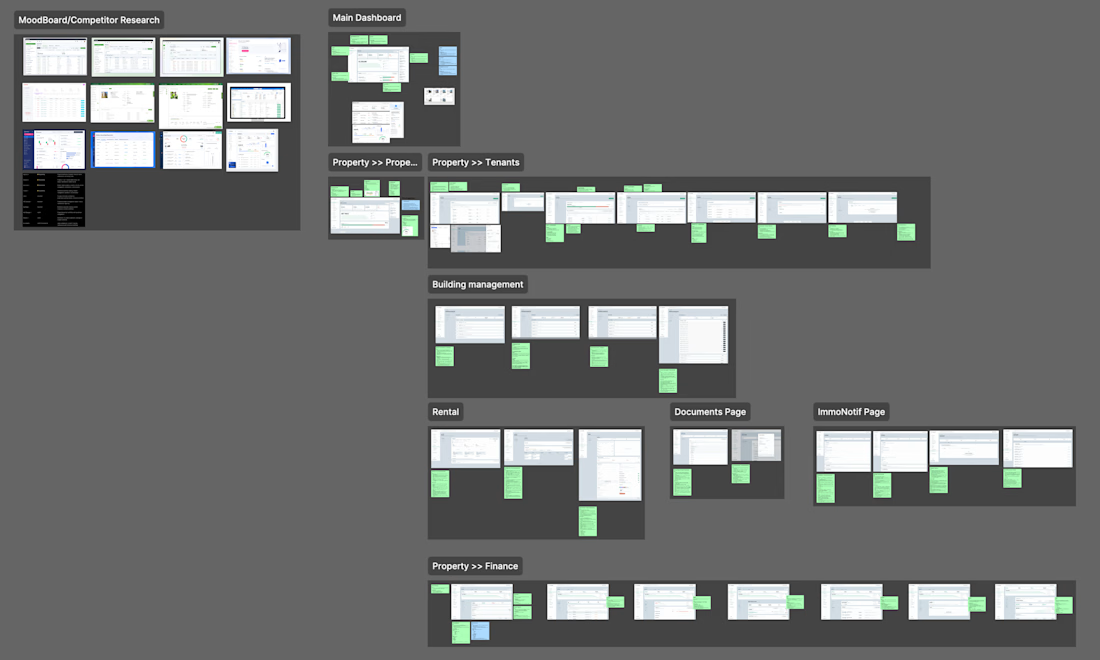
UX Audit: ImmoAdmin (Property Management SaaS)
-> UX issues mapped with improvement notes
-> Competitor research & mood board
-> 8 modules audited screen by screen
-> Wireframes with cleaner flows

Really thoughtful approach to simplifying complex SaaS flows. 👏

I'm offering 10 landing pages. $250 each. One-week turnaround. 🚀
I'm running a small experiment with SUR and opening 10 spots for people who need a simple, professionally designed landing page.
For founders, freelancers, creators and small businesses who have been putting their website off, need a place to launch something, or simply want a more professional online presence.
The offer includes:
• UX + UI design
• Responsive landing page
• Build and launch
• 1 week turnaround
Simple scope by design. If a project needs complex functionality, integrations, databases, e-commerce or custom development, we'll evaluate it separately.
Domain not included.
I'm curious to see what happens when you make it this simple to get a proper landing page out into the world.
10 spots. $250. First come, first served.
DM me or use the link in the comments to apply.


Amazing work